system_bt_AOSP10_r33_CVE-2021-0435

Android Bluetooth stack (AOSP 10 r33) with fix for CVE-2021-0435, addressing remote code execution in Bluetooth pairing.

Android Bluetooth stack (AOSP 10 r33) with fix for CVE-2021-0435, addressing remote code execution in Bluetooth pairing.

Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.

Exploit for CVE-2021-0507, a remote code execution vulnerability in Android's Bluetooth stack (system/bt). Provides proof-of-concept for the flaw.

Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…

Injects arbitrary code into a client's game.

Python-based proof-of-concept exploit for CVE-2022-34718, a remote code execution vulnerability in IPv6 on Windows, using Scapy to craft and send…

Flipper Zero firmware source code

🚨 CVE-2023-45866 - BlueDucky Implementation (Using DuckyScript) 🔓 Unauthenticated Peering Leading to Code Execution (Using HID Keyboard)

Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…

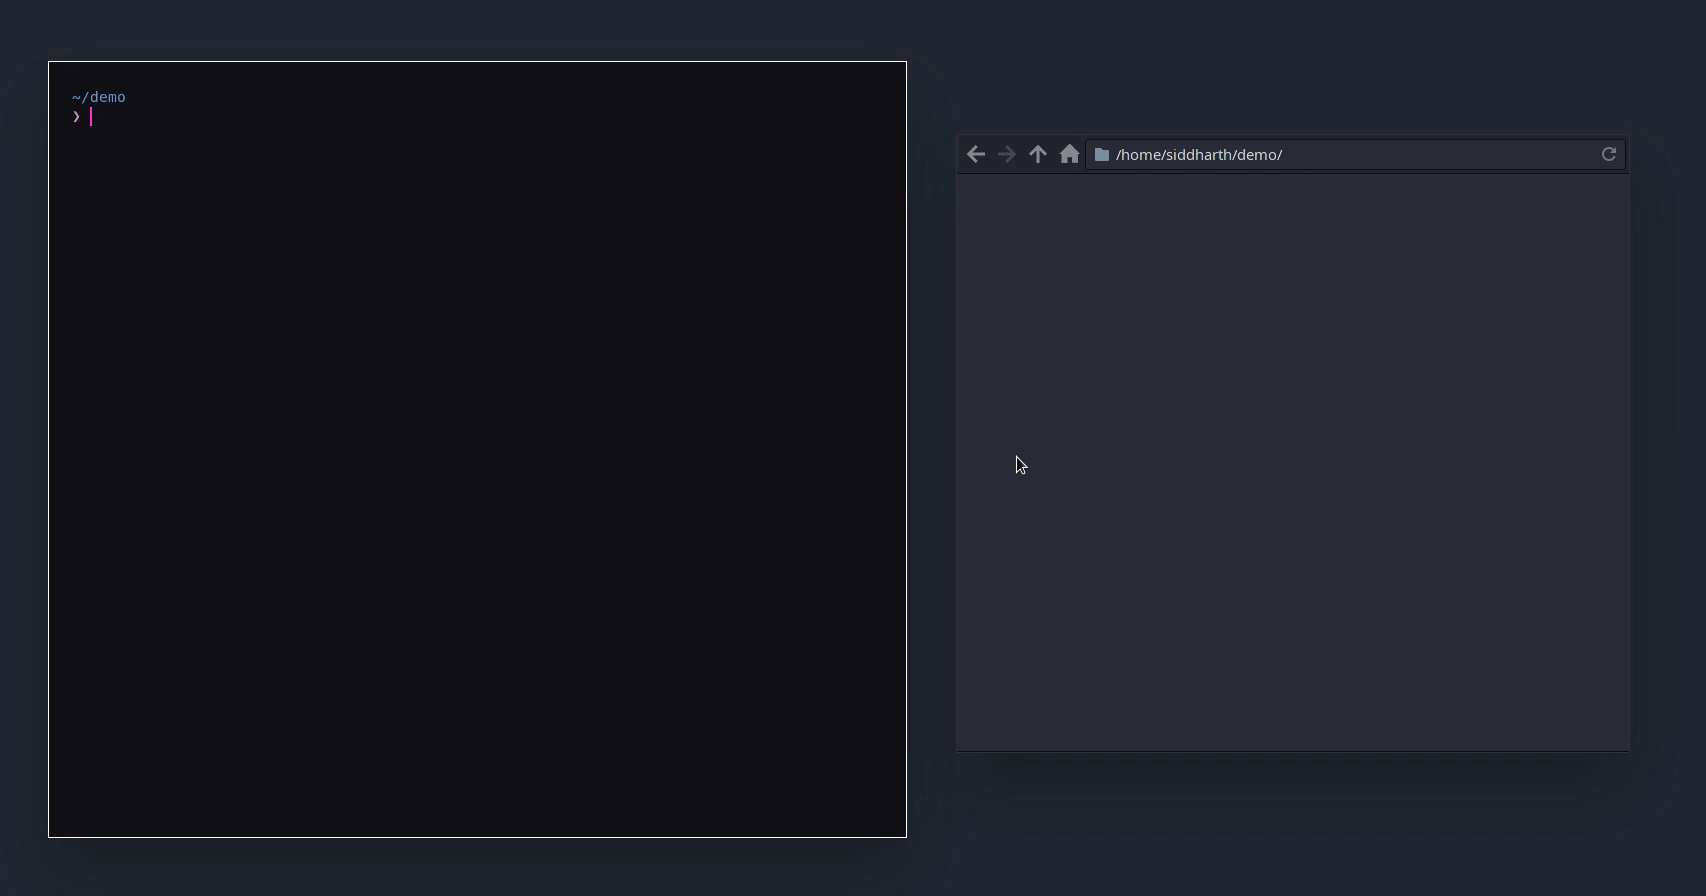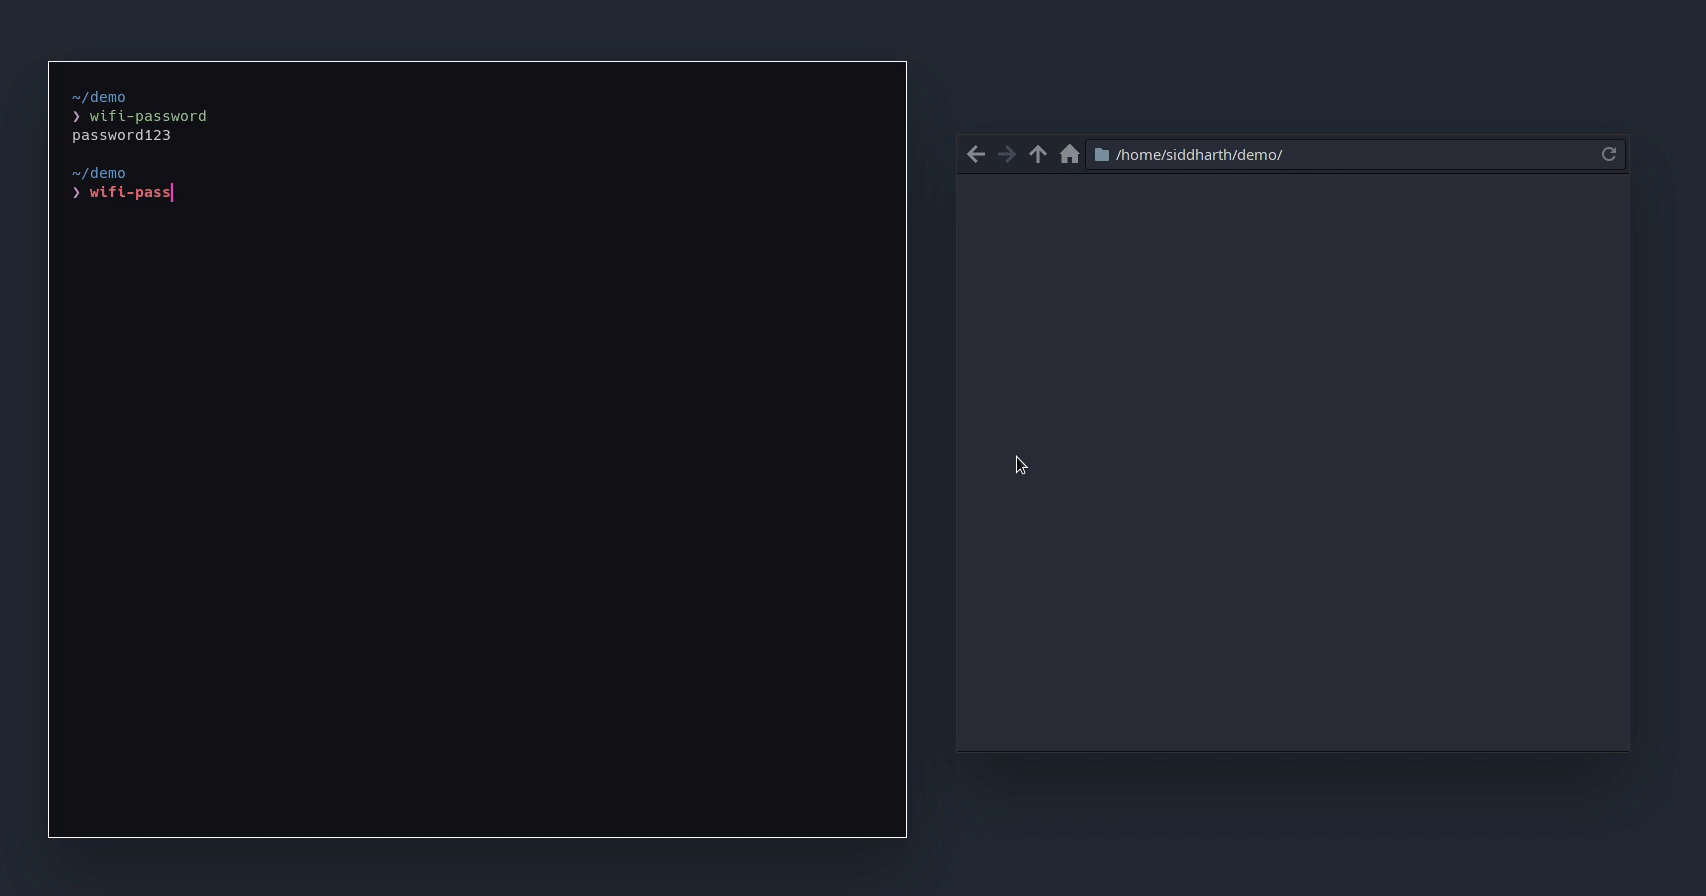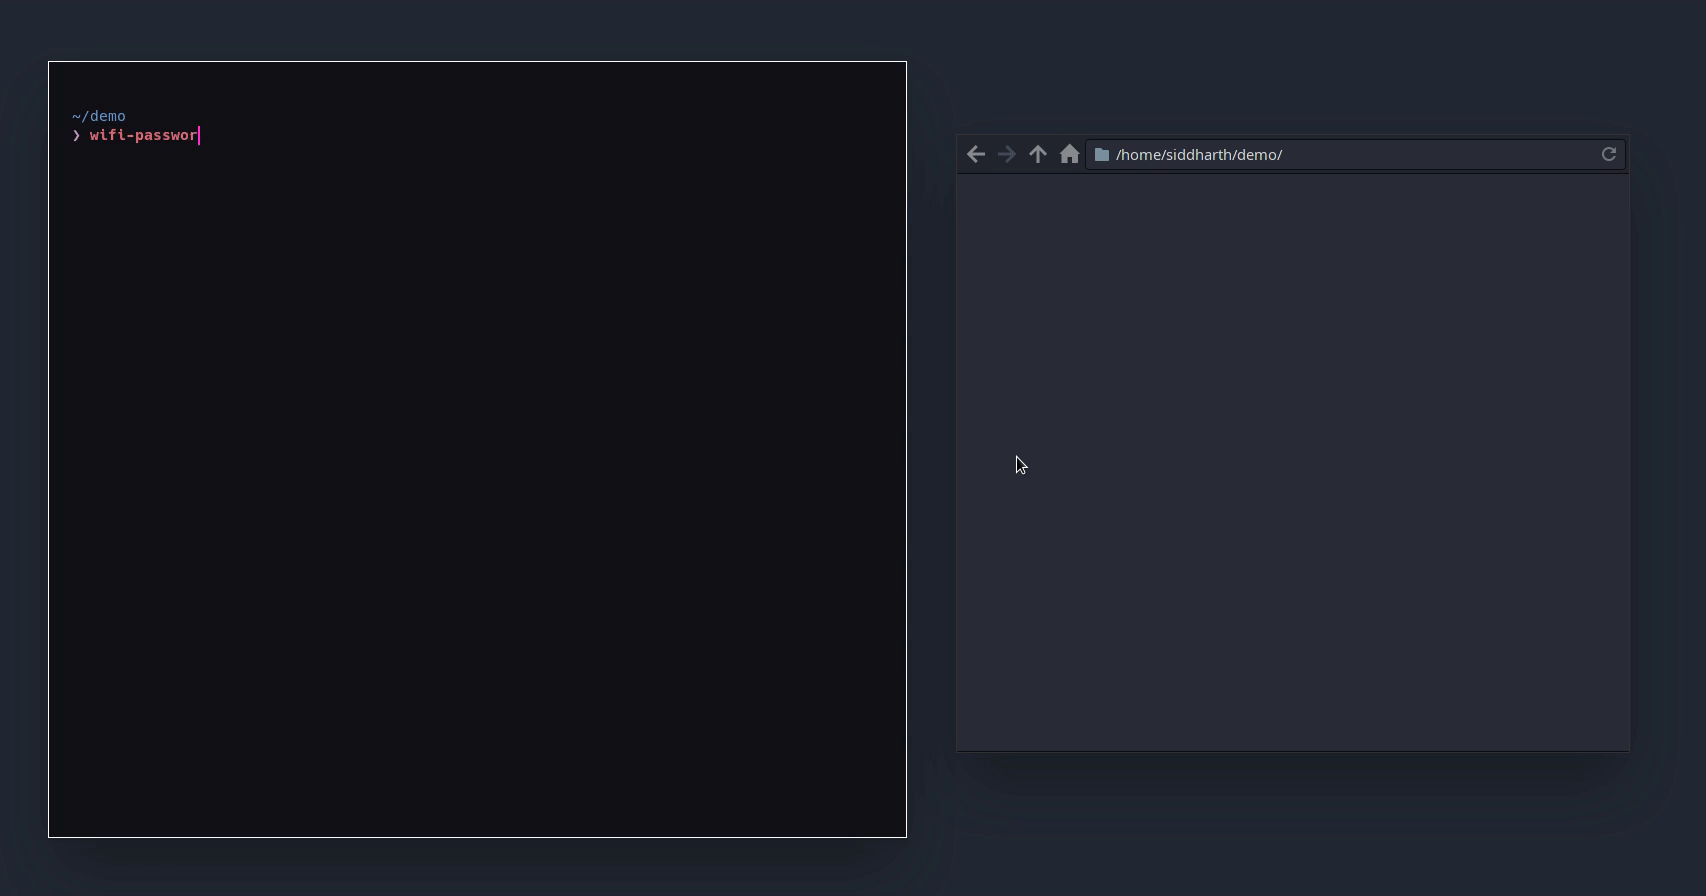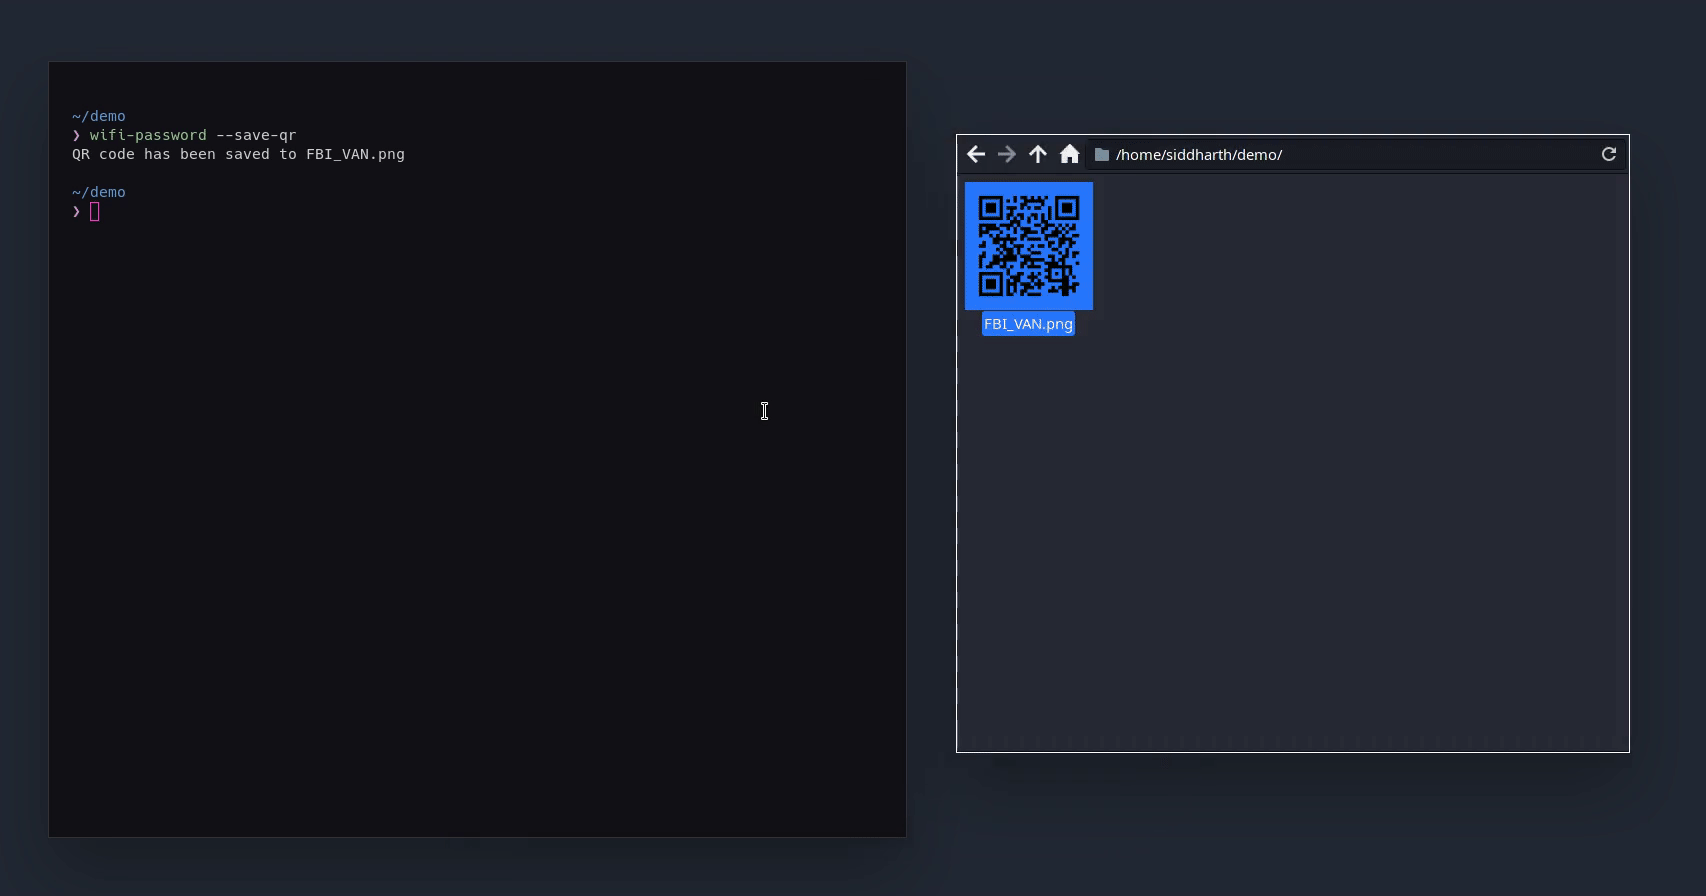
Quickly fetch your WiFi password and if needed, generate a QR code of your WiFi to allow phones to easily connect

Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…

PoC exploit for CVE-2023-35803 unauthenticated buffer overflow in Aerohive HiveOS/Extreme Networks IQ Engine, enabling remote code execution on…

BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…

Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893

Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…

This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…

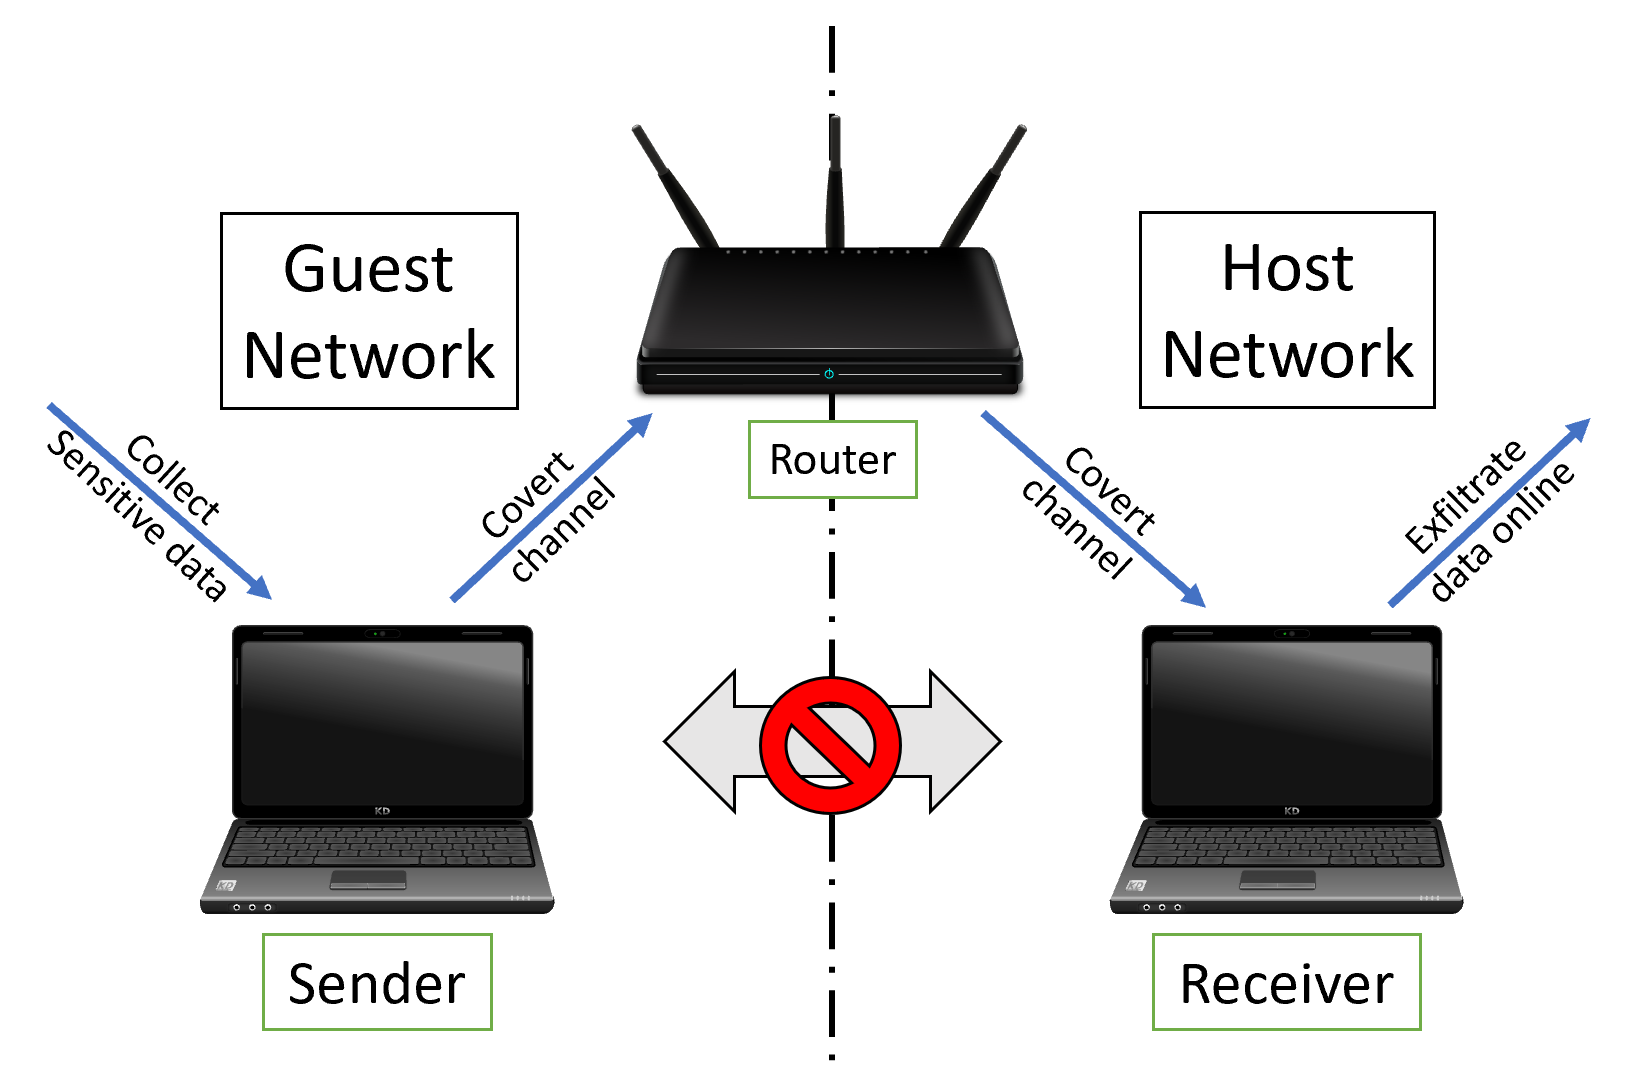
This repository includes the source code used in the "Characterization and Detection of Cross-Router Covert Channels" paper.

Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…