
CVE-2023-33538
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
command-and-controleducationexploitation+5
11 year ago
explxx/cve-2023-33538Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 samyk/skyjack
A drone engineered to autonomously seek out, hack, and wirelessly take full control over any other Parrot or 3DR drones within wireless or flying…
 0xsamy/sweet-pineapple-builder
Build your own custom WiFi Pineapple Tetra firmware tailored to any based MIPS 24Kc architecture router. (WiFi Pineapple Tetra DIY)
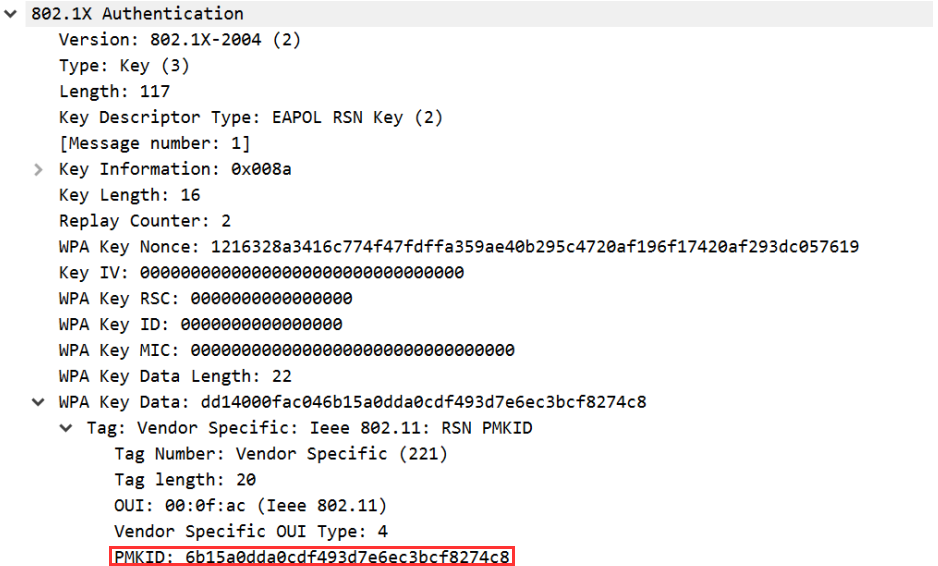 n0mi1k/pmkidcracker
A tool to crack WPA2 passphrase with PMKID value without clients or de-authentication
 qingxp9/cve-2019-6203-poc
PoC for CVE-2019-6203, works on < iOS 12.2, macOS < 10.14.4
 tomasz-lisowski/swsim
A software SIM card.
 uberguidoz/flipper
Playground (and dump) of stuff I make or modify for the Flipper Zero
 george0papasotiriou/cve-2026-21006-zigbee-light-link-factory-reset-exploit
Simulated Zigbee Light Link (ZLL) factory reset exploit for CVE-2026-21006, demonstrating unauthenticated TouchLink command injection that wipes…
 anonymouz4/apple-remote-crash-tool-cve-2018-4407
Crashes any macOS High Sierra or iOS 11 device that is on the same WiFi network
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
 xtr4nge/fruitywifi
FruityWiFi is a wireless network auditing tool. The application can be installed in any Debian based system (Jessie) adding the extra packages.…
 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…