

kr00k
 0x13enny/kr00k
PoC of CVE-2019-15126 kr00k vulnerability
exploitationpacket-sniffing-analysisvulnerability-analysis+2
0x13enny/kr00kPoC of CVE-2019-15126 kr00k vulnerability
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…
 helica-core/eap_pwn
poc of CVE-2023-52160
 eternityforest/lazymesh
Proof of concept IoT/Ham Radio mesh network with global routing over the internet
 keldnorman/cve-2024-0230-blue
Helper script to POC of CVE-2024-0230 Bluetooth
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893
 d3adp3nguin/cve-2023-33105-transient-dos-in-wlan-host-and-firmware
This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…
 george0papasotiriou/cve-2026-0101-ble-address-spoofing-via-weak-resolvable-private-address
Python PoC for CVE-2026-0101 demonstrating BLE address spoofing via replay of a captured Resolvable Private Address to impersonate a trusted…
 george0papasotiriou/cve-2026-11109-bluetooth-classic-knob-attack-key-negotiation-of-bluetooth-
Python simulation of the Bluetooth Classic KNOB attack, showing encryption key-size downgrade and brute-force decryption of intercepted Bluetooth…
 orensv/characterization-and-detection-of-cross-router-covert-channels
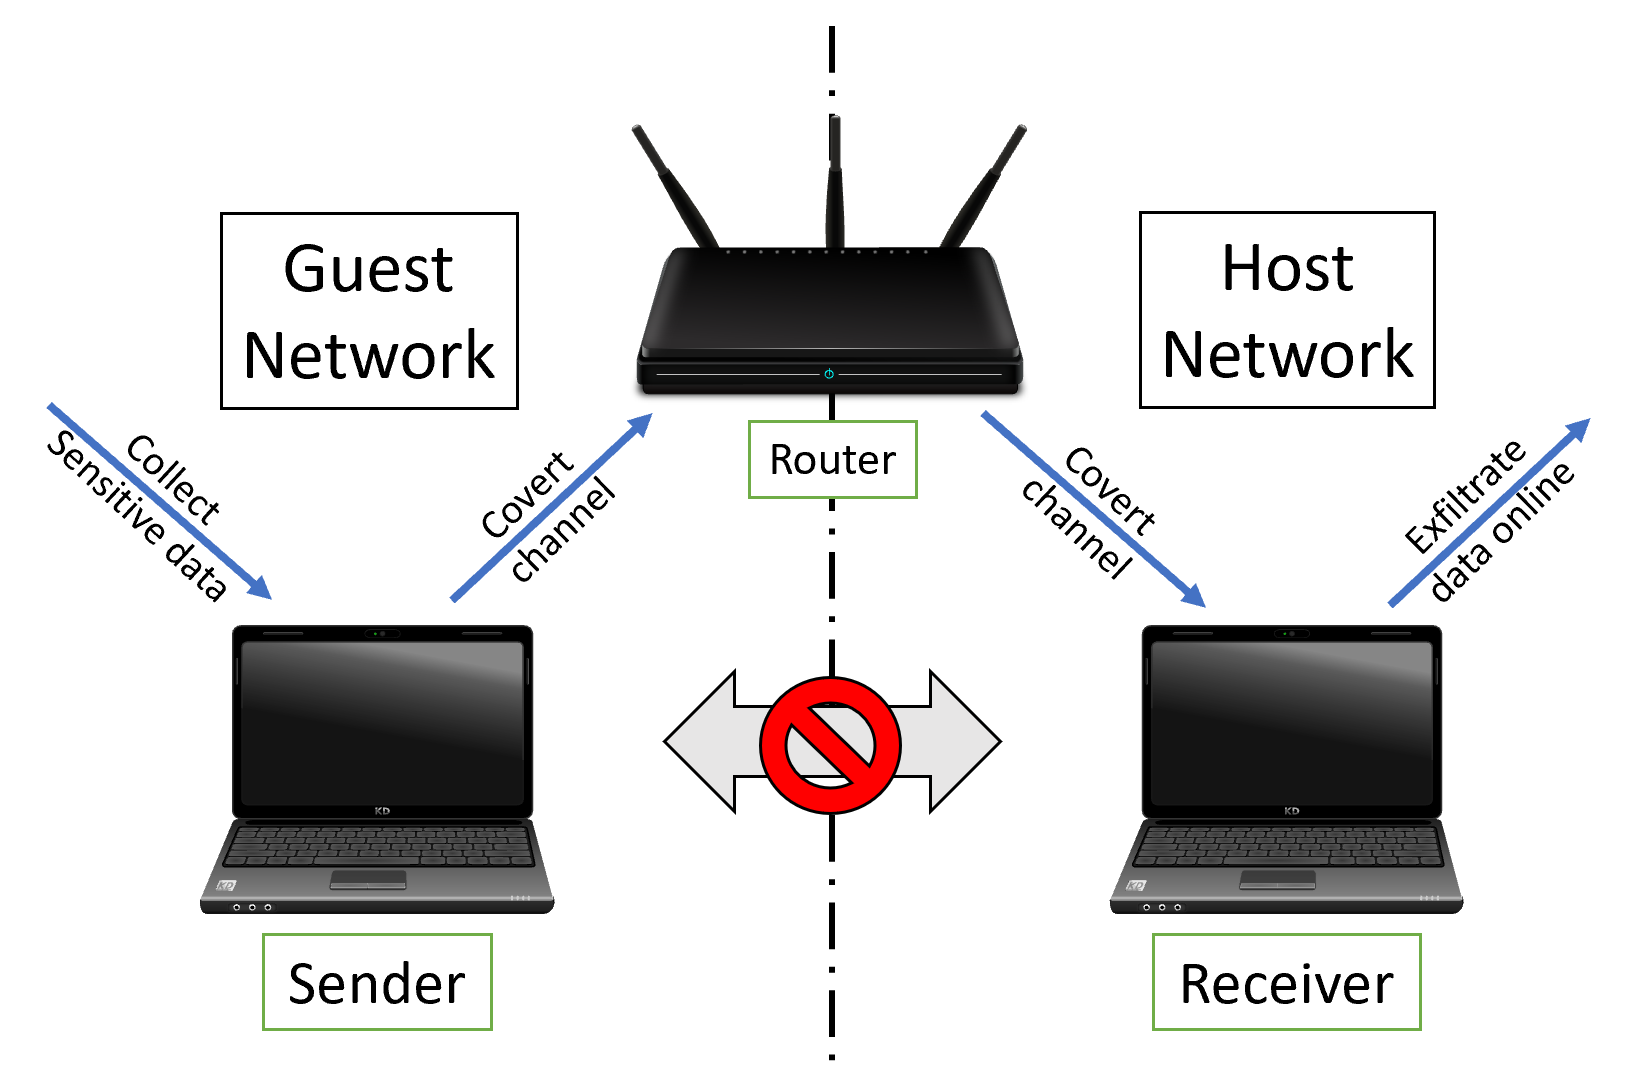
This repository includes the source code used in the "Characterization and Detection of Cross-Router Covert Channels" paper.
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 takistmr/cve-2024-20137
Python code for expoiting of vulnerability in wlan driver of MediaTek SOCs MT6890, MT7622, MT7915, MT7916, MT7981, MT7986
 mastercode112/upgraded_bluebourne-cve-2017-0785-
upgraded of BlueBourne CVE-2017-0785 to python3
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
 xg3nesis/rustyinjector
Rust implementation of Marc Newlin's keystroke injection proof of concept (CVE-2023-45866).
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 web-logs2/hostapd_mirror
mirror of https://w1.fi/cgit/hostap/ till 30/01/2023 for CVE-2022-23303/4 - c22