

 yashodhanvivek/firebolt-wristphone-vulnerability
This repository is for Firebolt wristphone vulnerability for CVE ID CVE-2024-30656 suggested by MITRE. Mitre yet to confirm on ID
 osqzss/gps-sdr-sim
Software-Defined GPS Signal Simulator
 pulkin/esp8266-injection-example
Example project to demonstrate packet injection / sniffer capabilities of ESP8266 IC.
 vabold/ds-wireless-communication-remote-code-execution
Injects arbitrary code into a client's game.
 osqzss/bladegps
Real-time GPS signal simulator for bladeRF
 salgio/esptouchcatcher
eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
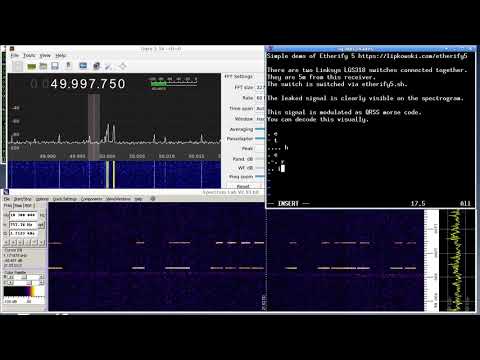 sq5bpf/etherify
Etherify - bringing the ether back to ethernet
 rdomanski/exploits_and_advisories
Repository that tracks public exploits, vulnerabilities and advisories that I [co-]discovered or [co-]authored.
 riverloopsec/killerbee
IEEE 802.15.4/ZigBee Security Research Toolkit
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 applied-risk/loracrack
LoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys
 hanianis/cve-2025-63353
A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…
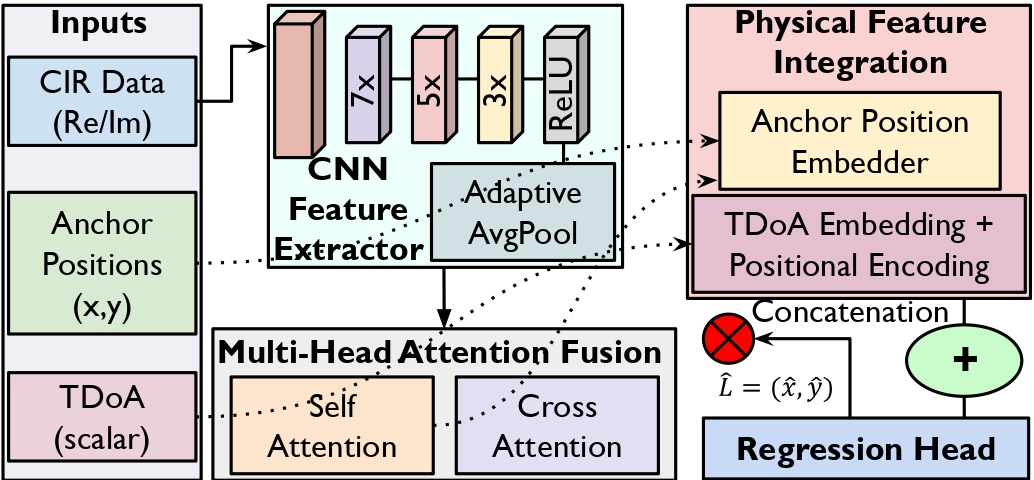 sec5gloc/sec5gloc
Adversary-resilient deep learning architecture for secure 5G indoor localization, combining CNN and multi-head attention to defend against signal…
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 itseclab-hsel/cve-2022-24611
Details regarding the Z-Wave S0-No-More attack
 kh4sh3i/cve-2025-34152
Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…