
CVE-2023-45866_WIP
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…

Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…

Proof-of-concept exploit for CVE-2021-36630 targeting Ruckus SmartZone wireless controllers via UDP command injection on port 9001.

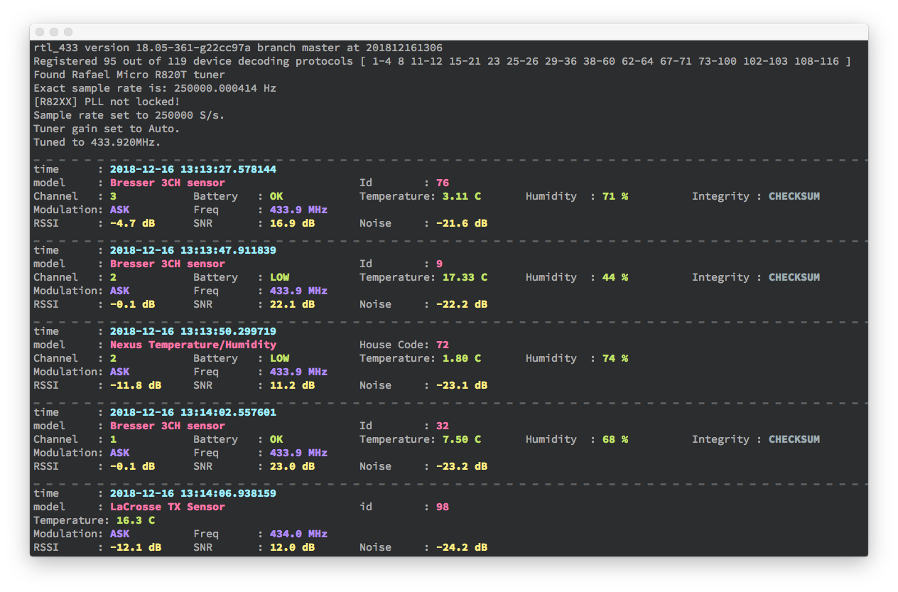
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)

⚡️An awesome list of the best Termux hacking tools

A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.

The RF and reverse engineering framework for everyone. Follow and ★ to show your support!

Damn Vulnerable Drone is an intentionally vulnerable drone hacking simulator based on the popular ArduPilot/MAVLink architecture, providing a…

WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…

PIrateRF transforms your Raspberry Pi Zero W into a portable RF signal generator that spawns its own WiFi hotspot. Control everything from FM…

Blueborne CVE-2017-0781 Android heap overflow vulnerability

Remote buffer overflow over wifi_stack in wpa_supplicant binary in android 11, platform:samsung a20e, stock options so like works out of the box

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…

Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…

Python simulation of CVE-2026-11117 demonstrating WPA2 4-way handshake PTK reinstallation and nonce reuse to illustrate the KRACK attack.

Details regarding the Z-Wave S0-No-More attack

This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).