

-BuL
 hegaz0y/-bul
EDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
bluetooth-securityexploitationexploit-frameworks+3
1
hegaz0y/-bulEDSEC_BKIF is a keystroke injection tool for Android, Linux, and iOS. With the help of CVE-2023-45866, it grants users unprecedented control over…
 xdavidhu/probesniffer
🔍 A tool for sniffing unencrypted wireless probe requests from devices.
 blackhillsinfosec/wififorge
Automated WiFi hacking lab environment using mininet-wifi to simulate wireless attack vectors for pentester training, eliminating hardware overhead.
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 matheus-garbelini/esp32_esp8266_attacks
Proof of Concept of ESP32/8266 Wi-Fi vulnerabilties (CVE-2019-12586, CVE-2019-12587, CVE-2019-12588)
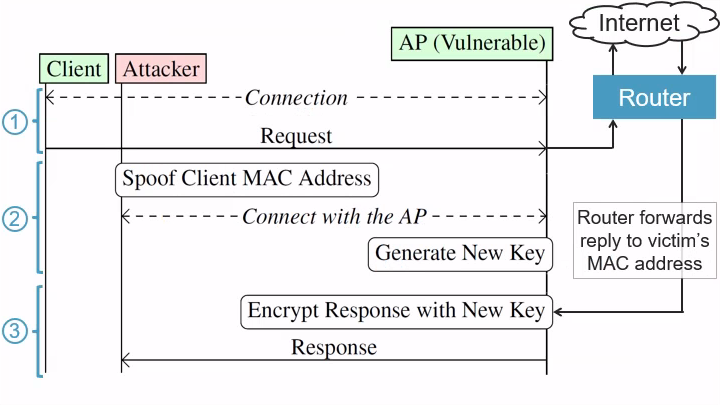 vanhoefm/macstealer
MacStealer: Wi-Fi Client Isolation Bypass
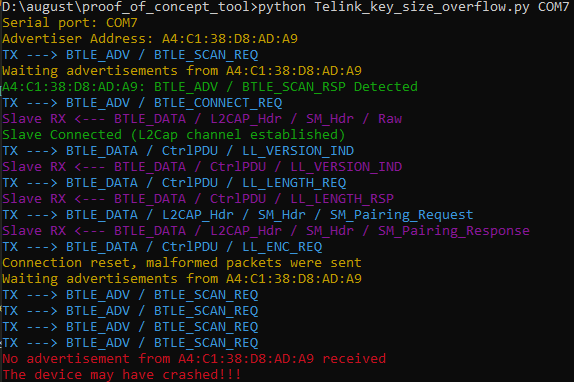 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
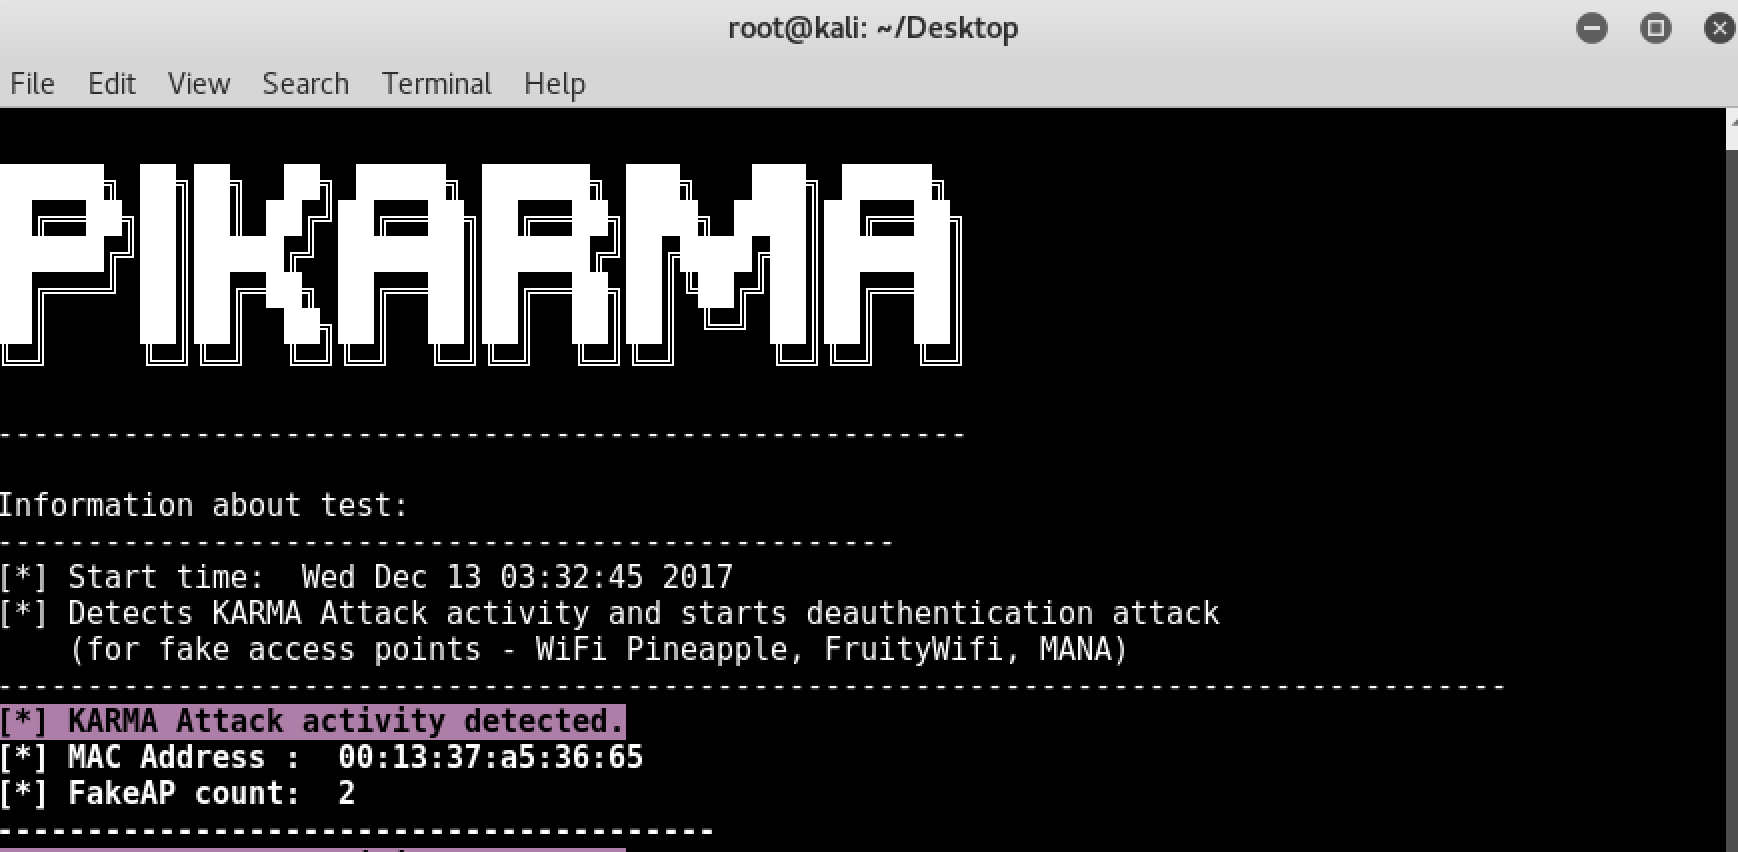 wipi-hunter/pikarma
📡🍓🍍 Detects wireless network attacks performed by KARMA module (fake AP). Starts deauthentication attack (for fake access points)
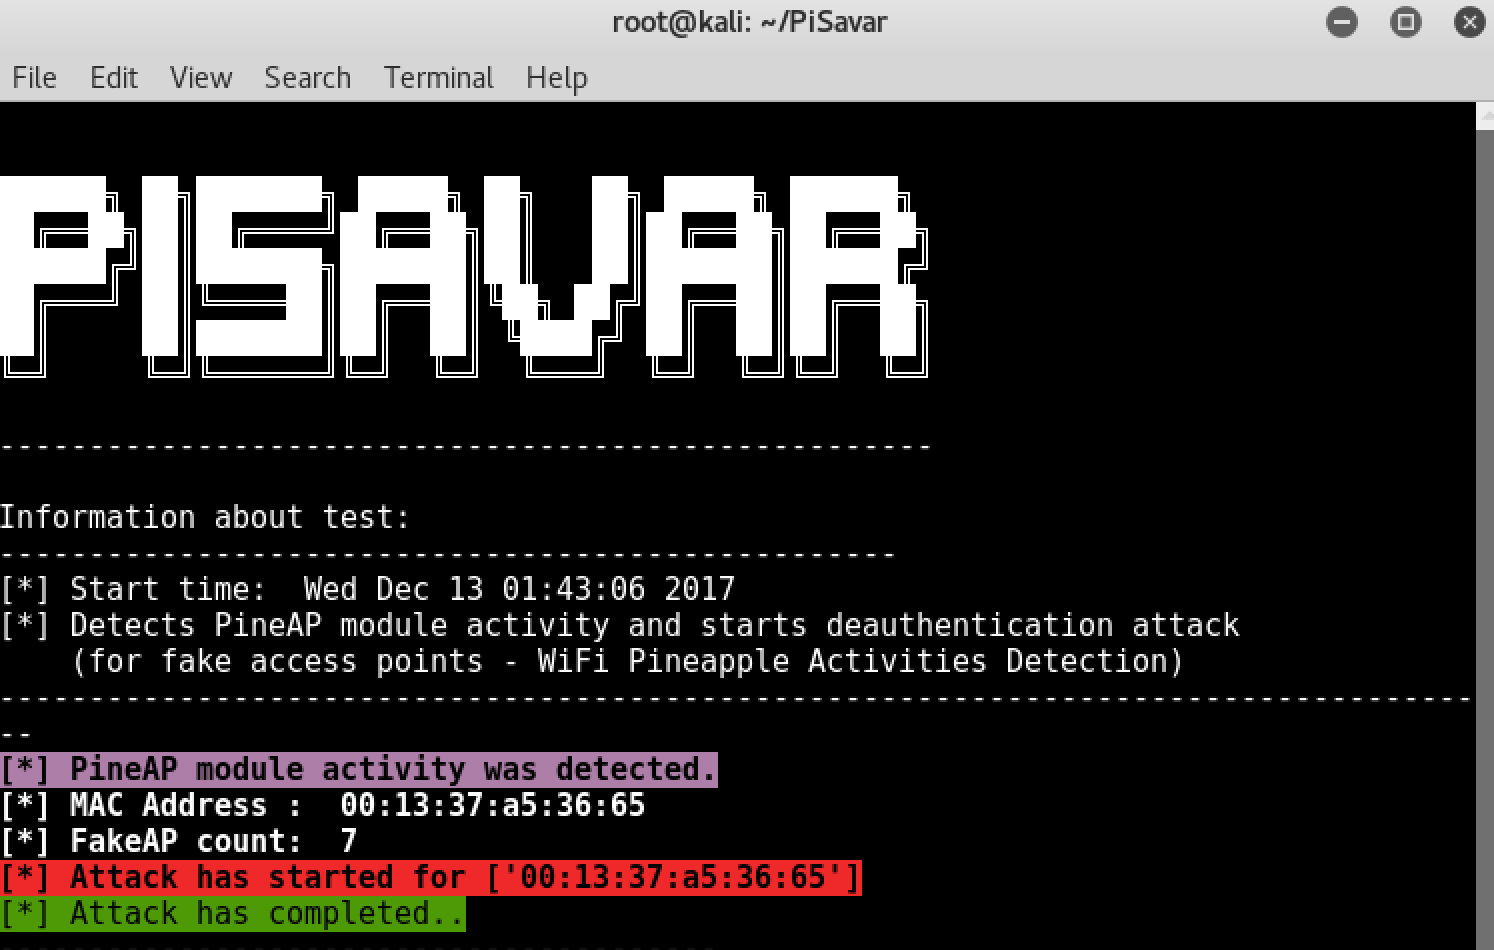 wipi-hunter/pisavar
📡 🍍Detects activities of PineAP module and starts deauthentication attack (for fake access points - WiFi Pineapple Activities Detection)
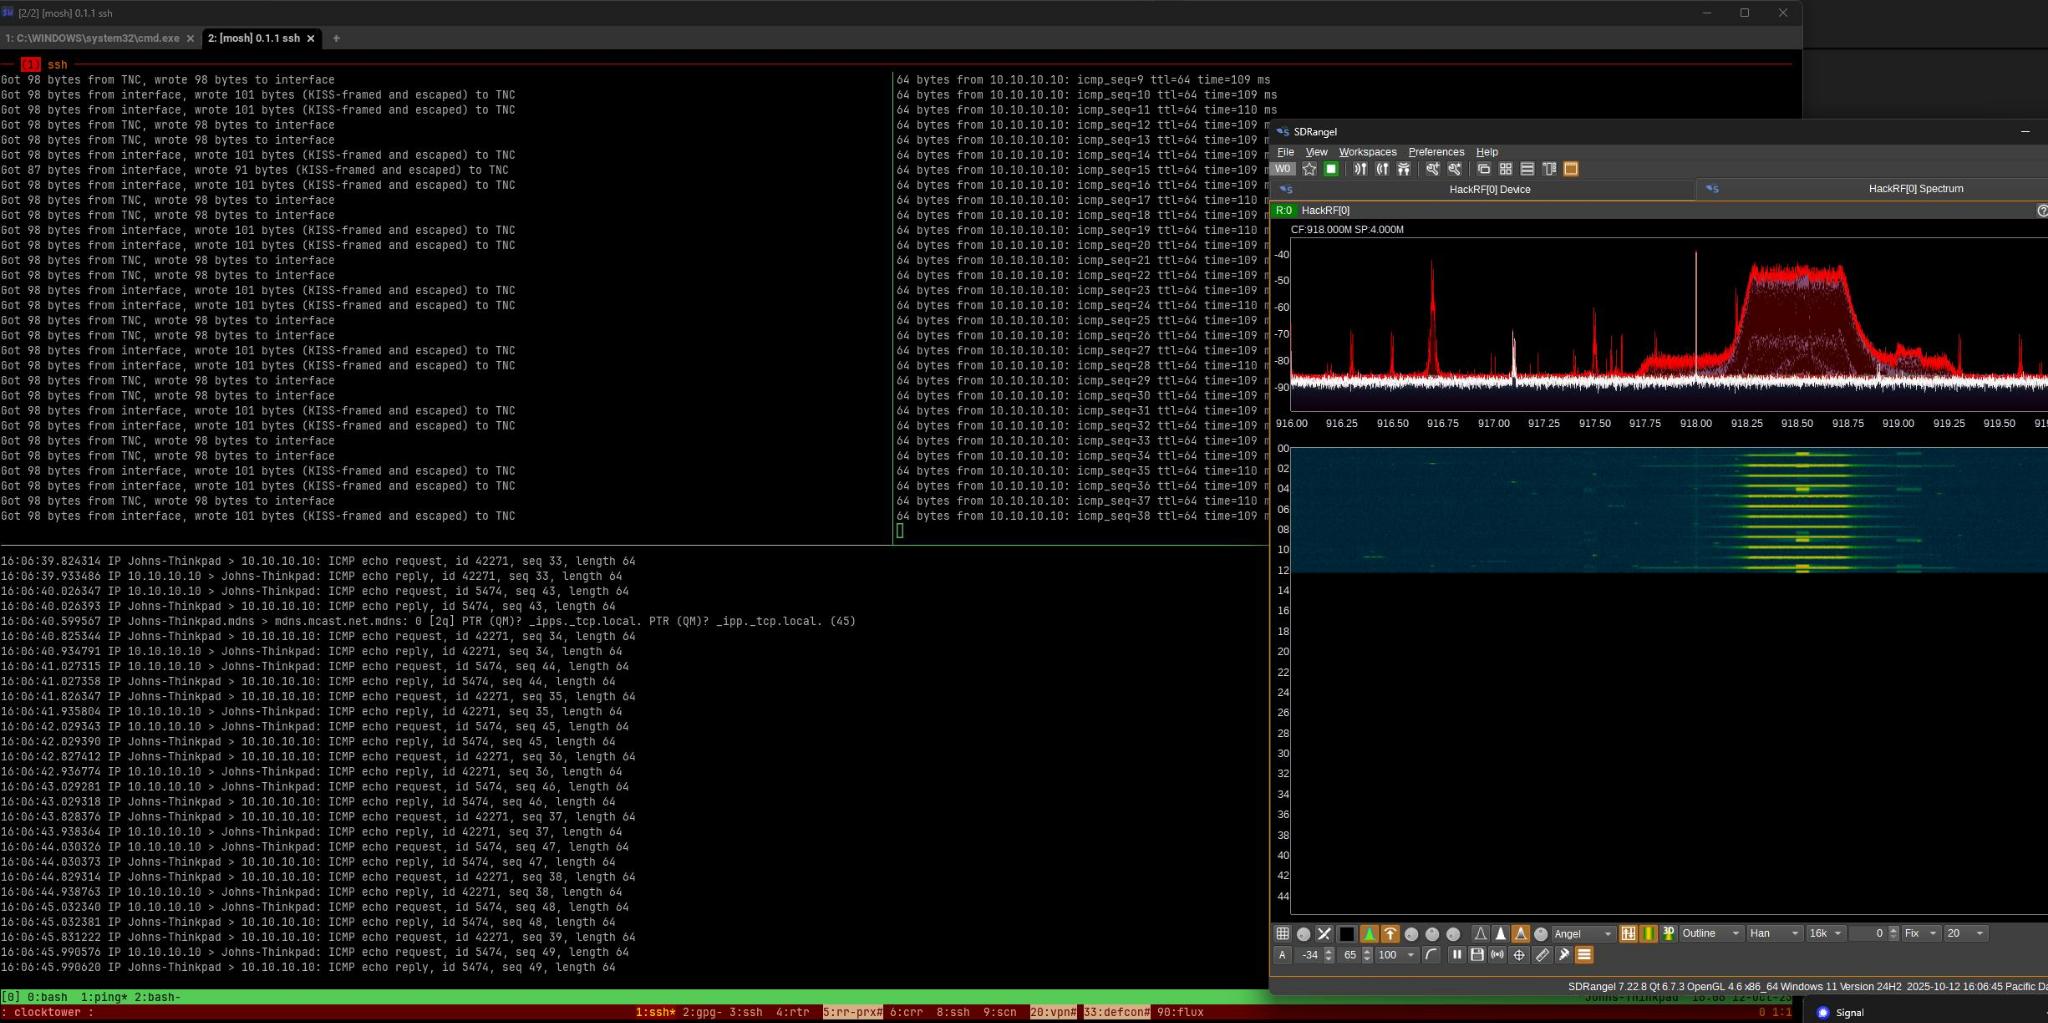 datapartyjs/meshtnc
Firmware for converting consumer LoRa radios into KISS TNC modems with serial CLI, BLE packet sniffing, and APRS/AX.25 compatibility for packet radio…
 plantdaddy/fuzzap
A python script for obfuscating wireless networks
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 phuchaudeveloper/badblue
CVE-2024-21306 BadBlue implementation (Using DuckyScript)
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
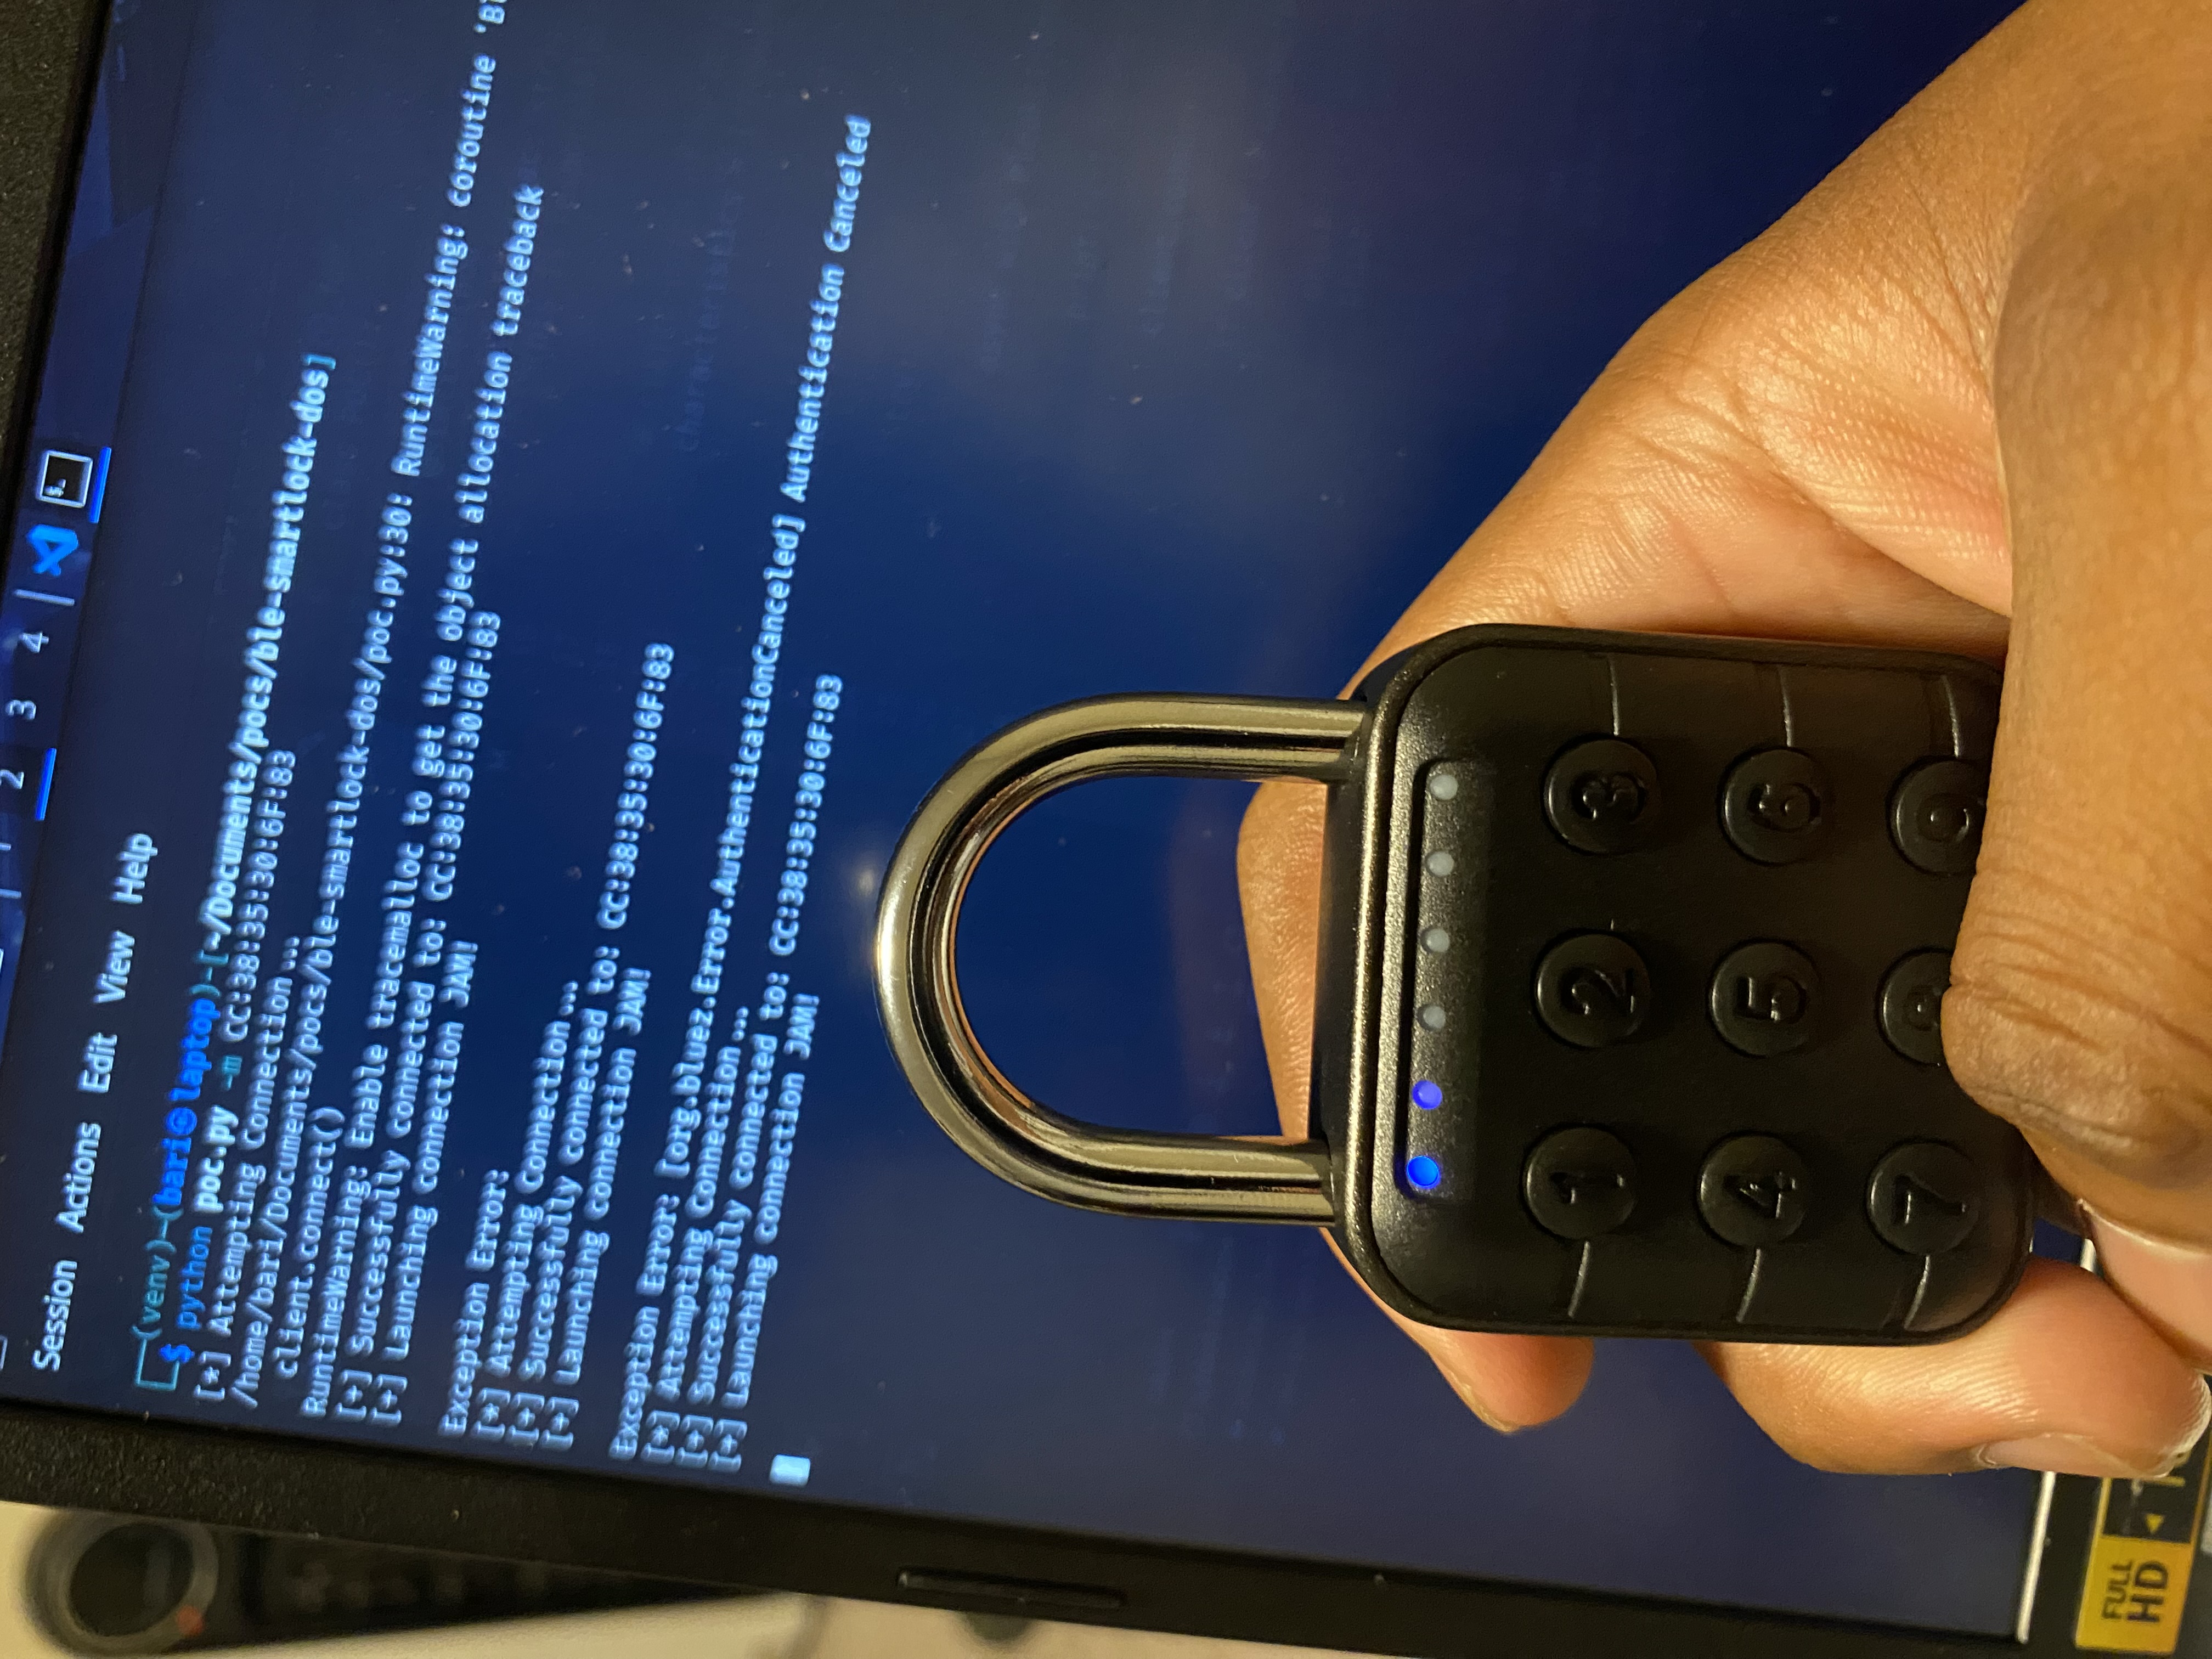 nsm-barii/cve-2025-15474
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …
 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.
 kimocoder/android_kernel_oneplus_avicii
OnePlus Nord (avicii) NeverSettle Kernel Source
 mretallack/dronecamera
Drone HASAKEE FPV video app for Android