
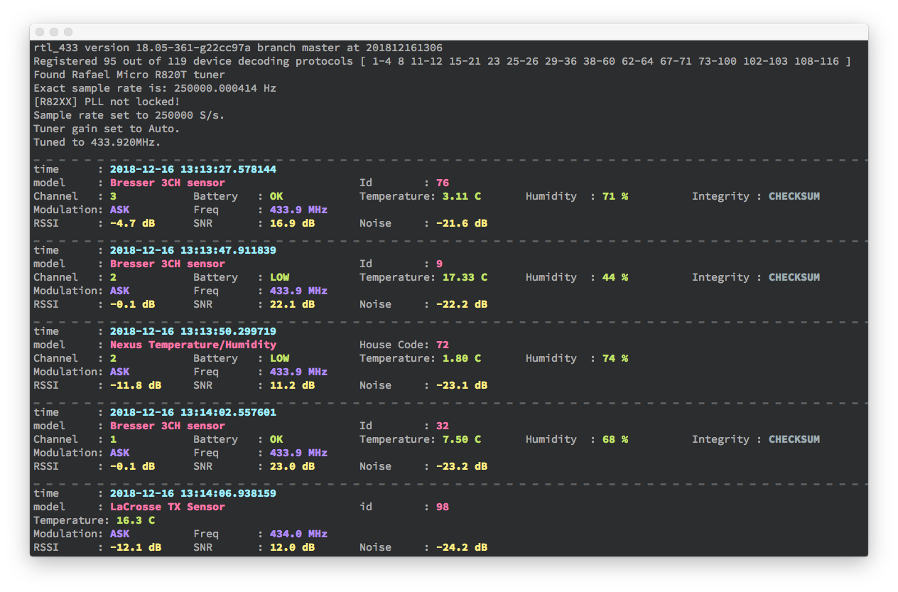
rtl_433
 merbanan/rtl_433
Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
hardware-iot-securityinformation-gatheringreverse-engineering+1
7.9k
merbanan/rtl_433Program to decode radio transmissions from devices on the ISM bands (and other frequencies)
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 samyk/skyjack
A drone engineered to autonomously seek out, hack, and wirelessly take full control over any other Parrot or 3DR drones within wireless or flying…
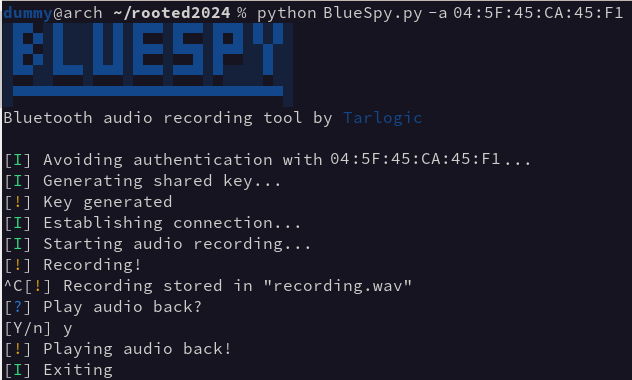 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 martinmarinov/tempestsdr
Remote video eavesdropping using a software-defined radio platform
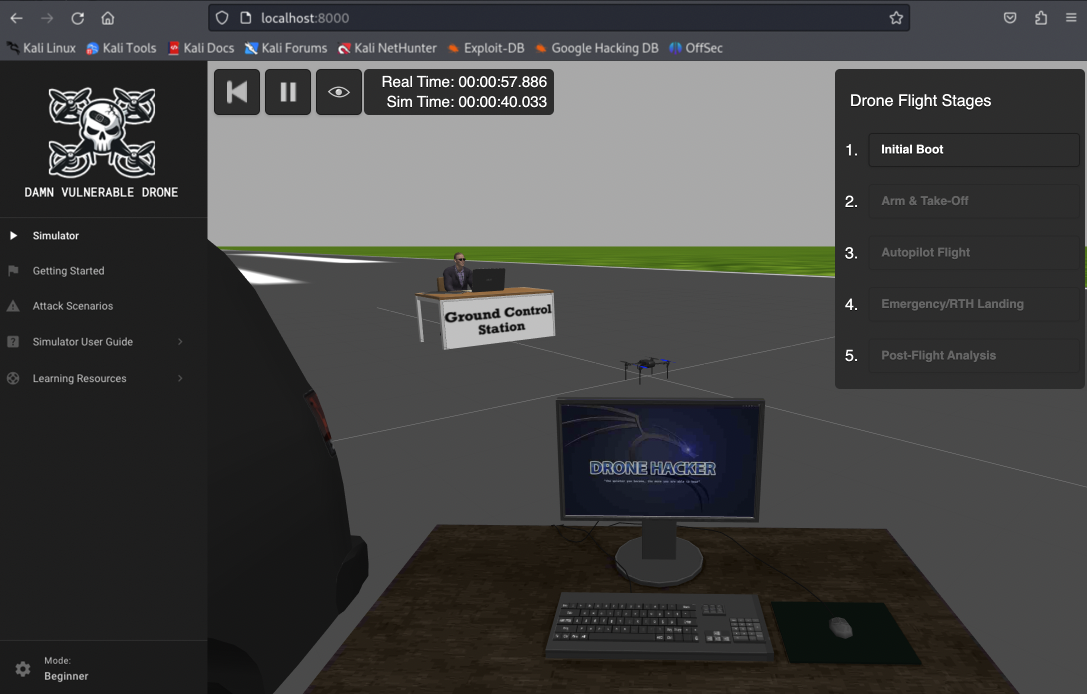 nicholasaleks/damn-vulnerable-drone
Damn Vulnerable Drone is an intentionally vulnerable drone hacking simulator based on the popular ArduPilot/MAVLink architecture, providing a…
 t6x/reaver-wps-fork-t6x
Brute-force attack tool against WPS registrar PINs to recover WPA/WPA2 passphrases, supporting online brute force and offline Pixie Dust attacks on…
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
 tylous/sniffair
A framework for wireless pentesting.
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 ricardojoserf/wifi-pentesting-guide
WiFi Penetration Testing Guide
 kamorin/dhcpig
DHCP exhaustion script written in python using scapy network library