
Zhilly
 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…
embedded-systems-securityhardware-hackingiot-security+6
2
sacriphanius/zhilly🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…

 keldnorman/cve-2024-0230-blue
Helper script to POC of CVE-2024-0230 Bluetooth
 moften/cve-2025-24271
Vulnerabilidad en AirPlay expone información sensible en dispositivos Apple
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
 bayazid-bit/cve-2018-18441-exploit
D-Link DCS series Wi-Fi camera expose sensitive information.
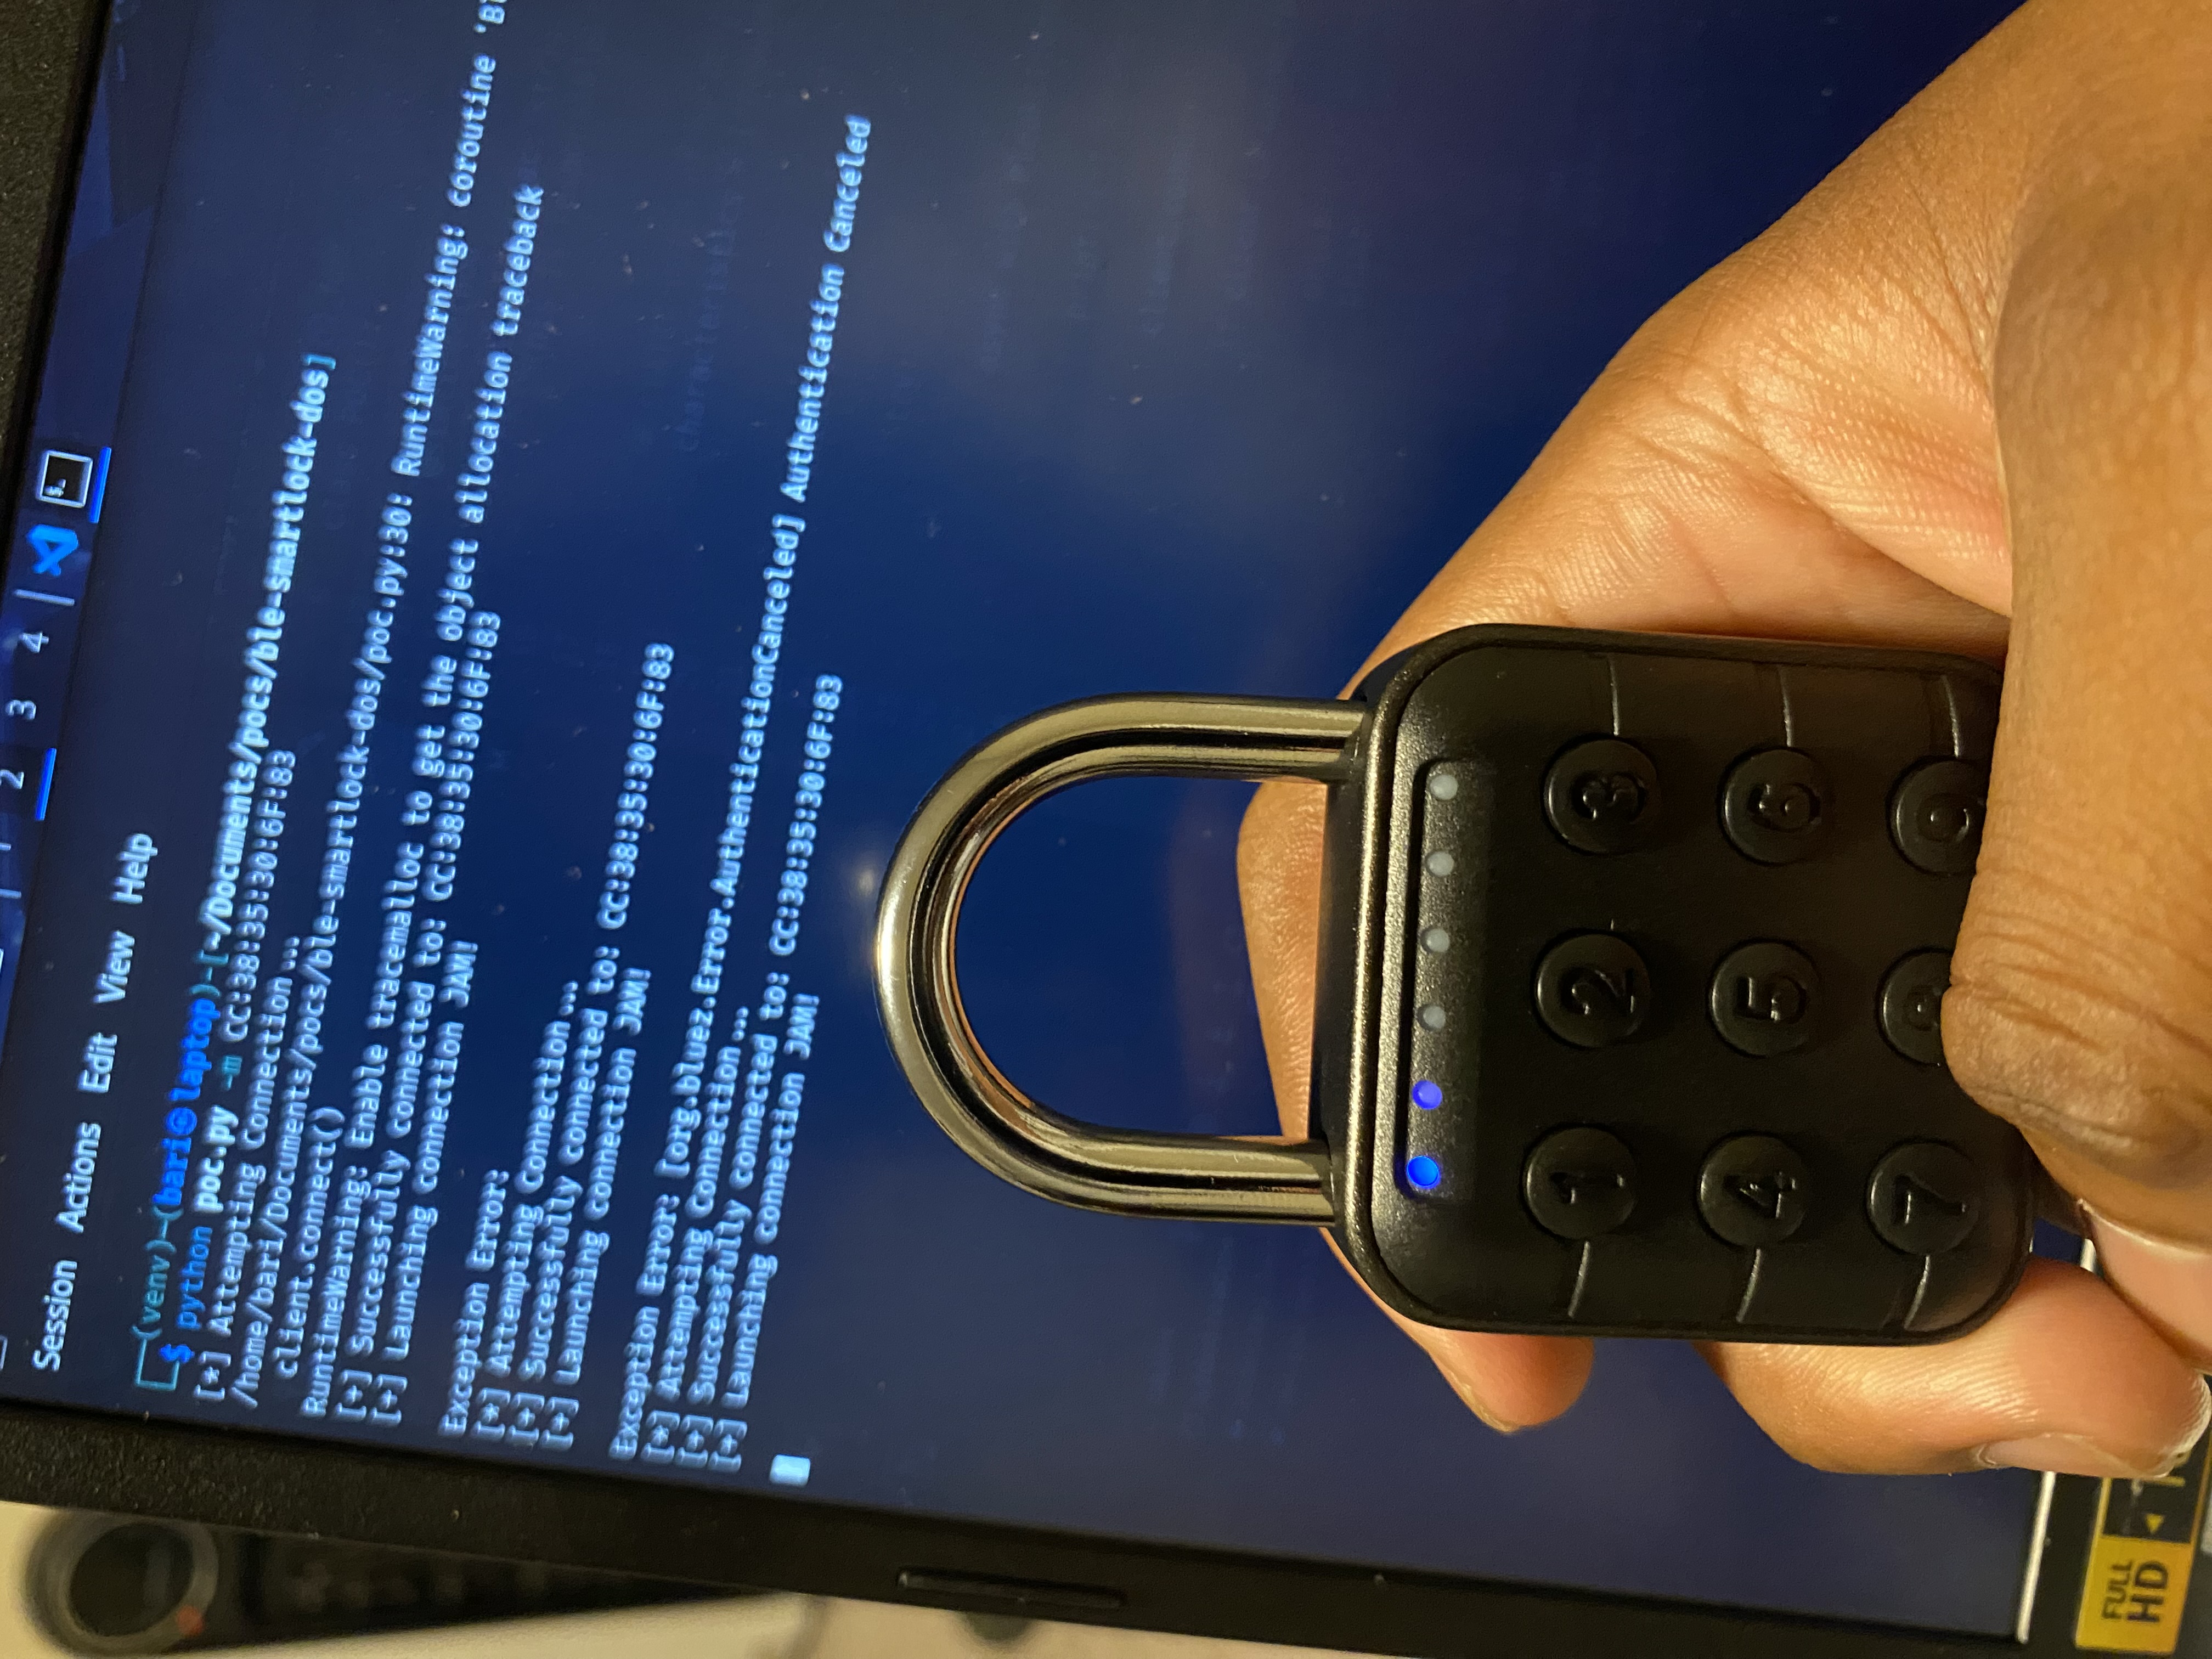 nsm-barii/cve-2025-15474
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …
 george0papasotiriou/cve-2026-11109-bluetooth-classic-knob-attack-key-negotiation-of-bluetooth-
Python simulation of the Bluetooth Classic KNOB attack, showing encryption key-size downgrade and brute-force decryption of intercepted Bluetooth…
 coleshelly/bandexploit
M1 Band Smart Watch Bluetooth Low Energy Exploit python script (CVE-2018-11631)
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 alainx277/cve-2025-24797
Meshtastic buffer overflow vulnerability - CVE-2025-24797
 cedric-martz/cve-2025-36911_scan
This script can be used to check if a Bluetooth device is vulnerable to CVE-2025-36911.
 naren-jayram/linux-heap-based-type-confusion-in-l2cap
CVE-2020-12351
 itseclab-hsel/cve-2022-24611
Details regarding the Z-Wave S0-No-More attack
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…
 mastercode112/upgraded_bluebourne-cve-2017-0785-
upgraded of BlueBourne CVE-2017-0785 to python3
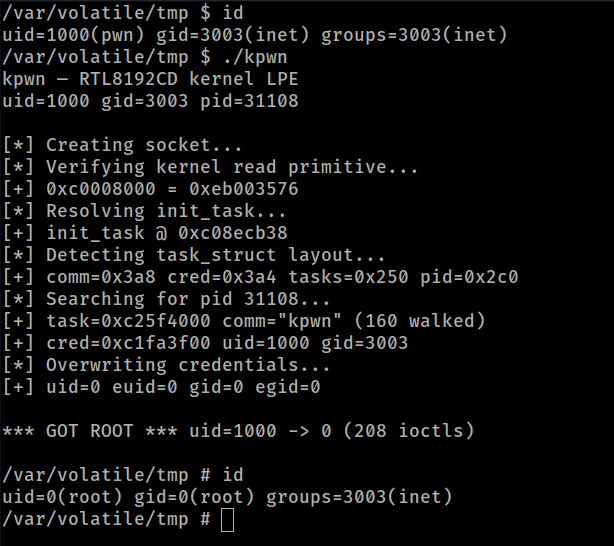 totekuh/cve-2026-36355
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…
 the-girl-who-lived/cve-2020-11539
Improper Access Control in Tata Sonata Smartband