
WiFi-SpiderWeb
 badrrx/wifi-spiderweb
An active cyber defense & honeypot system for OpenWrt routers running from a USB drive.
defensive-toolsembedded-systems-securityhardware-security+7
3
badrrx/wifi-spiderwebAn active cyber defense & honeypot system for OpenWrt routers running from a USB drive.
 george0papasotiriou/cve-2026-0101-ble-address-spoofing-via-weak-resolvable-private-address
Python PoC for CVE-2026-0101 demonstrating BLE address spoofing via replay of a captured Resolvable Private Address to impersonate a trusted…
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 coleshelly/bandexploit
M1 Band Smart Watch Bluetooth Low Energy Exploit python script (CVE-2018-11631)
 alt3kx/airdecloak-ng
My Aircrack-ng contribution with Thomas d'Otreppe
 0xa1m/cve-2025-63353
This is a Proof-Of-Concept of CVE-2025-63353
 alainx277/cve-2025-24797
Meshtastic buffer overflow vulnerability - CVE-2025-24797
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 xqi1337/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 naren-jayram/linux-heap-based-type-confusion-in-l2cap
CVE-2020-12351
 itseclab-hsel/cve-2022-24611
Details regarding the Z-Wave S0-No-More attack
 sergeb250/blueducky
BlueDucky exploits a Bluetooth vulnerability, specifically CVE-2023-45866, which allows an attacker to inject keystrokes into a target device. The…
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 takistmr/cve-2024-20137
Python code for expoiting of vulnerability in wlan driver of MediaTek SOCs MT6890, MT7622, MT7915, MT7916, MT7981, MT7986
 mastercode112/upgraded_bluebourne-cve-2017-0785-
upgraded of BlueBourne CVE-2017-0785 to python3
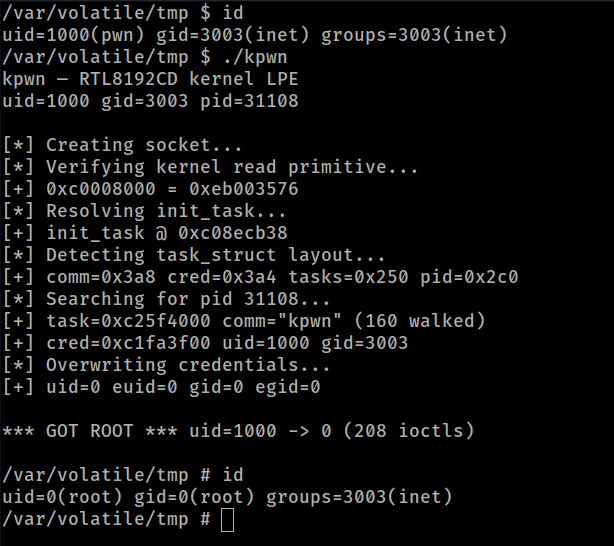 totekuh/cve-2026-36355
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls
 the-girl-who-lived/cve-2020-11539
Improper Access Control in Tata Sonata Smartband