
CVE-2023-33538
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
command-and-controleducationexploitation+5
1
explxx/cve-2023-33538Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 nanopathi/system_bt_aosp10_r33_cve-2021-0522
Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
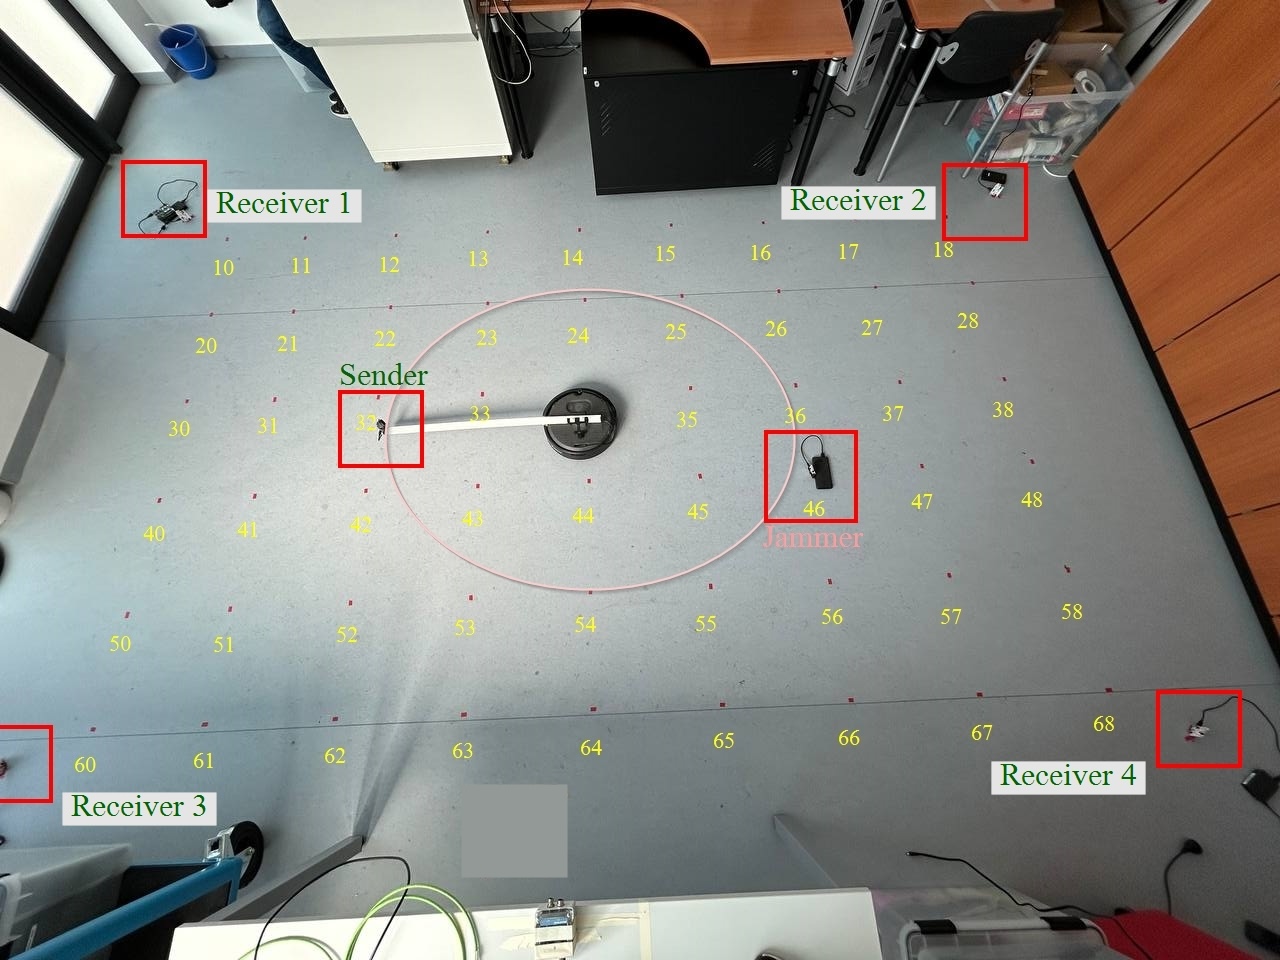 afbf4c8996f/jammer-loc
Implements machine and deep learning methods for indoor UWB jammer localization, including hyperparameter optimization, classification, and…
 trinadh465/system_bt_aosp10_r33_cve-2021-0589
Patched Android Bluetooth stack (AOSP10) addressing CVE-2021-0589, with build instructions for AOSP and Linux.
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516
Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0326
Patched wpa_supplicant and hostapd for Android 10 (r33) addressing CVE-2021-0326 vulnerability in Wi-Fi client and AP components, enhancing wireless…
 shaikusaf/external_wpa_supplicant_8_aosp10_r33cve-2021-0326
Android Wi-Fi vulnerability research repository containing patched wpa_supplicant source for CVE-2021-0326, enabling analysis and testing of the…
 trinadh465/packages_apps_nfc_aosp10_r33_cve-2020-0453
Android NFC package patched for CVE-2020-0453, addressing a security vulnerability in the NFC component.
 uthrasri/system_connectivity_wificond_cve-2021-0392
Exploit for CVE-2021-0392 targeting Android's wificond system service for privilege escalation via a connectivity vulnerability.
 761669642/mahesh-970-cve-2023-21125_bluedriod_repo
Targeted reference for CVE-2023-21125, an Android BlueDroid Bluetooth vulnerability, with code and documentation focused on the affected component.
 0n1con3/fluxer
FluxER - The bash script which installs and runs the Fluxion tool inside Termux. The wireless security auditing tool used to perform WPA/WPA2…
 xqi1337/poc-cve-2026-0073
CVE-2026-0073 - ADB Wireless Mutual Authentication Bypass PoC
 alwentiu/cve-2020-14292
Details of CVE-2020-14292
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…