
kr00ker
 akabe1/kr00ker
An experimental script PoC for Kr00k vulnerability (CVE-2019-15126)
encryption-decryption-toolsexploitationpenetration-testing+3
akabe1/kr00kerAn experimental script PoC for Kr00k vulnerability (CVE-2019-15126)
 hexway/r00kie-kr00kie
PoC exploit for the CVE-2019-15126 kr00k vulnerability
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 nickdaria/wyze-bulb-color-pwned
No-open firmware exploit for the Wyze WLPA19CV2 color bulb
 hayzamjs/blueborne-cve-2017-1000251
Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.
 d4rkcat/killosx
use the Apple CoreText exploit (CVE-2012-3716) and launch an AP to affect all devices within wifi range
 olav-st/cve-2017-1000250-poc
Proof of concept exploit script for CVE-2017-1000250. Written while researching for the essay in TTM4137 Wireless Security.
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 kh4sh3i/cve-2025-34152
Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…
 chertogun/cve-2020-27301-hostapd
Proof-of-concept exploit for CVE-2020-27301 in hostapd, enabling rogue access point creation to test and demonstrate the vulnerability in WPA2/WPA3…
 barghest-ngo/cve-2026-51376
Proof-of-concept exploit for BLE cache poisoning in Bitchat 1.15.0, demonstrating a man-in-the-middle attack that poisons the Bluetooth Low Energy…
 nanopathi/system_bt_aosp10_r33_cve-2021-0507
Exploit for CVE-2021-0507, a remote code execution vulnerability in Android's Bluetooth stack (system/bt). Provides proof-of-concept for the flaw.
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 embedi/ble_norton_core
Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…
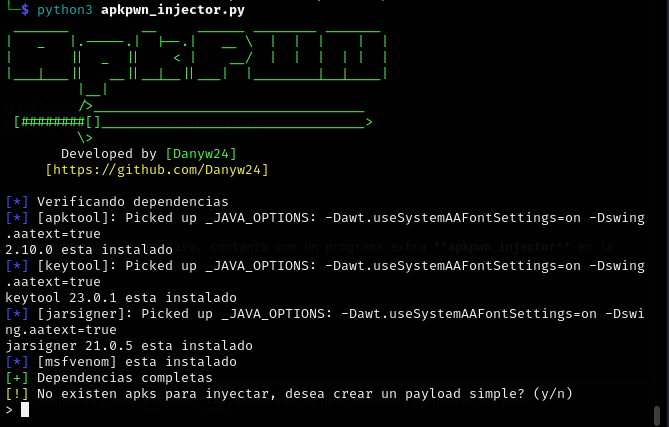 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 anonymouz4/apple-remote-crash-tool-cve-2018-4407
Crashes any macOS High Sierra or iOS 11 device that is on the same WiFi network
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability