

CVE-2020-11539
 the-girl-who-lived/cve-2020-11539
Improper Access Control in Tata Sonata Smartband
bluetooth-securityexploitationhardware-iot-security+3
the-girl-who-lived/cve-2020-11539Improper Access Control in Tata Sonata Smartband
 aprkr/cve-2023-48034
Weak encryption in Acer Wireless Keyboard SK-9662 allows attacker in physical proximity to both decrypt wireless keystrokes and inject wireless…

 jason996/maritime-security-paper
Comprehensive research on security vulnerabilities in autonomous maritime vessels and defense recommendations

 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 lnversed/cve-2020-10882
cve based on vulnerable cisco's Archer A7 routers
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 lixiang957/cve-2021-36630
Proof-of-concept exploit for CVE-2021-36630 targeting Ruckus SmartZone wireless controllers via UDP command injection on port 9001.
 yashodhanvivek/firebolt-wristphone-vulnerability
This repository is for Firebolt wristphone vulnerability for CVE ID CVE-2024-30656 suggested by MITRE. Mitre yet to confirm on ID
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss
 xchwarze/ar150-wifipineapple
Converting your AR150 to a Wifi Pineapple NANO
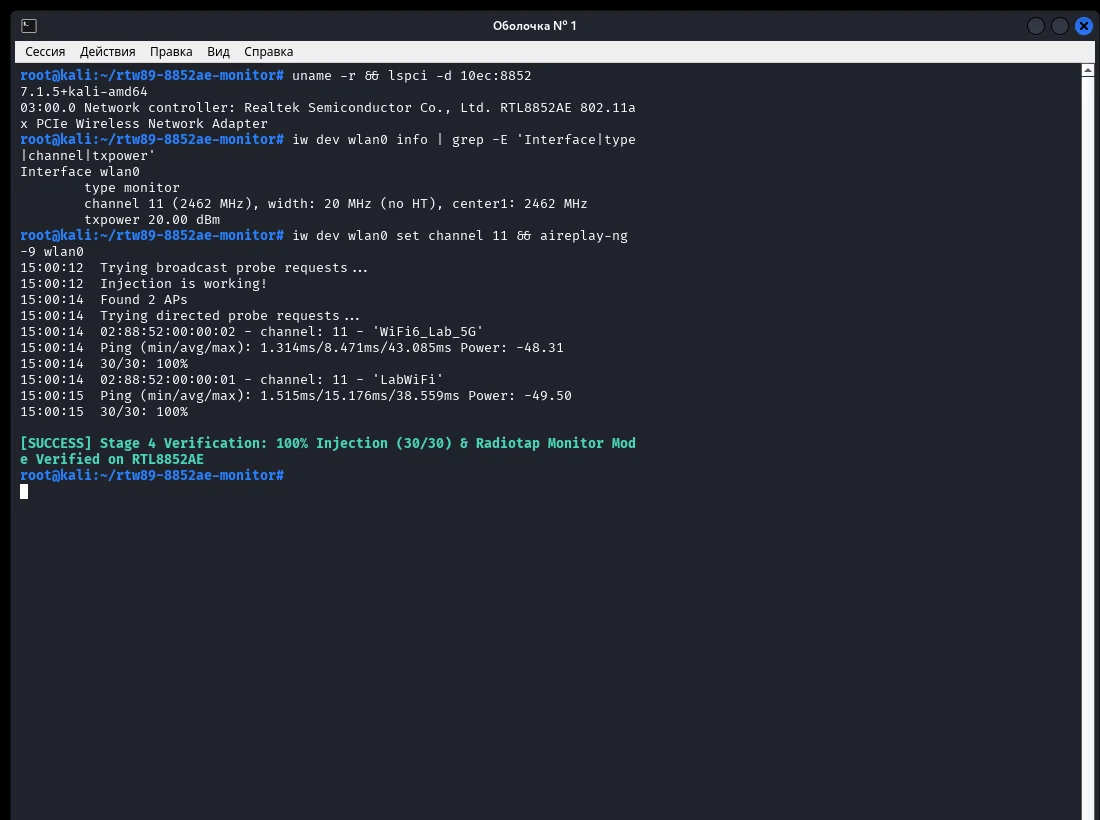 ph4ntom-rev/rtw89-monitor-injection
Realtek RTL8852AE / rtw89 Monitor Mode and Packet Injection (Raw TX) patch for Linux / Kali Linux
 permissionlesstech/bitchat-android
Decentralized, encrypted peer-to-peer messaging app over Bluetooth mesh networks. No internet, servers, or phone numbers required. Features X25519 +…
 spacehuhntech/esp8266_deauther
Affordable WiFi hacking platform for testing and learning
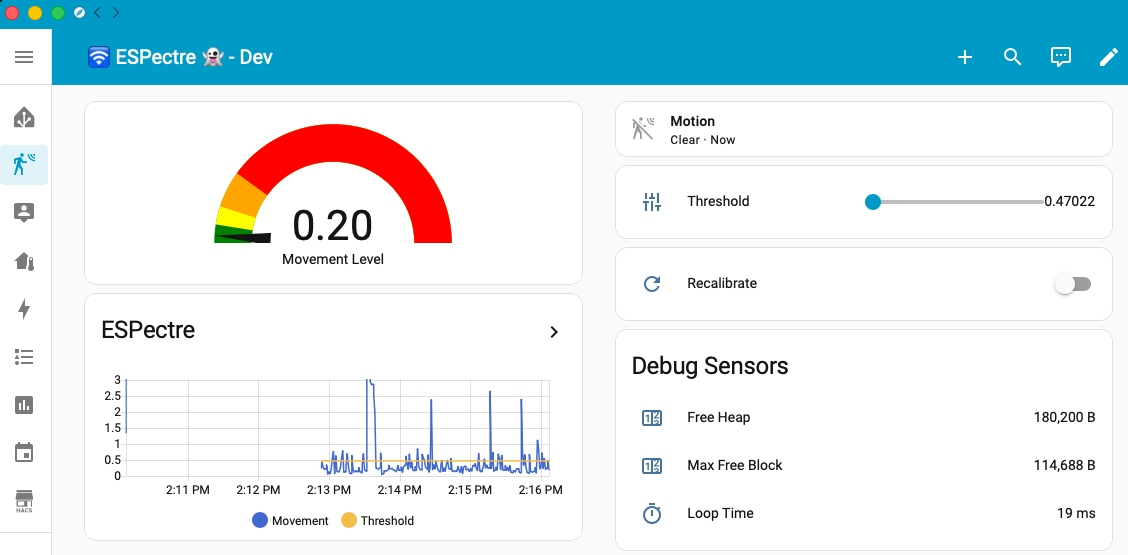 francescopace/espectre
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 v1s1t0r1sh3r3/airgeddon
This is a multi-use bash script for Linux systems to audit wireless networks.
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot