
trackem
 veteranop/trackem
Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
bluetooth-securityinformation-gatheringiot-security+6
4
veteranop/trackemPassive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 george0papasotiriou/cve-2026-21006-zigbee-light-link-factory-reset-exploit
Simulated Zigbee Light Link (ZLL) factory reset exploit for CVE-2026-21006, demonstrating unauthenticated TouchLink command injection that wipes…
 foxtrot/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.
 george0papasotiriou/cve-2026-11109-bluetooth-classic-knob-attack-key-negotiation-of-bluetooth-
Python simulation of the Bluetooth Classic KNOB attack, showing encryption key-size downgrade and brute-force decryption of intercepted Bluetooth…
 george0papasotiriou/cve-2026-11117-wpa2-4-way-handshake-reinstallation-krack-sim-
Python simulation of CVE-2026-11117 demonstrating WPA2 4-way handshake PTK reinstallation and nonce reuse to illustrate the KRACK attack.
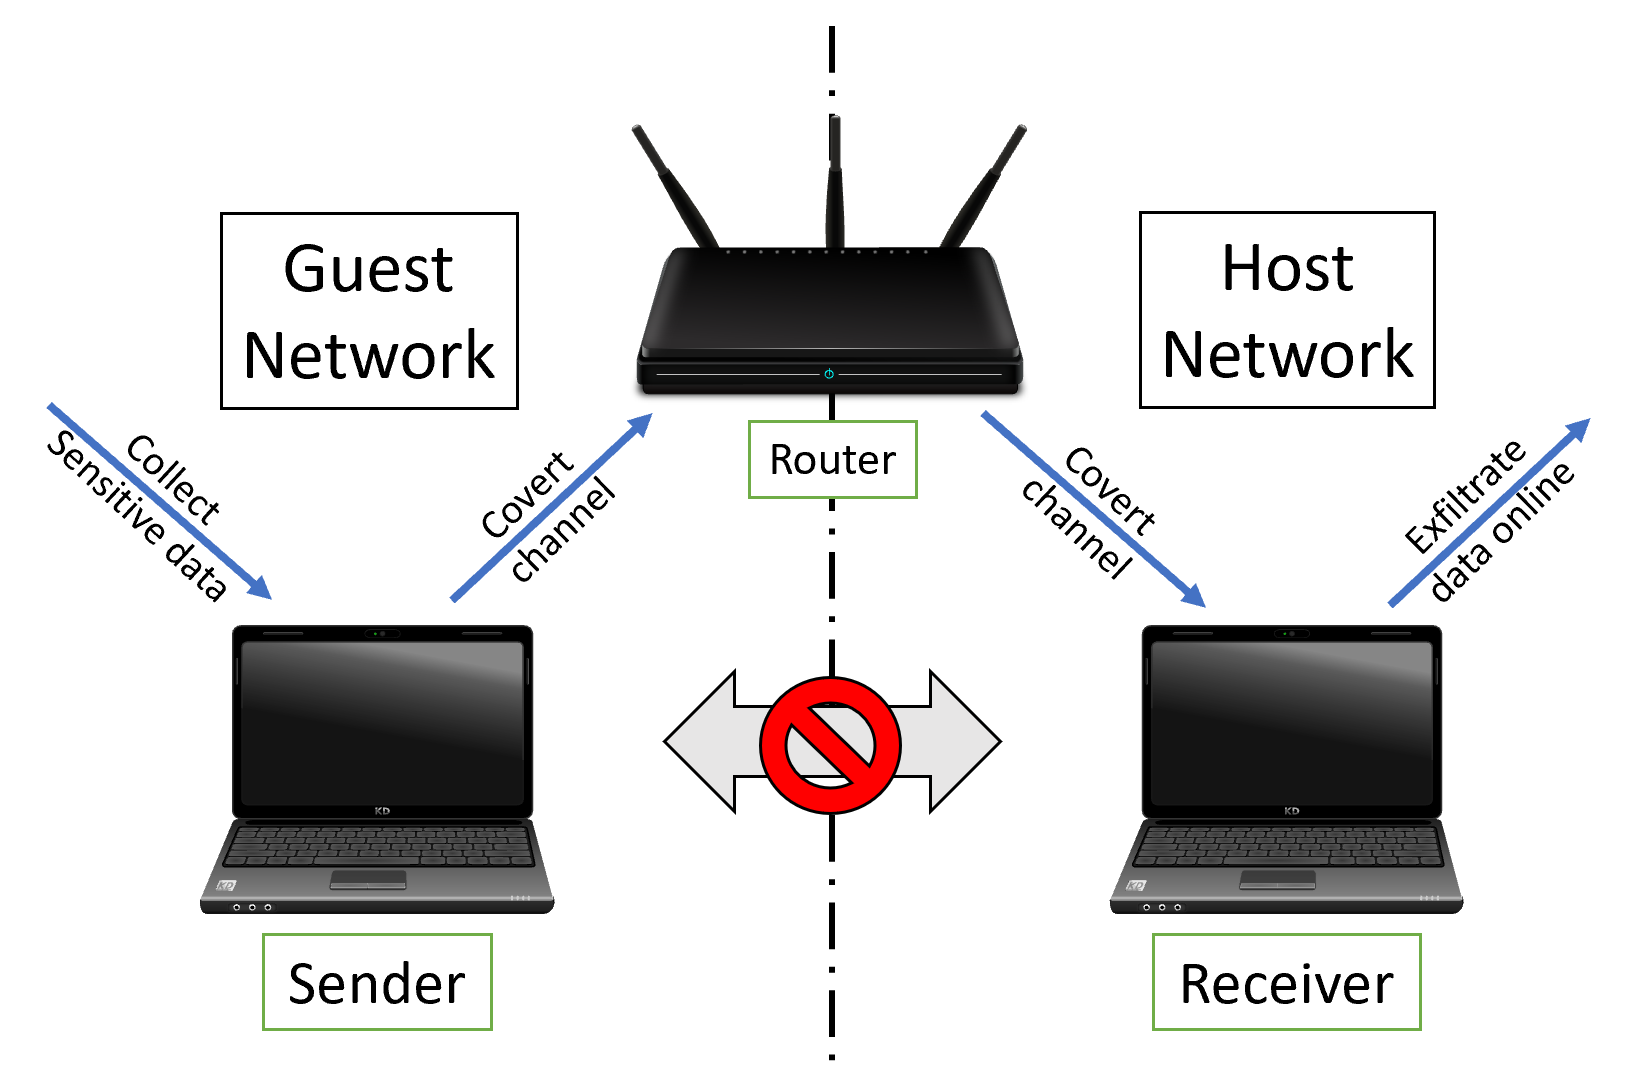 orensv/characterization-and-detection-of-cross-router-covert-channels
This repository includes the source code used in the "Characterization and Detection of Cross-Router Covert Channels" paper.
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 avishekdhakal/cve-2023-45866_exploits
Exploits Tested in Mi A2 Lite and Realme 2 pro
 ap425q/whisper-pair
Scans Bluetooth Low Energy devices for Fast Pair vulnerabilities (CVE-2025-36911), testing if accessories accept unencrypted Key-Based Pairing…
 kh4sh3i/cve-2025-34152
Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…
 magicbytes/magicarch
MagicArch is a comprehensive post-installation script built with Ansible, designed to transform a basic Arch Linux installation into a fully equipped…
 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…
 zvckster/cve-2025-63353
Multi-language PoC (Python · Go · JS · C) and technical documentation for CVE-2025-63353, a critical predictable-default-PSK vulnerability in…