
CVE-2023-33538
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
command-and-controleducationexploitation+5
11 year ago
explxx/cve-2023-33538Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 mastercode112/upgraded_bluebourne-cve-2017-0785-
upgraded of BlueBourne CVE-2017-0785 to python3
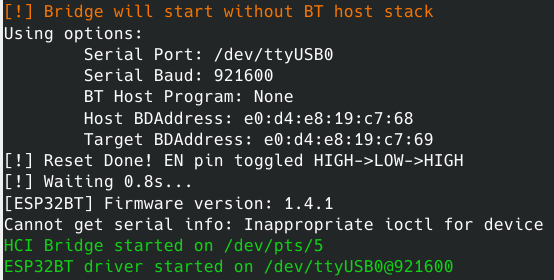 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
 josue87/airopy
Get clients and access points.
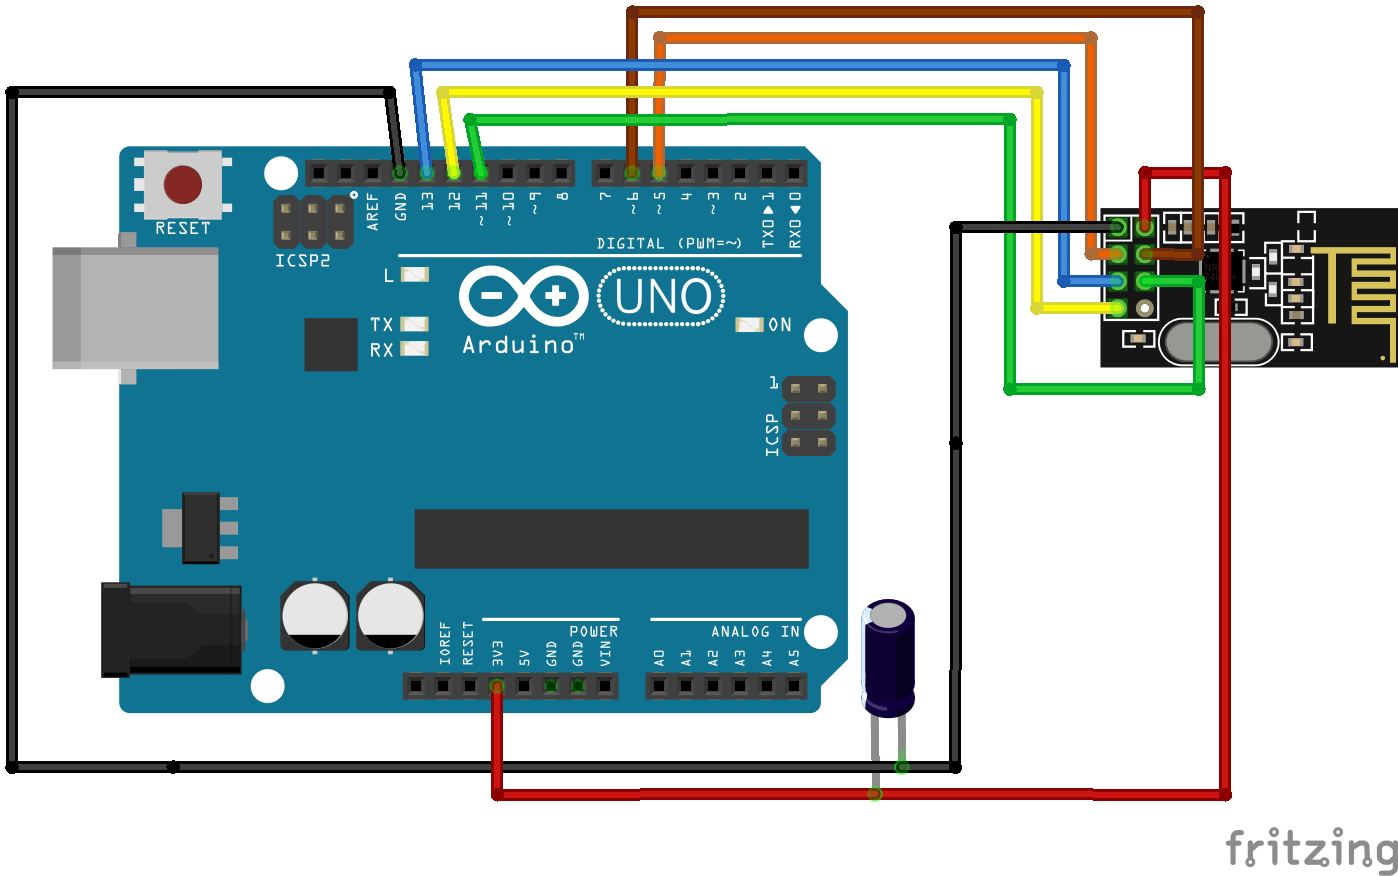 dnatividade/arduino_mousejack
Mousejack for Arduino UNO
 s0c5/remotepasswordwifi
Script in Ruby. Break Remote router wifi passwords.
 insecurityofthings/uc_mousejack
Mousejack for ATmega32u4
 silentghostx/ht-wps-breaker
HT-WPS Breaker (High Touch WPS Breaker)