
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
9 results
Whisper_Bully preview

Whisper_Bully

GitHubymsniper/whisper_bully

Three-stage Bluetooth BDADDR extraction, DoS & hijack on Fast Pair devices; unpatched primitives outside CVE-2025-36911 scope (no Ubertooth needed)
bluetooth-securityexploitationinformation-gathering+4
39
2 months ago
WPAxFuzz preview

WPAxFuzz

GitHubefchatz/wpaxfuzz

A full-featured open-source Wi-Fi fuzzer
exploitationfuzzingvulnerability-analysis+2
2153 months ago
fufu-sec preview

fufu-sec

GitHubkyllr-qwen/fufu-sec

Framework for Uninvited Frequency Usage
exploitationnetwork-securitypassword-attacks+4
104 months ago
wifi-deauth preview

wifi-deauth

GitHubflashnuke/wifi-deauth

A deauth attack that disconnects all devices from the target wifi network (2.4Ghz & 5Ghz), WPA3 also supported (PMF not tested)

penetration-testingwi-fi-auditingwireless-security
9167 months ago
CVE-2023-52709-PoC preview

CVE-2023-52709-PoC

GitHubkevinmitchell-oswp-cissp/cve-2023-52709-poc

PoC for 2023-52709 - TI Bluetooth stack can fail to generate a resolvable Random Private Address (RPA) leading to DoS for already bonded peer devices.
bluetooth-securityexploitationpenetration-testing+2
52 years ago
CVE-2024-42861 preview

CVE-2024-42861

GitHubqiupy123/cve-2024-42861

the

exploitationiot-securitynetwork-security+2
2 years ago
CVE-2023-33105-Transient-DOS-in-WLAN-Host-and-Firmware preview

CVE-2023-33105-Transient-DOS-in-WLAN-Host-and-Firmware

GitHubd3adp3nguin/cve-2023-33105-transient-dos-in-wlan-host-and-firmware

This repository contains the exploit code for CVE-2023-33105, a vulnerability identified in Qualcomm devices. The exploit leverages authentication…
exploitationpenetration-testingred-teaming+2
32 years ago
Blueborne-CVE-2017-1000251 preview

Blueborne-CVE-2017-1000251

GitHubhayzamjs/blueborne-cve-2017-1000251

Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.
bluetooth-securityexploitationpenetration-testing+2
193 years ago
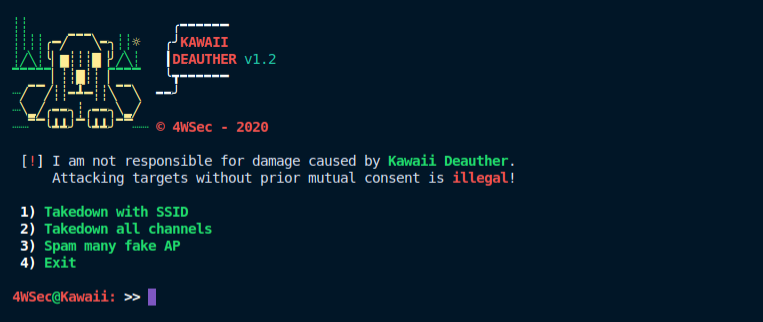
KawaiiDeauther preview
Archived

KawaiiDeauther

GitHubaryanrtm/kawaiideauther

Jam all wifi clients/routers.

network-securitypenetration-testingred-teaming+2
6666 years ago