
Claude-Red
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
ai-securitycurated-resourceseducation+8
7.3k
snailsploit/claude-redCurated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
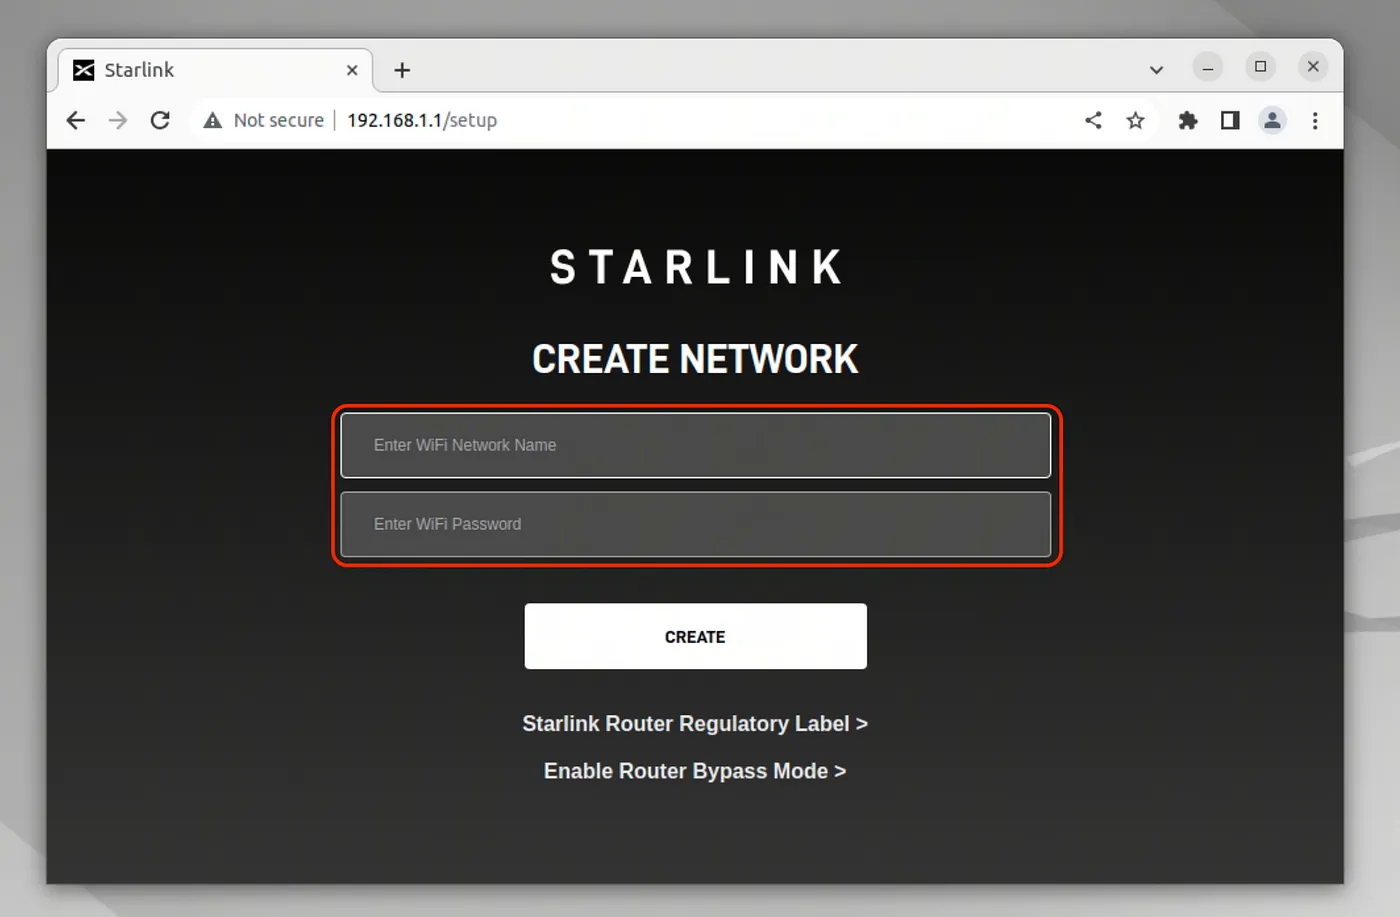 yoshida-git-ai/spacex-starlink-router-gen-2-xss
CVE-2023-49965 | SpaceX / Starlink Router Gen 2 XSS
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 lachlan2k/cve-2023-35803
PoC exploit for CVE-2023-35803 unauthenticated buffer overflow in Aerohive HiveOS/Extreme Networks IQ Engine, enabling remote code execution on…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 efchatz/easy-exploits
Curated collection of proof-of-concept exploits for 16 CVEs targeting web applications (ASUS, D-Link, Netgear, TP-Link, Xiaomi) and Wi-Fi WPA3-SAE,…
 ultimatehg/cve-2025-52689-poc
Proof-of-concept exploit for CVE-2025-52689, an authentication bypass in Alcatel-Lucent Enterprise AP1361D Wi-Fi access points, enabling session…
 elvira-alec/fracture
FragAttacks WiFi penetration framework — CVE-2020-24586/87/88
 bttea/cve-2018-14714-rce-exploit
ASUS wifi router RCE vulnerability
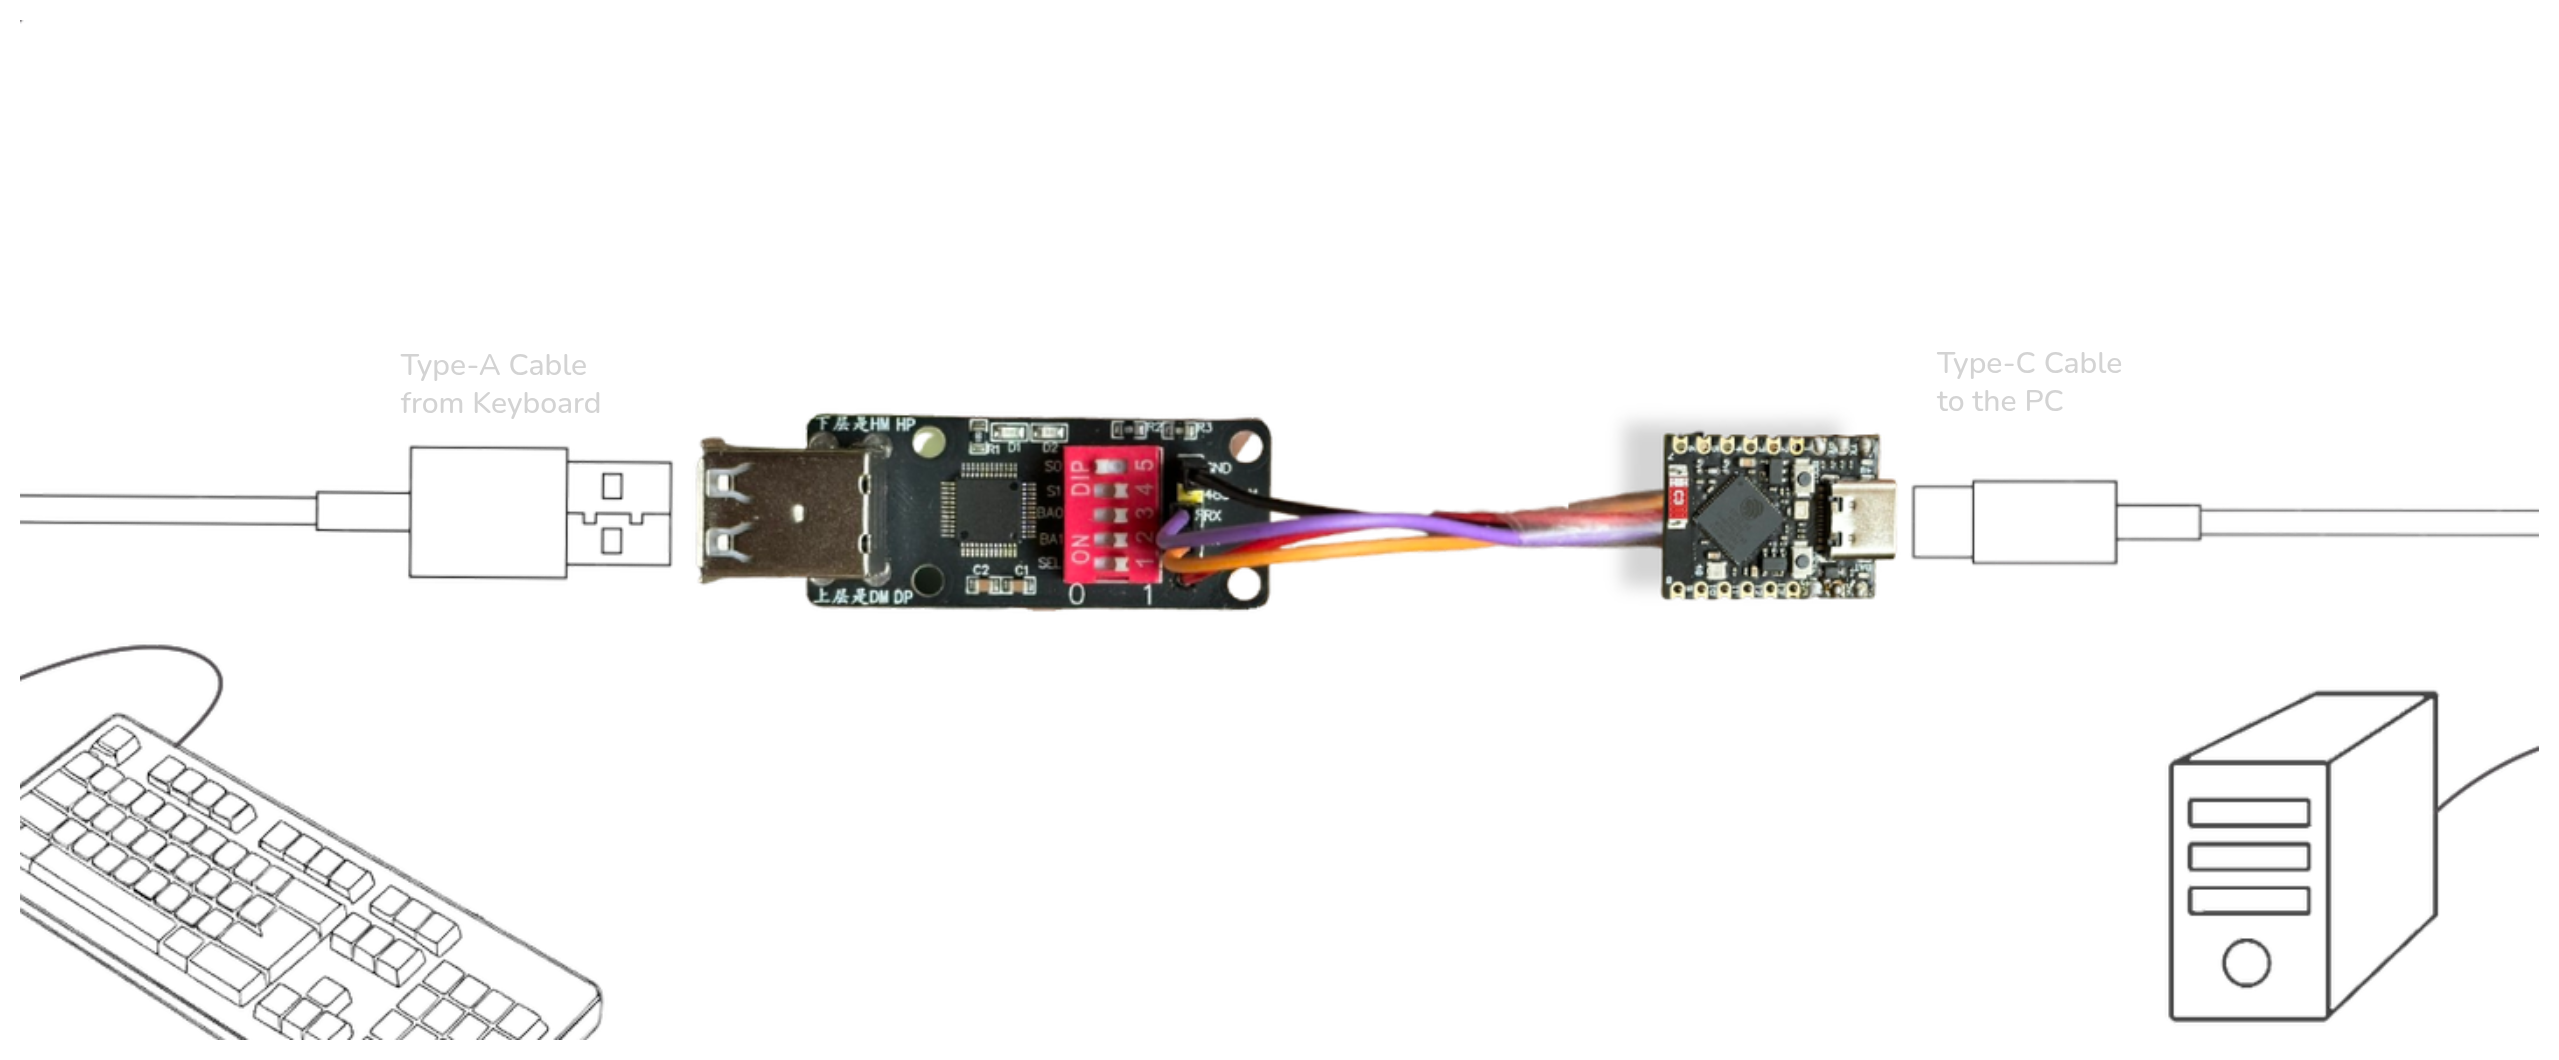 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 manisso/fsociety
fsociety Hacking Tools Pack – A Penetration Testing Framework
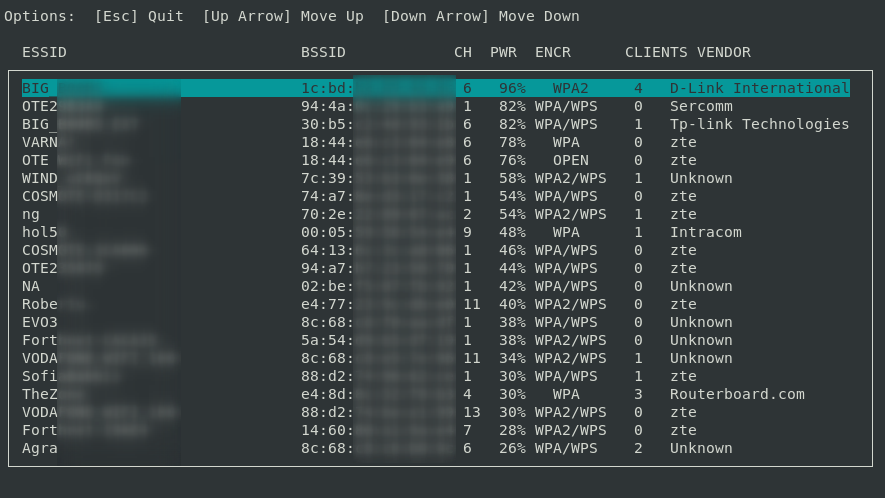 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 entropy1337/infernal-twin
wireless hacking - This is automated wireless hacking tool
 sobri3195/pegasus-neo
PEGASUS-NEO is a comprehensive penetration testing framework designed for security professionals and ethical hackers. It combines multiple security…