
CVE-2021-1965
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
exploitationmobile-securitypenetration-testing+2
3
sqrtrev/cve-2021-1965Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
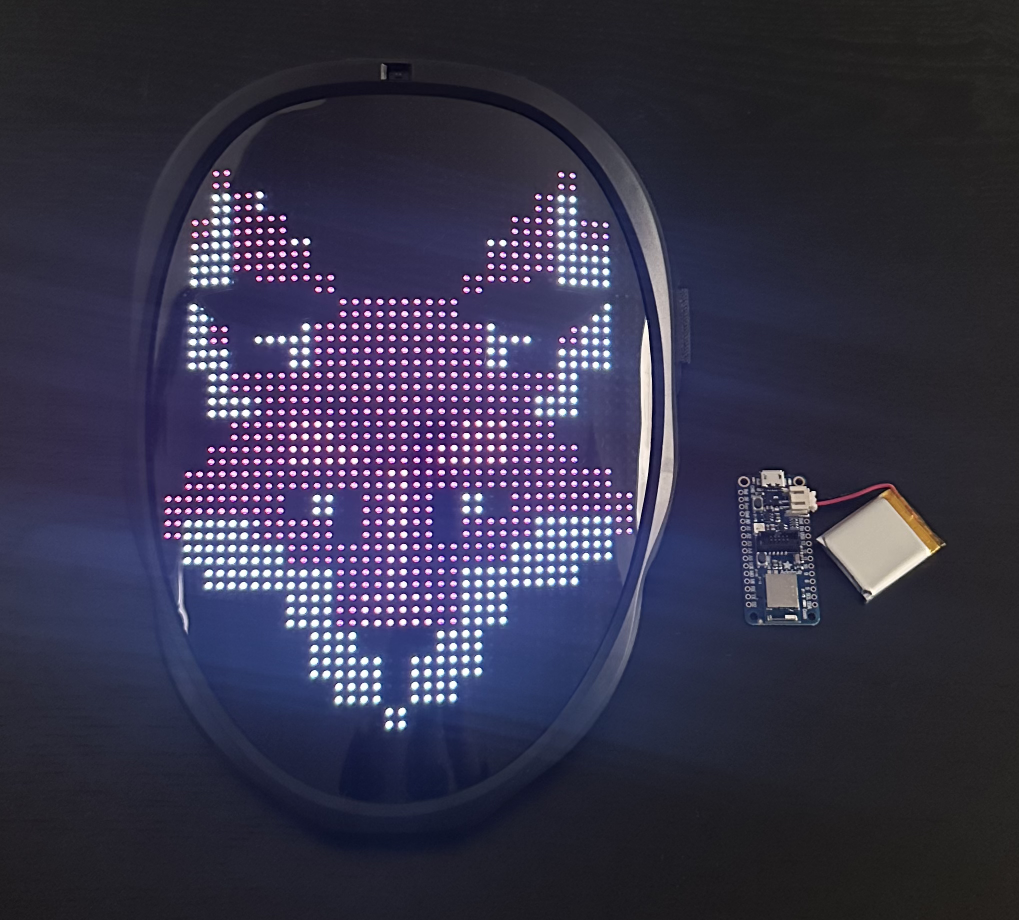 bishopfox/shining-mask
BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…
 nanopathi/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
 eonraider/violent-python3
Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 lachlan2k/cve-2023-35803
PoC exploit for CVE-2023-35803 unauthenticated buffer overflow in Aerohive HiveOS/Extreme Networks IQ Engine, enabling remote code execution on…
 lodi-g/cve-2019-13361
Smanos W100 1.0.0 devices have Insecure Permissions, exploitable by an attacker on the same Wi-Fi network.
 pentestfunctions/blueducky
🚨 CVE-2023-45866 - BlueDucky Implementation (Using DuckyScript) 🔓 Unauthenticated Peering Leading to Code Execution (Using HID Keyboard)
 phuchaudeveloper/badblue
CVE-2024-21306 BadBlue implementation (Using DuckyScript)
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 kh4sh3i/cve-2025-34152
Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…
