
mousejack
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
exploitationfirmware-analysishardware-iot-security+3
1.4k
bastilleresearch/mousejackResearch tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 sgxgsx/bluetoolkit
Modular Bluetooth Classic (BR/EDR) vulnerability testing framework with reconnaissance, exploit modules for 43 public attacks/CVEs, and structured…
 msdmehdipour/meshtastic-cve-2025-52464-poc
Software-only proof of concept for CVE-2025-52464 in Meshtastic Direct Messages
 george0papasotiriou/cve-2026-22017-firmware-update-via-ble-without-authentication
Simulated BLE peripheral exposing an unauthenticated GATT firmware-update characteristic; demonstrates critical CVE-2026-22017 device-takeover…
 nanopathi/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
 yoshida-git-ai/spacex-starlink-router-gen-2-xss
CVE-2023-49965 | SpaceX / Starlink Router Gen 2 XSS
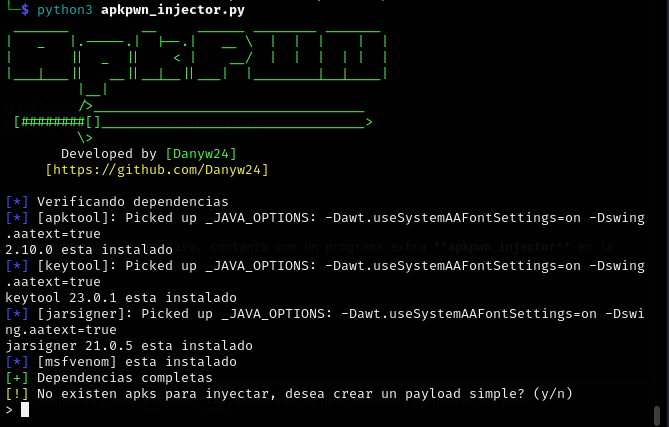 danyw24/bluexploit
Exploit basado en vulnerabilidades criticas Bluetooth (CVE-2023-45866, CVE-2024-21306)
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
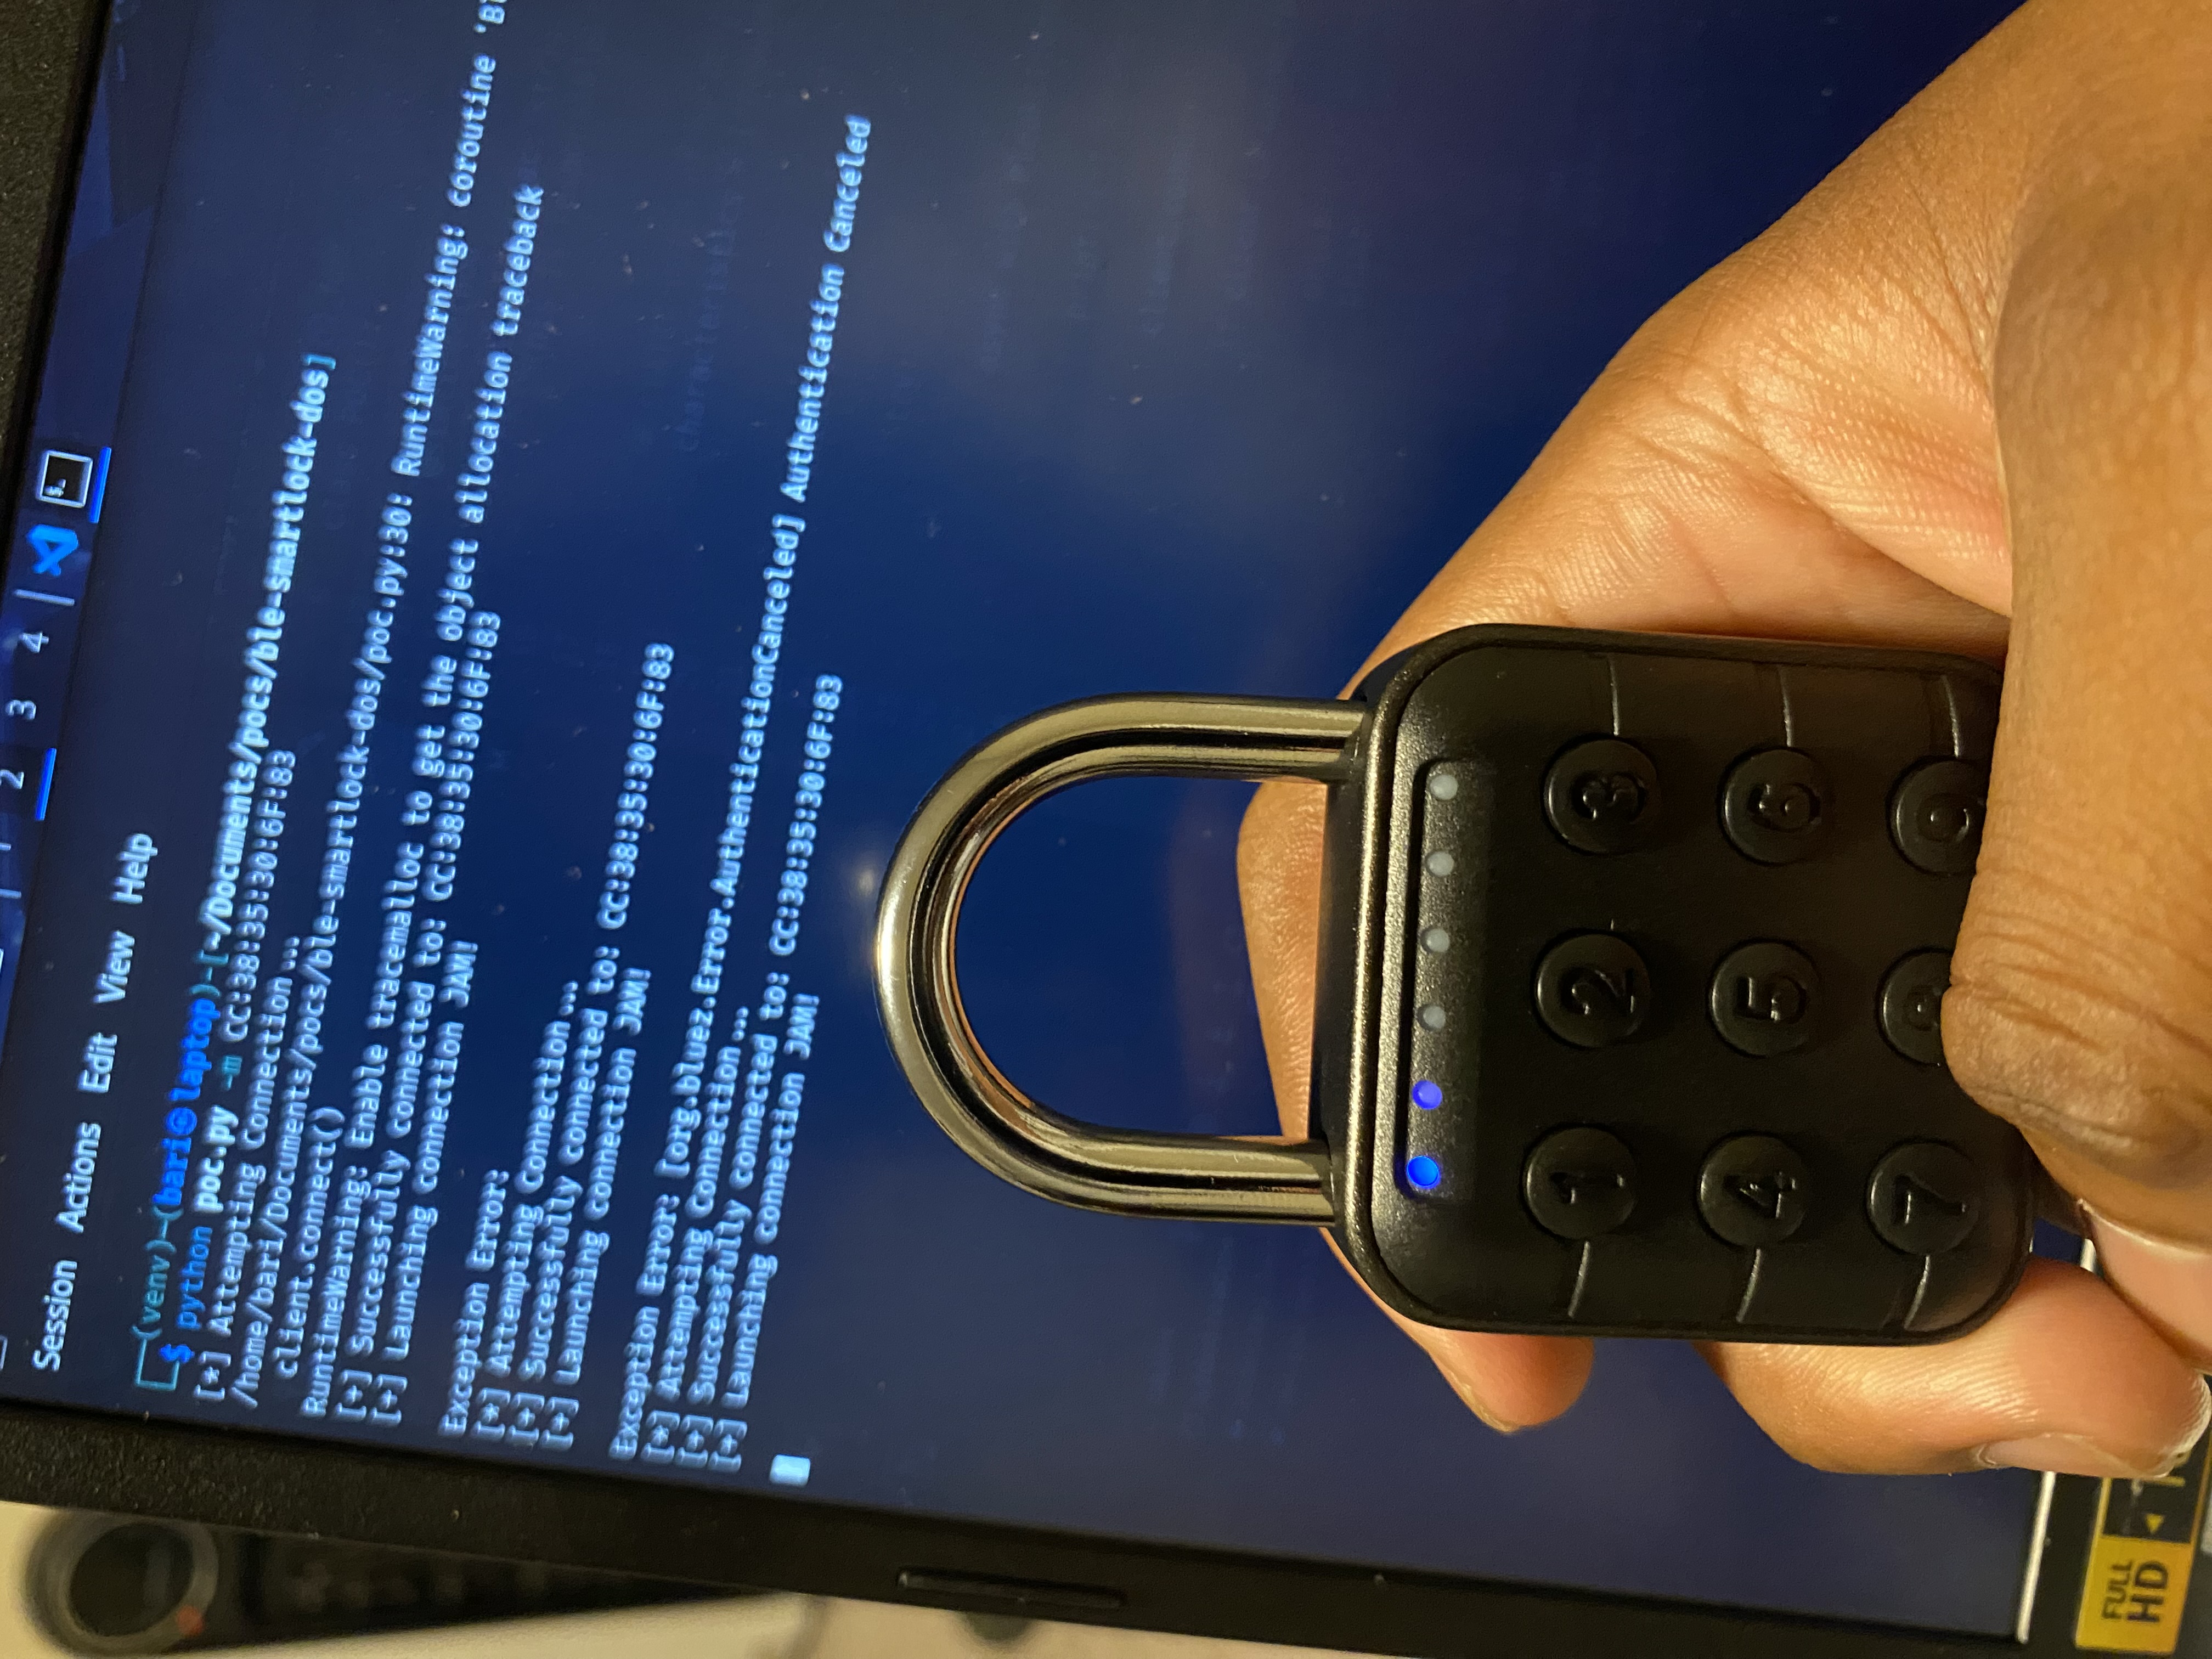 nsm-barii/cve-2025-15474
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …
 penthertz/cve-2025-36911-exploit
Exploit of the CVE-2025-36911 vulnerability in Python for testing our own equipment
 pivotchip/frostedfastpair
WhisperPair (CVE-2025-36911) POC for ESP32 device
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 hanianis/cve-2025-63353
A vulnerability in fiberhome GPON ONU HG6145F1 RP4423 allows the device's factory default Wi-Fi password (WPA/WPA2 pre-shared key) to be predicted…
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability