
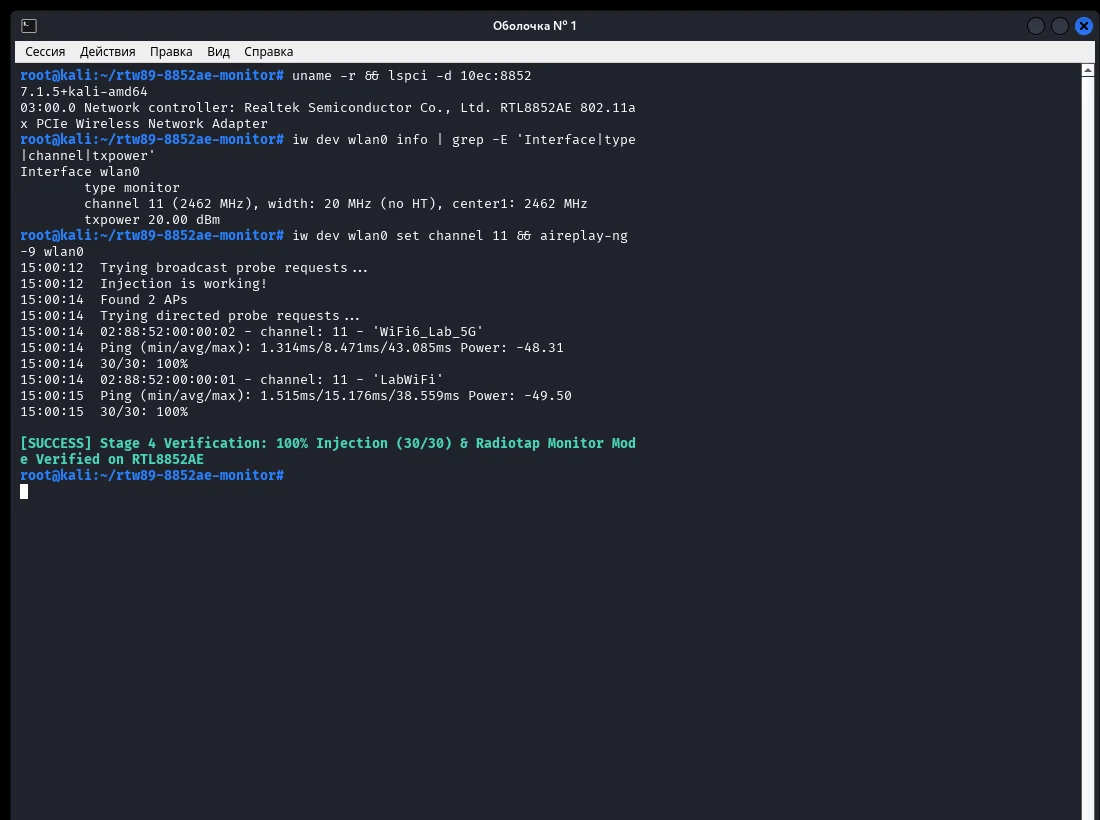
rtw89-monitor-injection
 ph4ntom-rev/rtw89-monitor-injection
Realtek RTL8852AE / rtw89 Monitor Mode and Packet Injection (Raw TX) patch for Linux / Kali Linux
hardware-securitynetwork-securitypacket-sniffing-analysis+4
2
ph4ntom-rev/rtw89-monitor-injectionRealtek RTL8852AE / rtw89 Monitor Mode and Packet Injection (Raw TX) patch for Linux / Kali Linux
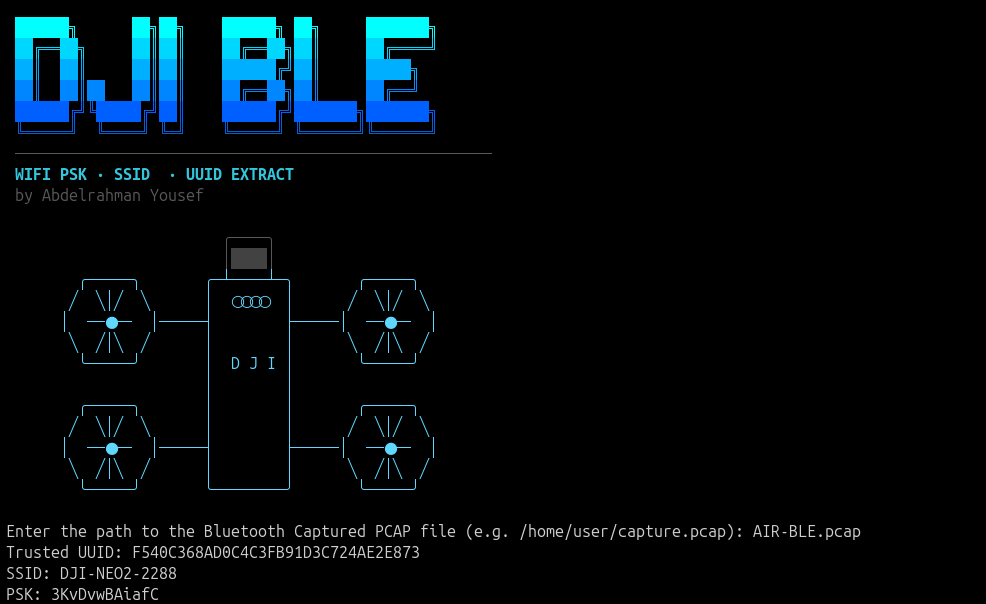 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 c2a2-at-florida-atlantic-university/gr-physec
GNU Radio module for physical layer security using deep learning channel fingerprinting, feature quantization, and SHA3-512 key generation from SDR…
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
 nfc-tools/mfcuk
Recovers cryptographic keys from MiFare Classic RFID cards using DarkSide and nested-auth attacks for security testing of NFC/RFID systems.
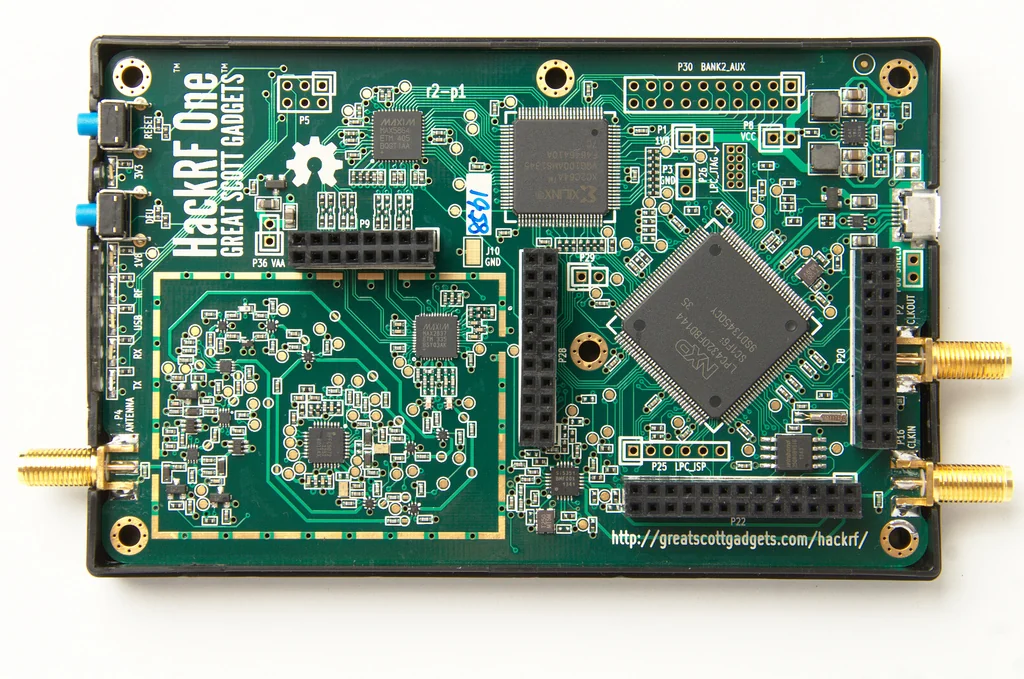 greatscottgadgets/hackrf
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 kimocoder/android_kernel_oneplus_avicii
OnePlus Nord (avicii) NeverSettle Kernel Source
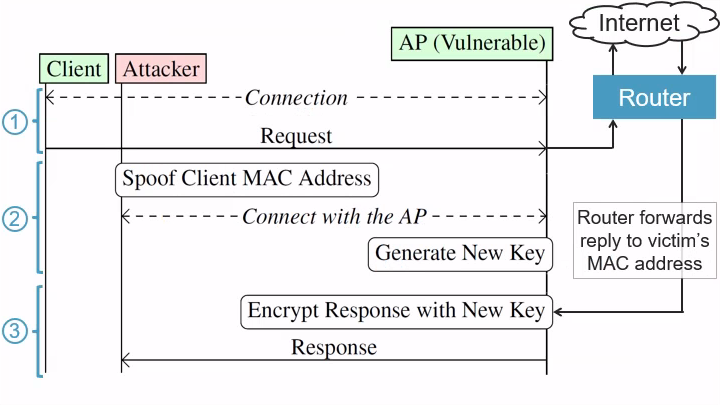 vanhoefm/macstealer
MacStealer: Wi-Fi Client Isolation Bypass
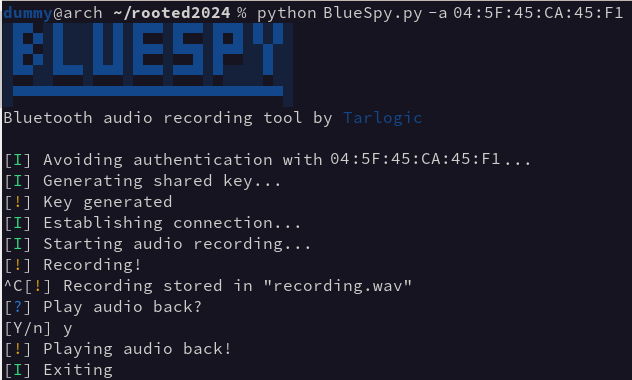 tarlogicsecurity/bluespy
PoC to record audio from a Bluetooth device
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
 catatonicprime/tospovirus
A WiFi Pineapple infecting worm.
 alt3kx/airdecloak-ng
My Aircrack-ng contribution with Thomas d'Otreppe
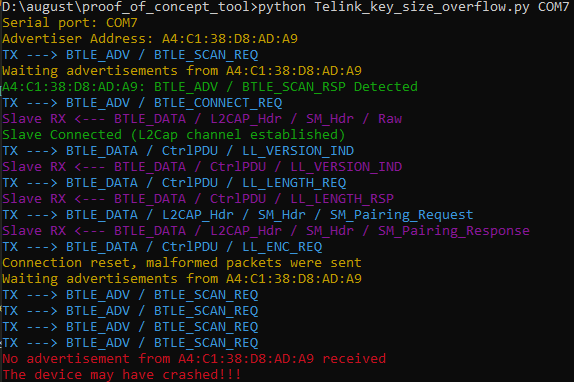 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.

 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.