
radioguard
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
android-securityanomaly-detectiondefensive-tools+7
pushkarreddyy/radioguardZero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 infobyte/pyrmax
Decoder/encoder for Ubiquiti AirMAX wireless protocol frames; parse pcap/live captures, discover devices, scan for vulnerable firmware, craft…
 v33ru/awesome-connected-things-sec
A Curated list of Security Resources for all connected things
 antoinet/obike
Reverse engineering of the oBike protocol communication (BLE and HTTP)
 nccgroup/blesuite
BLESuite is a Python package that provides an easier way to test Bluetooth Low Energy (BLE) device
 nccgroup/nobex
nOBEX allows emulating the PBAP, MAP, and HFP profiles to test vehicle infotainment systems and similar devices using these profiles
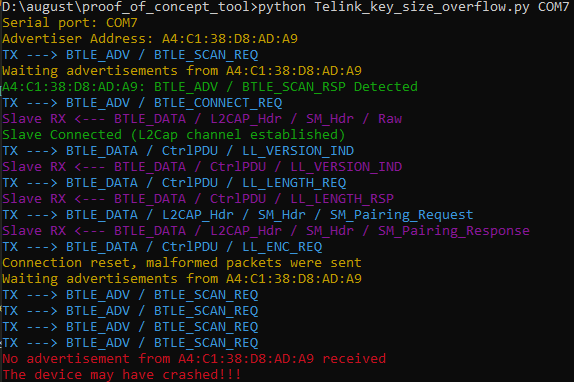 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 kamorin/dhcpig
DHCP exhaustion script written in python using scapy network library
 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.
 w00t3k/awesome-cellular-hacking
Awesome-Cellular-Hacking
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 nomis/eero-zero-length-ipv6-options-header-dos
eeroOS Ethernet Interface Denial of Service Vulnerability (CVE-2023-5324)
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32