
CVE-2021-1965
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
exploitationmobile-securitypenetration-testing+2
3
sqrtrev/cve-2021-1965Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
 francozappa/bluffs
Toolkit for testing Bluetooth session establishment against forward and future secrecy attacks, using firmware patching, PCAP analysis, and automated…
 flipperdevices/flipperzero-firmware
Flipper Zero firmware source code
 ebux/cable-modems
Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…
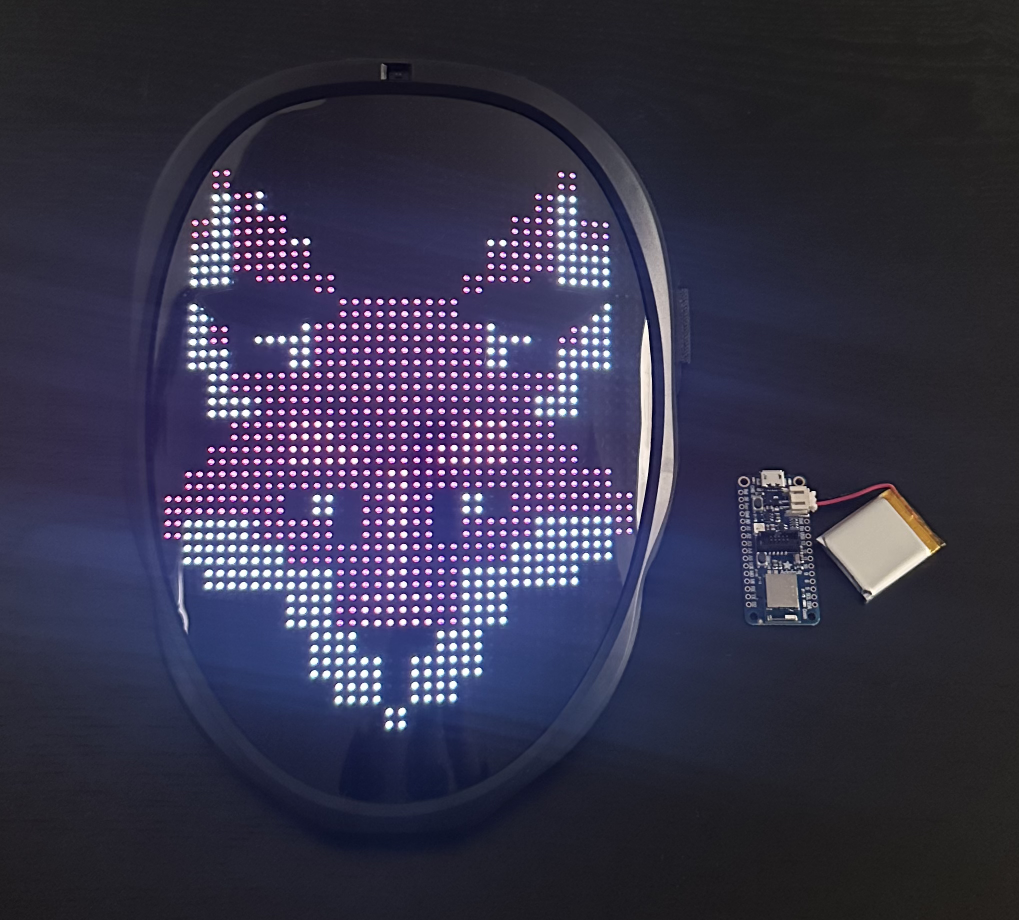 bishopfox/shining-mask
BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…
 nanopathi/packages_wpa_supplicant8_cve-2021-0326
Source code of wpa_supplicant and hostapd, focused on CVE-2021-0326 vulnerability for analysis, testing, and understanding of Wi-Fi security flaws.
 nanopathi/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…
 nanopathi/system_bt_aosp10_r33_cve-2021-0435
Android Bluetooth stack (AOSP 10 r33) with fix for CVE-2021-0435, addressing remote code execution in Bluetooth pairing.
 nanopathi/system_bt_aosp10_r33_cve-2021-0507
Exploit for CVE-2021-0507, a remote code execution vulnerability in Android's Bluetooth stack (system/bt). Provides proof-of-concept for the flaw.
 nanopathi/system_bt_aosp10_r33_cve-2021-0522
Android Bluetooth stack (system/bt) source code including patch for CVE-2021-0522 privilege escalation vulnerability.
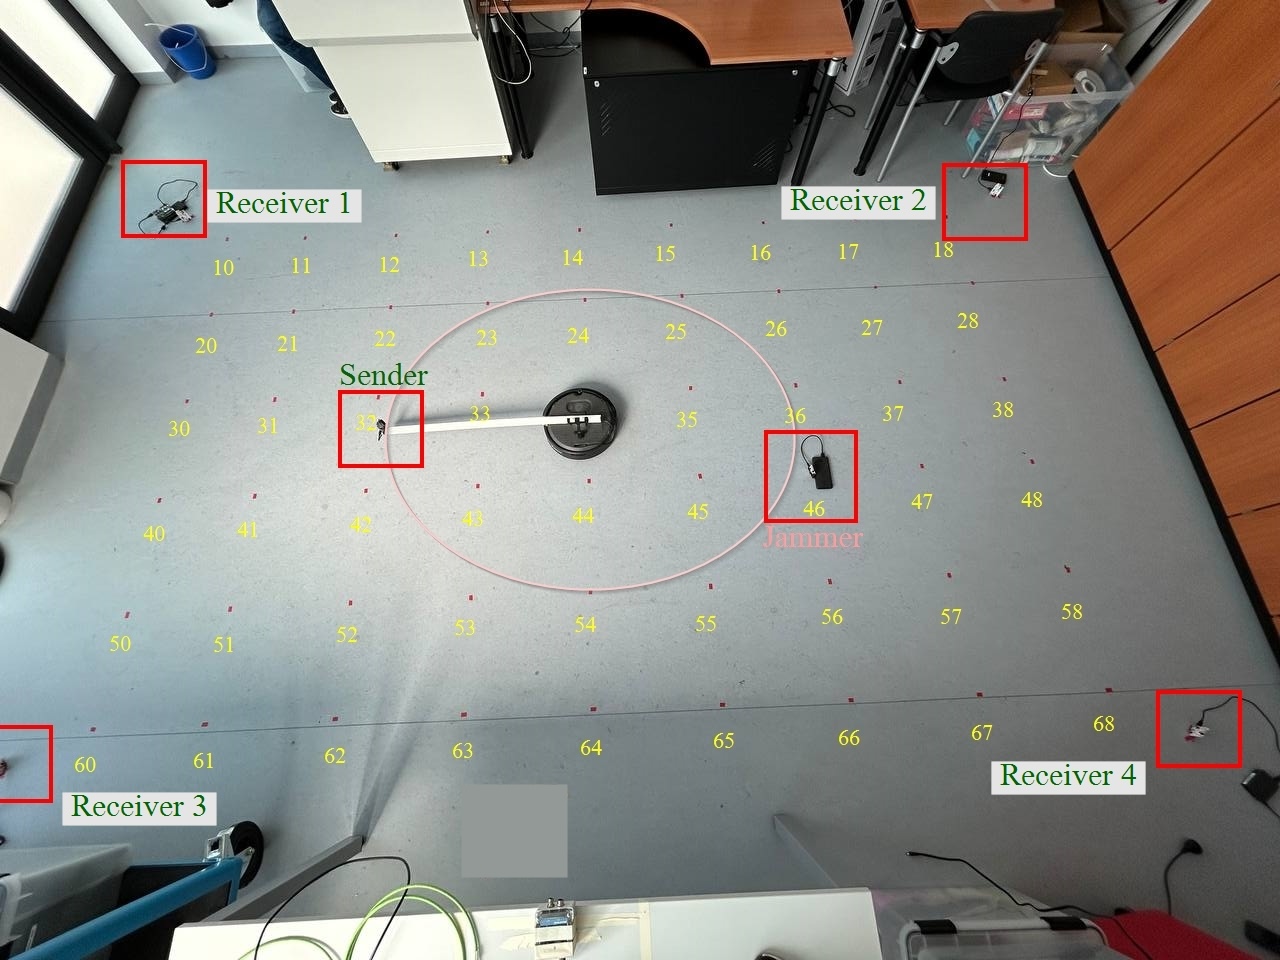 afbf4c8996f/jammer-loc
Implements machine and deep learning methods for indoor UWB jammer localization, including hyperparameter optimization, classification, and…
 sensepost/snoopy-ng
Snoopy v2.0 - modular digital terrestrial tracking framework
 eonraider/violent-python3
Source code for the book "Violent Python" by TJ O'Connor. The code has been fully converted to Python 3, reformatted to comply with PEP8 standards…
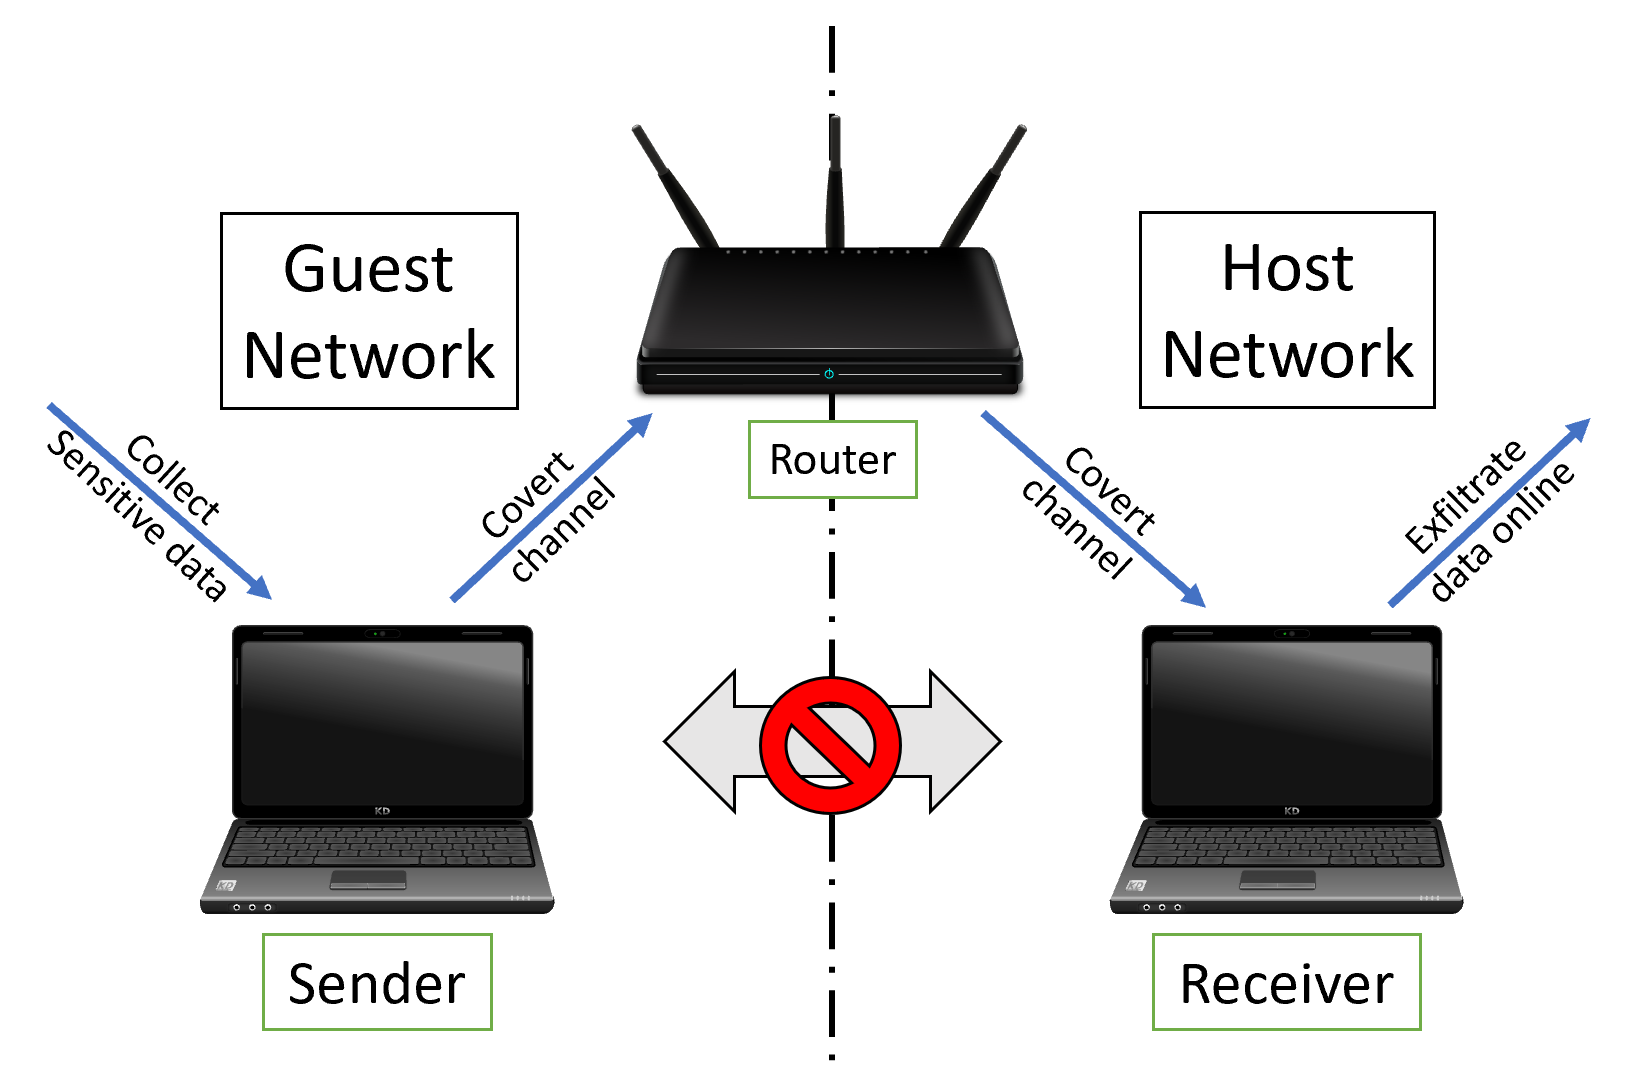 orensv/characterization-and-detection-of-cross-router-covert-channels
This repository includes the source code used in the "Characterization and Detection of Cross-Router Covert Channels" paper.
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 xen0bit/fwbt
Proof of Concept code for interaction with Firewalla via Bluetooth Low-Energy and exploitation of CVE-2024-40892 / CVE-2024-40893