
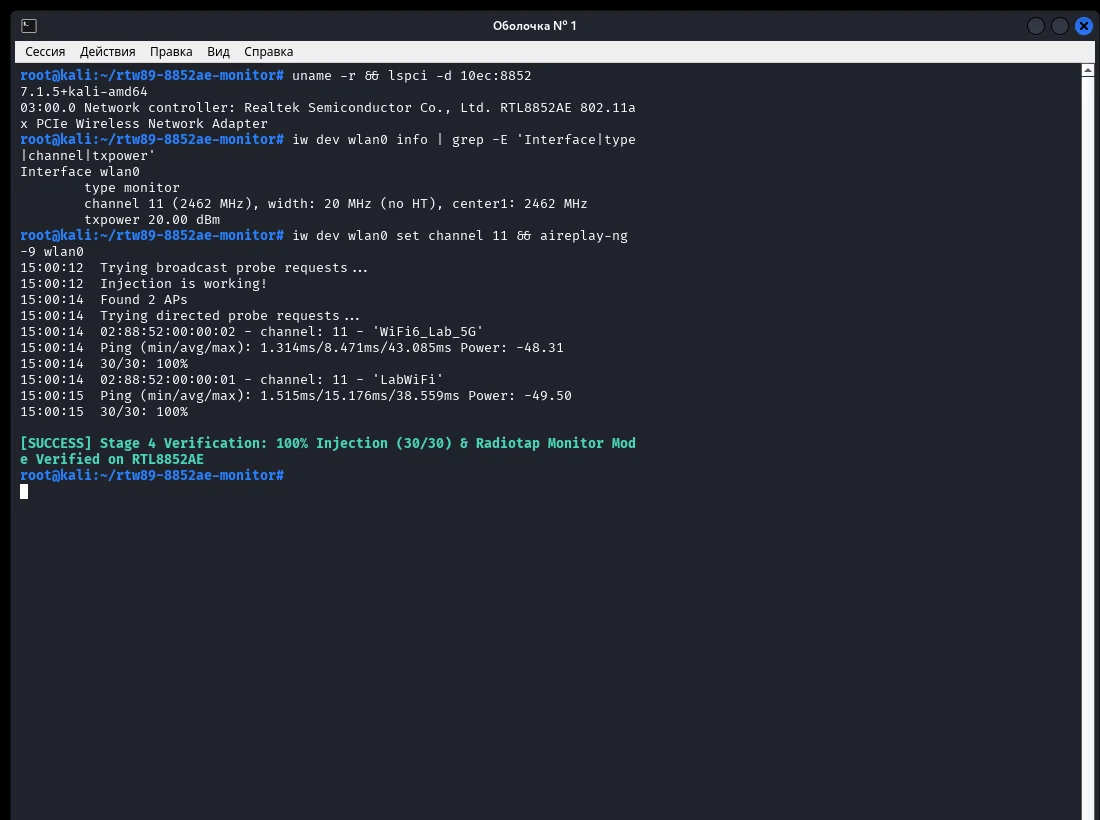
rtw89-monitor-injection
 ph4ntom-rev/rtw89-monitor-injection
Realtek RTL8852AE / rtw89 Monitor Mode and Packet Injection (Raw TX) patch for Linux / Kali Linux
hardware-securitynetwork-securitypacket-sniffing-analysis+4
2
ph4ntom-rev/rtw89-monitor-injectionRealtek RTL8852AE / rtw89 Monitor Mode and Packet Injection (Raw TX) patch for Linux / Kali Linux
 fengguan/arpcut
Rooted Android app that scans LAN devices and cuts or restores their network access via ARP spoofing, with OUI vendor lookup, whitelist, and…
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 phantom-brigade1/wifisting
GTK4 and CLI wireless security toolkit with 57 standalone modules for Wi-Fi, Bluetooth, 802.15.4, SDR/RF, NFC and router-side or network MITM testing…
 yslxotwod/imsisting
GTK4 and CLI cellular security toolkit with 57 modules for 2G GSM, 3G UMTS, 4G LTE and 5G NR air interface, core network, SIM identity, RF tracking,…
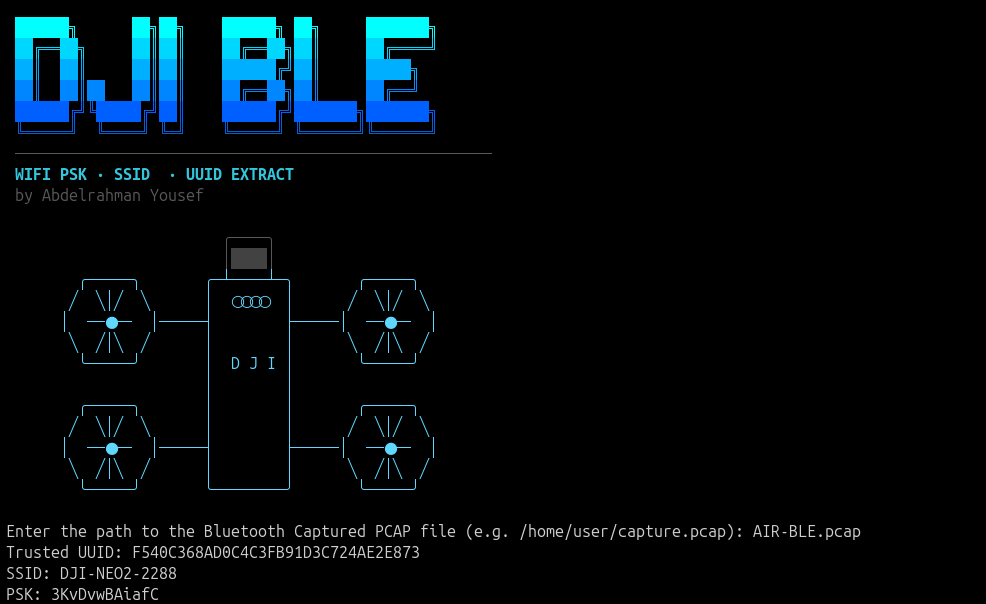 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 c2a2-at-florida-atlantic-university/gr-physec
GNU Radio module for physical layer security using deep learning channel fingerprinting, feature quantization, and SHA3-512 key generation from SDR…
 barghest-ngo/cve-2026-51376
Proof-of-concept exploit for BLE cache poisoning in Bitchat 1.15.0, demonstrating a man-in-the-middle attack that poisons the Bluetooth Low Energy…
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 v3ilsm1th/cve-2024-53027-wip
Proof-of-concept for CVE-2024-53027, a Wi-Fi beacon Country IE denial-of-service vulnerability affecting Qualcomm WLAN chipsets. Includes educational…
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…
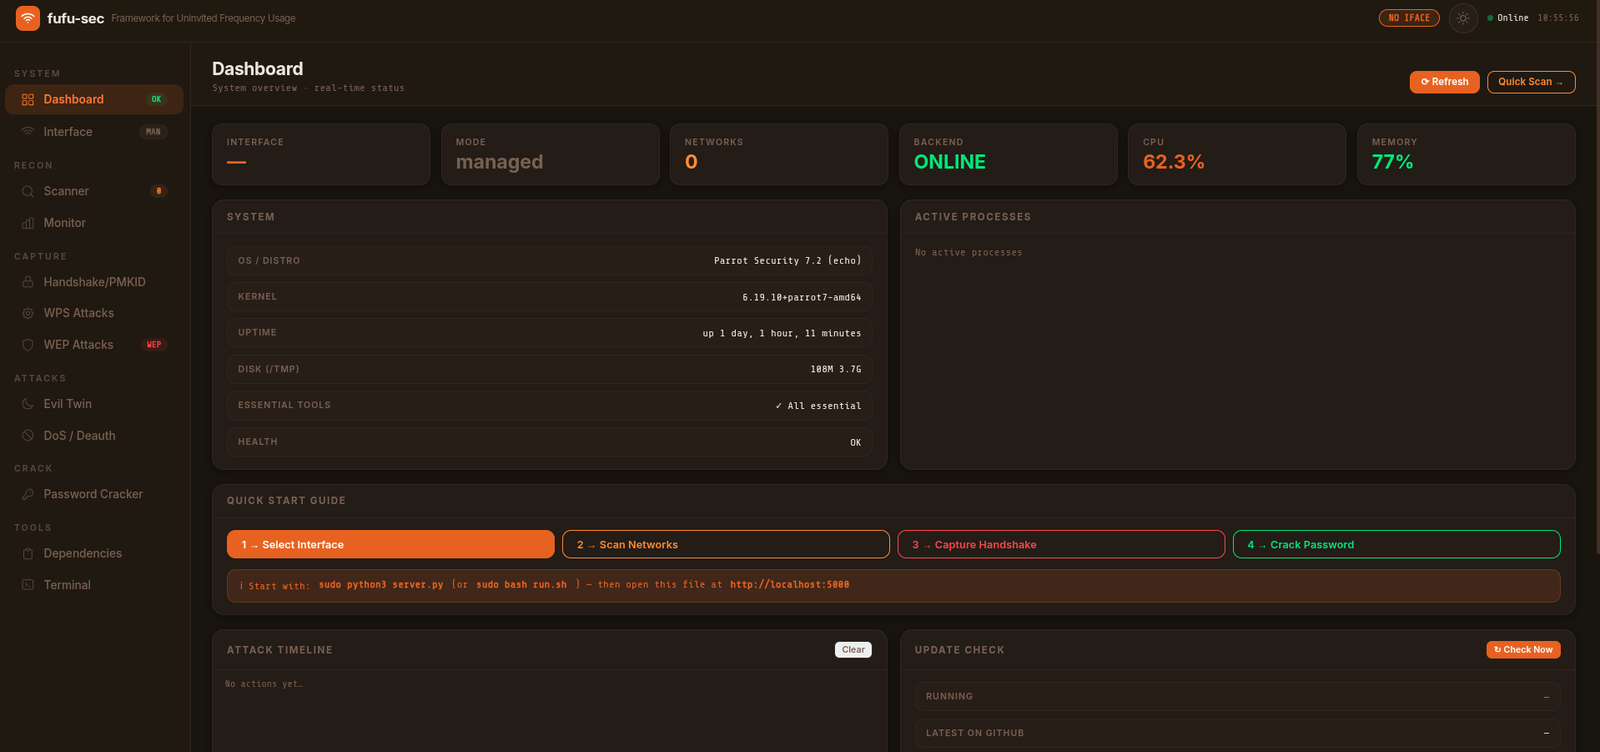 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
 applied-risk/loracrack
LoRaWAN session cracker - A PoC for exploiting weak or shared Application Keys
 sqrtrev/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a WiFi zero-click RCE in Android's MBSSID parsing, causing buffer overflow and device reboot.
 foxtrot/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.
 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 eason-zz/bluetoothducky
Exploit implementation for CVE-2023-45866 enabling unauthenticated Bluetooth keyboard injection using DuckyScript payloads on Raspberry Pi.