

kitsune
 bitplugg/kitsune
🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install
exploit-frameworksnetwork-mappingpassword-attacks+8
bitplugg/kitsune🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install
 ilias1988/hacking-cheatsheets
A comprehensive collection of penetration testing cheatsheets, guides, and tools.
 codingranjith/hackingtoolkit
ALL IN ONE Hacking Tool For Hackers, Penetration Tester and Cybersecurity. New Version Beginner to Advanced Tool. This Tool is made for educational…
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 agampreet-singh/redroot
RedRoot is a Python-based, CLI-driven offensive security framework that brings essential red teaming tools into one unified terminal environment.…
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 lucasvanhaaren/cve-2026-22226
Proof of Concept for the CVE-2026-22226
 yoshida-git-ai/spacex-starlink-router-gen-2-xss
CVE-2023-49965 | SpaceX / Starlink Router Gen 2 XSS
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
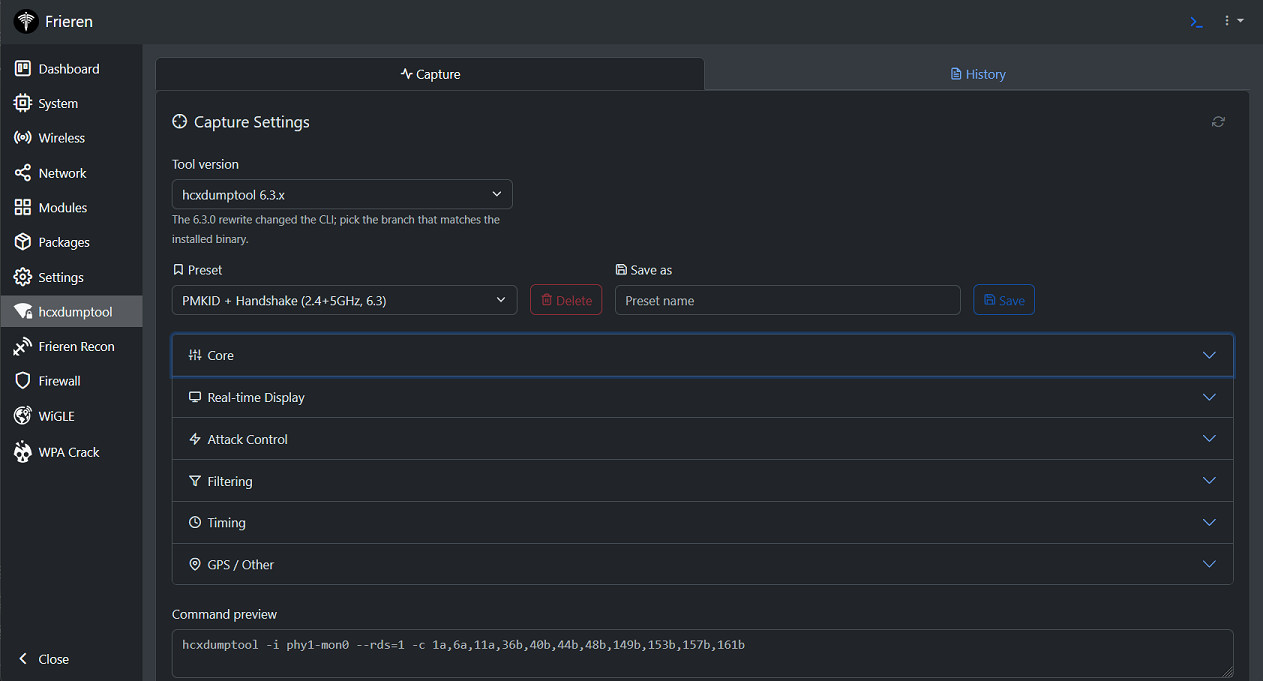 xchwarze/frieren
Frieren is a micro-framework designed for use in routers and Single Board Computers (SBCs). This framework is built to be lightweight, efficient, and…
 lachlan2k/cve-2023-35803
PoC exploit for CVE-2023-35803 unauthenticated buffer overflow in Aerohive HiveOS/Extreme Networks IQ Engine, enabling remote code execution on…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…
 explxx/cve-2023-33538
Python Exploit for TP-Link TL-WR940N/TL-WR841N Command Injection Vulnerability
 efchatz/easy-exploits
Curated collection of proof-of-concept exploits for 16 CVEs targeting web applications (ASUS, D-Link, Netgear, TP-Link, Xiaomi) and Wi-Fi WPA3-SAE,…