

wifiphisher
 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
impersonation-toolsmalware-analysisphishing+6
14.9k
wifiphisher/wifiphisherRogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 infamoussyn/rogue
An extensible toolkit providing penetration testers an easy-to-use platform to deploy Access Points during penetration testing and red team…
 mahmoud-sadder/airstrike
AirStrike is an advanced wireless security assessment framework designed to simplify and enhance Wi-Fi penetration testing through an integrated,…
 garagehq/nightcrawler
Local AI powered red teamer on a phone
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
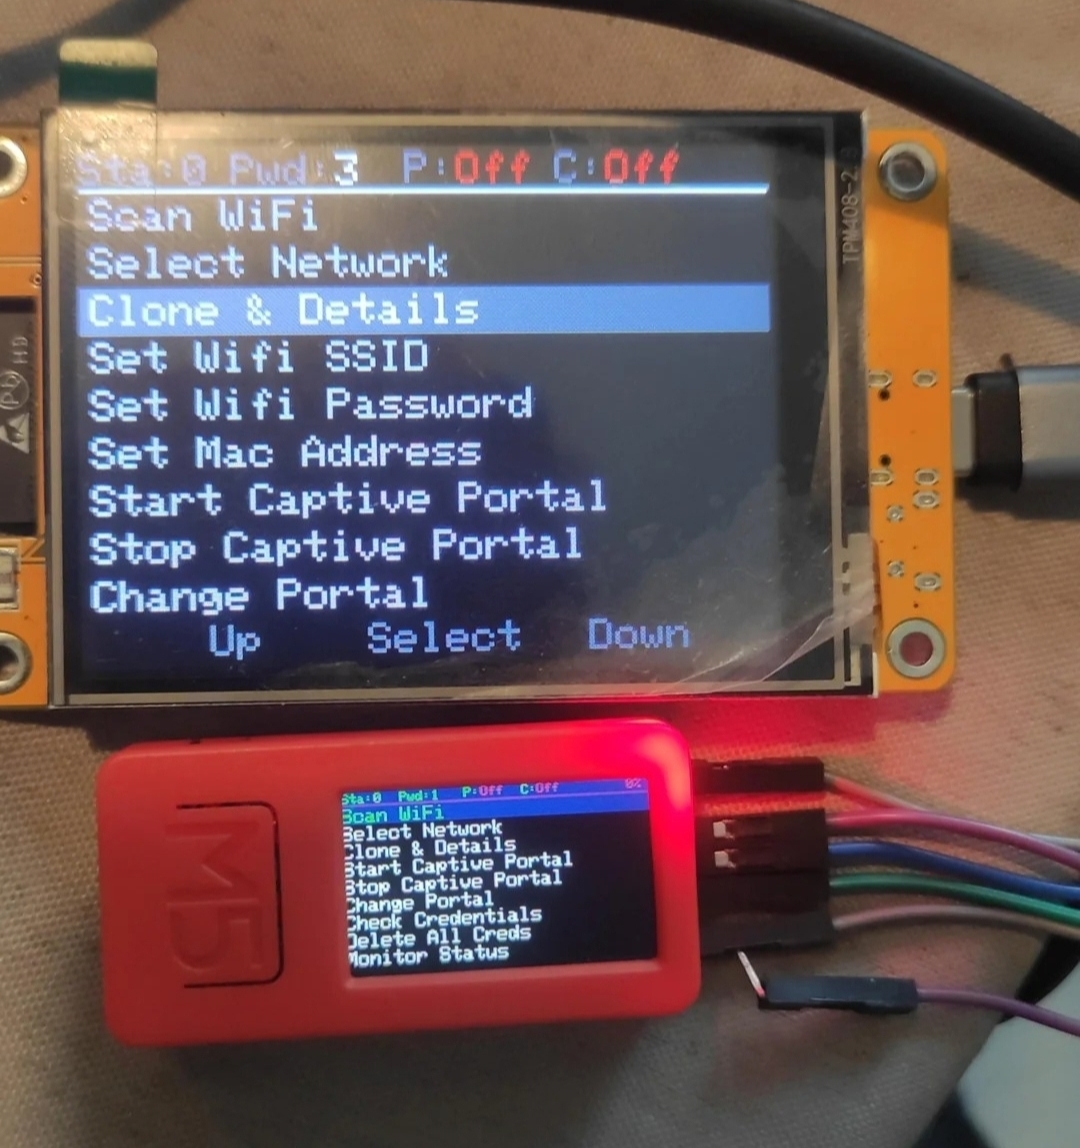 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 rogandawes/p4wnp1_aloa
P4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.
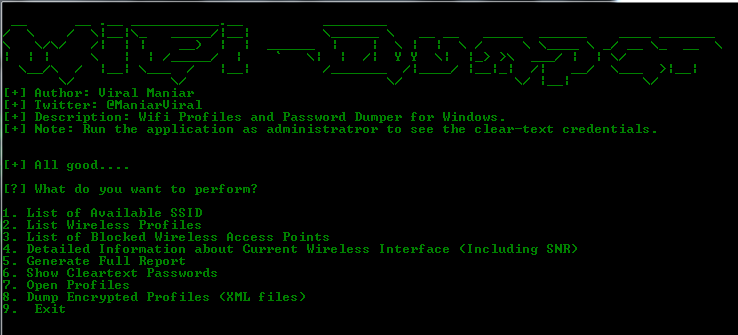 viralmaniar/wifi-dumper
This is an open source tool to dump the wifi profiles and cleartext passwords of the connected access points on the Windows machine. This tool will…
 pinecone-wifi/pinecone
Modular WLAN auditing framework for red teams with deauthentication, rogue AP, and WPA handshake capture modules. Features a Metasploit-like CLI for…
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
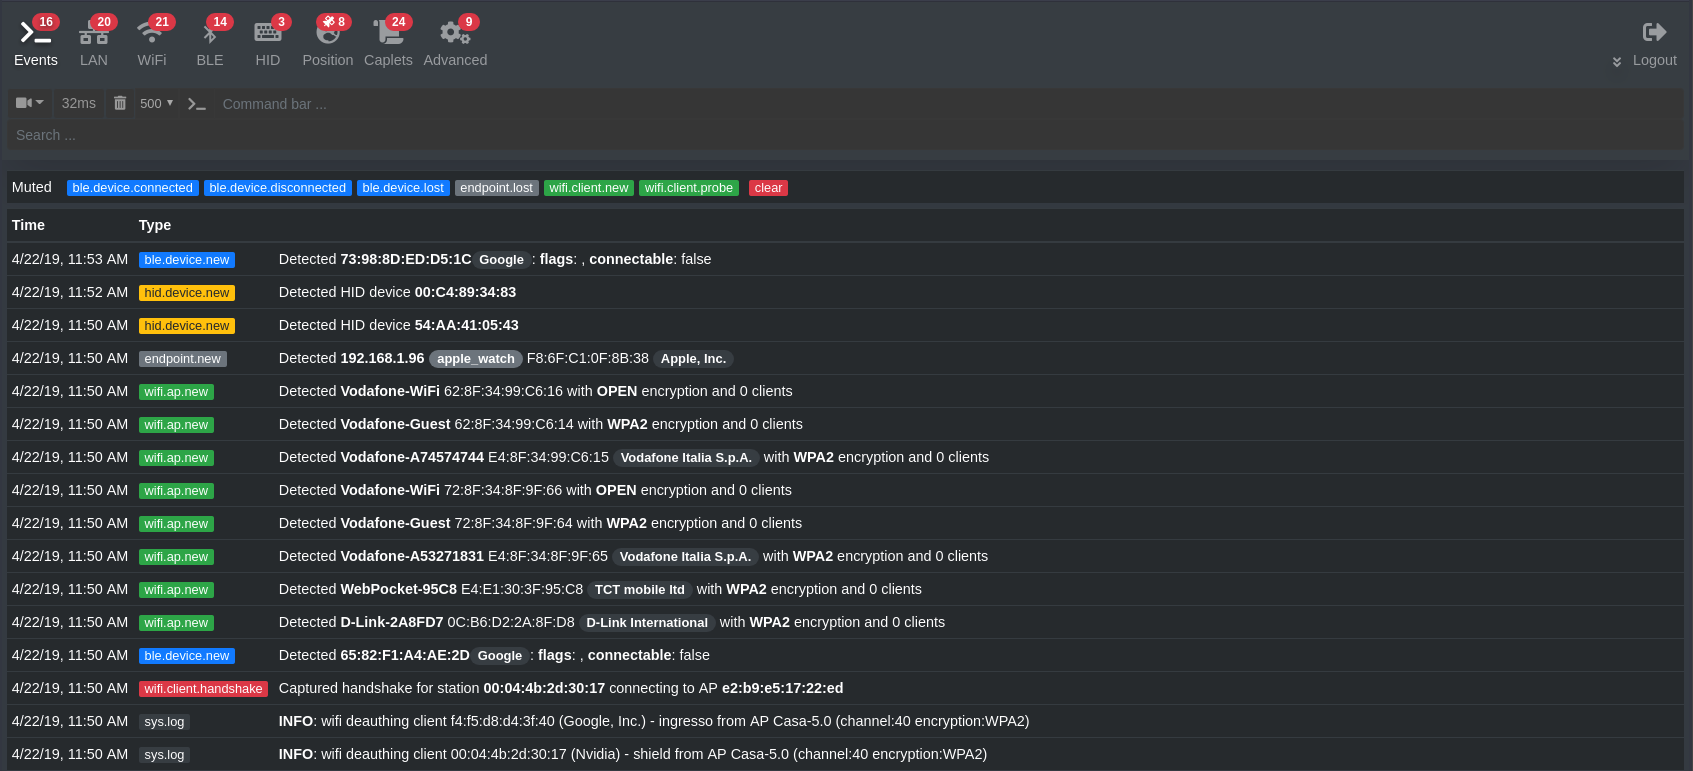 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 brucedevices/firmware
Predatory ESP32 Firmware
 aleksamcode/preferred-network-list-sniffer
A reconnaissance tool for capturing and displaying SSIDs from device's Preferred Network List.
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
 danmcinerney/wifijammer
Continuously jam all wifi clients/routers
 sensepost/hostapd-mana
SensePost's modified hostapd for wifi attacks.