
WPAxFuzz
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
exploitationfuzzingvulnerability-analysis+2
2143 months ago
efchatz/wpaxfuzzA full-featured open-source Wi-Fi fuzzer
 nmap/nmap
High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
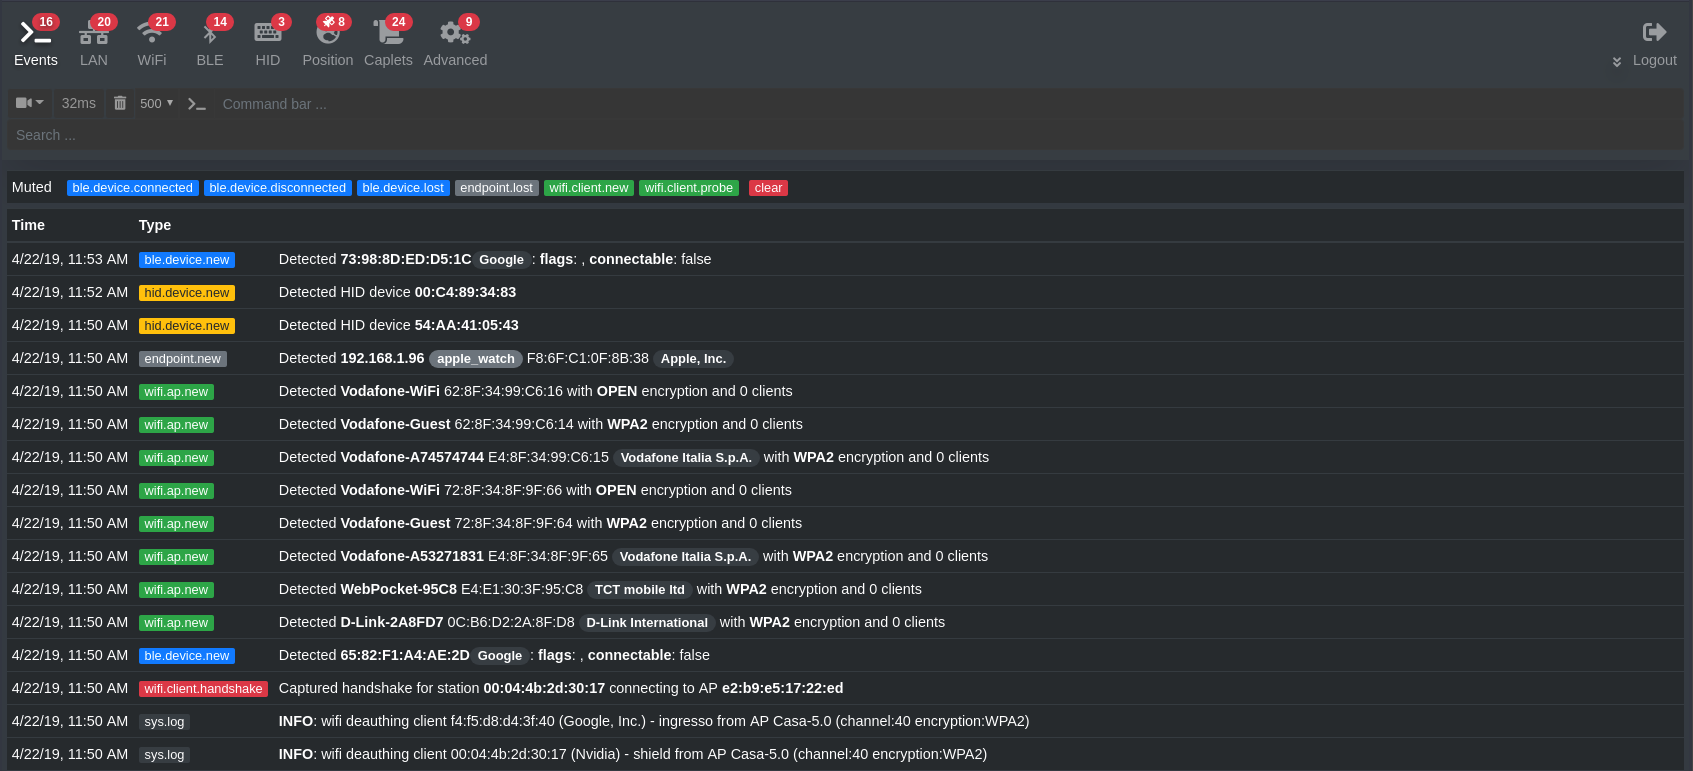 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 brucedevices/firmware
Predatory ESP32 Firmware
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 flock4h/freeway
WiFi Penetration Testing & Auditing Tool
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
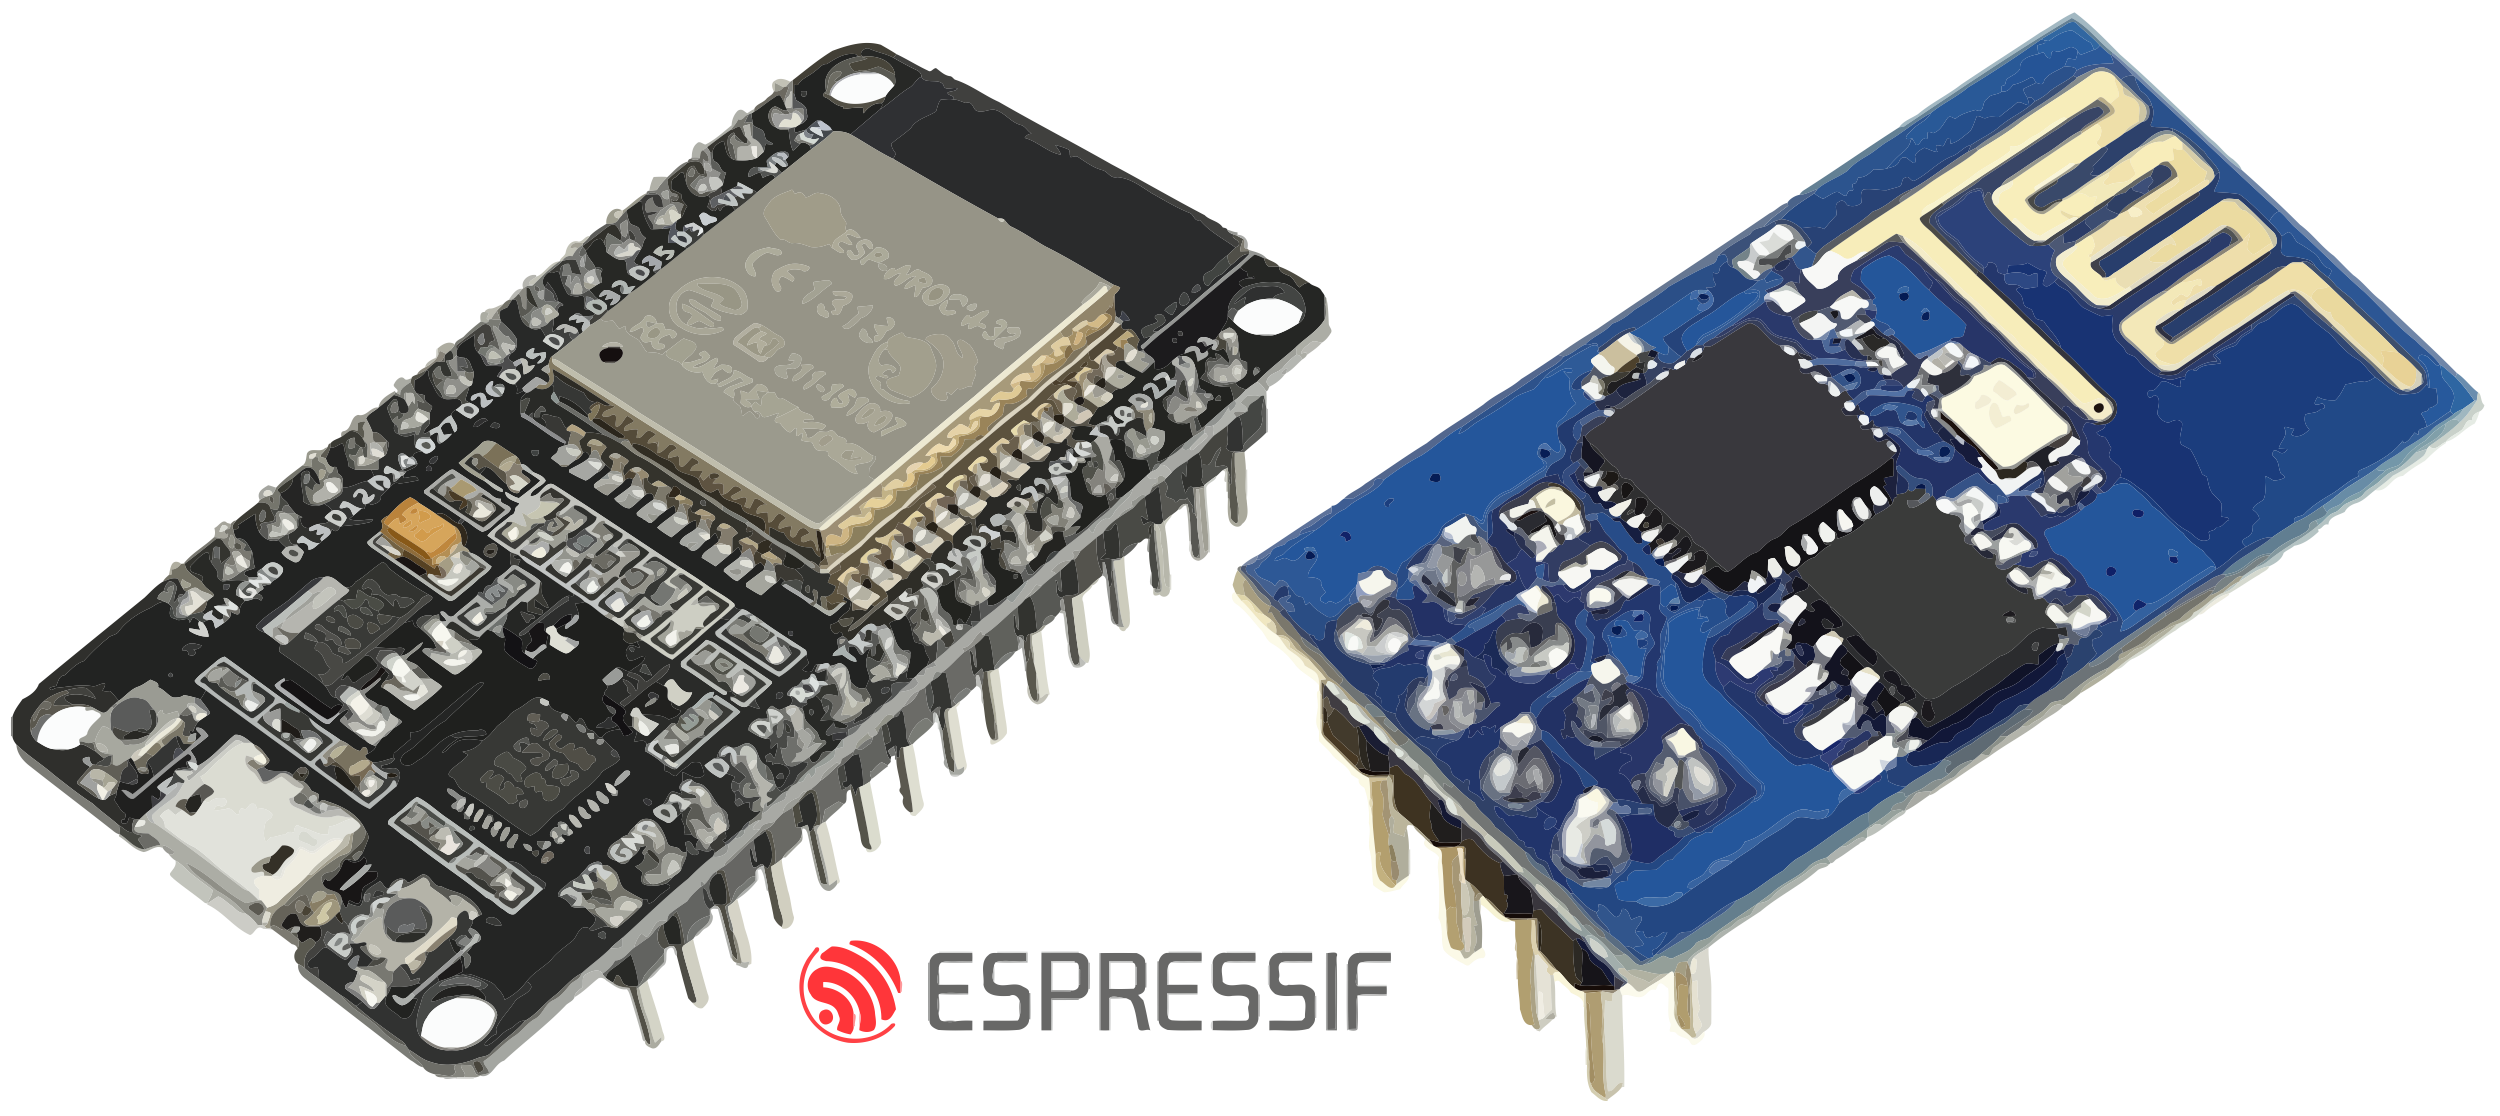 matheus-garbelini/esp32_esp8266_attacks
Proof of Concept of ESP32/8266 Wi-Fi vulnerabilties (CVE-2019-12586, CVE-2019-12587, CVE-2019-12588)
 domienschepers/wifi-framework
Wi-Fi Framework for creating proof-of-concepts, automated experiments, test suites, fuzzers, and more.
 generaldussduss/poseidon
80+ feature pentesting firmware for M5Stack Cardputer-Adv. WiFi, BLE, sub-GHz (CC1101), 2.4GHz (nRF24), LoRa (SX1262), IR, BadUSB, DHCP attacks,…
 0ldev/politician
Modern WiFi auditing library for ESP32 using advanced 802.11 techniques. Captures WPA/WPA2/WPA3 handshakes via PMKID extraction and CSA injection…
 iotsrg/iot-pentest-devices-and-purpose
Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…