Firebolt-wristphone-vulnerability

This repository is for Firebolt wristphone vulnerability for CVE ID CVE-2024-30656 suggested by MITRE. Mitre yet to confirm on ID

This repository is for Firebolt wristphone vulnerability for CVE ID CVE-2024-30656 suggested by MITRE. Mitre yet to confirm on ID

Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…

Proof-of-concept exploit for CVE-2020-27301 in hostapd, enabling rogue access point creation to test and demonstrate the vulnerability in WPA2/WPA3…

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

Proof-of-concept exploit for CVE-2018-4084, a WiFi credential leak vulnerability in macOS High Sierra, demonstrating interception of plaintext Wi-Fi…

High-performance network discovery and security auditing tool with advanced port scanning, OS detection, service version detection, and scriptable…

PoC exploit for the CVE-2019-15126 kr00k vulnerability

An experimental script PoC for Kr00k vulnerability (CVE-2019-15126)

PoC of CVE-2019-15126 kr00k vulnerability

Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.

This vulnerability impacts device availability and reliable operation of Atomberg Erica Smart Fan(Firmware Version 1.0.36). The issue arises due to a…

Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.

This is a Proof-Of-Concept of CVE-2025-63353

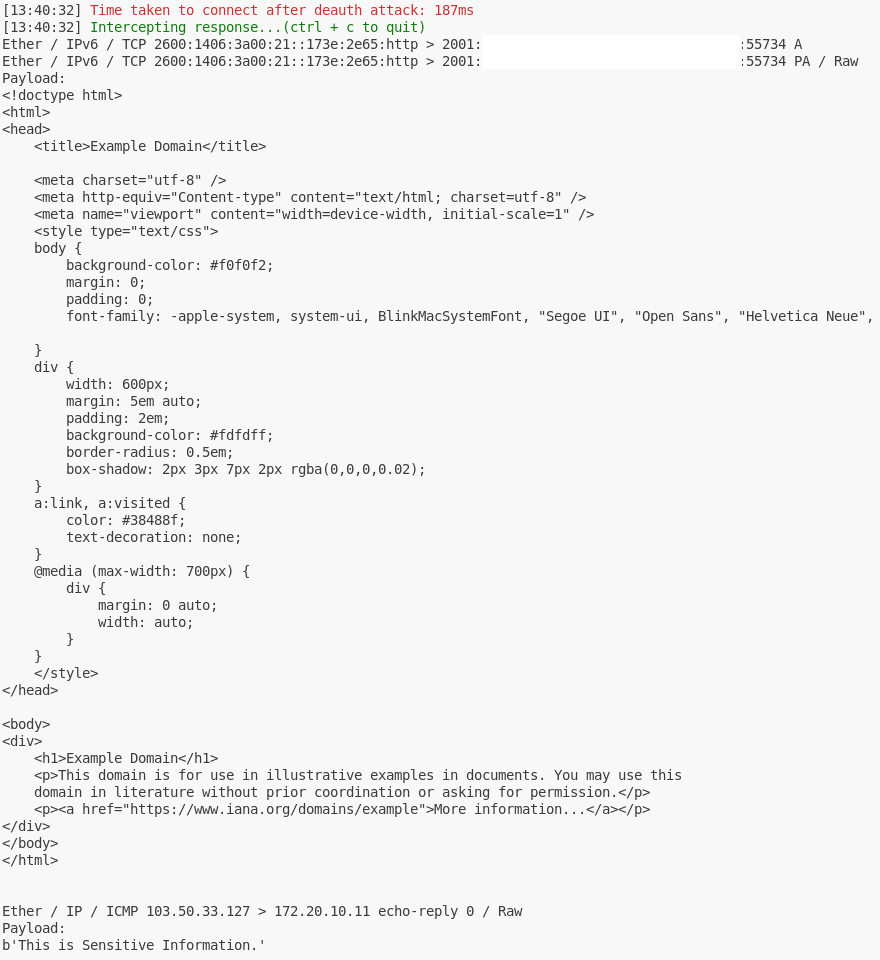
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…

Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.

A full-featured open-source Wi-Fi fuzzer

PoC for CVE-2019-6203, works on < iOS 12.2, macOS < 10.14.4

use the Apple CoreText exploit (CVE-2012-3716) and launch an AP to affect all devices within wifi range