

ESP32-DIV
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
bluetooth-securityeducationembedded-systems-security+8
4.1k
cifertech/esp32-divESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 fluxionnetwork/fluxion
Automated WPA/WPA2 phishing tool that captures handshakes, spawns a rogue access point, and lures users to a captive portal to harvest credentials…
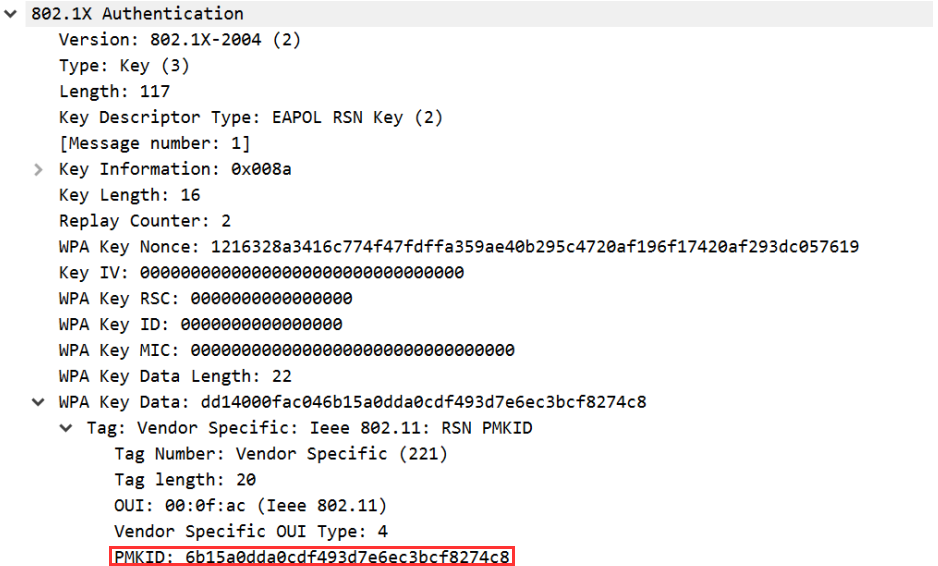 n0mi1k/pmkidcracker
A tool to crack WPA2 passphrase with PMKID value without clients or de-authentication
 nanopathi/wpa_supplicant_8_cve-2021-0326.
Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 aircrack-ng/aircrack-ng
Complete suite for WiFi network security auditing, including packet capture, injection attacks, deauthentication, fake AP creation, and WEP/WPA PSK…
 efchatz/wpaxfuzz
A full-featured open-source Wi-Fi fuzzer
 priyankvadaliya/hack-captive-portal
This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
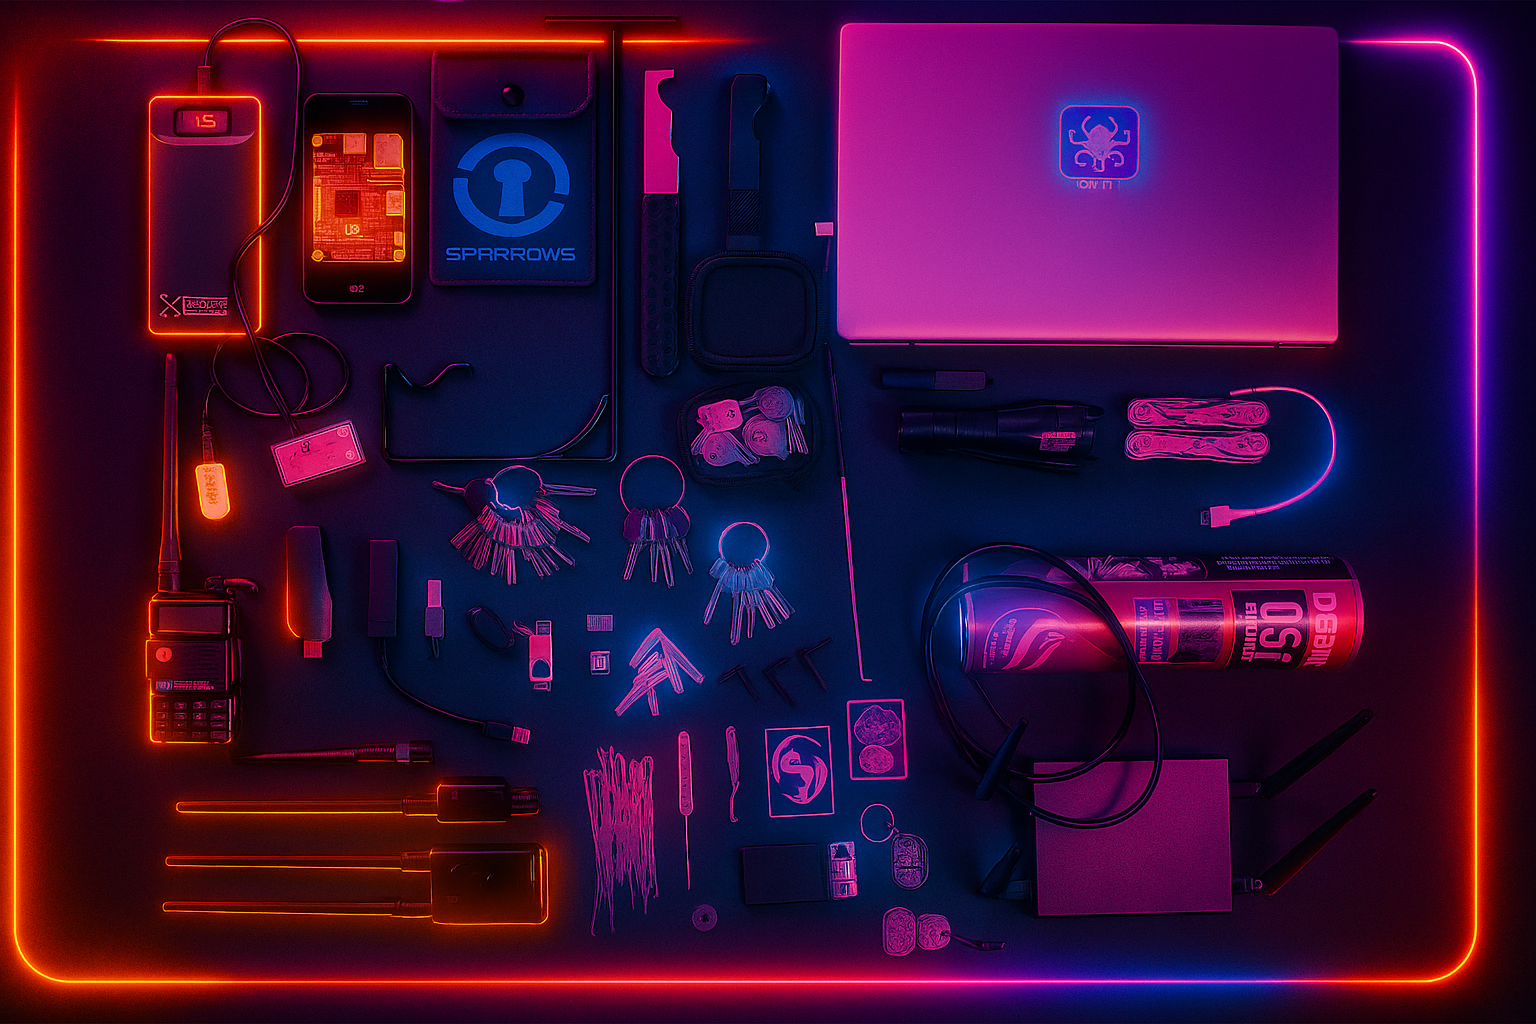 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.
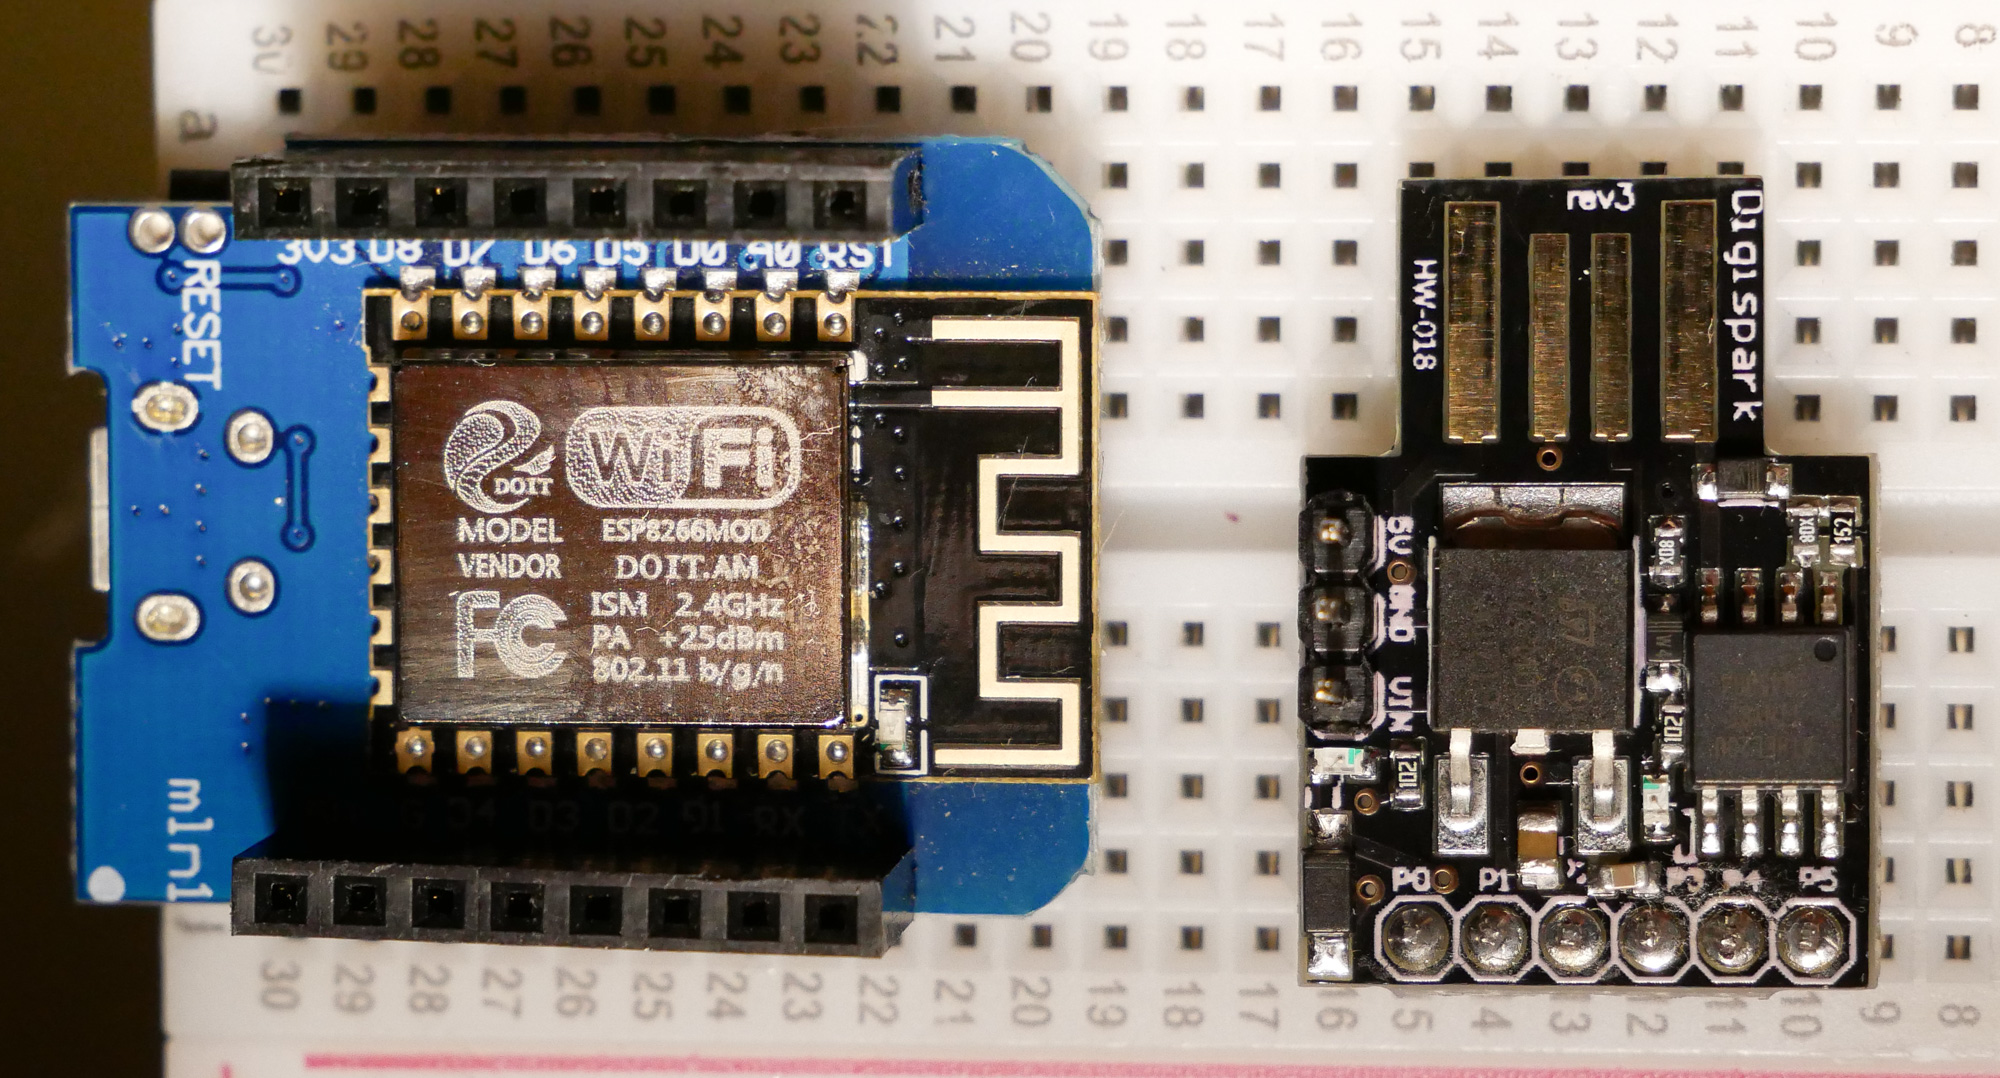 skickar/digitrack
Attacks for $5 or less using Arduino
 satheesh575555/external_wpa_supplicant_8_aosp10_r33_cve-2021-0516
Proof-of-concept exploit for CVE-2021-0516 in wpa_supplicant on AOSP 10, demonstrating a buffer overflow vulnerability in Wi-Fi authentication.
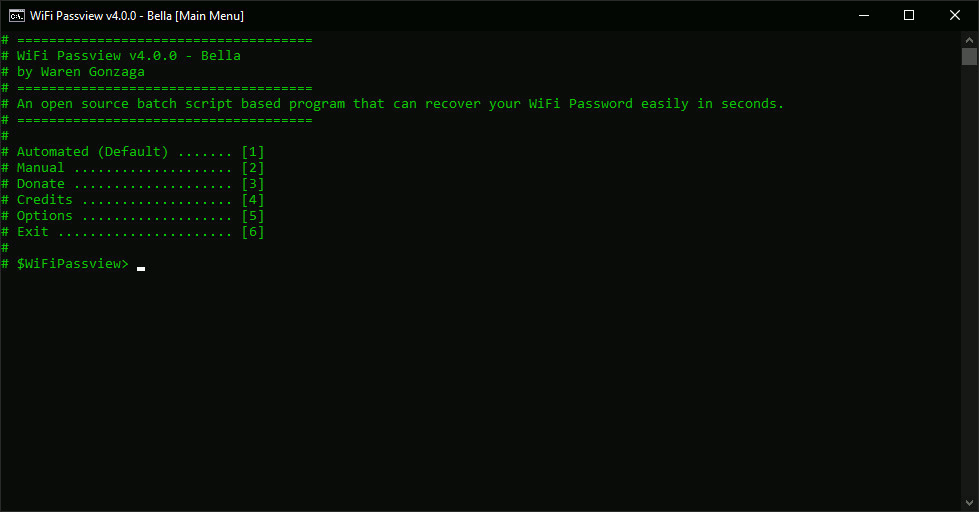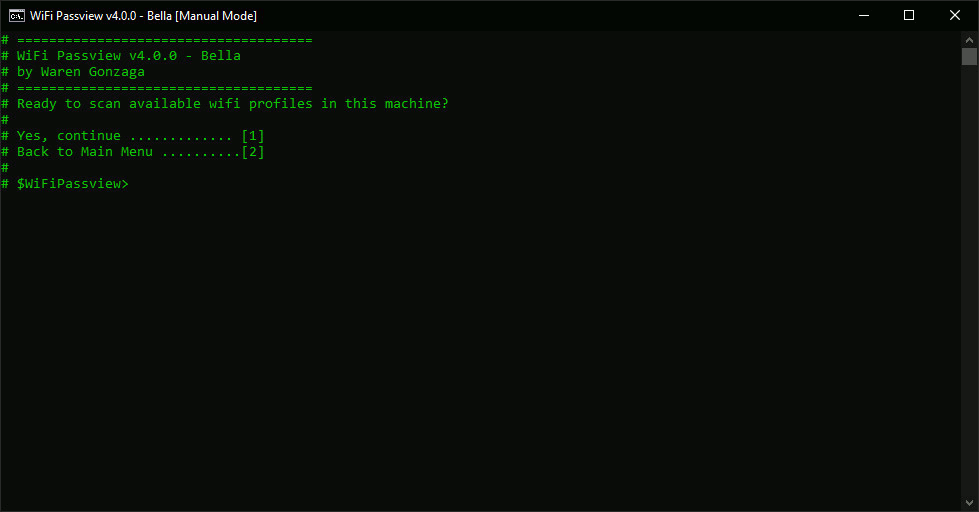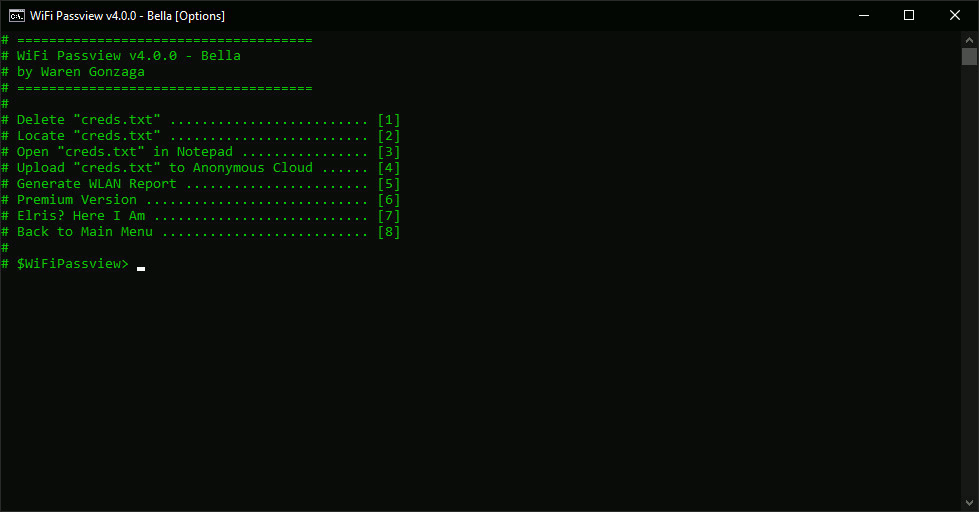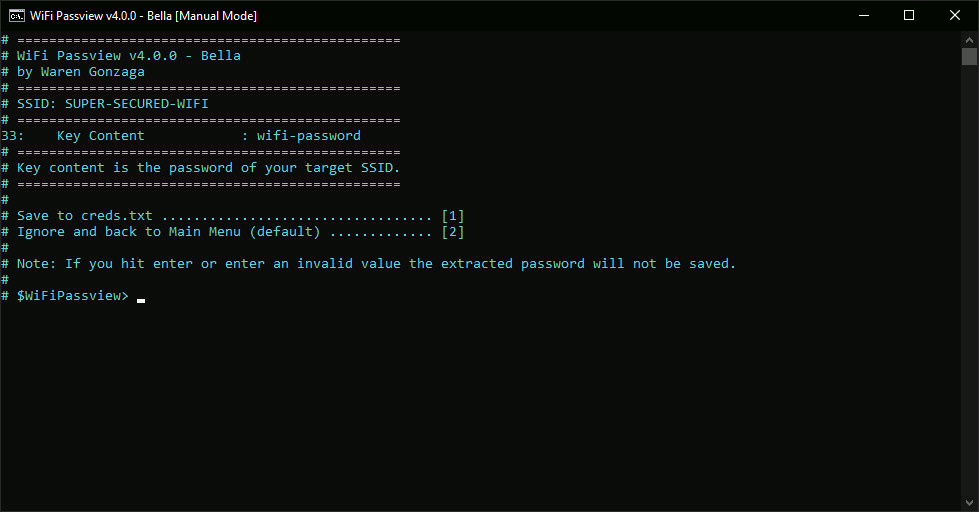 warengonzaga/wifi-passview
An open source batch script based WiFi Passview for Windows!
 zerbea/hcxdumptool
Small tool to capture packets from wlan devices.
 esc0rtd3w/wifi-hacker
Shell Script For Attacking Wireless Connections Using Built-In Kali Tools. Supports All Securities (WEP, WPS, WPA, WPA2)
 s0c5/remotepasswordwifi
Script in Ruby. Break Remote router wifi passwords.