

gotestwaf
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
api-securityapi-security-testingpenetration-testing+4
1.8k
wallarm/gotestwafAn open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 m4cs/traxss
traxss | Automated XSS Vulnerability Scanner Currently In Development 🐍 HACKTOBERFEST PROJECT 2019
 bwasp/bwasp
BoB Web Application Security Project
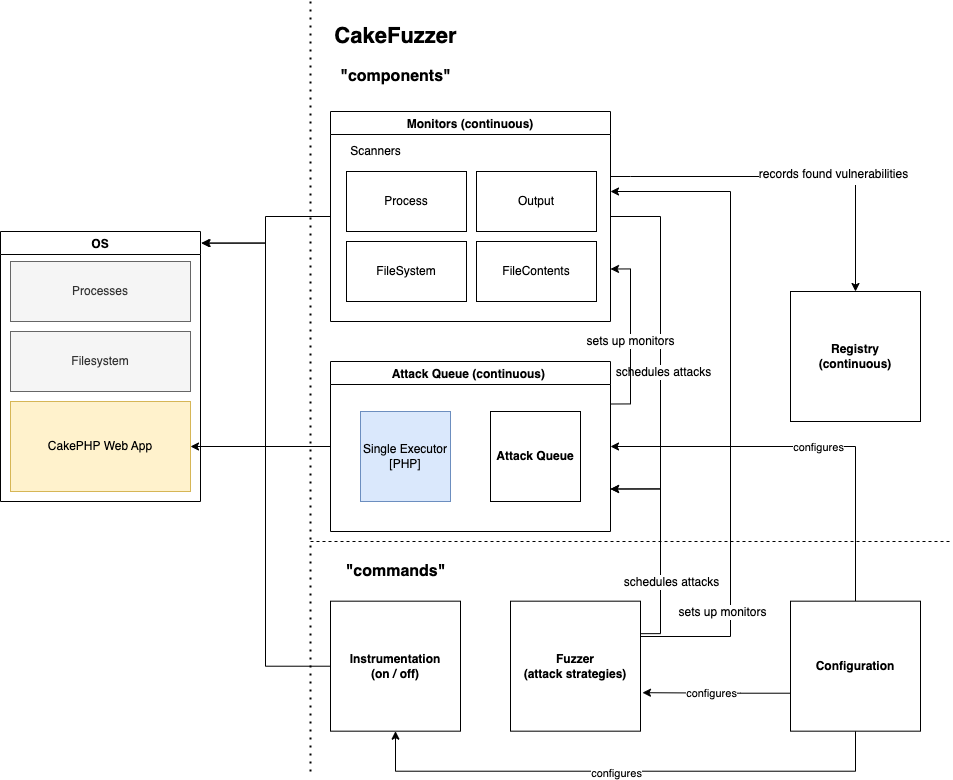 zigrin-security/cakefuzzer
Cake Fuzzer is a project that is meant to help automatically and continuously discover vulnerabilities in web applications created based on specific…
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
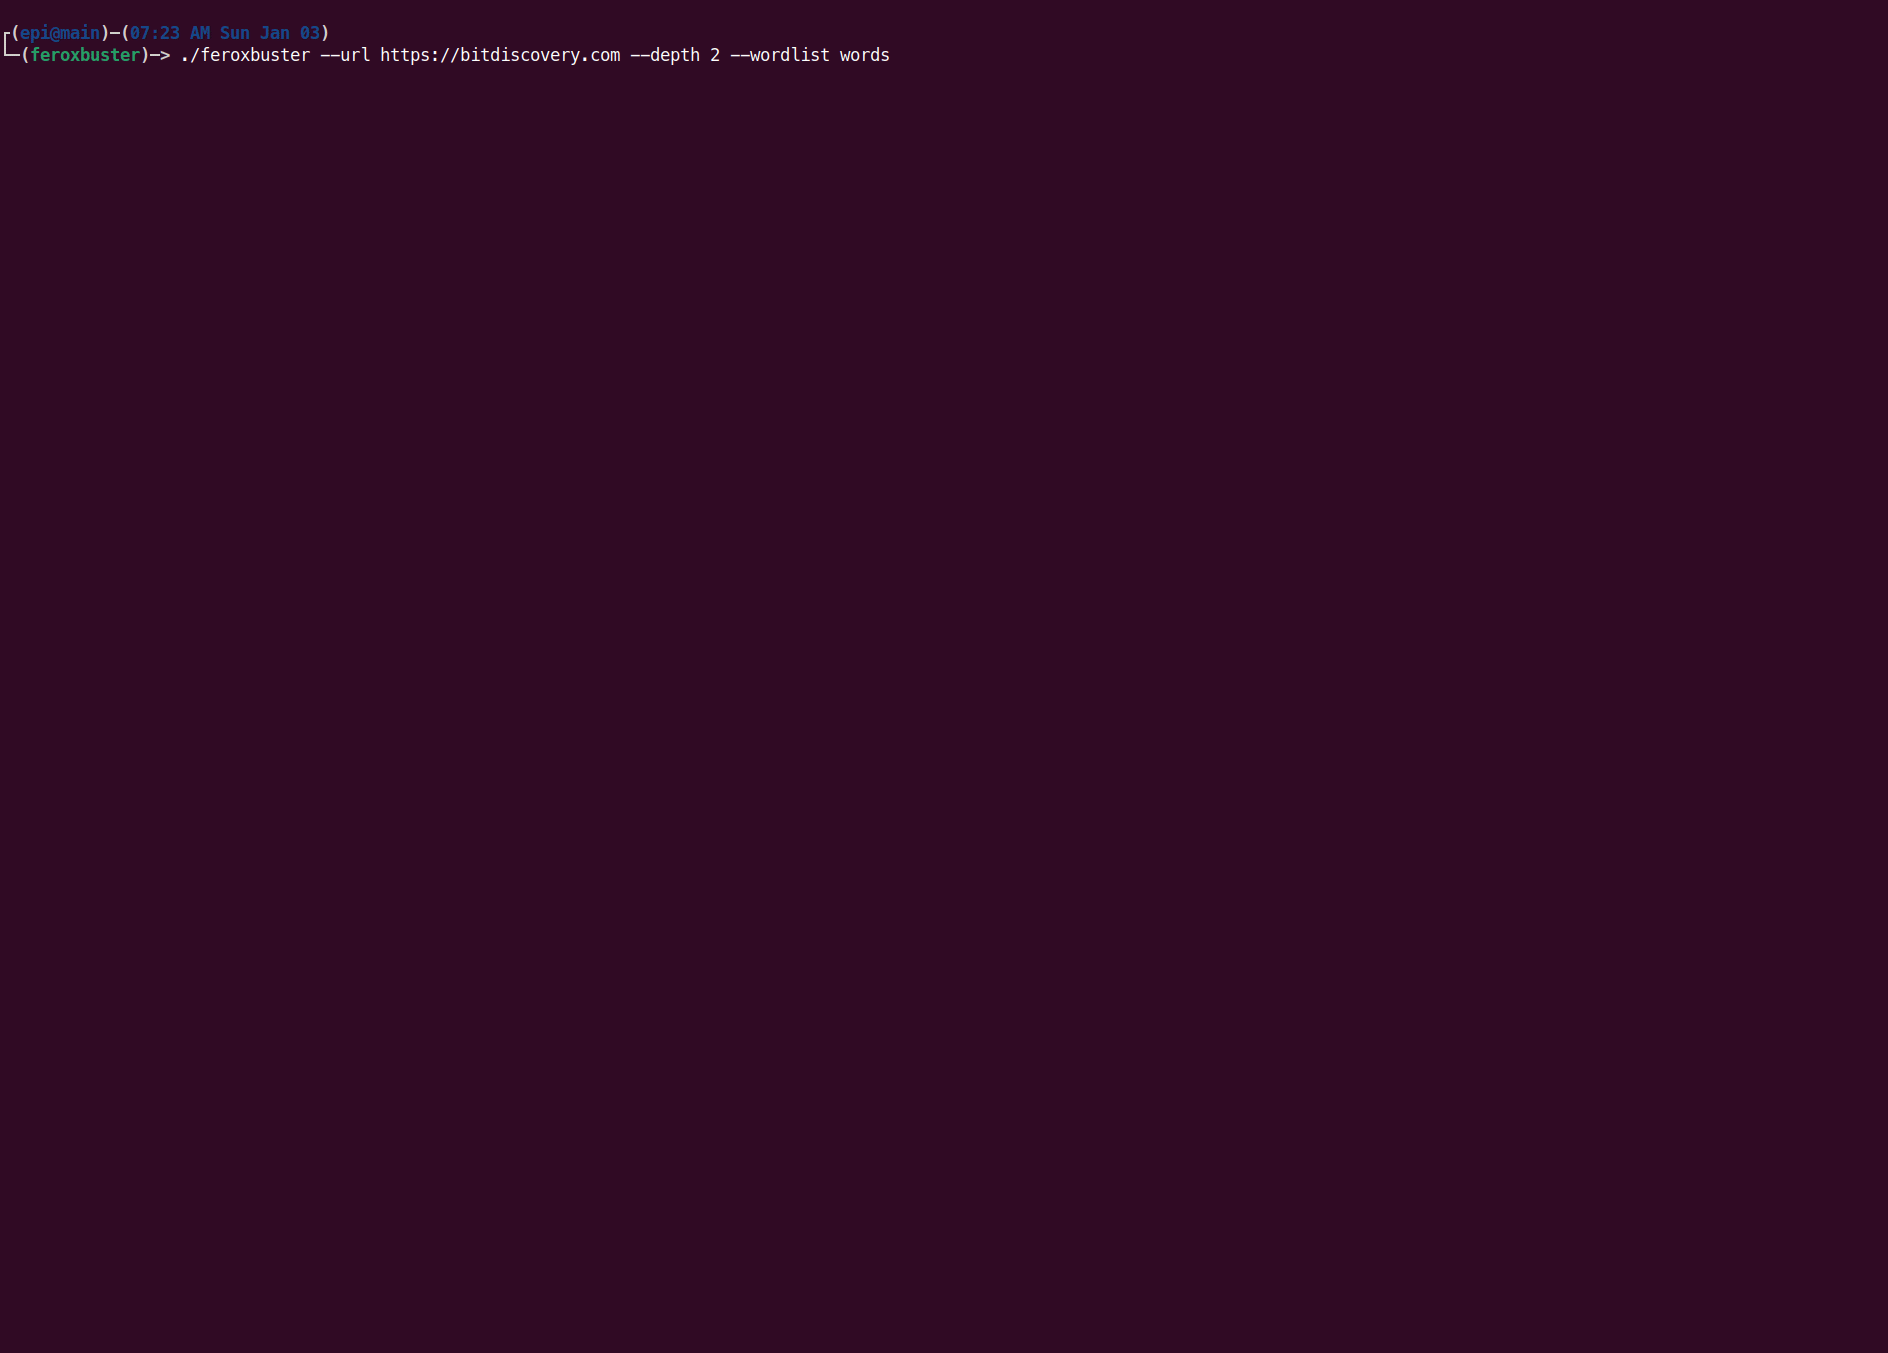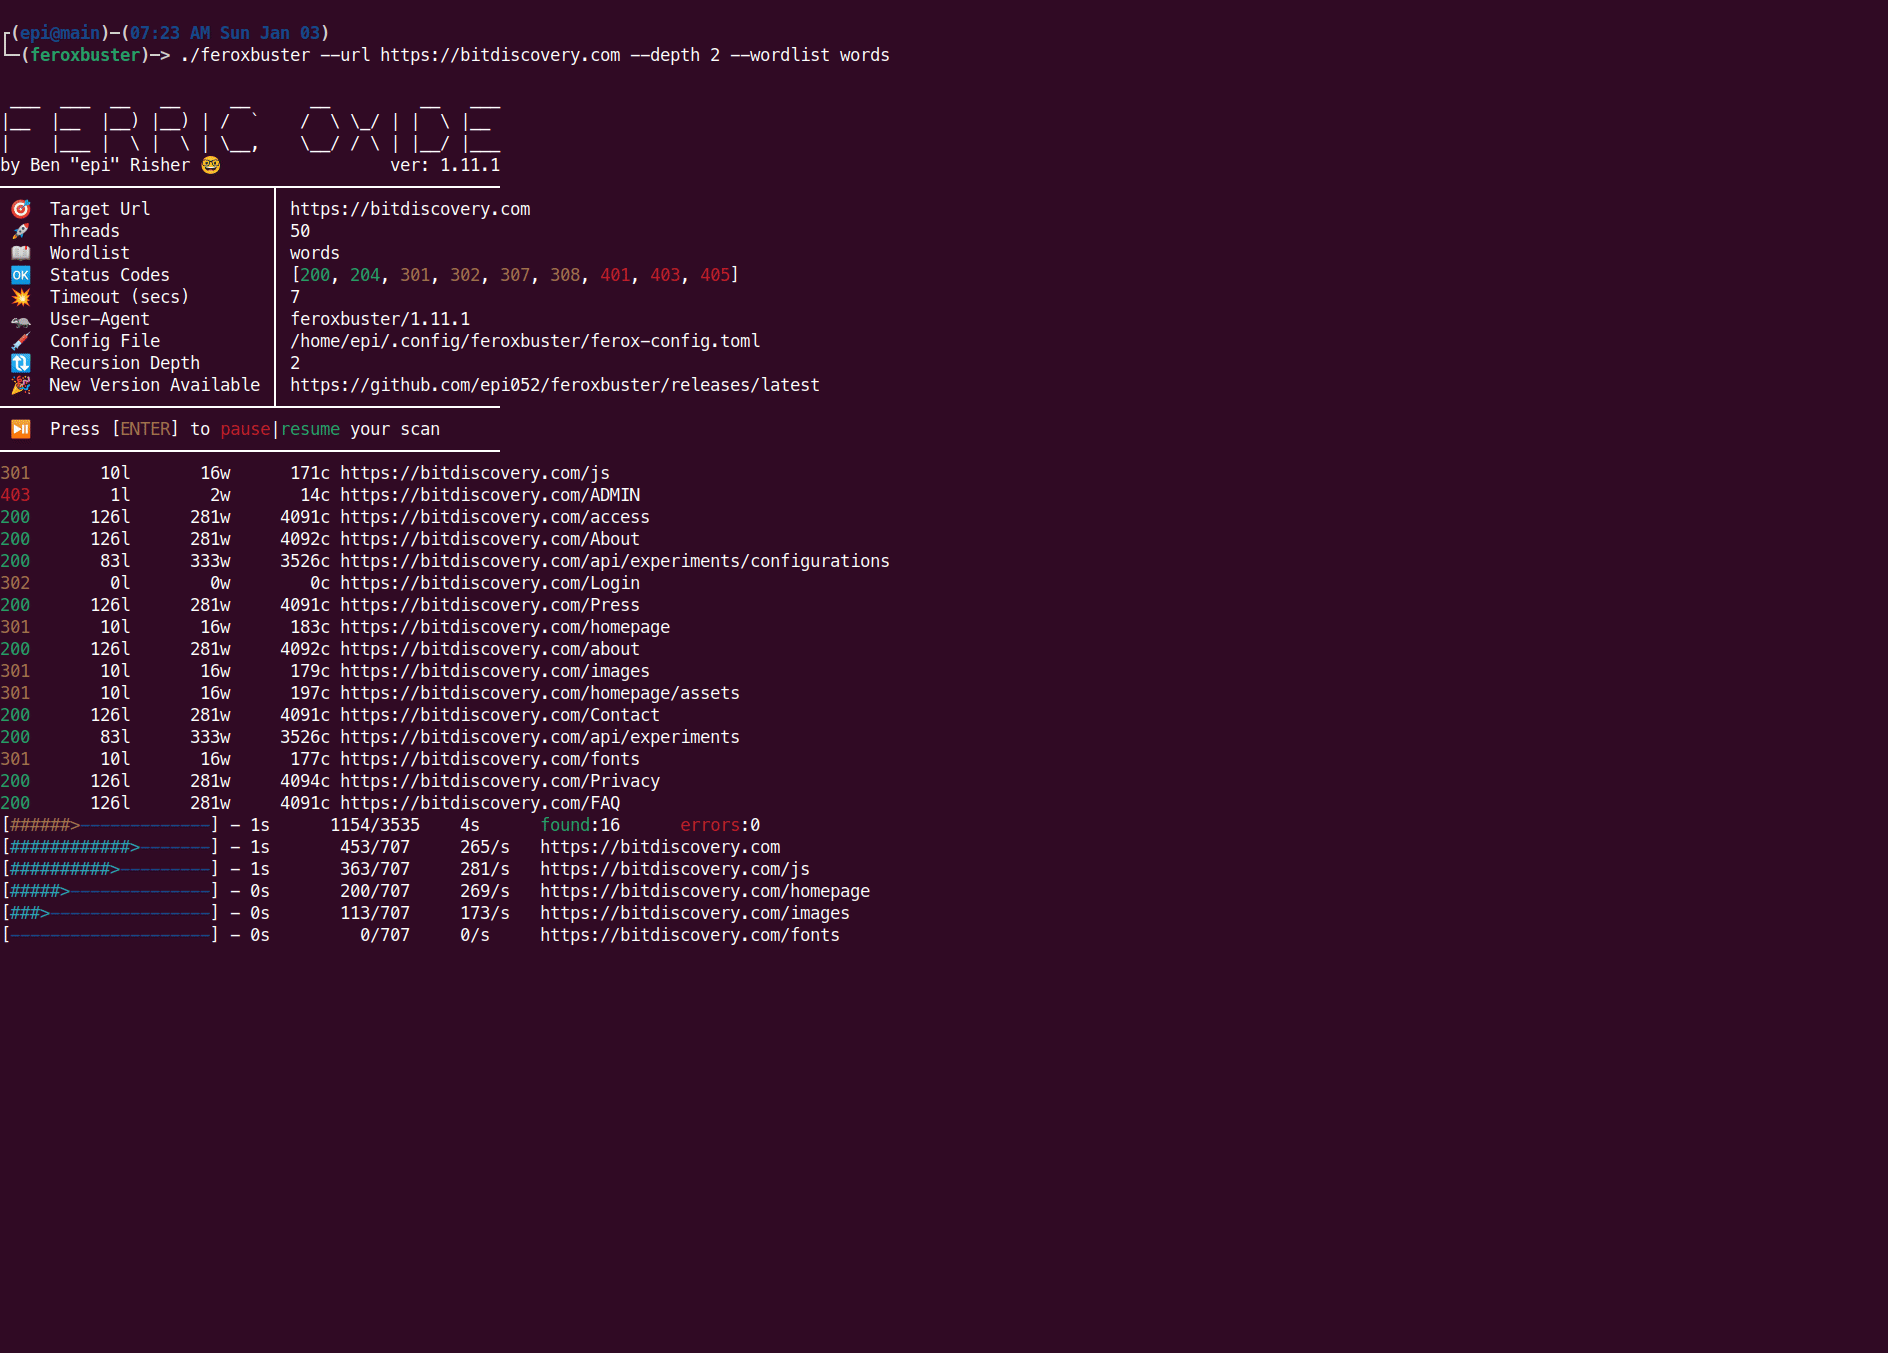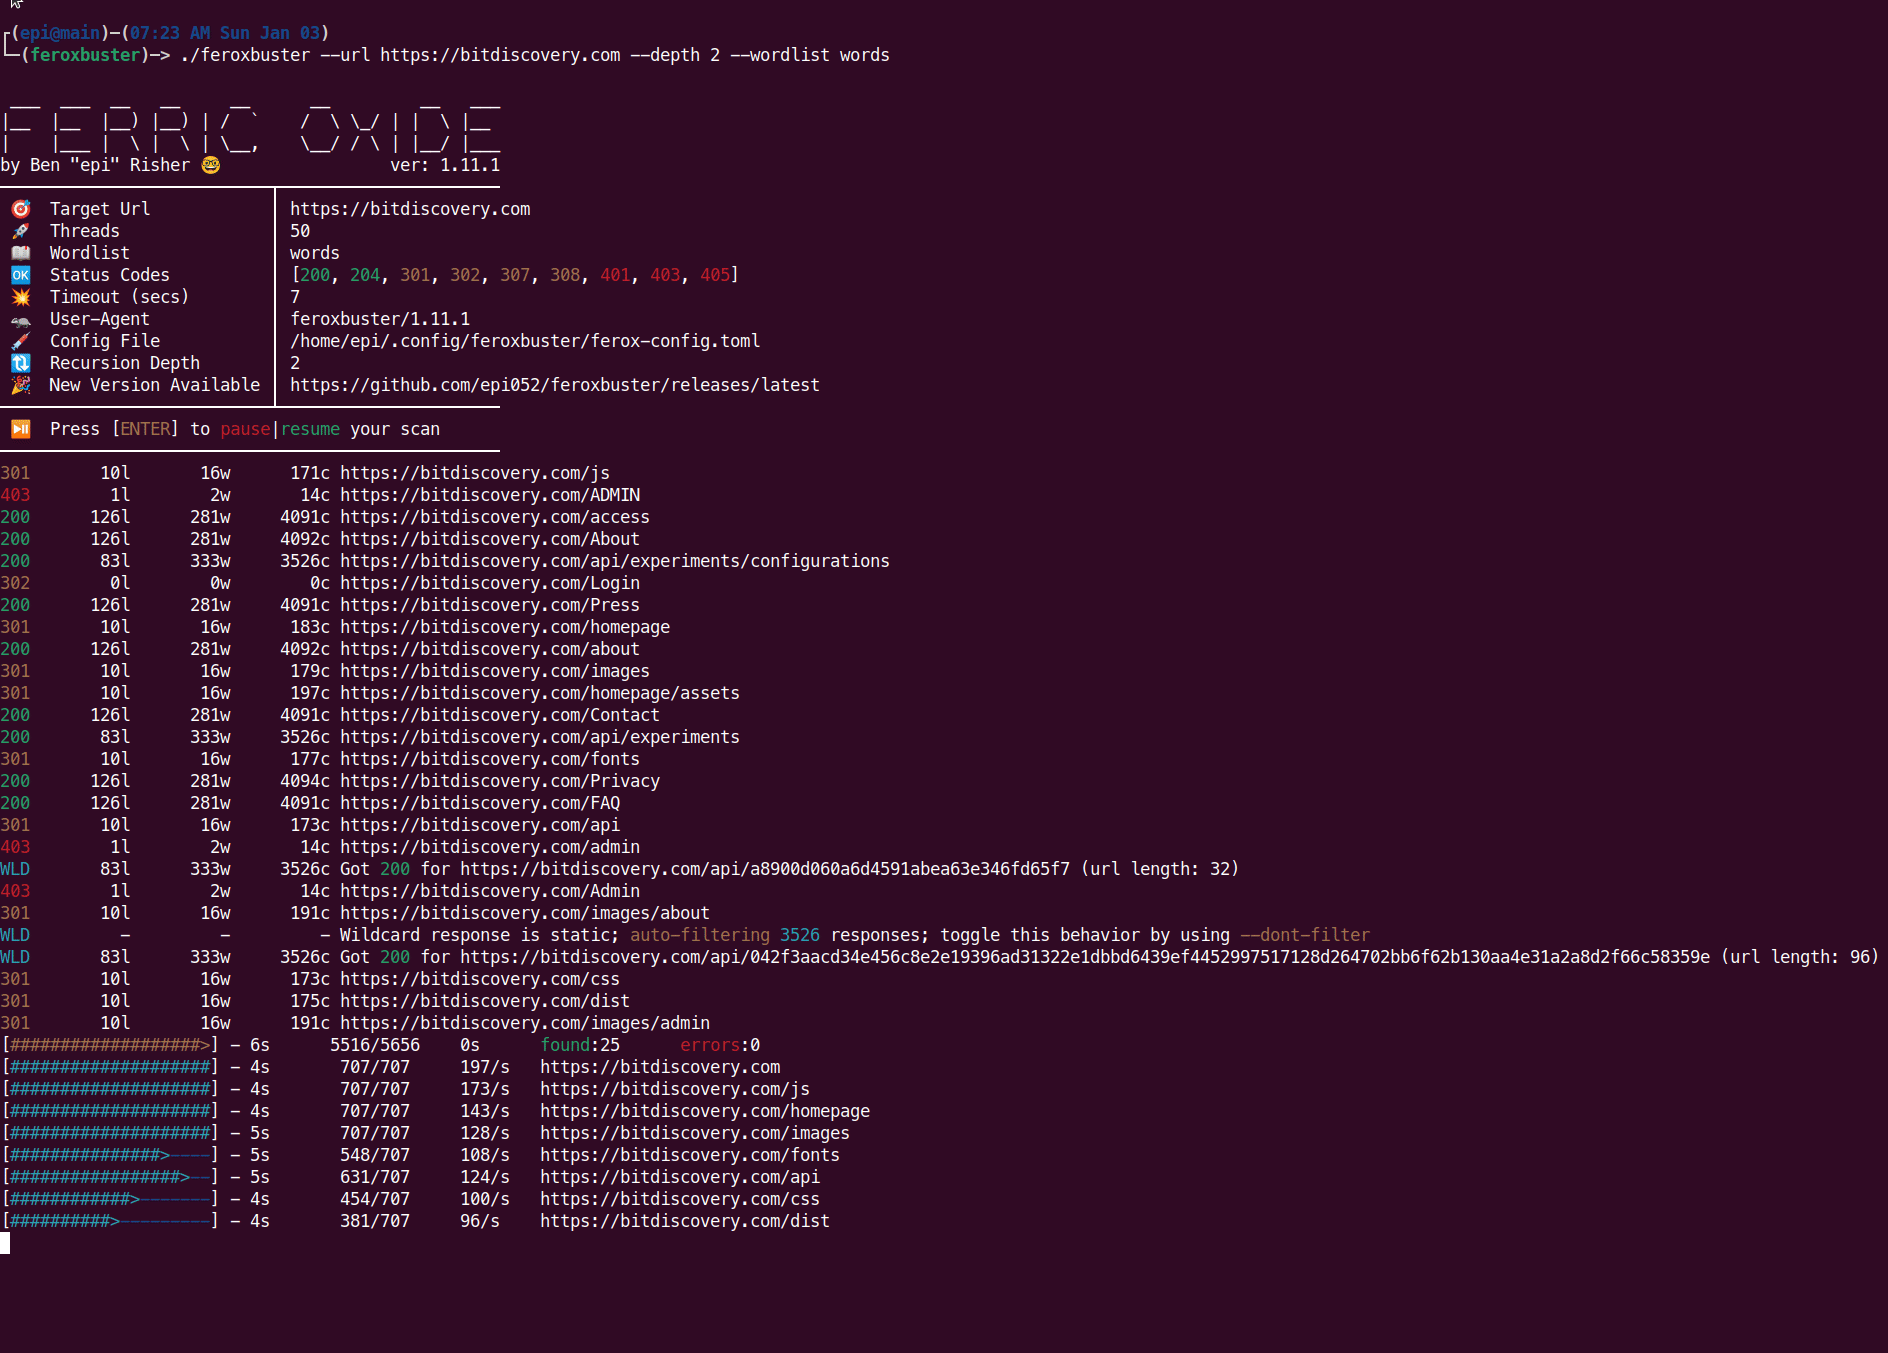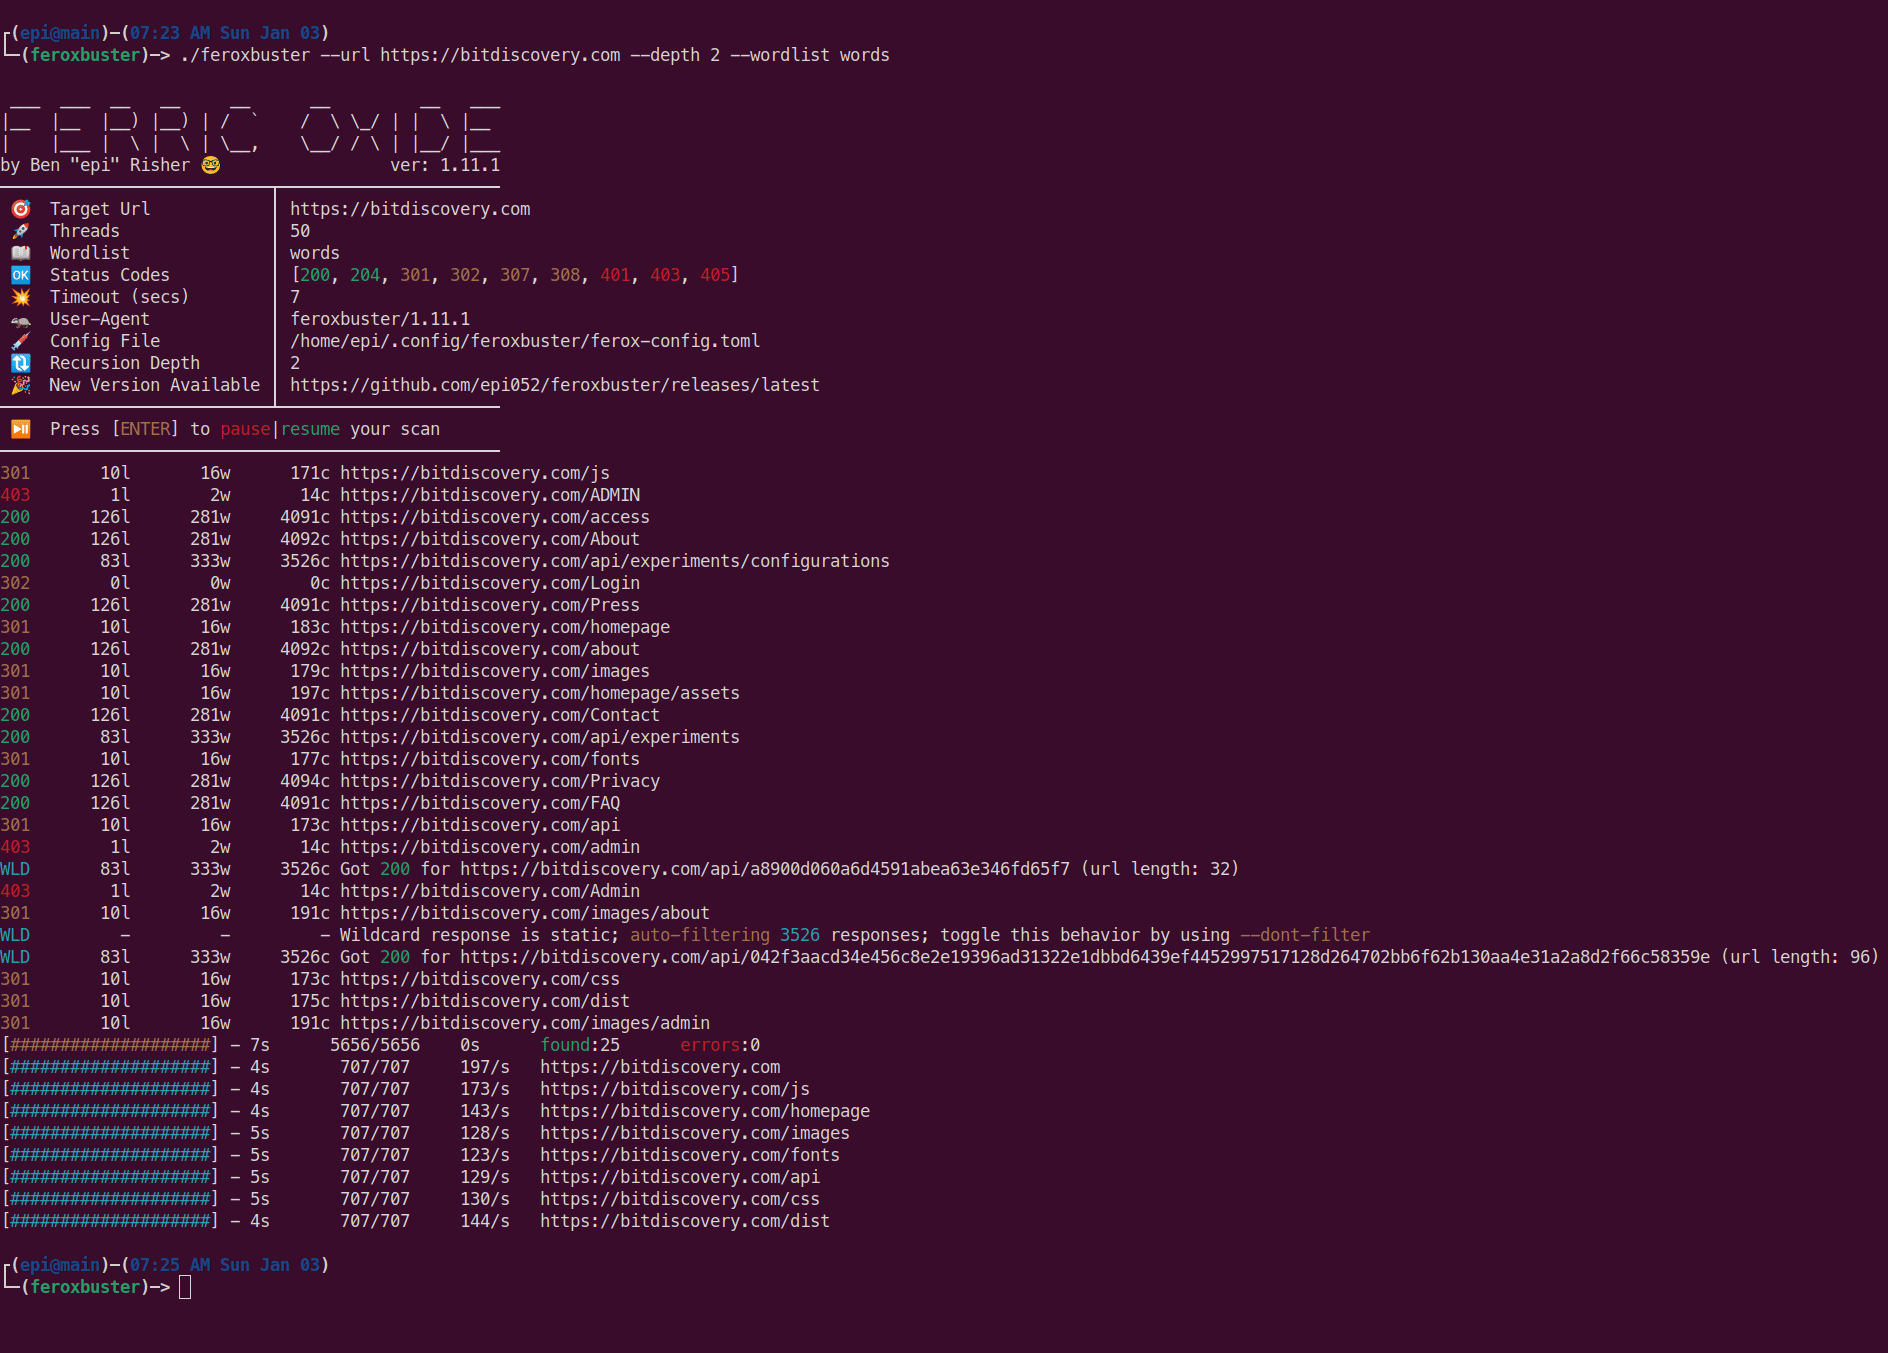 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
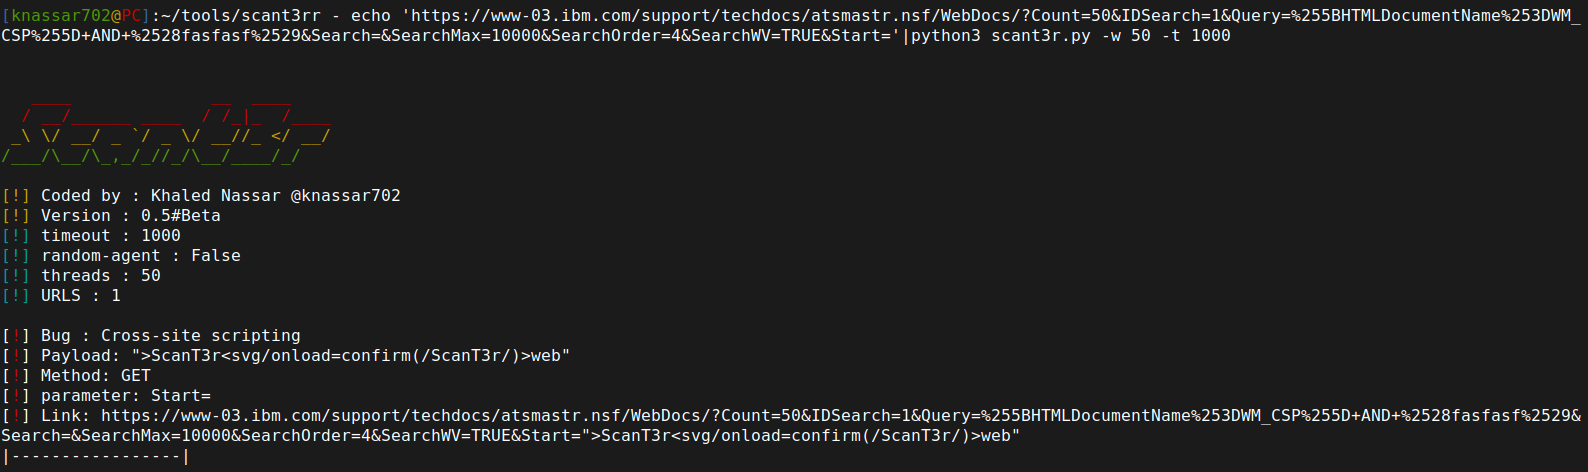 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 zigoo0/webpwn3r
WebPwn3r - Web Applications Security Scanner.
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
 ekultek/pybelt
The hackers tool belt
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 ostesayed/oste-meta-scan
Multi-engine DAST scanner aggregating Nikto, ZAP, Nuclei, SkipFish, and Wapiti for automated web injection vulnerability detection with consolidated…
 gwroblew/detectxsslib
C++ library for detecting cross-site scripting (XSS) vulnerabilities in URLs through pattern analysis, with server modules and command-line tools for…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 erman-bolukbasi/web-penetration-drupal
Penetration test of a Drupal web app — CVE-2018-7600 (Drupalgeddon 2) exploited using Nmap, Burp Suite & Metasploit | Internship @ BB CyberSec
 shivanshkuntal/exploitation-of-a-remote-code-execution-vulnerability--cve-2024-7954-
Exploitation of a Remote Code Execution vulnerability- (CVE-2024-7954)