
XSLeaker
 philesiv/xsleaker
Searcher for cross-site leaks (XS-Leaks)
penetration-testingprivacyvulnerability-analysis+2
philesiv/xsleakerSearcher for cross-site leaks (XS-Leaks)
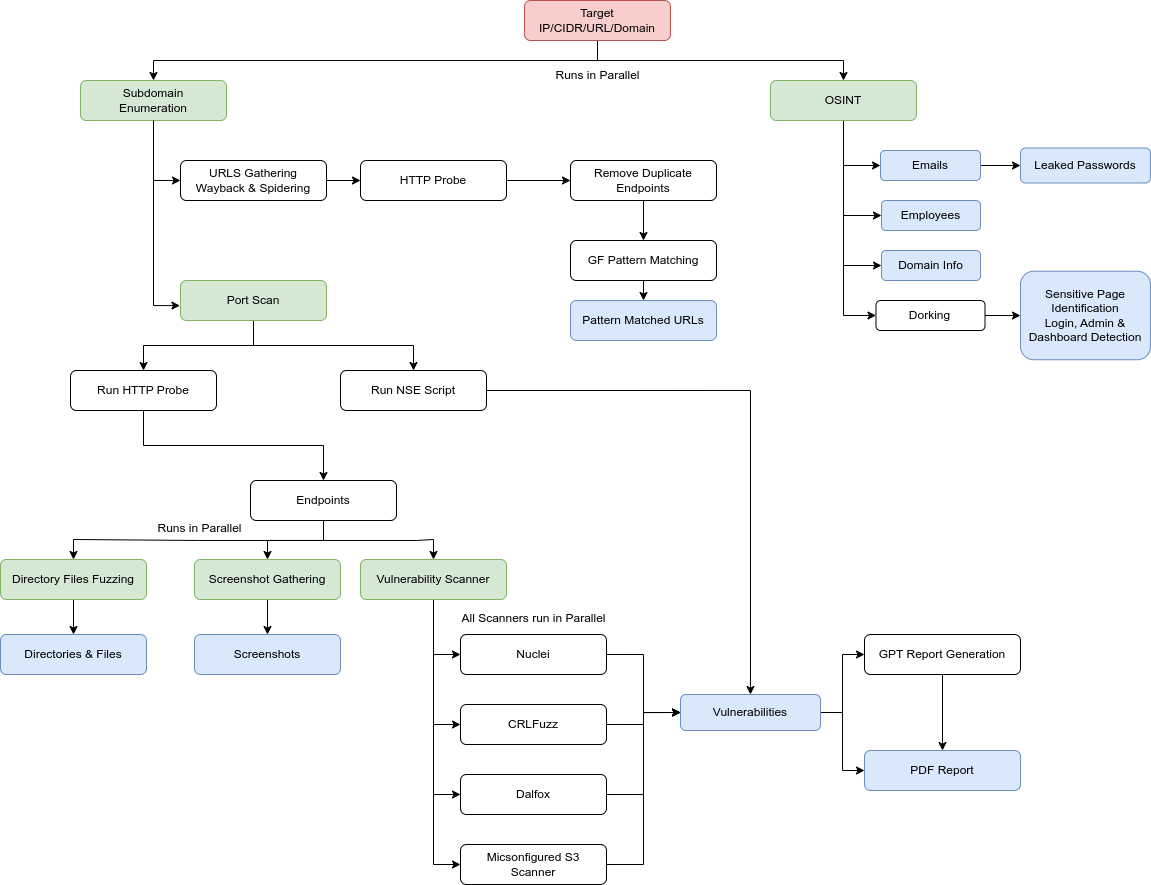 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 ronin-rb/ronin
Ronin is a Free and Open Source Ruby Toolkit for Security Research and Development. Ronin also allows for the rapid development and distribution of…
 fcavallarin/htcap
htcap is a web application scanner able to crawl single page application (SPA) recursively by intercepting ajax calls and DOM changes.
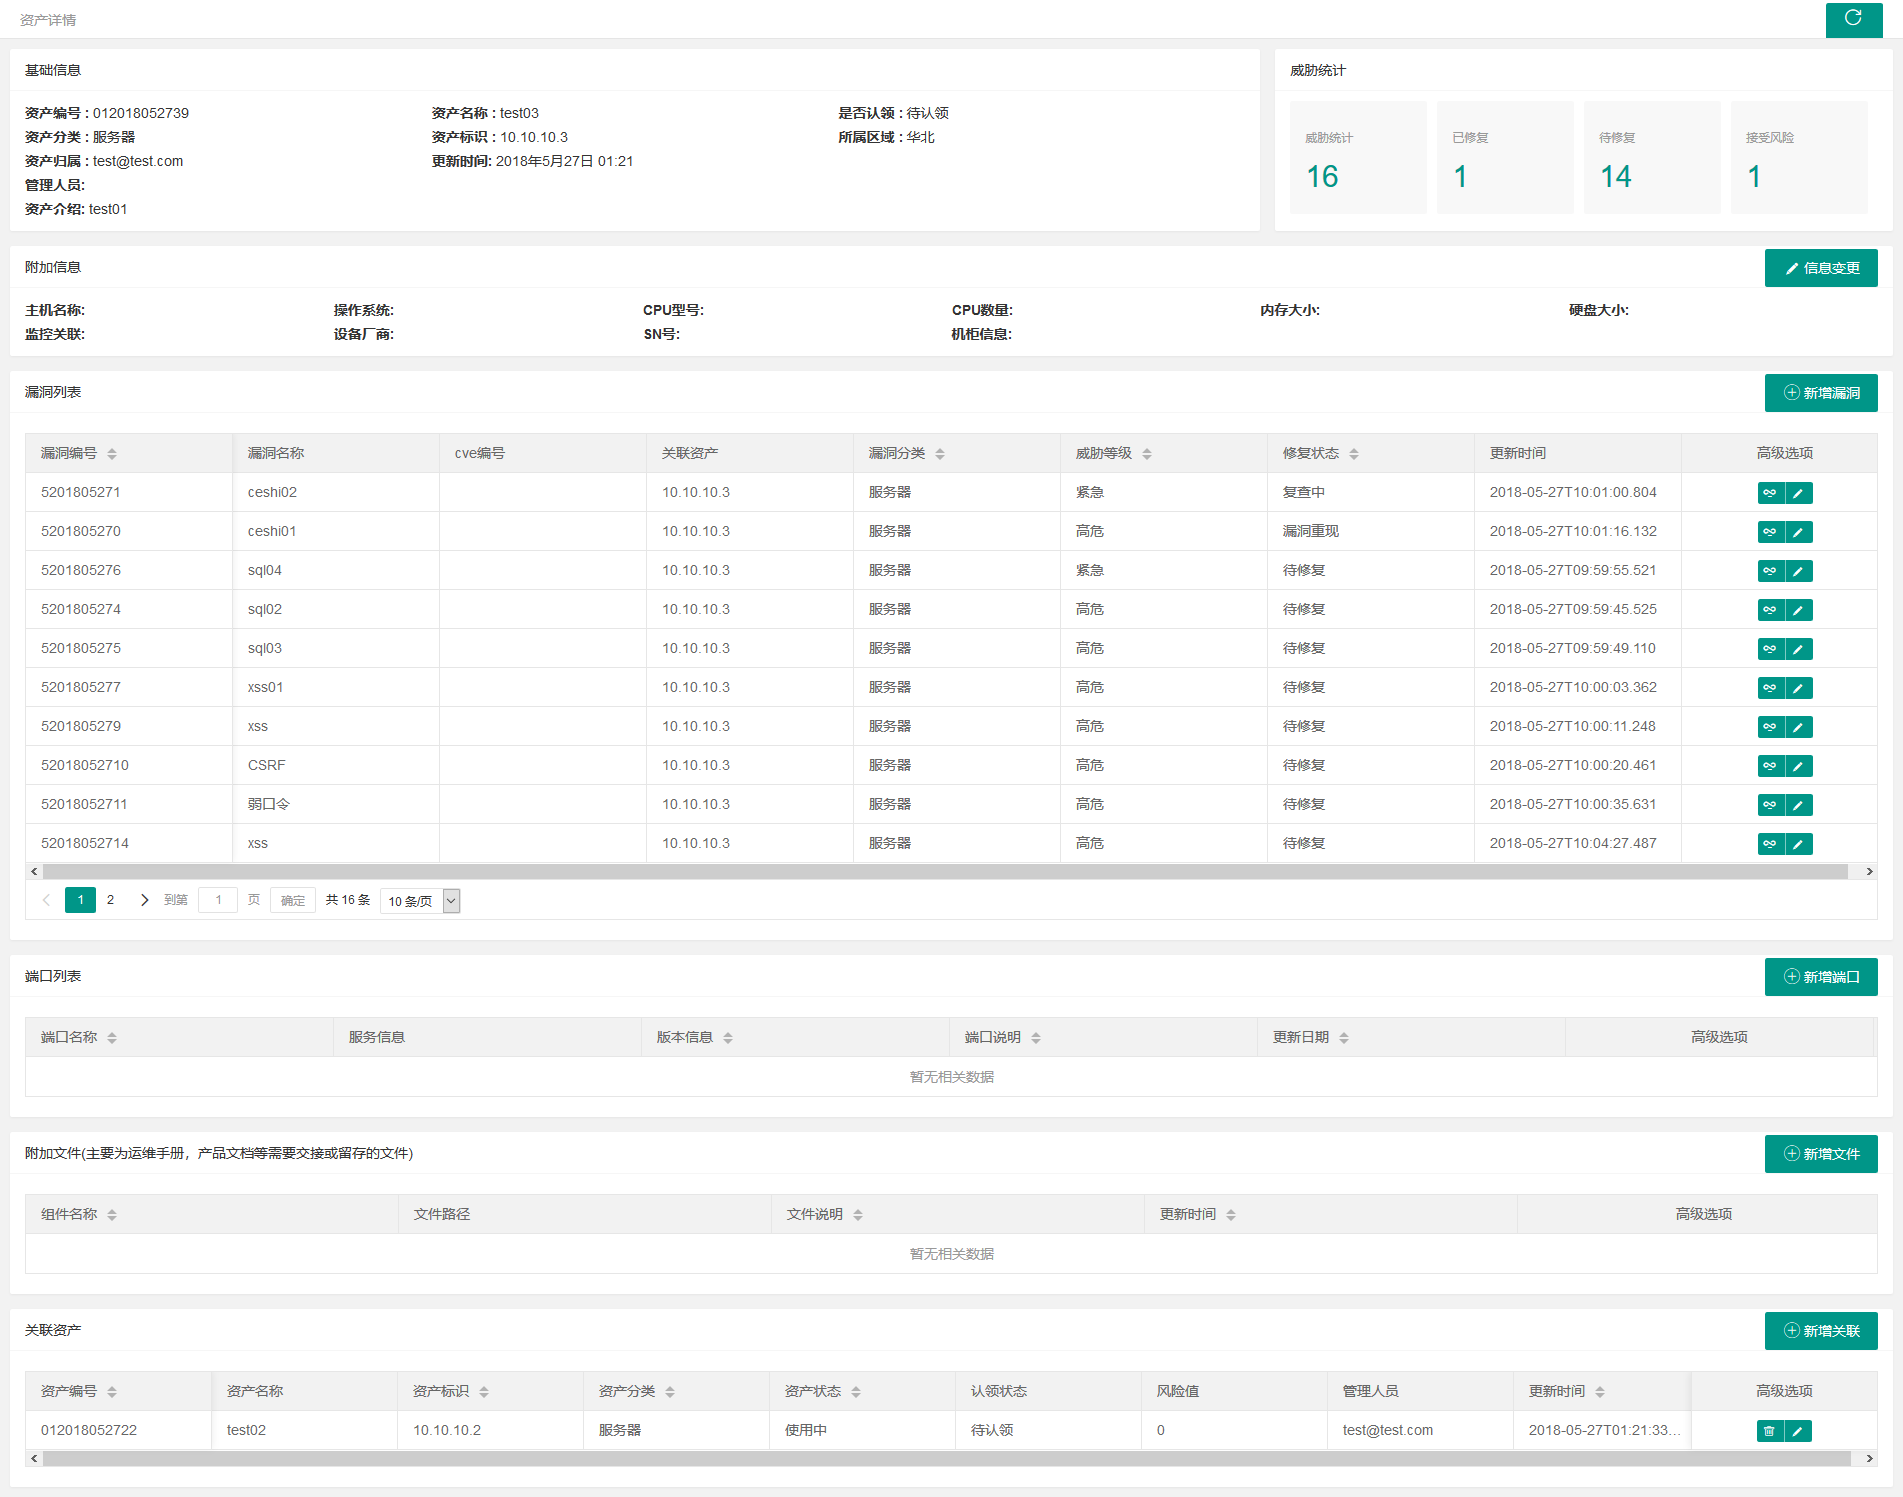 we1h0/securitymanageframwork
Security Manage Framwork is a security management platform for enterprise intranet, which includes asset management, vulnerability management,…
 ethicalhackingplayground/bxss
Blind XSS Scanner is a tool that can be used to scan for blind XSS vulnerabilities in web applications.
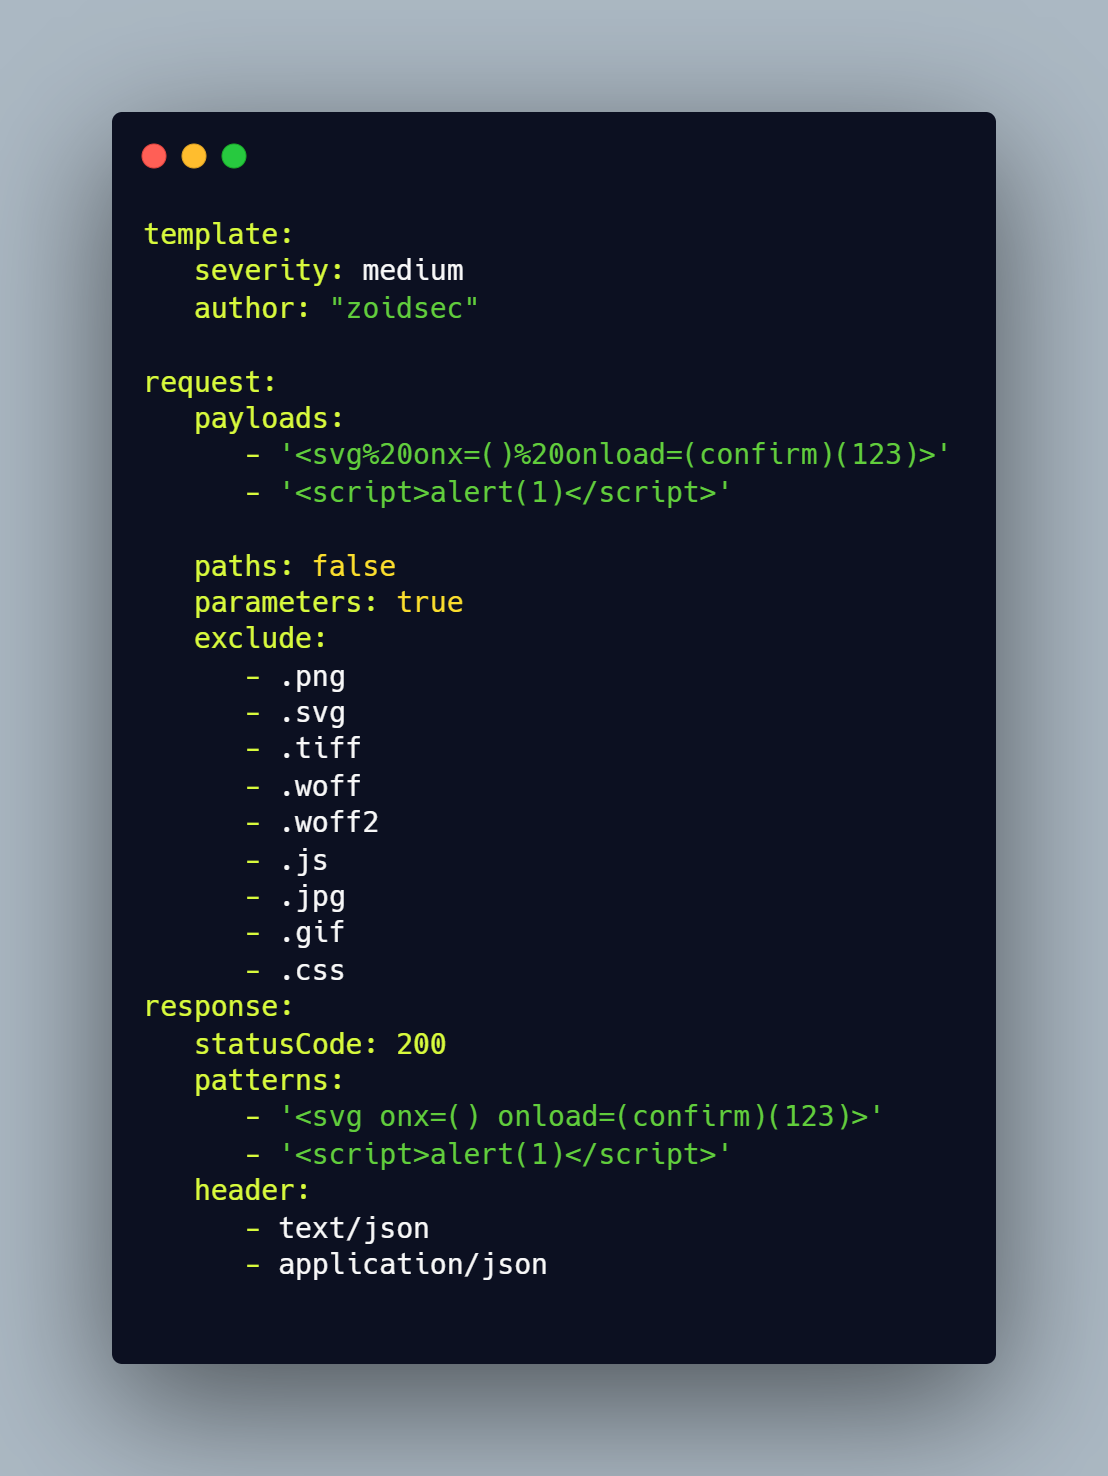 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
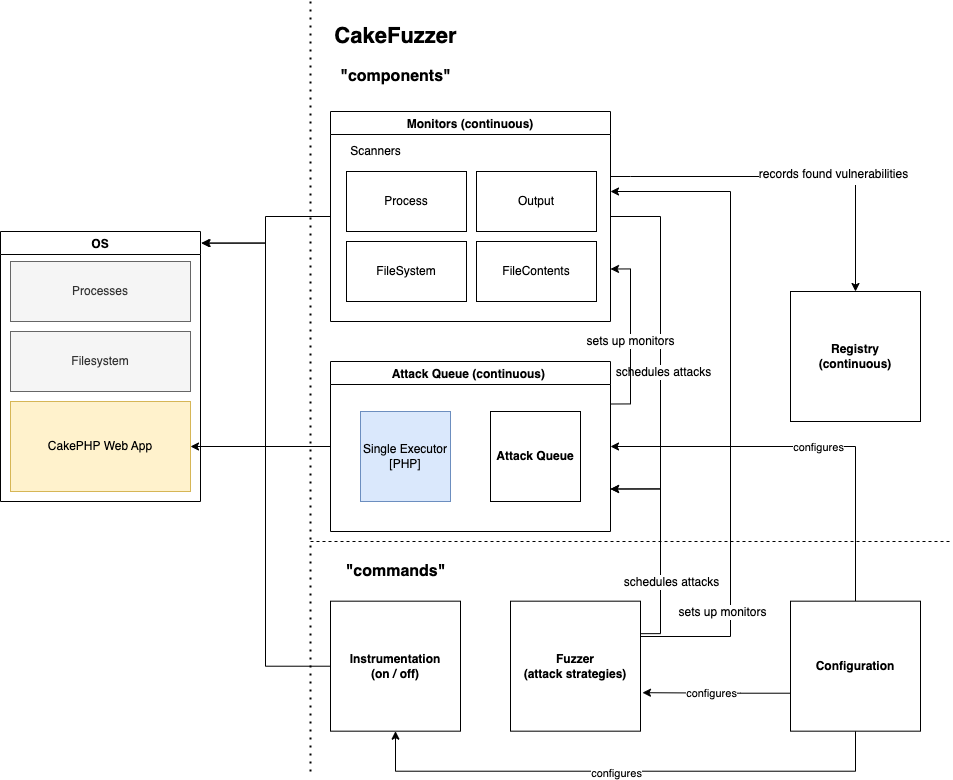 zigrin-security/cakefuzzer
Cake Fuzzer is a project that is meant to help automatically and continuously discover vulnerabilities in web applications created based on specific…
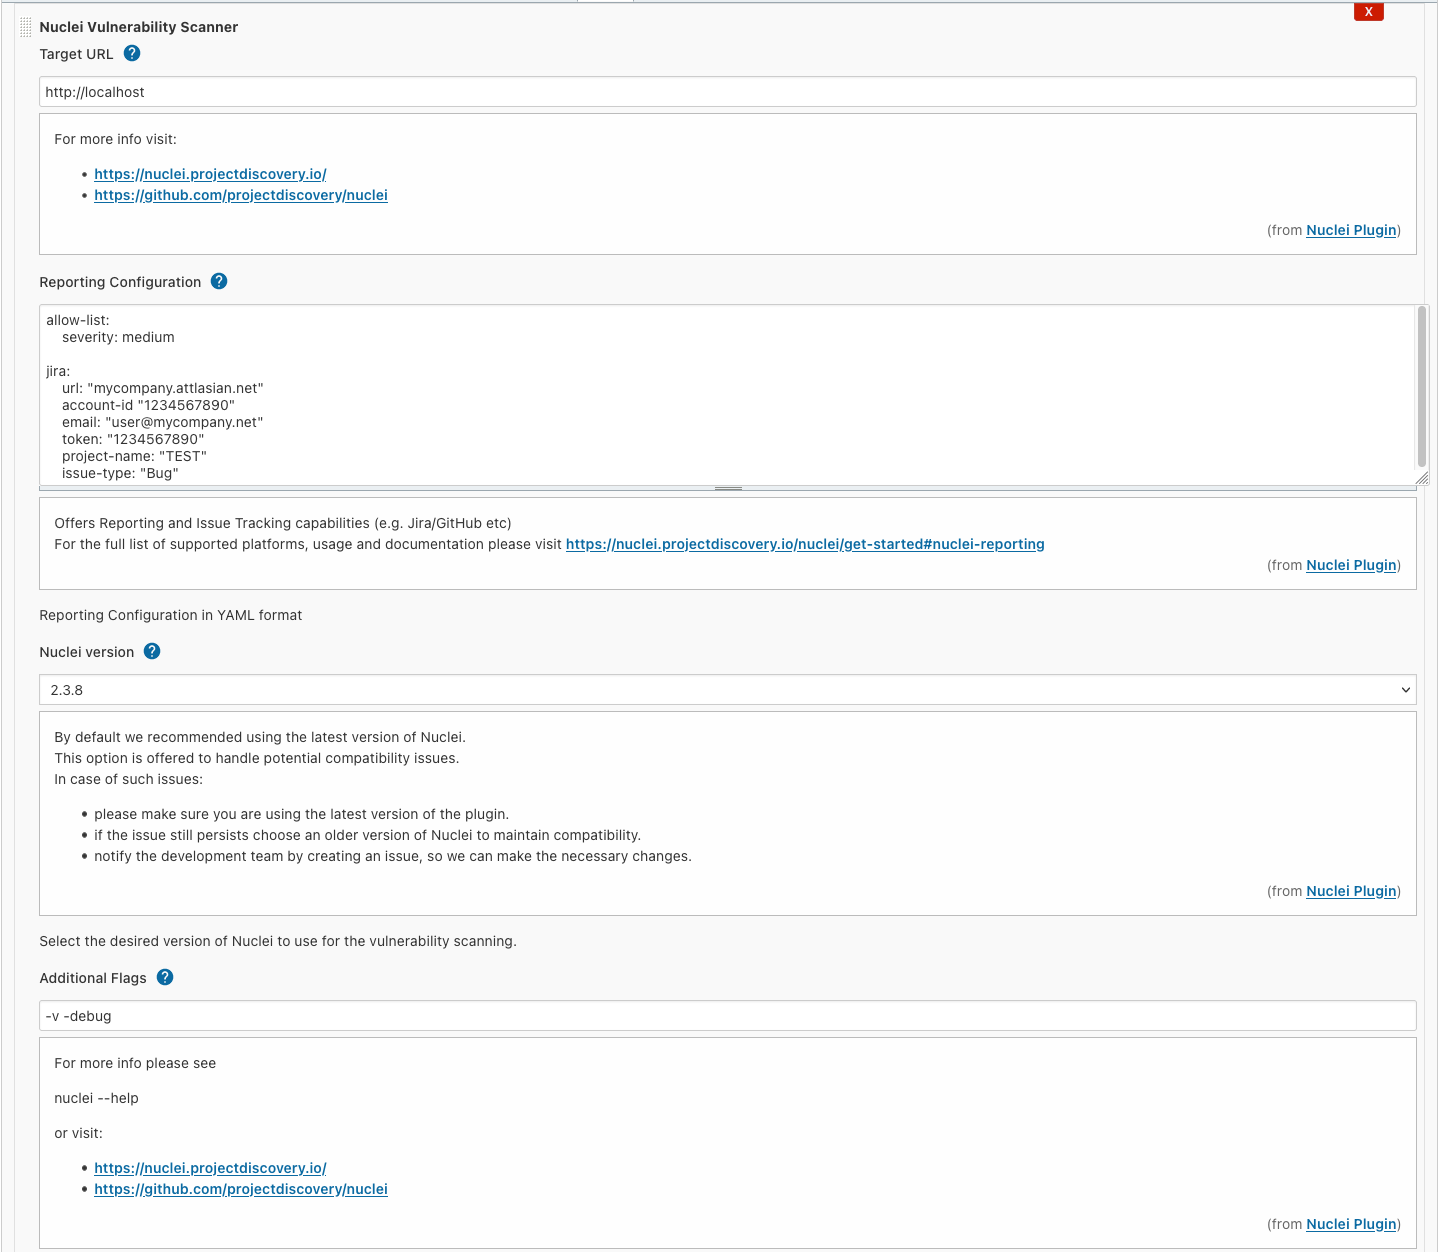 jenkinsci/nuclei-plugin
Nuclei is a fast tool for configurable targeted vulnerability scanning based on templates offering massive extensibility and ease of use.
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 mattb709/cve-2025-24813-scanner
CVE-2025-24813-Scanner is a Python-based vulnerability scanner that detects Apache Tomcat servers vulnerable to CVE-2025-24813, an arbitrary file…
 cappricio-securities/crlfi
This is a tool used by several security researchers to find Carriage Return Line Feed Injection Bug
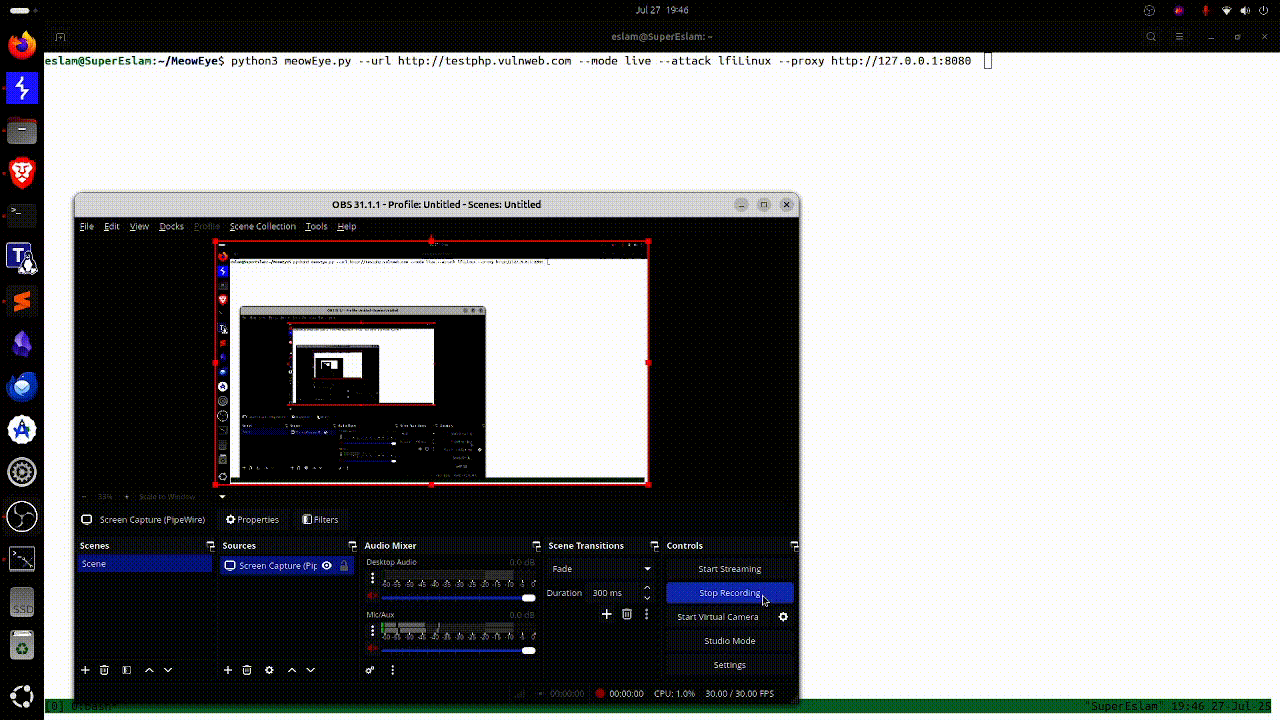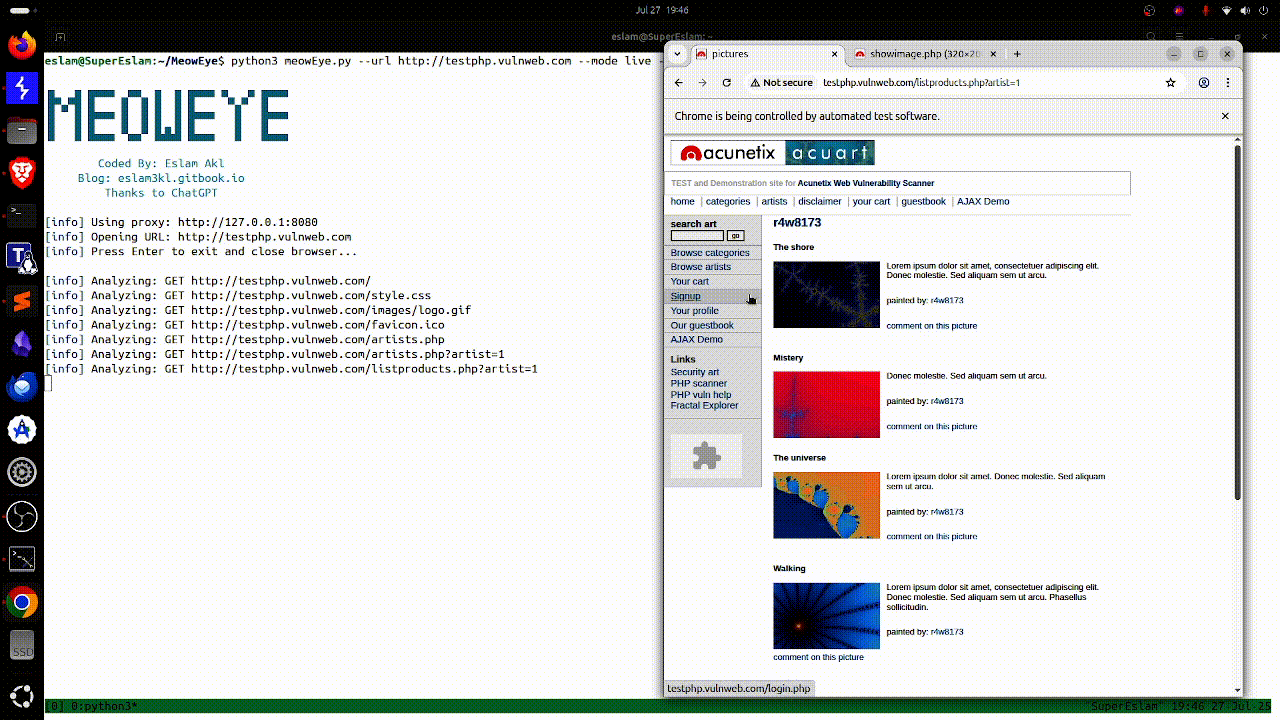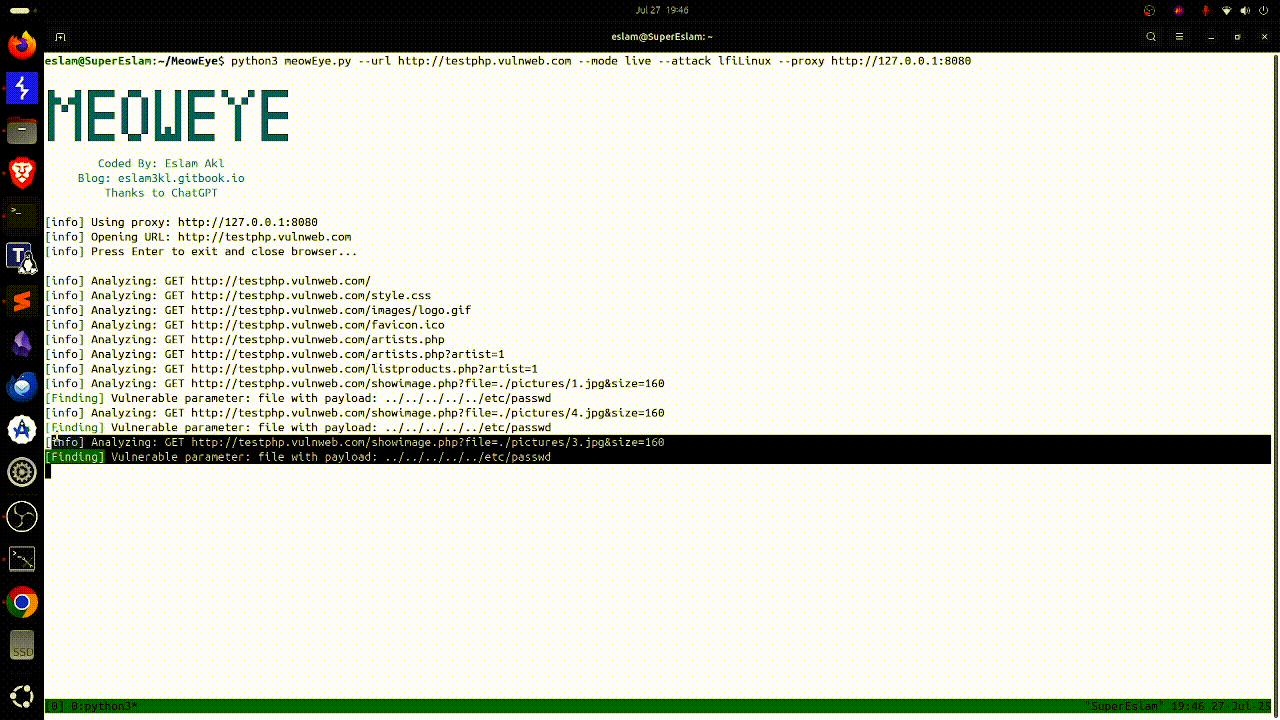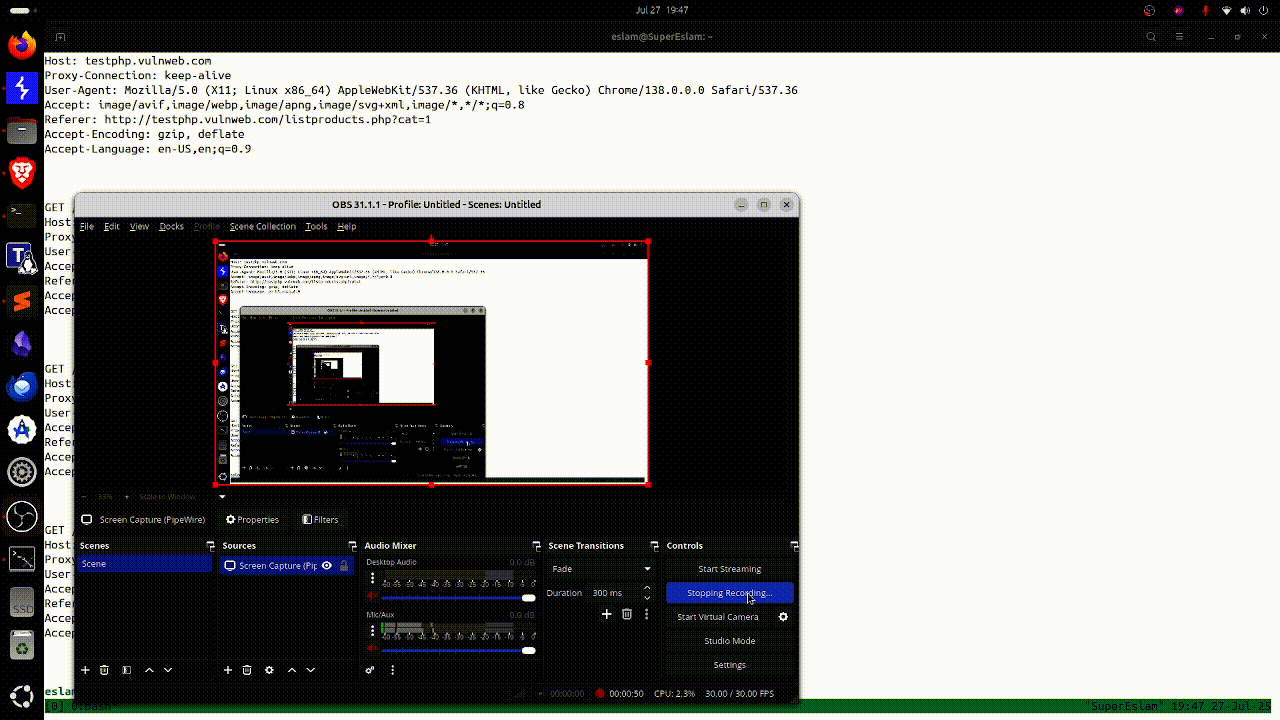 eslam3kl/meoweye
MeowEye is a real-time scanner for identifying multiple web vulnerabilities in live applications.
 rxerium/cve-2025-31324
SAP NetWeaver Visual Composer Metadata Uploader is not protected with a proper authorization, allowing unauthenticated agent to upload potentially…
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
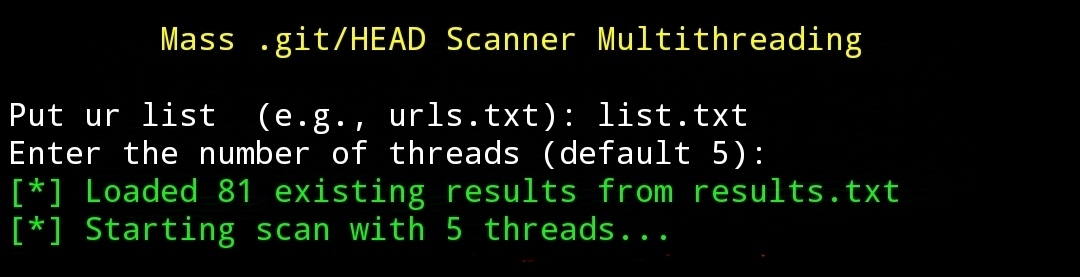 jenderal92/git-scan
This tool is designed to scan and identify whether a website has an exposed ".git" directory, which may contain sensitive information such as source…