
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
w3af preview

w3af

GitHubandresriancho/w3af

Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
6 years ago
scant3r preview

scant3r

GitHubmindpatch/scant3r

Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
penetration-testingscripting-automationvulnerability-scanners+2
6861 day ago
Egyscan preview

Egyscan

GitHubdragonked2/egyscan

Egyscan The Best web vulnerability scanner; it's a multifaceted security powerhouse designed to fortify your web applications against malicious…
crawlerinformation-gatheringpenetration-testing+4
3031 month ago
argumentinjectionhammer preview

argumentinjectionhammer

GitHubnccgroup/argumentinjectionhammer

A Burp Extension designed to identify argument injection vulnerabilities.
api-security-testingpenetration-testingvulnerability-scanners+2
1257 years ago
crlfi-scanner preview

crlfi-scanner

GitHubcappricio-securities/crlfi-scanner

CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…

fuzzingpenetration-testingweb-application-exploitation+2
46 months ago
BurpSuite-For-Pentester preview

BurpSuite-For-Pentester

GitHubignitetechnologies/burpsuite-for-pentester

This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…

authentication-authorizationcurated-resourceseducation+7
2.6k6 months ago
CVE-2024-2997 preview

CVE-2024-2997

GitHublfillaz/cve-2024-2997

The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…

educationexploitationpenetration-testing+3
111 year ago
wp2shell-rce preview

wp2shell-rce

GitHubjohnlodan/wp2shell-rce

WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.
penetration-testingreconnaissancevulnerability-analysis+4
32 months ago
CVE-2024-2997 preview

CVE-2024-2997

GitHub0xuho/cve-2024-2997

The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…
educationexploitationpenetration-testing+3
7 months ago
SQLi_Sleeps preview

SQLi_Sleeps

GitHubhernanrodriguez1/sqli_sleeps

Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
penetration-testingweb-application-exploitationweb-security+1
1251 year ago
SqlMap_BurpSuite preview

SqlMap_BurpSuite

GitHubjas502n/sqlmap_burpsuite

SqlMap_BurpSuite
database-securitypenetration-testingweb-application-exploitation+2
507 years ago
crlf-powered-desync-scanner preview

crlf-powered-desync-scanner

GitHubt0xodile/crlf-powered-desync-scanner

Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…

exploitationpenetration-testingweb-application-exploitation+2
222 months ago
CVE-2026-65540 preview

CVE-2026-65540

GitHubtestardou/cve-2026-65540

Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
exploitationvulnerability-analysisweb-application-exploitation+2
21 days ago
Clickjacking-Exploit-Detector preview

Clickjacking-Exploit-Detector

GitHubjenderal92/clickjacking-exploit-detector

The Clickjacking Exploit Detector uses webpage scanning techniques to identify potential vulnerabilities and provide analysis of those elements.
penetration-testingweb-application-exploitationweb-security+1
34 months ago
WebPort-v1.19.1-Reflected-XSS preview

WebPort-v1.19.1-Reflected-XSS

GitHubemreovunc/webport-v1.19.1-reflected-xss

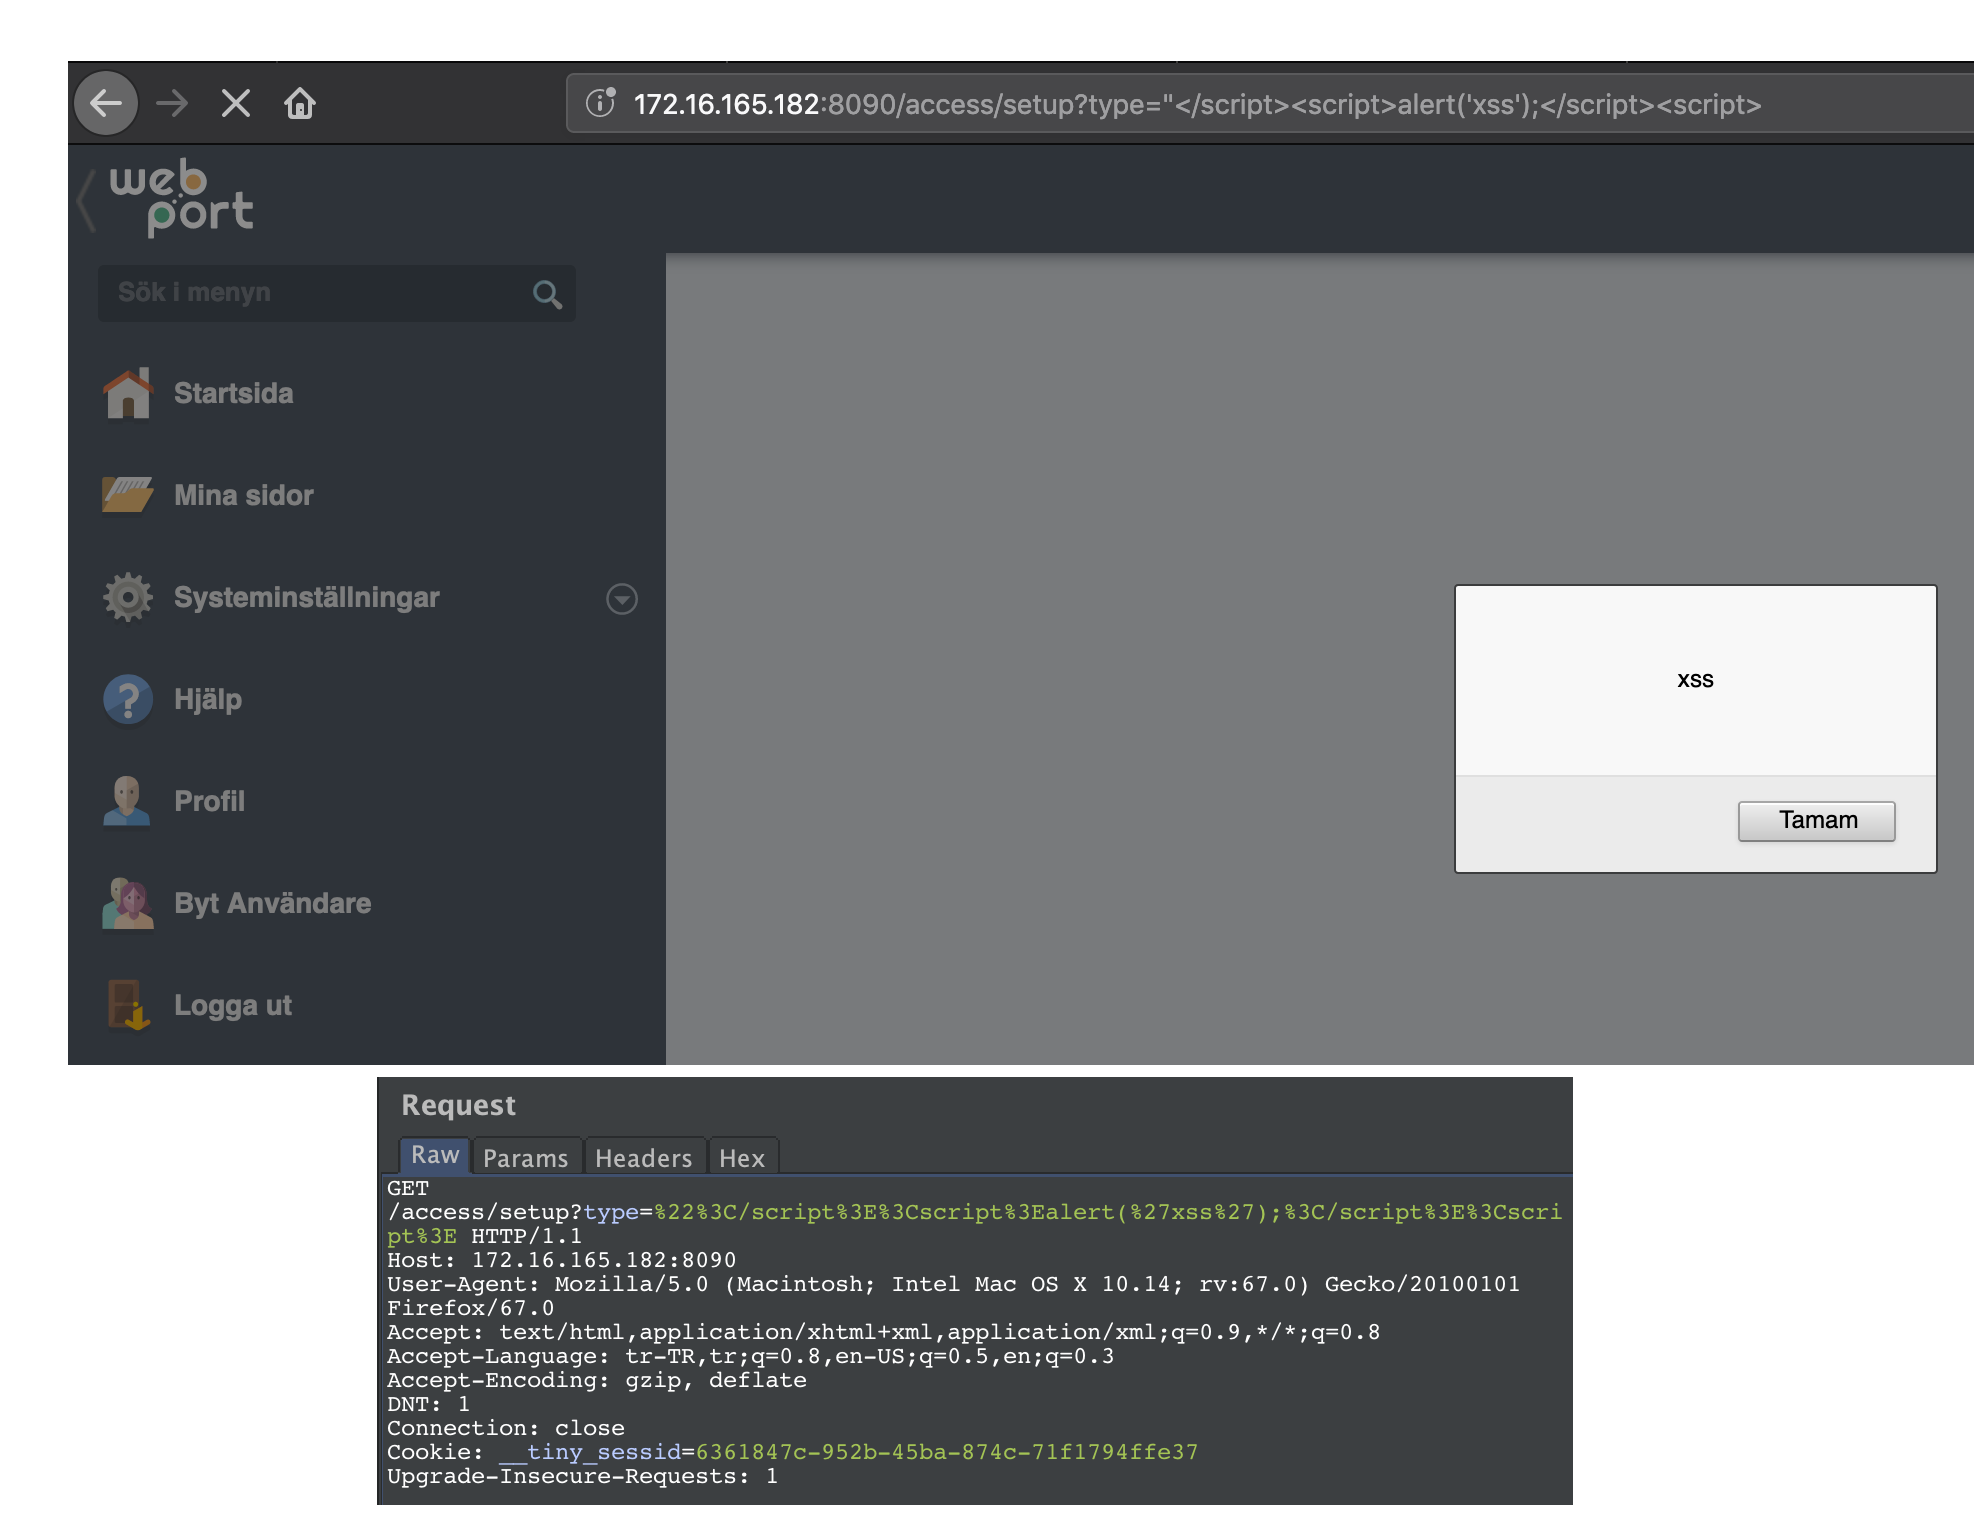
CVE-2019-12460|Reflected XSS in WebPort-v1.19.1 impacts users who open a maliciously crafted link or third-party web page.

exploitationpenetration-testingvulnerability-analysis+2
37 years ago
Vehicle-Service-Management-System-Service-List-Stored-Cross-Site-Scripting-XSS preview

Vehicle-Service-Management-System-Service-List-Stored-Cross-Site-Scripting-XSS

GitHubsanupl/vehicle-service-management-system-service-list-stored-cross-site-scripting-xss

CVE-2021-46072 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Service List Section in…
exploitationpenetration-testingvulnerability-analysis+3
14 months ago
CVE-2024-38856-ApacheOfBiz preview

CVE-2024-38856-ApacheOfBiz

GitHubgraysignal/cve-2024-38856-apacheofbiz

Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
exploitationvulnerability-analysisweb-application-exploitation+1
12 years ago
aem-xss preview

aem-xss

GitHubcappricio-securities/aem-xss

Adobe Experience Manager Childlist Selector - Cross-Site Scripting

penetration-testingweb-application-exploitationweb-vulnerability-scanners
12 years ago
Previous12Next