
lulzbuster
 noptrix/lulzbuster
A multithreaded, very fast and smart HTTP(S) directory and file bruteforcer written in C on top of libcurl
fuzzinginformation-gatheringpenetration-testing+3
141
noptrix/lulzbusterA multithreaded, very fast and smart HTTP(S) directory and file bruteforcer written in C on top of libcurl
 skavngr/rapidscan
:new: The Multi-Tool Web Vulnerability Scanner.
 h4r5h1t/webcopilot
An automation tool that enumerates subdomains then filters out xss, sqli, open redirect, lfi, ssrf and rce parameters and then scans for…
 stefanoj3/dirstalk
Modern alternative to dirbuster/dirb

 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 sleepingbag945/dddd
Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…
 nccgroup/webfeet
Web Filter External Enumeration Tool (WebFEET)
 flenz00/cve-2026-18110-poc
Python PoC and Nuclei template exploiting CVE-2026-18110, an unauthenticated user enumeration flaw in Concrete CMS 9.0.0-9.5.2 via the user…
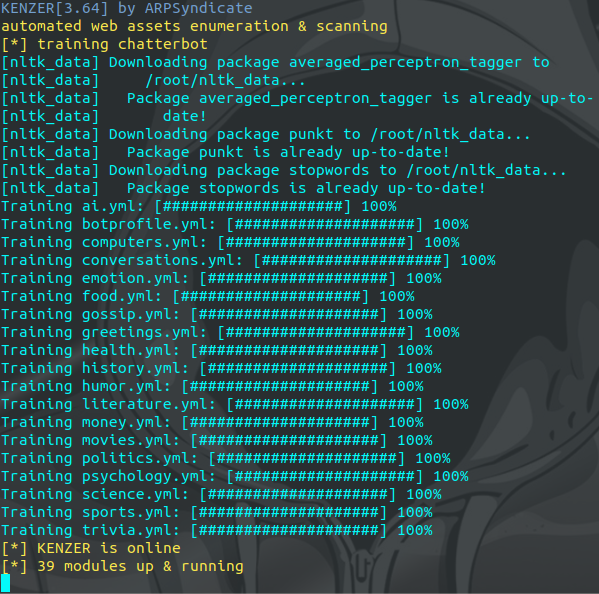 arpsyndicate/kenzer
automated web assets enumeration & scanning [DEPRECATED]
 stanislav-web/opendoor
OWASP Web Recon & Directory Discovery Platform
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
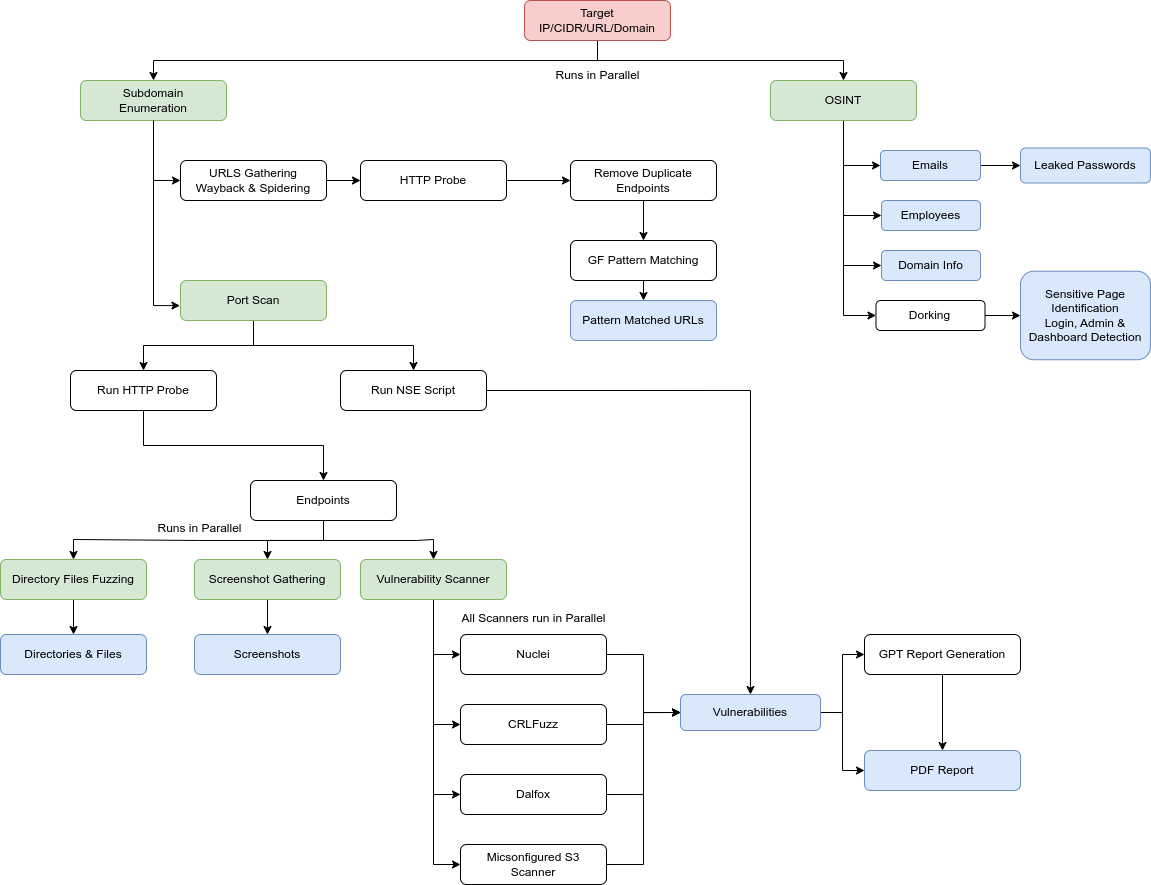
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 yogeshojha/rengine
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…