

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
31 results
w3af preview

w3af

GitHubandresriancho/w3af

Open-source web application security scanner that identifies and exploits 200+ vulnerabilities including XSS, SQL injection, and OS commanding.…
exploitationpenetration-testingvulnerability-scanners+3
4.9k
6 years ago
crlfi-scanner preview

crlfi-scanner

GitHubcappricio-securities/crlfi-scanner

CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
fuzzingpenetration-testingweb-application-exploitation+2
47 months ago
SQLi_Sleeps preview

SQLi_Sleeps

GitHubhernanrodriguez1/sqli_sleeps

Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
penetration-testingweb-application-exploitationweb-security+1
1261 year ago
crlf-powered-desync-scanner preview

crlf-powered-desync-scanner

GitHubt0xodile/crlf-powered-desync-scanner

Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
exploitationpenetration-testingweb-application-exploitation+2
233 months ago
CVE-2026-18143 preview

CVE-2026-18143

GitHubwayang1337/cve-2026-18143

Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup

exploitationvulnerability-analysisweb-application-exploitation+2
23 days ago
CVE-2026-65540 preview

CVE-2026-65540

GitHubtestardou/cve-2026-65540

Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
exploitationvulnerability-analysisweb-application-exploitation+2
1 month ago
CVE-2024-38856-ApacheOfBiz preview

CVE-2024-38856-ApacheOfBiz

GitHubgraysignal/cve-2024-38856-apacheofbiz

Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
exploitationvulnerability-analysisweb-application-exploitation+1
12 years ago
CVE-2024-55982 preview

CVE-2024-55982

GitHubrandomrobbiebf/cve-2024-55982

Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
database-securitypenetration-testingvulnerability-analysis+3
11 year ago
WebPort-v1.19.1-Reflected-XSS preview

WebPort-v1.19.1-Reflected-XSS

GitHubemreovunc/webport-v1.19.1-reflected-xss

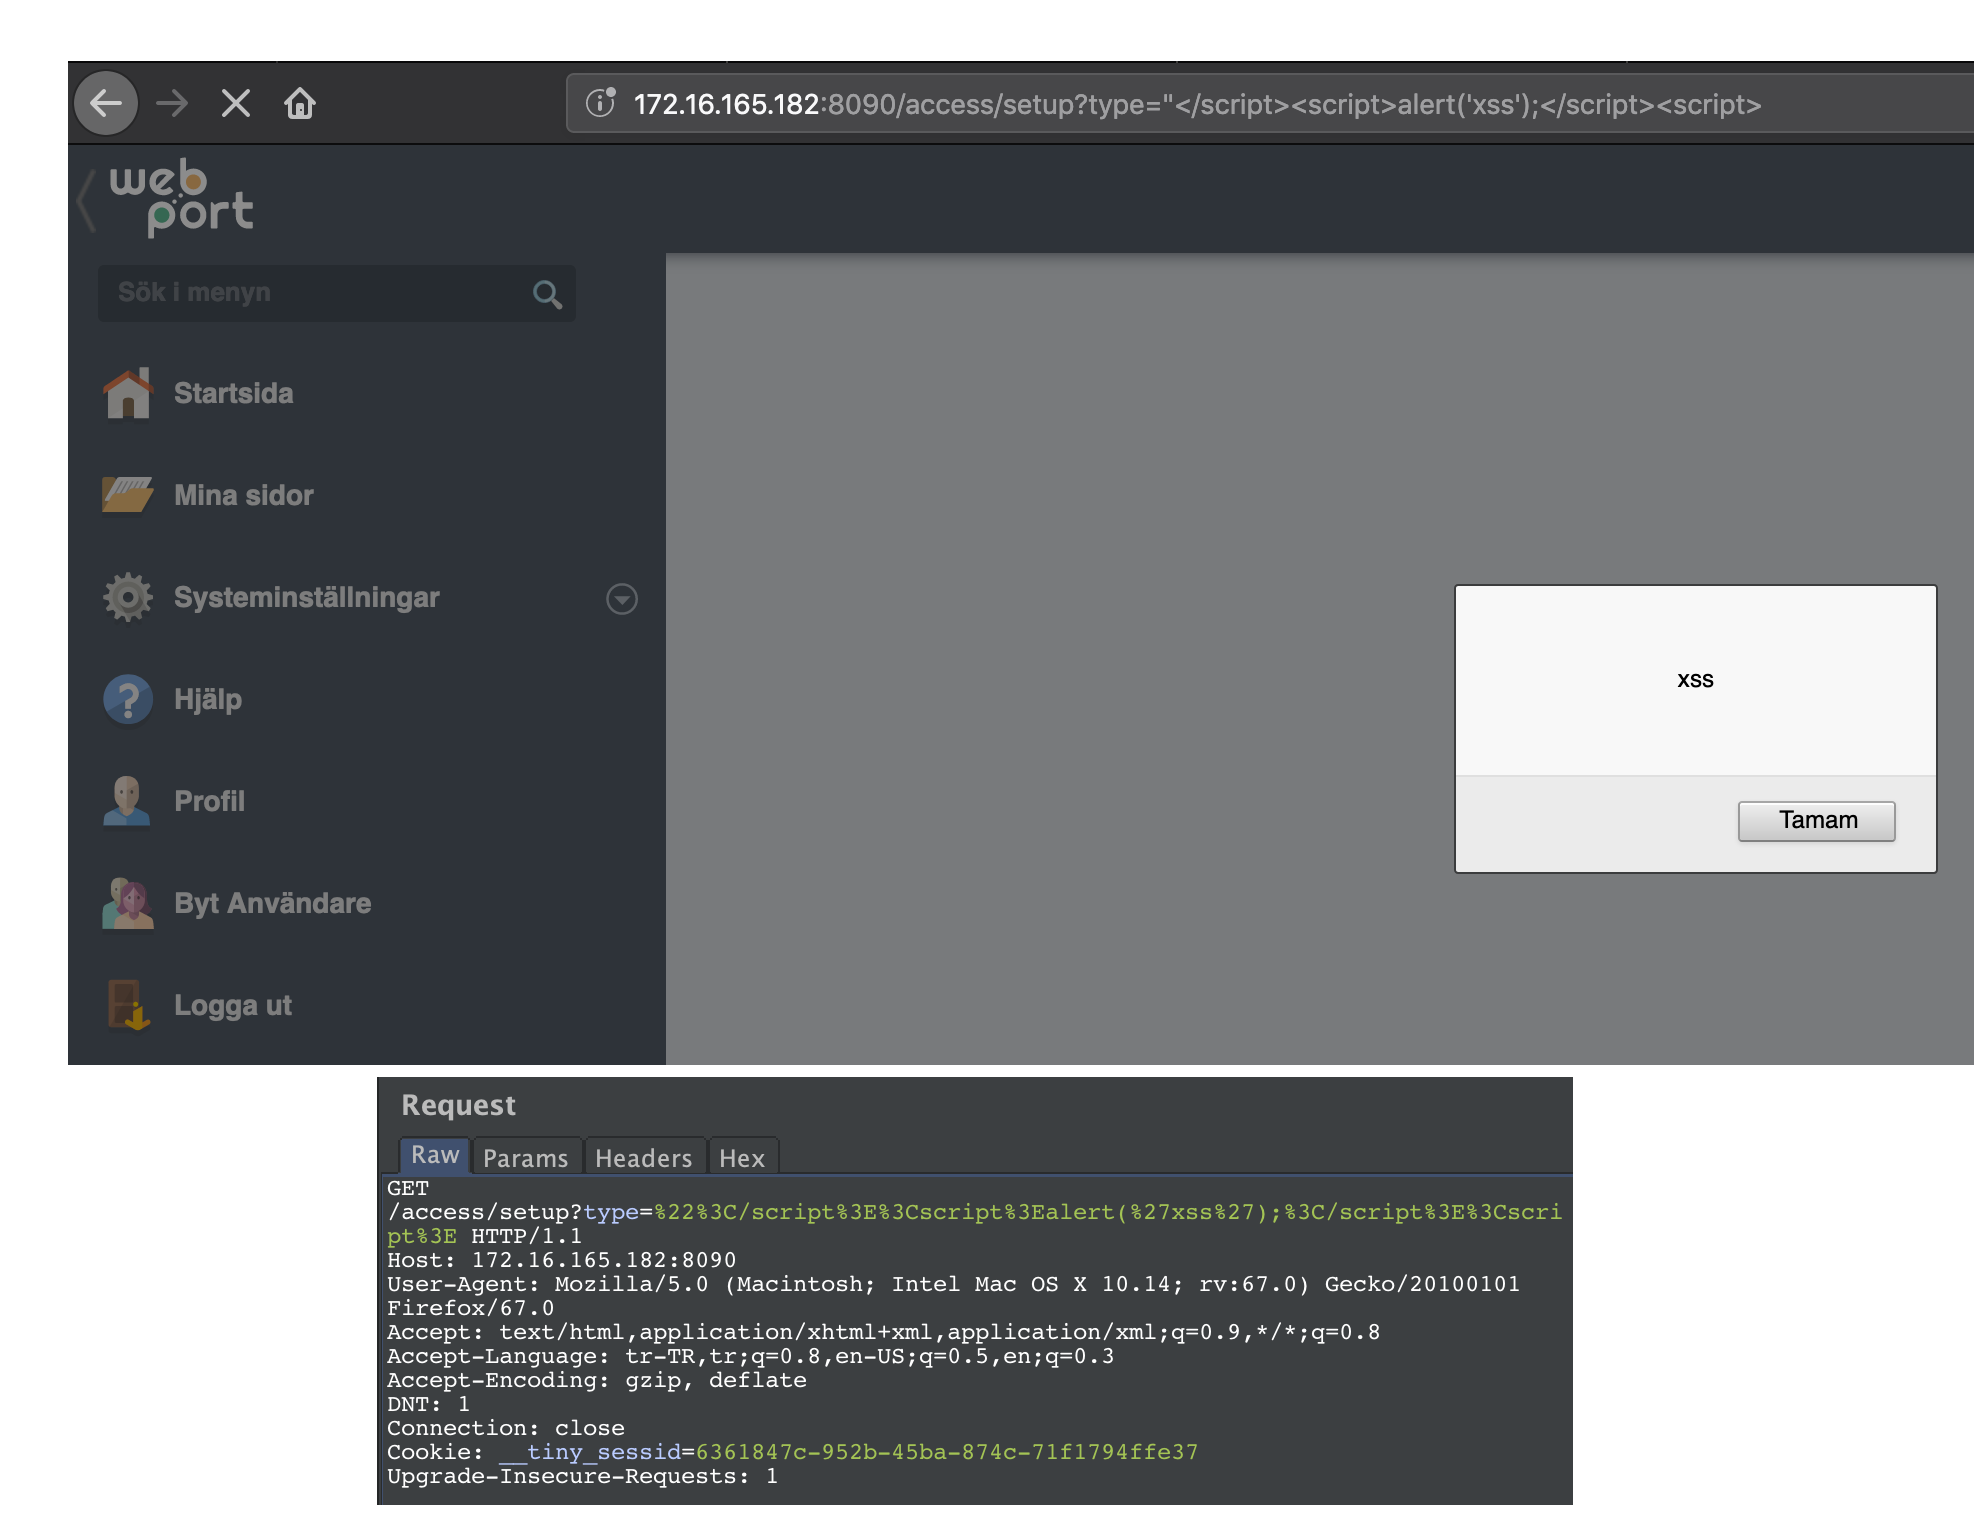
CVE-2019-12460|Reflected XSS in WebPort-v1.19.1 impacts users who open a maliciously crafted link or third-party web page.
exploitationpenetration-testingvulnerability-analysis+2
37 years ago
Vehicle-Service-Management-System-Service-List-Stored-Cross-Site-Scripting-XSS preview

Vehicle-Service-Management-System-Service-List-Stored-Cross-Site-Scripting-XSS

GitHubsanupl/vehicle-service-management-system-service-list-stored-cross-site-scripting-xss

CVE-2021-46072 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Service List Section in…
exploitationpenetration-testingvulnerability-analysis+3
15 months ago
Vehicle-Service-Management-System-Mechanic-List-Stored-Cross-Site-Scripting-XSS preview

Vehicle-Service-Management-System-Mechanic-List-Stored-Cross-Site-Scripting-XSS

GitHubsanupl/vehicle-service-management-system-mechanic-list-stored-cross-site-scripting-xss

CVE-2021-46069 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Mechanic List Section in…
exploitationpenetration-testingvulnerability-analysis+3
5 months ago
Vehicle-Service-Management-System-Settings-Stored-Cross-Site-Scripting-XSS preview

Vehicle-Service-Management-System-Settings-Stored-Cross-Site-Scripting-XSS

GitHubsanupl/vehicle-service-management-system-settings-stored-cross-site-scripting-xss

CVE-2021-46074 - A Stored Cross Site Scripting (XSS) vulnerability exists in Sourcecodester Vehicle Service Management System 1.0 via the Settings…
exploitationpenetration-testingvulnerability-analysis+2
5 months ago
0xMiddleware preview

0xMiddleware

GitHubev3rpalestine/0xmiddleware

CVE-2025-29927: Next.js Middleware Exploit

authenticationexploitationpenetration-testing+3
1 year ago
BurpSuite-For-Pentester preview

BurpSuite-For-Pentester

GitHubignitetechnologies/burpsuite-for-pentester

This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
authentication-authorizationcurated-resourceseducation+7
2.6k7 months ago
WAES preview

WAES

GitHubshiva108/waes

CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result
ctfeducationinformation-gathering+7
709 months ago
SecurityManageFramwork preview

SecurityManageFramwork

GitHubwe1h0/securitymanageframwork

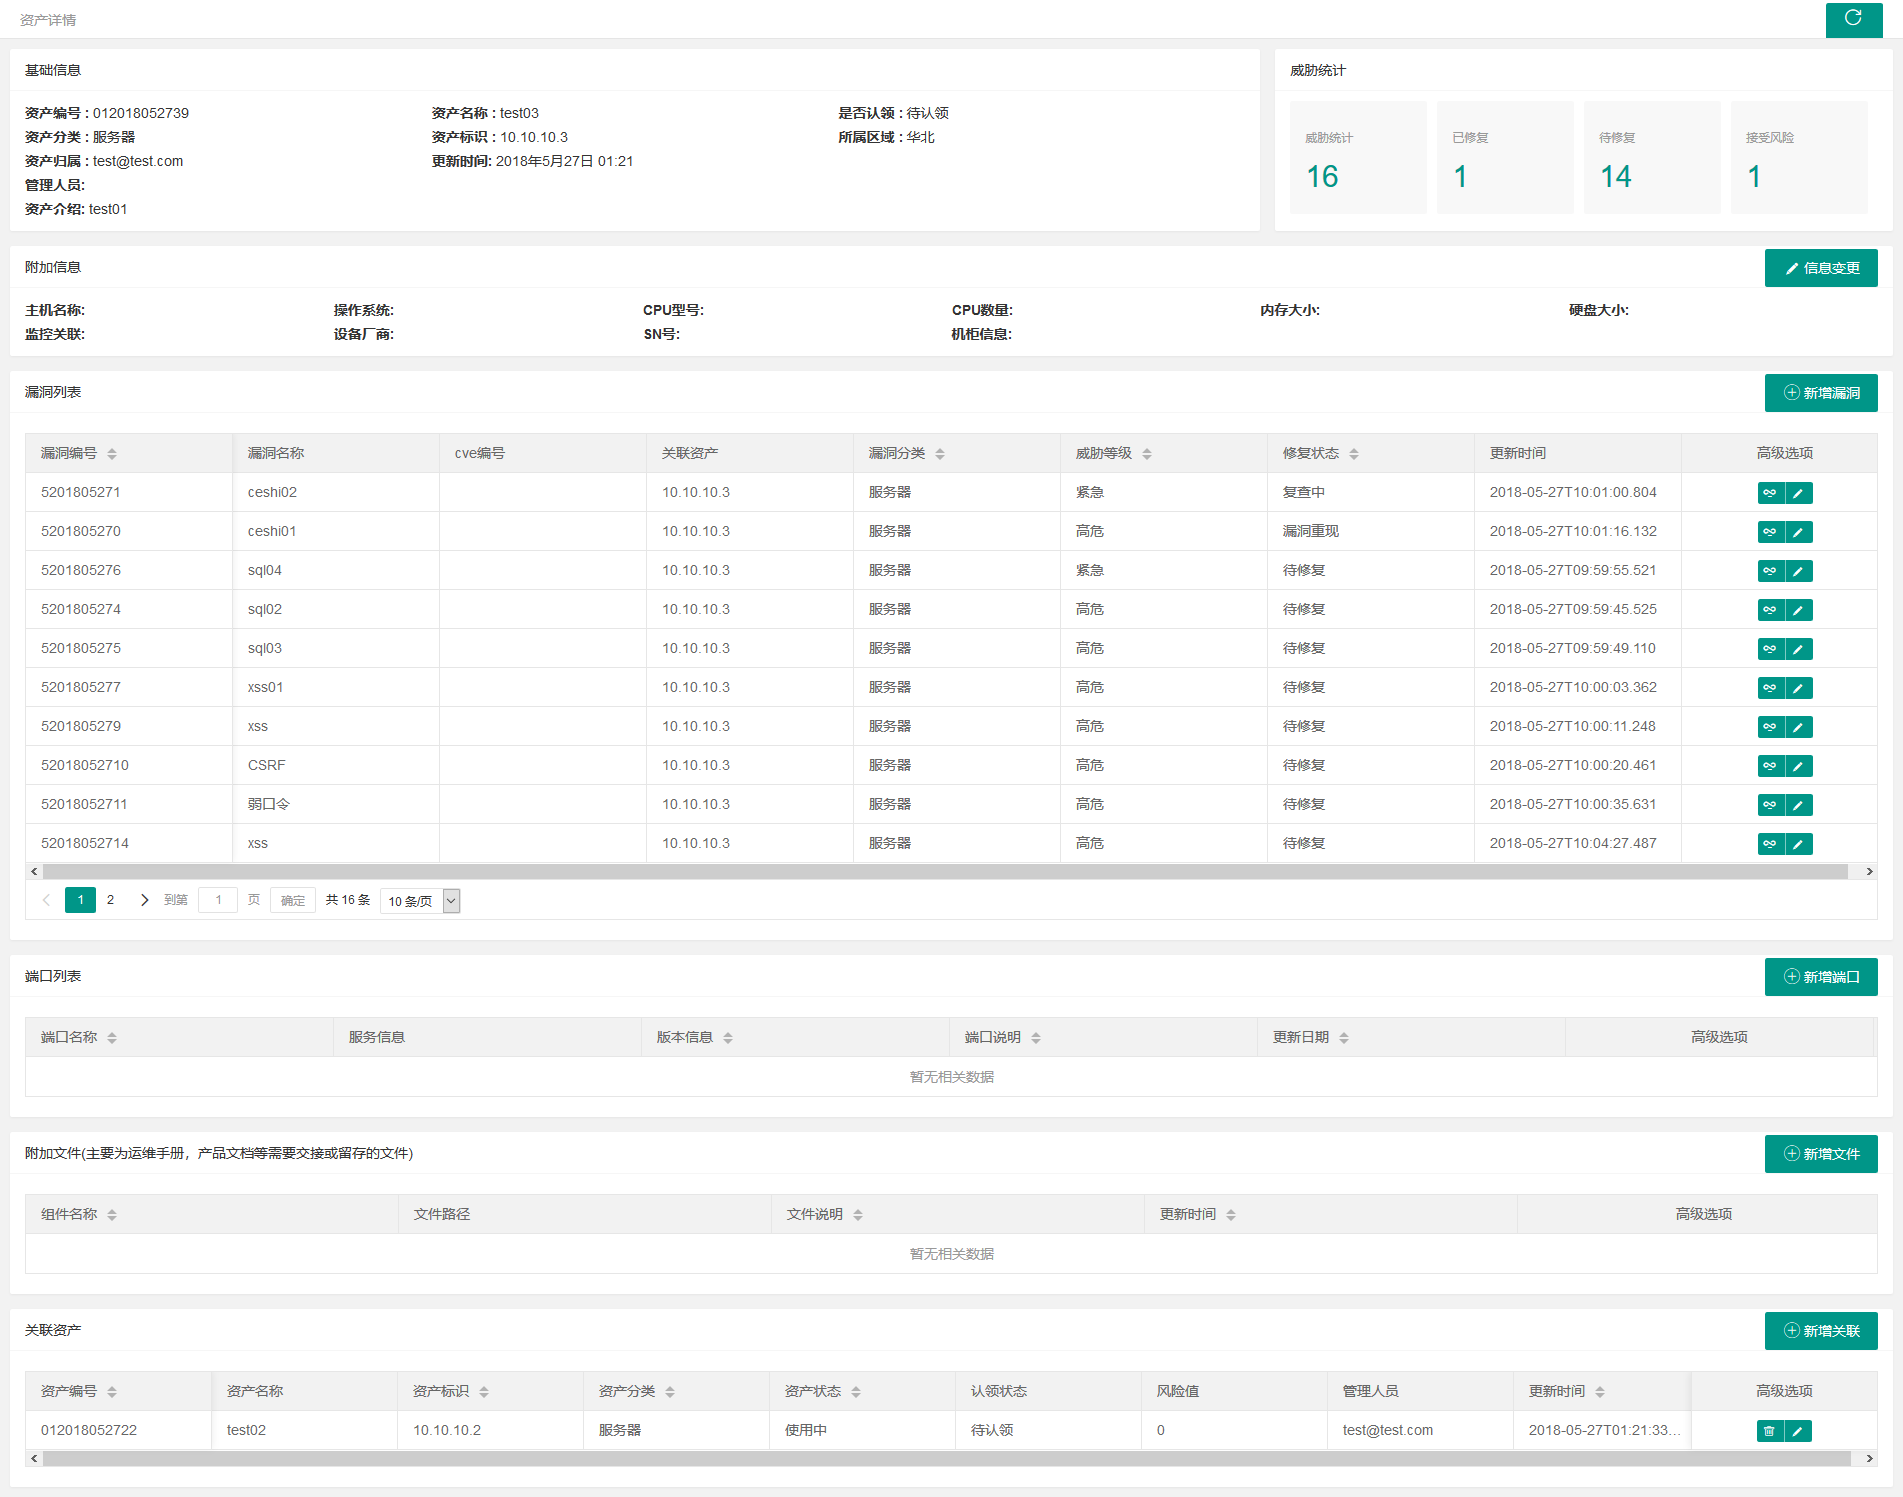
Security Manage Framwork is a security management platform for enterprise intranet, which includes asset management, vulnerability management,…
configuration-auditingnetwork-mappingpassword-cracking+4
4306 years ago
scant3r preview

scant3r

GitHubmindpatch/scant3r

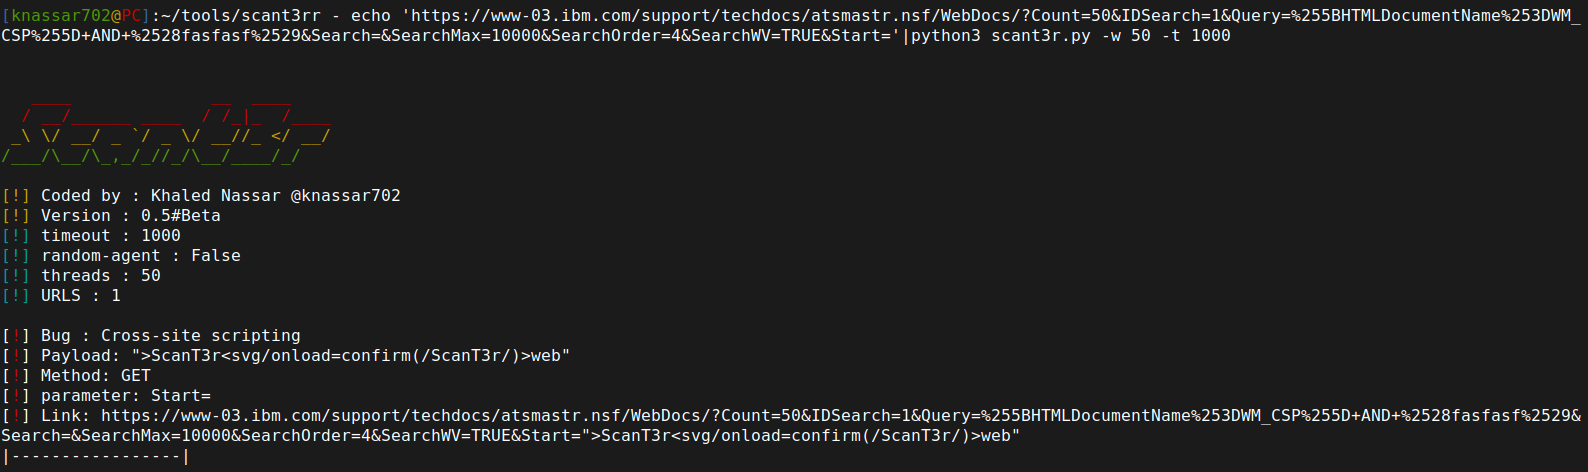
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
penetration-testingscripting-automationvulnerability-scanners+2
68617 days ago
CVE-2025-25163-Nuclei-Template preview

CVE-2025-25163-Nuclei-Template

GitHubrootharpy/cve-2025-25163-nuclei-template

This repository features a Nuclei template specifically designed to detect the Path Traversal vulnerability (CVE-2025-25163) in the Plugin A/B Image…

exploitationinformation-gatheringpenetration-testing+3
11 year ago
Previous12Next