
vulmap
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
exploitationpenetration-testingvulnerability-analysis+1
3.5k
zhzyker/vulmapWeb vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
 ev3rpalestine/0xmiddleware
CVE-2025-29927: Next.js Middleware Exploit
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 elsanose01/cve-2021-43798-grafana-path-traversal-tester
Automated path traversal testing tool for Grafana plugin endpoints using curl and Bash.
 call123x/-cve-2025-55182
cve-2025-55182
 sqlmapproject/sqlmap
Automatic SQL injection and database takeover tool
 mrmtwoj/apache-vulnerability-testing
Apache HTTP Server Vulnerability Testing Tool | PoC for CVE-2024-38472 , CVE-2024-39573 , CVE-2024-38477 , CVE-2024-38476 , CVE-2024-38475 ,…
 talha1112/fyp
Desktop-based vulnerability assessment tool for security teams — scan web apps & networks, detect CVEs, map exploits, auto-score risk, and generate…
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
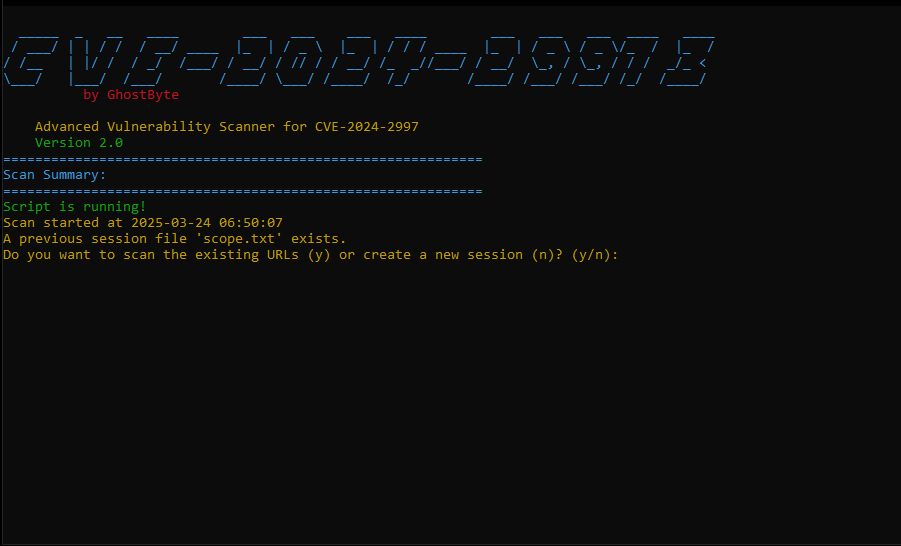 o9-9/cve-2024-2997
The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…
 xuemian168/cve-2025-30208
全网首发 CVE-2025-31125 CVE-2025-30208 CVE-2025-32395 Vite Scanner
 orwagodfather/react2shell-scanner
RSC/Next.js RCE (CVE-2025-55182 & CVE-2025-66478)
 inteleon404/cve-2025-0133
Reflected XSS vulnerability found in Palo Alto GlobalProtect Gateway & Portal. Attackers can inject malicious scripts via crafted requests.
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 0xkr1x/cve-2025-53770-scanner
🎯 Vulnerability scanner for SharePoint servers affected by CVE-2025-53770. Detects unsafe deserialization using ToolPane.aspx with a crafted…
 0xans/cve-2024-24919
Scans web applications for CVE-2024-24919 vulnerabilities via CLI, supporting a single target or wordlist-based bulk URL scanning.