

phpinfo-files-leaks
 cappricio-securities/phpinfo-files-leaks
This tool is used to find php info page
information-gatheringmisconfigurationpenetration-testing+4
1
cappricio-securities/phpinfo-files-leaksThis tool is used to find php info page
 cappricio-securities/cve-2020-3452
Cisco Adaptive Security Appliance (ASA)/Firepower Threat Defense (FTD) - Local File Inclusion
 gotr00t0day/cve-2025-68461
A C++ security scanner tool to detect Cross-Site Scripting (XSS) vulnerabilities in Roundcube Webmail installations.
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking
 hood3drob1n/bingoo
BinGoo! A Linux bash based Bing and Google Dorking Tool
 amkkk221/cve-2025-43990-magento-rce
Magento APSB25-94 Unauthenticated File Upload to RCE (CVE-2026-XXXX) - Eval Shell + Probe Scanner
 karthi-the-hacker/cve-2021-31589
Lightweight CLI scanner for CVE-2021-31589 that checks single or multiple URLs for the vulnerability, outputting results to a file for bug bounty and…
 rxerium/cve-2025-52691
Detection for CVE-2025-52691
 karthi-the-hacker/cve-2006-2842
CLI scanner for CVE-2006-2842 (PHP include() path truncation) vulnerability. Scans single or multiple URLs to detect this specific web application…
 shoucheng3/spring-cloud__spring-cloud-gateway_cve-2022-22947_3-0-6
Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.
 mattb709/cve-2025-24813-scanner
CVE-2025-24813-Scanner is a Python-based vulnerability scanner that detects Apache Tomcat servers vulnerable to CVE-2025-24813, an arbitrary file…
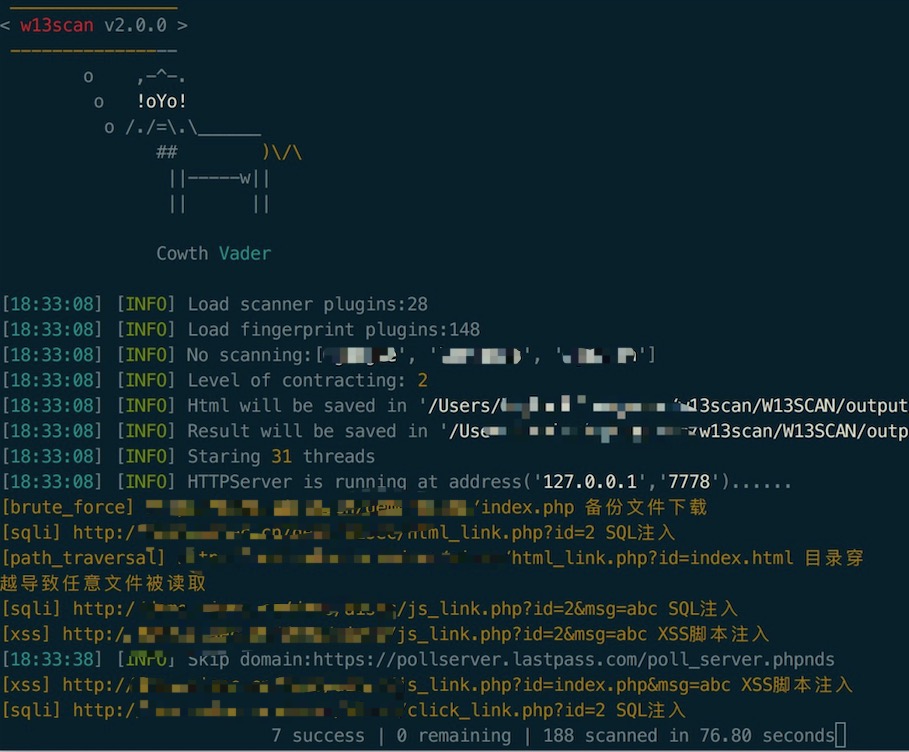 w-digital-scanner/w13scan
Passive and active web vulnerability scanner with plugin-based detection for XSS, SQL injection, command injection, and sensitive file disclosure.…
 jenderal92/cve-2024-10508
This tool scans WordPress sites for vulnerabilities in the "RegistrationMagic" plugin (CVE-2024-10508). It checks for the presence of a specific…
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 isee857/cve-2024-9047-poc
WordPress File Upload插件任意文件读取漏洞(CVE-2024-9047)批量检测脚本
 shinthink/cve-2026-63223
CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…
 agampreet-singh/cve-2024-25202
A vulnerability was found in PHPgurukul visitor management system 1.0. it has been rated as problemic. Affected by the issue is some unknown…
 huseyinstif/cve-2024-28995-nuclei-template
Nuclei template for detecting CVE-2024-28995, a directory traversal vulnerability in Serv-U FTP server, enabling file read via crafted HTTP requests.