
goWAPT
 dzonerzy/gowapt
Go Web Application Penetration Test
fuzzingpenetration-testingscripting-automation+4
dzonerzy/gowaptGo Web Application Penetration Test
 yogeshojha/rengine
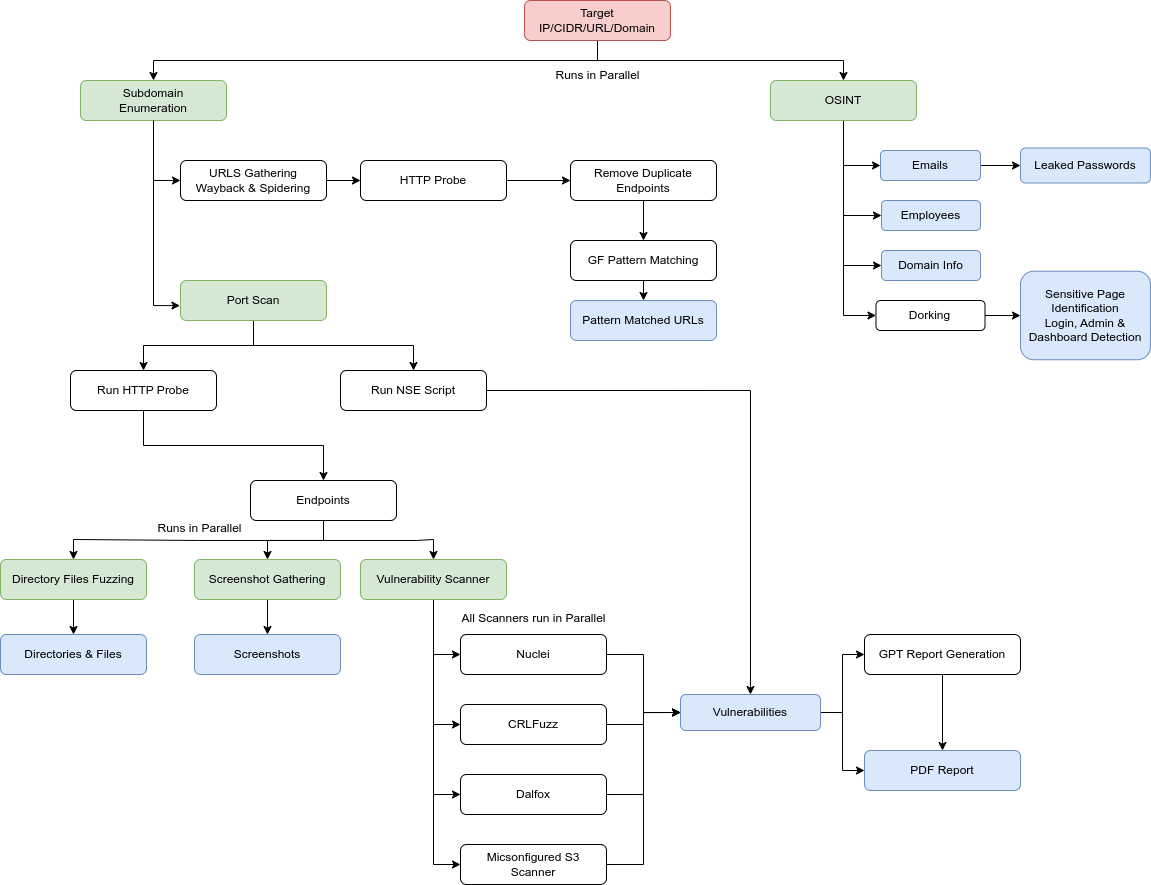
reNgine is an automated reconnaissance framework for web applications with a focus on highly configurable streamlined recon process via Engines,…
 bugcrowd/hunt
Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 awarexone/agentic-bug-hunter
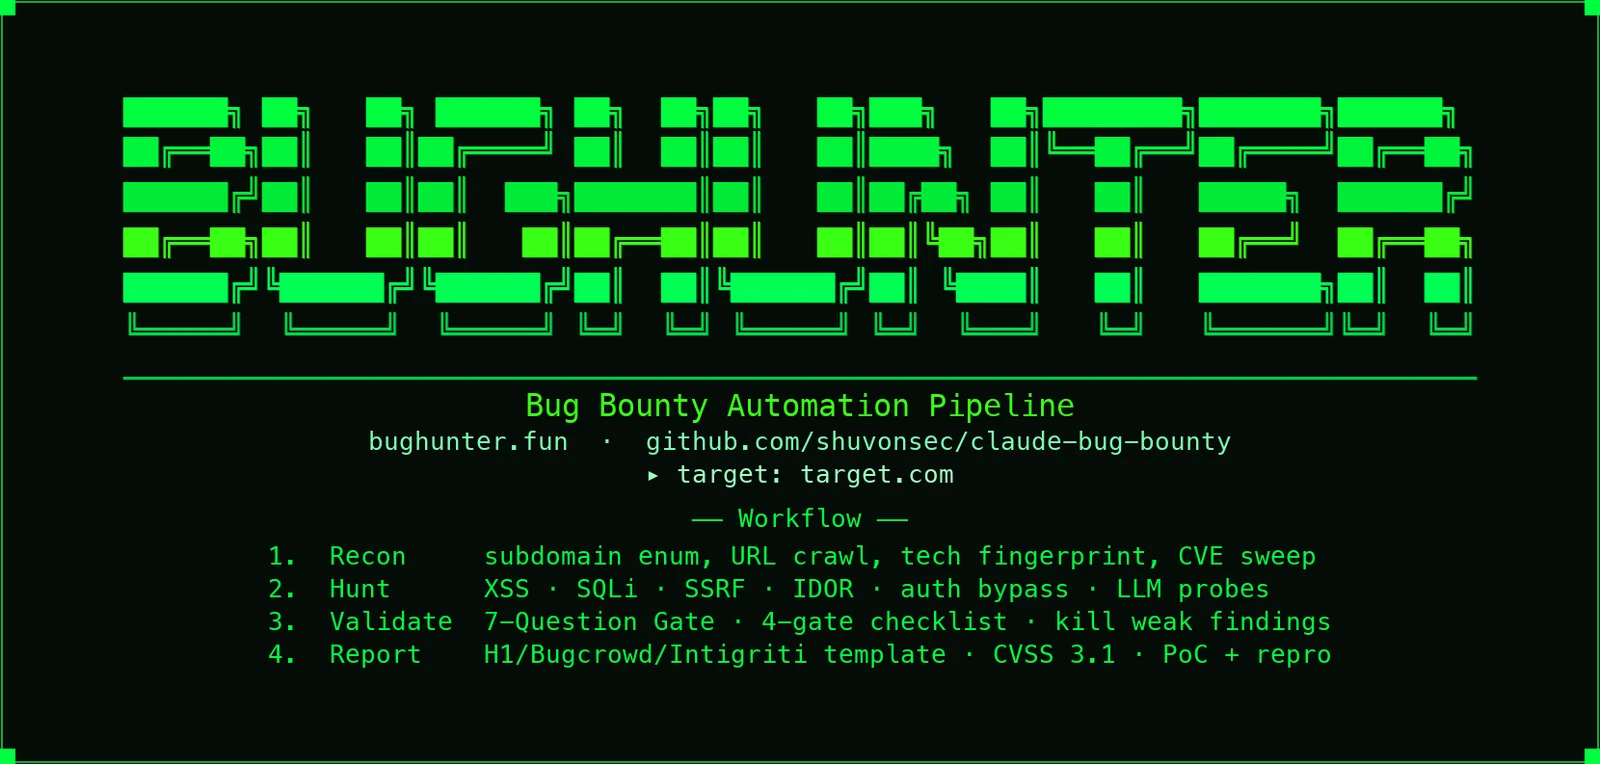
AI-powered bug bounty hunting toolkit that works with or without subscription.
 hahwul/dalfox
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 openai/php2shell-checker
CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…
 zhzyker/vulmap
Web vulnerability scanner and exploitation tool with POC/EXP modes for known CVEs across webapps such as Weblogic, Shiro, Struts2, and Tomcat;…
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
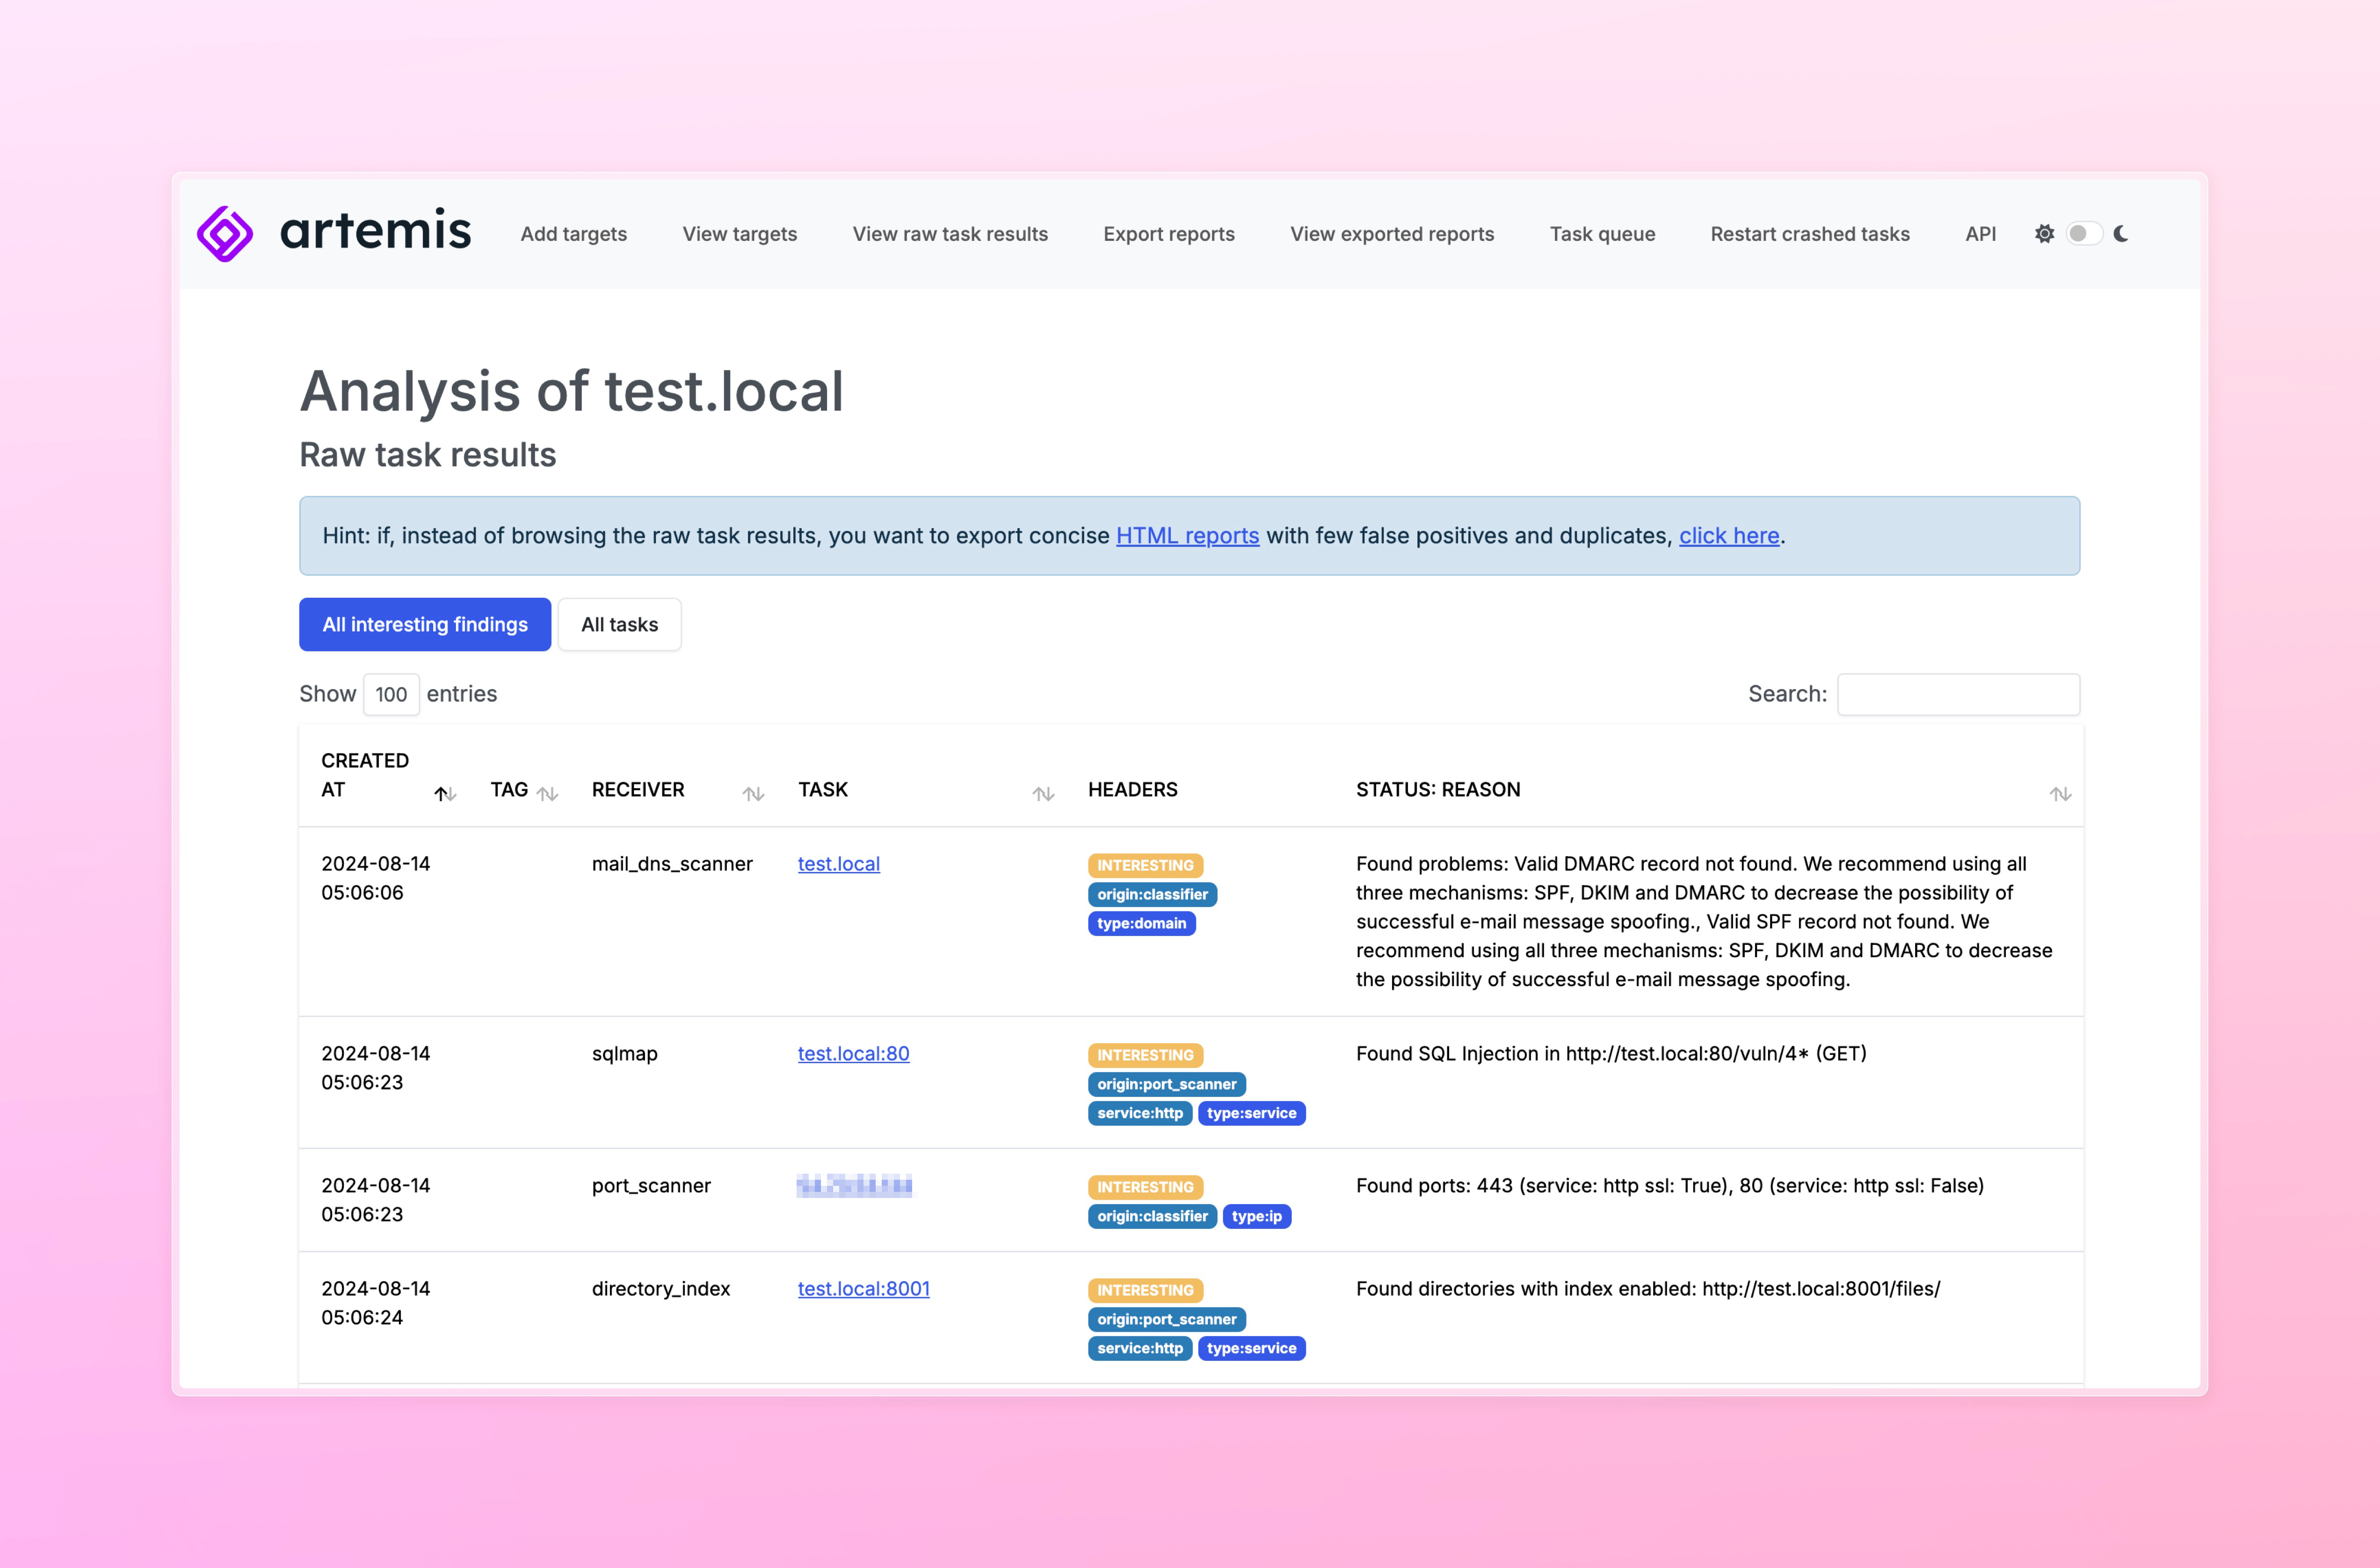 cert-polska/artemis
A modular vulnerability scanner with automatic report generation capabilities.
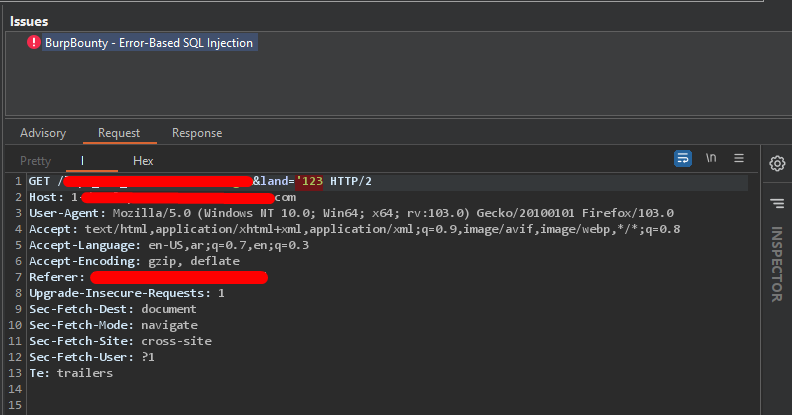 eslam3kl/sqlidetector
Simple python script supported with BurpBouty profile that helps you to detect SQL injection "Error based" by sending multiple requests with 14…
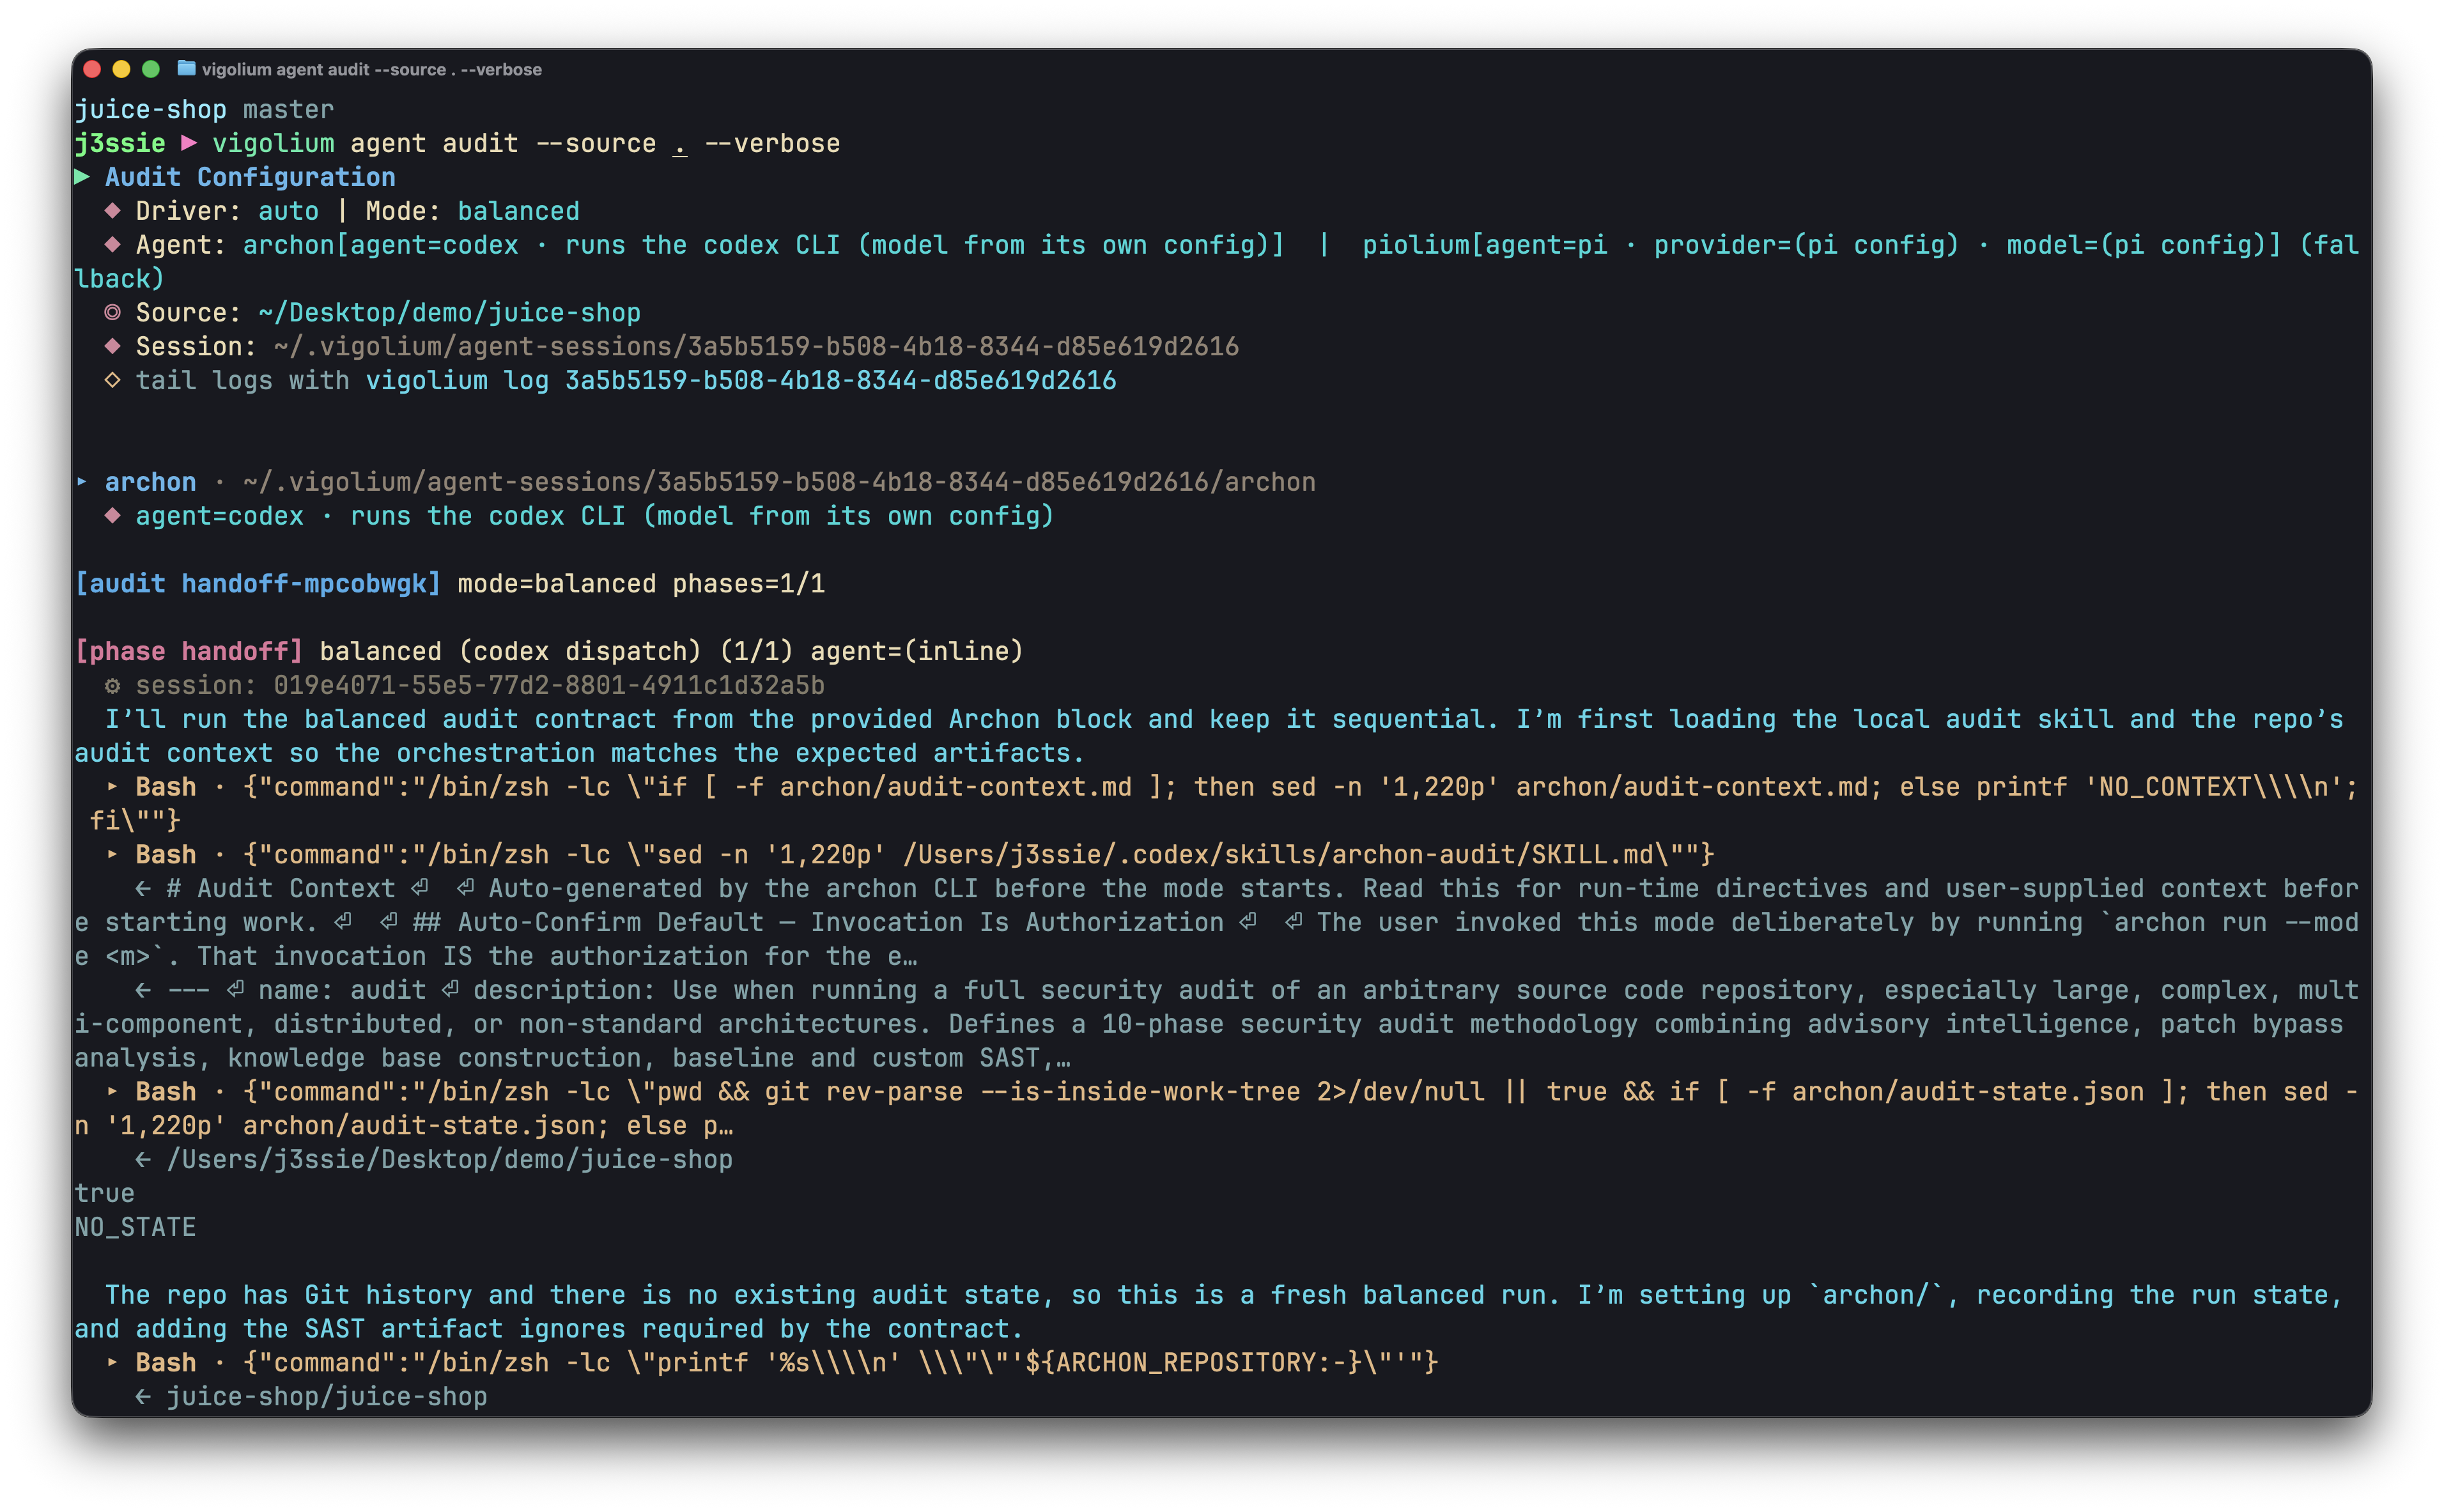 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
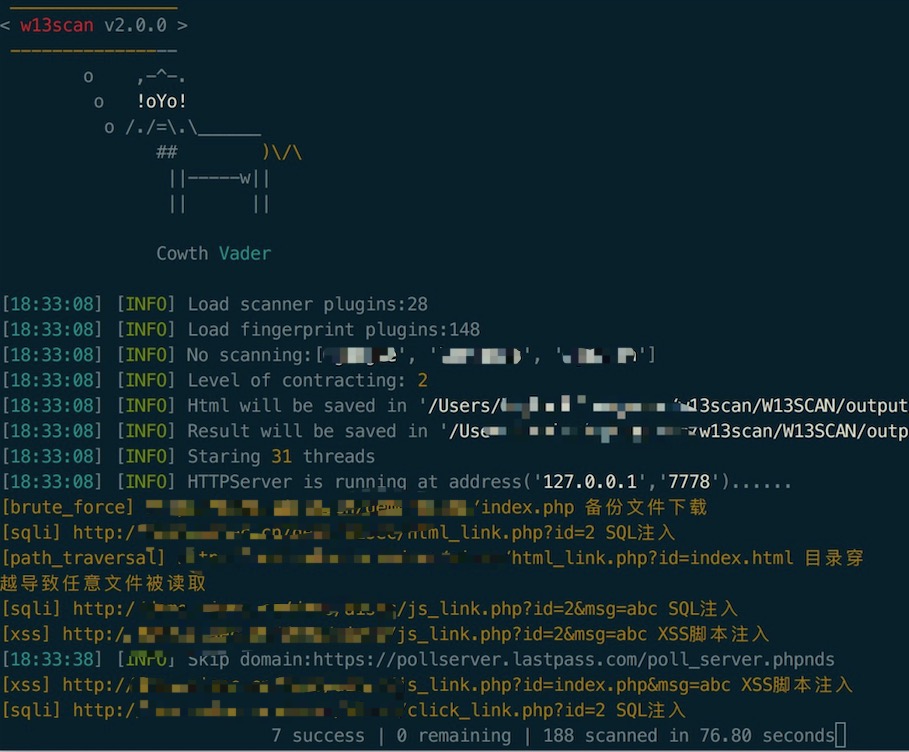 w-digital-scanner/w13scan
Passive and active web vulnerability scanner with plugin-based detection for XSS, SQL injection, command injection, and sensitive file disclosure.…
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…