

BurpAPISecuritySuite
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
api-securityapi-security-testingfuzzing+4
340
teycir/burpapisecuritysuiteBurp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 rxerium/cms-exploitation-campaign
Large Scale Exploitation Campaign against CMS devices reported in July 2026
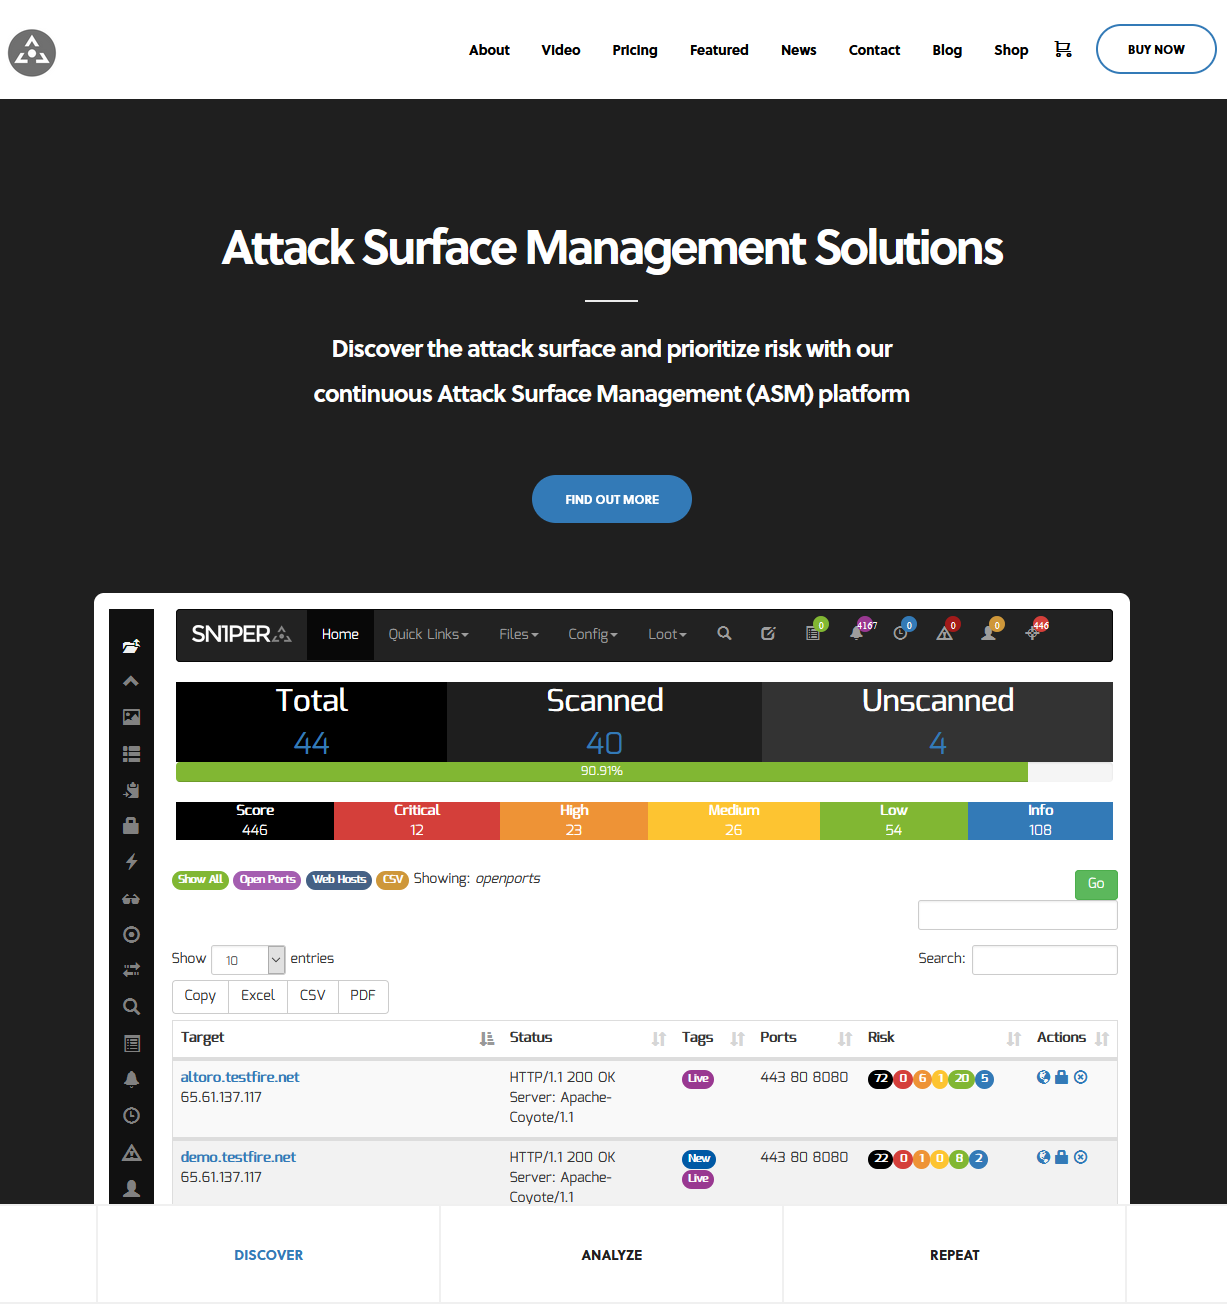 1n3/attacksurfacemanagement
Discover the attack surface and prioritize risks with our continuous Attack Surface Management (ASM) platform - Sn1per Professional #pentest #redteam…
 johnlodan/wp2shell-rce
WordPress CVE-2026-63030 and CVE-2026-60137 security tool for detecting exposure to the WP2Shell pre-authentication RCE chain.
 rxerium/cve-2025-53072-cve-2025-62481
Detection for CVE-2025-53072 + CVE-2025-62481
 rxerium/n8n-vulnerability-detection
Vulnerability detection scripts for the n8n product.
 sebastianmautner/nuclei-cve-2025-24813
University Project of developing a template for safely testing for the CVE 2025-24813 on a server. It is intentionally made to not leave any lasting…
 inteleon404/cve-2025-0133
Reflected XSS vulnerability found in Palo Alto GlobalProtect Gateway & Portal. Attackers can inject malicious scripts via crafted requests.
 cappricio-securities/laravel-ignition-rxss
Laravel Ignition contains a cross-site scripting vulnerability when debug mode is enabled.
 ridhinva/ghe-push-option-rce-scanner
Scanner: CVE-2026-3854 GitHub Enterprise Server Pre-auth RCE via Push Option Injection — Python checker (CISA KEV)
 1n3/sn1per
Automated penetration testing & attack surface management platform. Recon, scan, exploit, report — 600+ exploits, 90+ integrations, 10K+ detections.
 ghosttroops/scan4all
Official repository vuls Scan: 15000+PoCs; 23 kinds of application password crack; 7000+Web fingerprints; 146 protocols and 90000+ rules Port…
 nxploited/cve-2026-18366
Events Manager < 7.4.1 - Unauthenticated Privilege Escalation to Administrator