
CVE-2022-24086
An attacker could place HTML containing executable JavaScript inside element attributes. This markup becomes unescaped, causing arbitrary markup to…

An attacker could place HTML containing executable JavaScript inside element attributes. This markup becomes unescaped, causing arbitrary markup to…

Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15

Nuclei template for detecting CVE-2024-28995, a directory traversal vulnerability in Serv-U FTP server, enabling file read via crafted HTTP requests.

cve-2025-55182

python 2.7

Passive detection for CVE-2025-58360

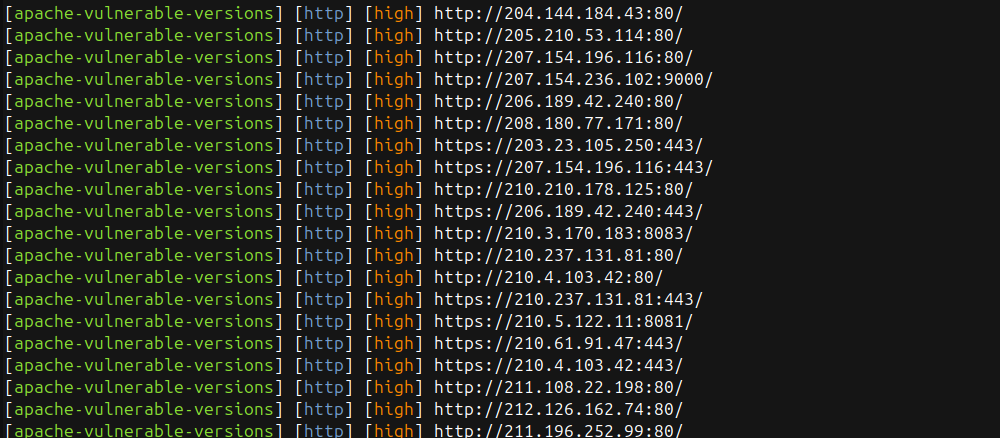
Detects Apache HTTP Server path traversal vulnerabilities (CVE-2021-41773, CVE-2021-42013) by checking for exposure of /etc/passwd through…

Adobe Experience Manager Childlist Selector - Cross-Site Scripting

CVE-2021-46074 - A Stored Cross Site Scripting (XSS) vulnerability exists in Sourcecodester Vehicle Service Management System 1.0 via the Settings…

CVE-2021-46069 - A Stored Cross Site Scripting (XSS) vulnerability exists in Vehicle Service Management System 1.0 via the Mechanic List Section in…

CVE-2025-29927: Next.js Middleware Exploit

Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection

Burp plugin that clusters responses to show an overview of received responses