CVE-2024-28995-Nuclei-Template

Nuclei template for detecting CVE-2024-28995, a directory traversal vulnerability in Serv-U FTP server, enabling file read via crafted HTTP requests.

Nuclei template for detecting CVE-2024-28995, a directory traversal vulnerability in Serv-U FTP server, enabling file read via crafted HTTP requests.

An attacker could place HTML containing executable JavaScript inside element attributes. This markup becomes unescaped, causing arbitrary markup to…

Detects Apache HTTP Server path traversal vulnerabilities (CVE-2021-41773, CVE-2021-42013) by checking for exposure of /etc/passwd through…

Passive detection for CVE-2025-58360

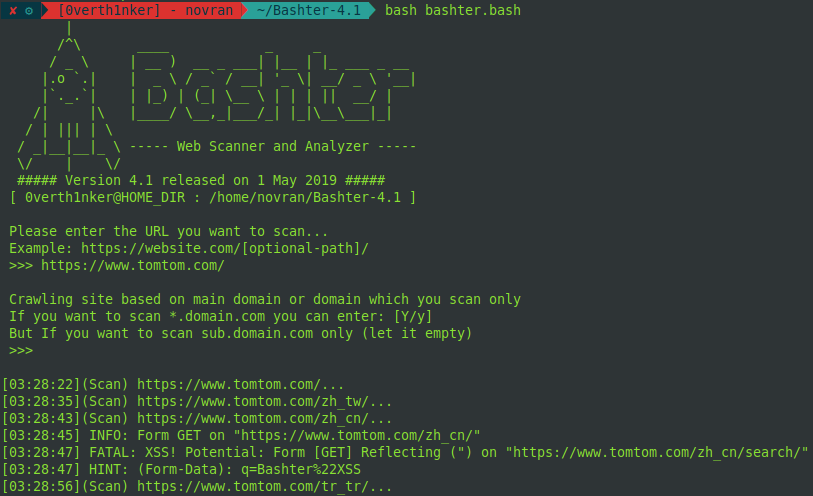
Web Vulnerability Scanner using Shell Script

massive SQL injection vulnerability scanner

A fast DOM based XSS vulnerability scanner with simplicity.

Python script that brute-forces web directories and admin paths using built-in or custom wordlists, with configurable request delays for directory…

Python script that checks Rancher instances for CVE-2026-88804 stored XSS and optionally injects an alert(1) payload to confirm exploitation.

Burp Suite extension for fuzzing WebSocket messages with custom Python code, supporting multiple engines, HTTP middleware routing, and response…

A black-box (DAST) security analysis of CVE-2026-34835 focusing on external validation methodology, observable behavior, security impact, and…

The Clickjacking Exploit Detector uses webpage scanning techniques to identify potential vulnerabilities and provide analysis of those elements.

Proof-of-concept and technical analysis for CVE-2026-12227, an unauthenticated LFI in the WordPress Visual Composer plugin (<=45.16.0) enabling file…

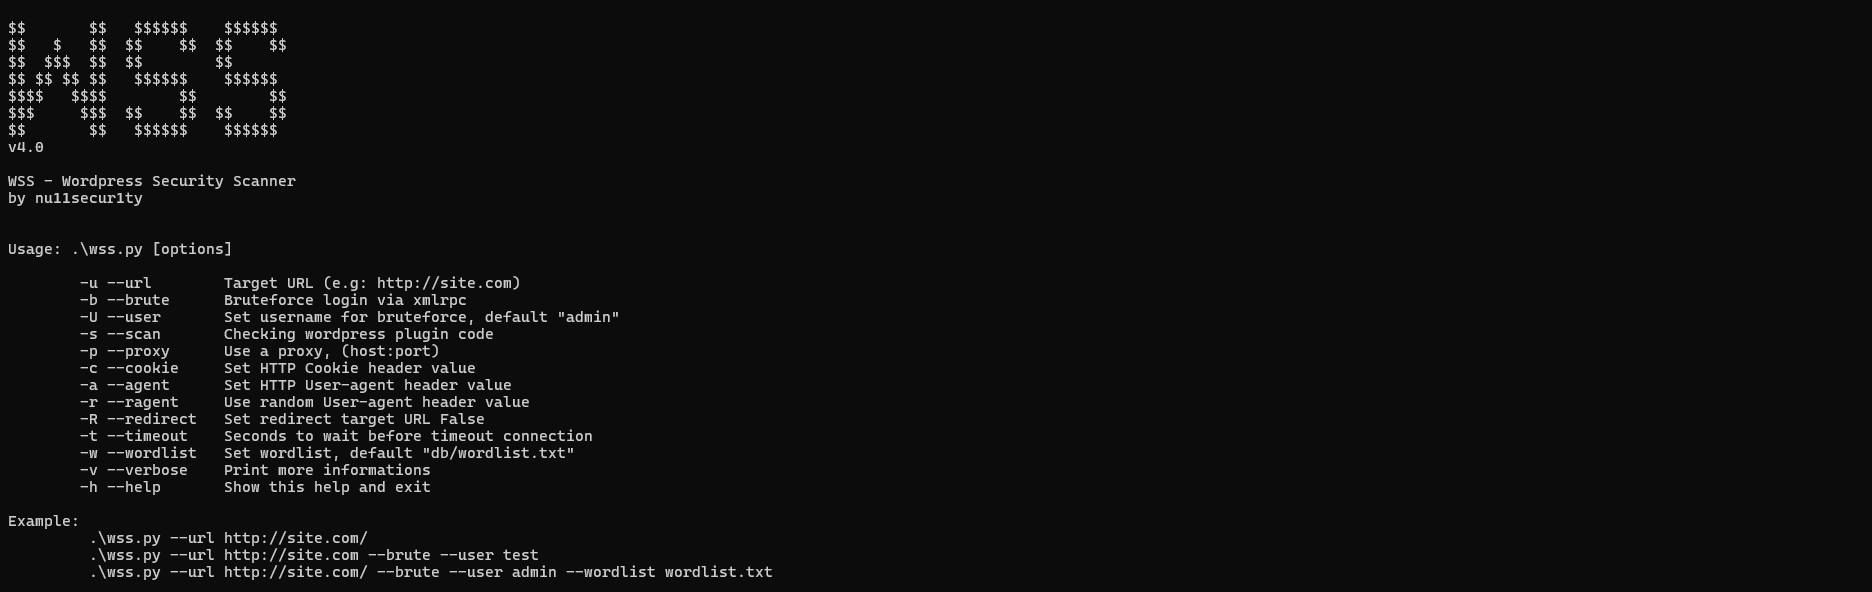
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…

CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…

This tool scans WordPress sites for vulnerabilities in the "RegistrationMagic" plugin (CVE-2024-10508). It checks for the presence of a specific…

Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.