
CVE-2022-24086
An attacker could place HTML containing executable JavaScript inside element attributes. This markup becomes unescaped, causing arbitrary markup to…

An attacker could place HTML containing executable JavaScript inside element attributes. This markup becomes unescaped, causing arbitrary markup to…

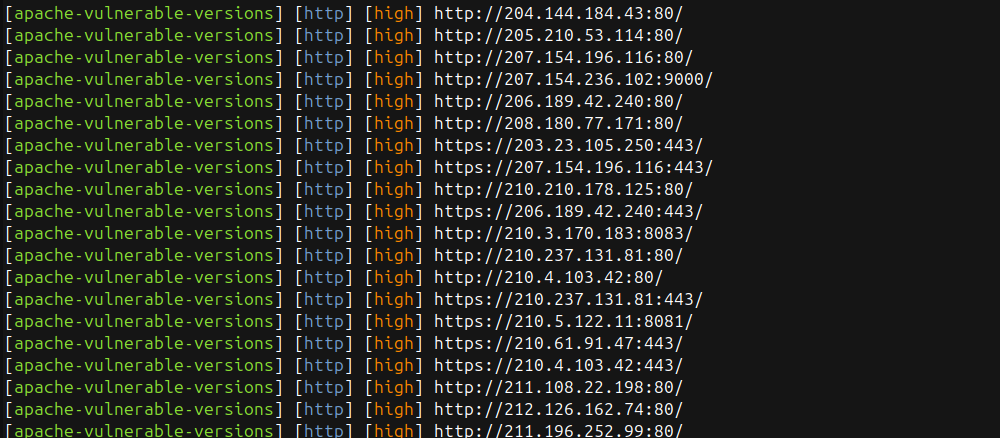
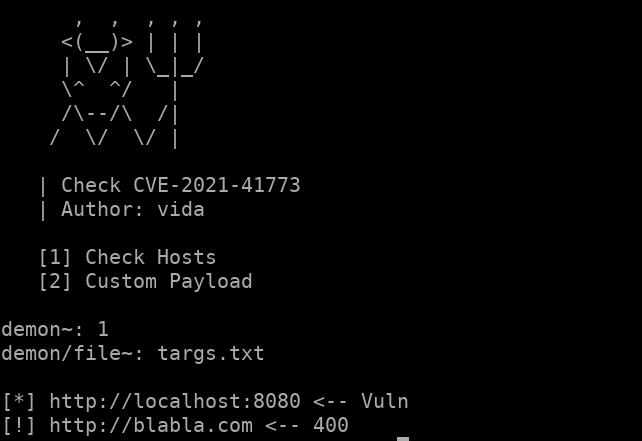
Detects Apache HTTP Server path traversal vulnerabilities (CVE-2021-41773, CVE-2021-42013) by checking for exposure of /etc/passwd through…

Escaner de identificacion de vulnerabilidades para CVE-2025-4322

SAP Knowledge Warehouse <=7.5.0 - Cross-Site Scripting

A automatic scanner to apache 2.4.49

BDU:2023-05144 Nuclei checker

Gryffin is a large scale web security scanning platform.

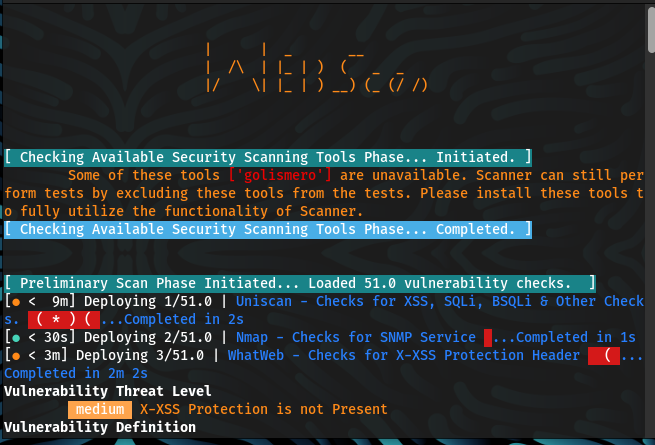
A Penetration Testing Framework, Information gathering tool & Website Vulnerability Scanner

CVE-2026-63223 — CI4RCE: CodeIgniter 4 is_image/mime_in File Upload RCE. Magic bytes bypass (getExtension vs getClientExtension). CVSS 9.8 | CWE-434…

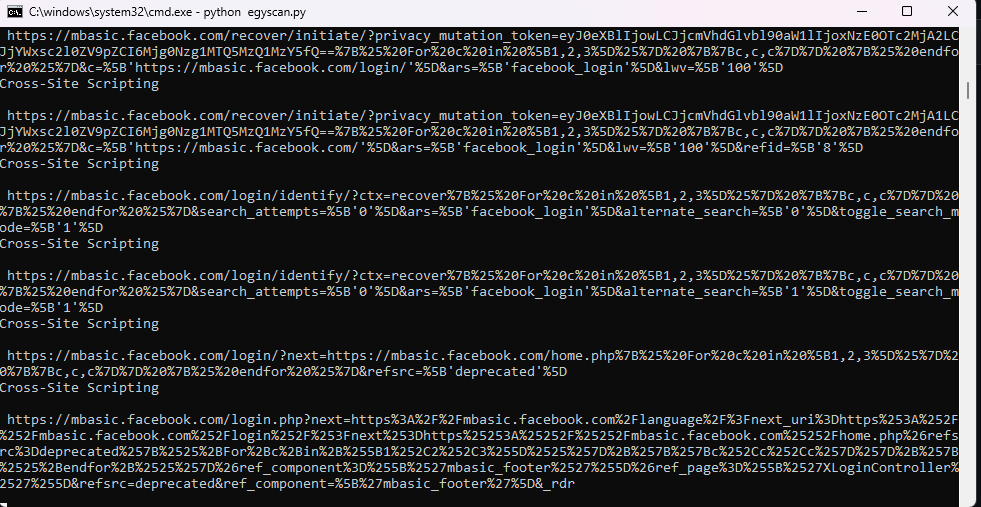
Egyscan The Best web vulnerability scanner; it's a multifaceted security powerhouse designed to fortify your web applications against malicious…

A Web Vulnerability Scanner and Patcher

Reflected XSS vulnerability found in Palo Alto GlobalProtect Gateway & Portal. Attackers can inject malicious scripts via crafted requests.

Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…

Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…

WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…

Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management

Web vulnerability scanner written in Python3

Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…