
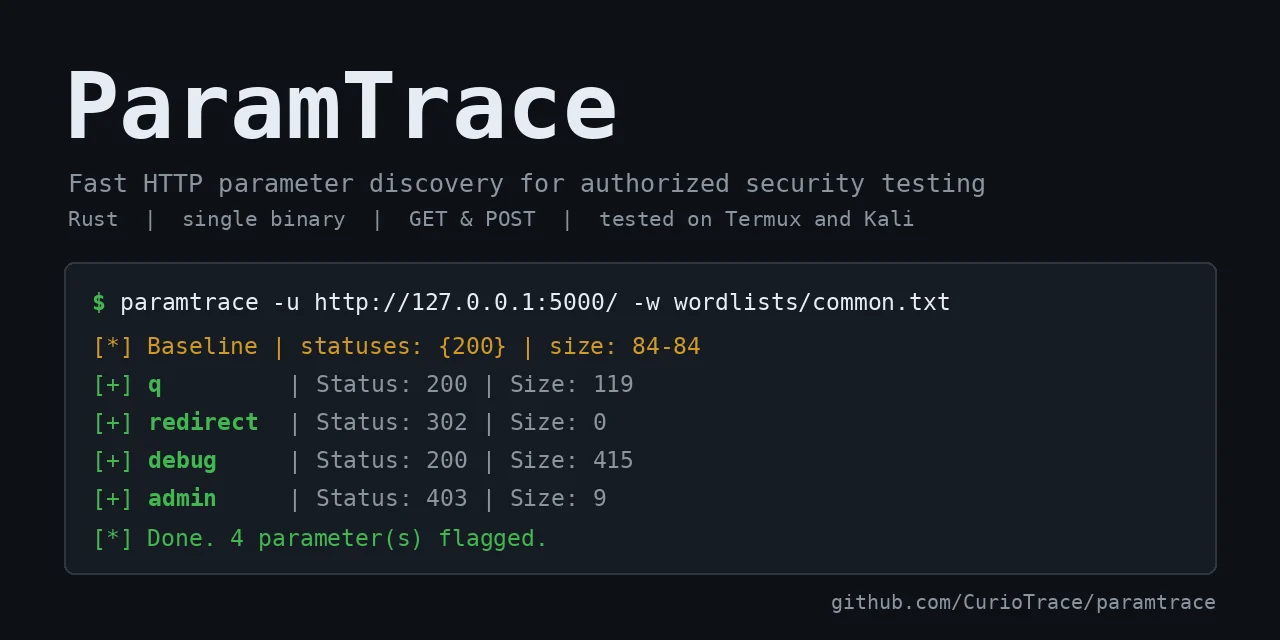
paramtrace
 curiotrace/paramtrace
Fast HTTP parameter discovery for authorized security testing
fuzzinginformation-gatheringpenetration-testing+5
316 days ago
curiotrace/paramtraceFast HTTP parameter discovery for authorized security testing
 isee857/cve-2024-9047-poc
WordPress File Upload插件任意文件读取漏洞(CVE-2024-9047)批量检测脚本
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
 yora1928/cve-2026-15748
Scans WordPress Forminator for CVE-2026-15748 unauthenticated RCE. Detects vulnerable sites, crawls forms, extracts nonces, runs safe upload tests.
 mycode83/godirb
Fast and easy-to-use directory brute-forcer written in Go.
 olafhaalstra/log4jcheck
Check list of URLs against Log4j vulnerability CVE-2021-44228
 gotr00t0day/cve-2025-68461
A C++ security scanner tool to detect Cross-Site Scripting (XSS) vulnerabilities in Roundcube Webmail installations.
 nullwhisper/cve-2026-56292-acymailing-sqli
CVE-2026-56292 - AcyMailing for Joomla unauthenticated SQL injection scanner
 mattb709/cve-2025-24813-scanner
CVE-2025-24813-Scanner is a Python-based vulnerability scanner that detects Apache Tomcat servers vulnerable to CVE-2025-24813, an arbitrary file…
 cappricio-securities/crlfi
This is a tool used by several security researchers to find Carriage Return Line Feed Injection Bug
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 be-keb/cve-2026-12227
Proof-of-concept and technical analysis for CVE-2026-12227, an unauthenticated LFI in the WordPress Visual Composer plugin (<=45.16.0) enabling file…
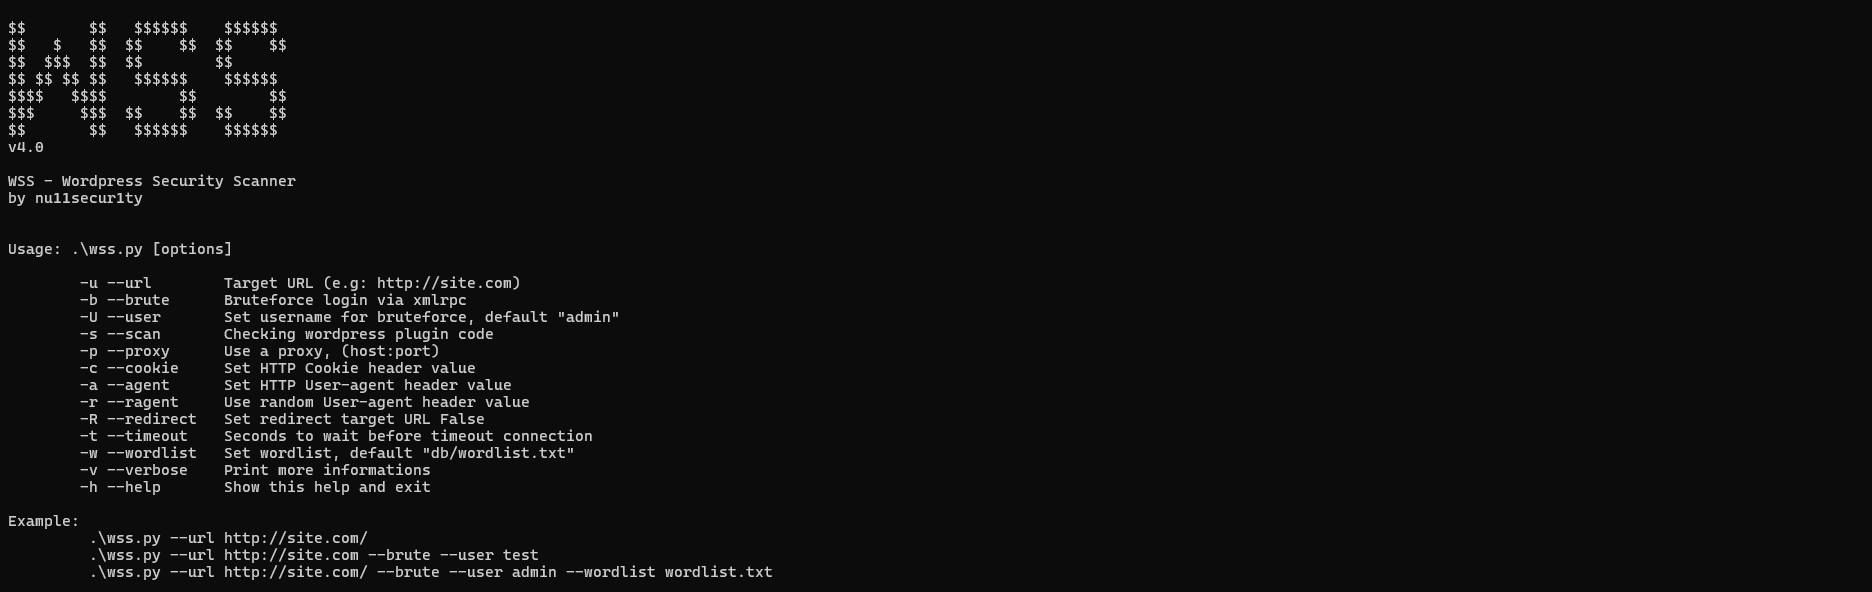 nu11secur1ty/wss
Black-box WordPress vulnerability scanner that detects security issues, enumerates users, brute-forces logins via XMLRPC, and performs static PHP…
 0xwhoknows/cve-2025-29927
Async Python scanner that detects CVE-2025-29927 in Next.js apps by processing URL lists with aiohttp, connection pooling, caching, and chunked…
 nxploited/cve-2026-18366
Events Manager < 7.4.1 - Unauthenticated Privilege Escalation to Administrator
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 bishopfox/cve-2026-19490-check
Safely detect Citrix NetScaler SAML auth bypass CVE-2026-19490
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…