
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
150 results
feroxbuster preview

feroxbuster

GitHubepi052/feroxbuster

A fast, simple, recursive content discovery tool written in Rust.
api-securityapi-security-testingcrawler+8
8.1k
10 days ago
kiterunner preview

kiterunner

GitHubassetnote/kiterunner

High-speed API and web content discovery tool that bruteforces routes using compiled Swagger datasets, supporting depth scanning, custom wordlists,…
api-securityapi-security-testingdynamic-code-analysis+5
3.3k5 years ago
graphql-cop preview

graphql-cop

GitHubdolevf/graphql-cop

Lightweight Python utility for automated security auditing of GraphQL APIs. Detects misconfigurations, information leaks, and denial-of-service…
api-securityapi-security-testingdynamic-code-analysis+5
69010 months ago
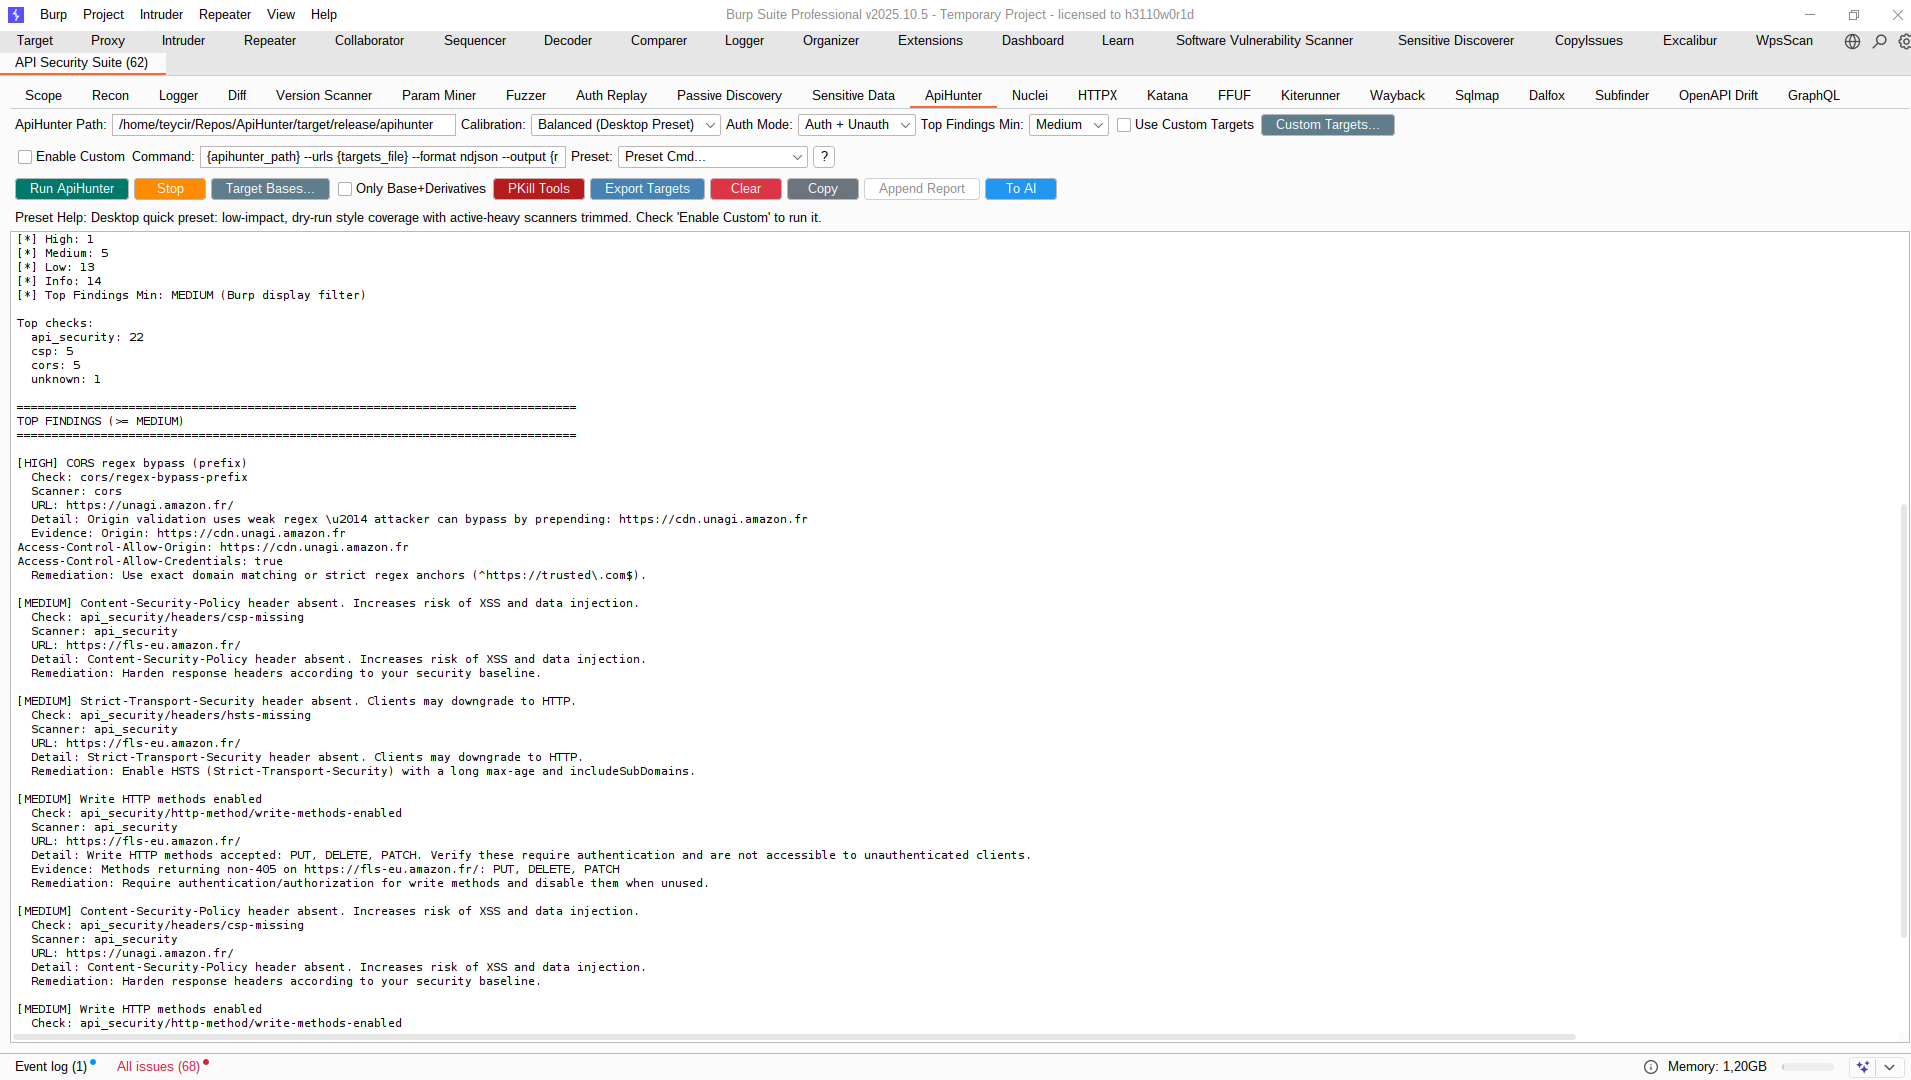
BurpAPISecuritySuite preview

BurpAPISecuritySuite

GitHubteycir/burpapisecuritysuite

Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
api-securityapi-security-testingfuzzing+4
3391 month ago
argumentinjectionhammer preview

argumentinjectionhammer

GitHubnccgroup/argumentinjectionhammer

A Burp Extension designed to identify argument injection vulnerabilities.
api-security-testingpenetration-testingvulnerability-scanners+2
1257 years ago
burpcommander preview

burpcommander

GitHubpentestgeek/burpcommander

Ruby command-line interface to Burp Suite's REST API

api-security-testingpenetration-testingscripting-automation+1
576 years ago
Pegasus-Pentest-Arsenal preview

Pegasus-Pentest-Arsenal

GitHubsobri3195/pegasus-pentest-arsenal

A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
api-security-testingctfeducation+9
575 months ago
CVE-2026-41473-CyberPanel-AI-Scanner-Unauth preview

CVE-2026-41473-CyberPanel-AI-Scanner-Unauth

GitHubpenteraio/cve-2026-41473-cyberpanel-ai-scanner-unauth

Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…
api-securityapi-security-testingvulnerability-analysis+3
2 months ago
Agentic-Bug-Hunter preview

Agentic-Bug-Hunter

GitHubawarexone/agentic-bug-hunter

AI-powered bug bounty hunting toolkit that works with or without subscription.

ai-securityapi-security-testingcloud-security+8
4.8k10 days ago
smugglex preview

smugglex

GitHubhahwul/smugglex

Rust-powered HTTP Request Smuggling Scanner.
api-security-testingdevsecopspenetration-testing+3
13216 days ago
wpx preview

wpx

GitHubgreg-randall/wpx

Asynchronous WordPress security scanner with WAF bypass via headless browser. Enumerates plugins, themes, users, and multisite installations with…
api-security-testingcrawlerinformation-gathering+6
105 months ago
spring-cloud__spring-cloud-gateway_CVE-2022-22947_3-0-6 preview

spring-cloud__spring-cloud-gateway_CVE-2022-22947_3-0-6

GitHubshoucheng3/spring-cloud__spring-cloud-gateway_cve-2022-22947_3-0-6

Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.
api-securityapi-security-testingexploitation+3
1 year ago
dirstalk preview

dirstalk

GitHubstefanoj3/dirstalk

Modern alternative to dirbuster/dirb

information-gatheringpenetration-testingreconnaissance+2
3984 years ago
CVE-2025-0133 preview

CVE-2025-0133

GitHubinteleon404/cve-2025-0133

Reflected XSS vulnerability found in Palo Alto GlobalProtect Gateway & Portal. Attackers can inject malicious scripts via crafted requests.

exploitationpenetration-testingreconnaissance+3
101 year ago
BurpSuite-For-Pentester preview

BurpSuite-For-Pentester

GitHubignitetechnologies/burpsuite-for-pentester

This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
authentication-authorizationcurated-resourceseducation+7
2.6k6 months ago
Open-Worldwide-Application-Security-Project-OWASP- preview

Open-Worldwide-Application-Security-Project-OWASP-

GitHubwaburig/open-worldwide-application-security-project-owasp-

Automated Web Vulnerability Assessment of DVWA using OWASP ZAP to identify and analyze critical security flaws like Remote Code Execution…
educationpenetration-testingvulnerability-analysis+2
8 months ago
CVE-2022-35499 preview

CVE-2022-35499

GitHubpn-tester/cve-2022-35499

Proof-of-concept exploit for reflected cross-site scripting (XSS) vulnerability in Trimble TM4WEB <=22.2.0, demonstrating injection via arbitrary URL…
exploitationinformation-gatheringpenetration-testing+3
1 month ago
XnlReveal preview

XnlReveal

GitHubxnl-h4ck3r/xnlreveal

A Chrome/Firefox browser extension to show alerts for reflected query params, show Wayback archive links for the current path, show hidden elements…

information-gatheringosintpenetration-testing+3
4544 months ago
Previous1…345…9Next