

extended-xss-search
 damian89/extended-xss-search
A better version of my xssfinder tool - scans for different types of xss on a list of urls.
information-gatheringpenetration-testingvulnerability-scanners+2
damian89/extended-xss-searchA better version of my xssfinder tool - scans for different types of xss on a list of urls.
 allyomalley/burpparamflagger
A Burp extension adding a passive scan check to flag parameters whose name or value may indicate a possible insertion point for SSRF or LFI.
 hannob/optionsbleed
Proof-of-concept scanner for the Optionsbleed vulnerability (CVE-2017-9798) that tests Apache HTTP servers for memory leak via HTTP OPTIONS method.
 dawgyg/bugbounty_tools
Collection of scripts and tools used during bug bounty work. This will be the location of my automation scripts created for my own personal use, and…
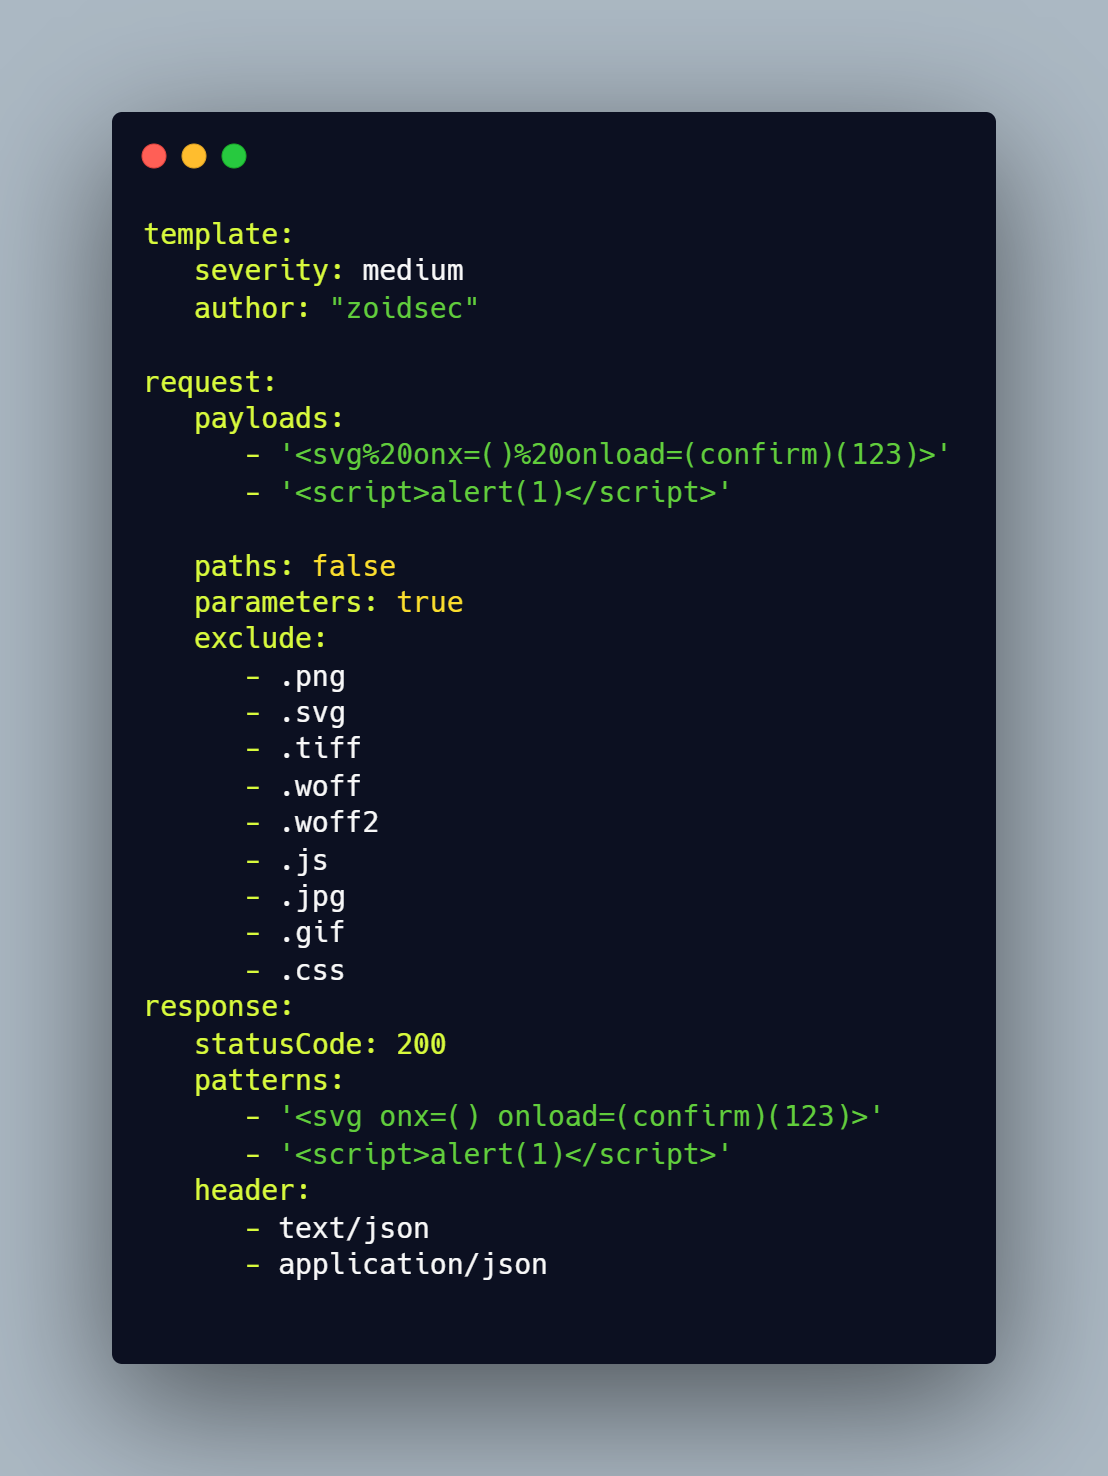 ethicalhackingplayground/erebus
Erebus is a fast tool for parameter-based vulnerability scanning using a Yaml based template engine like nuclei.
 northwavesecurity/log4jcheck
A script that checks for vulnerable Log4j (CVE-2021-44228) systems using injection of the payload in common HTTP headers.
 mrmtwoj/apache-vulnerability-testing
Apache HTTP Server Vulnerability Testing Tool | PoC for CVE-2024-38472 , CVE-2024-39573 , CVE-2024-38477 , CVE-2024-38476 , CVE-2024-38475 ,…
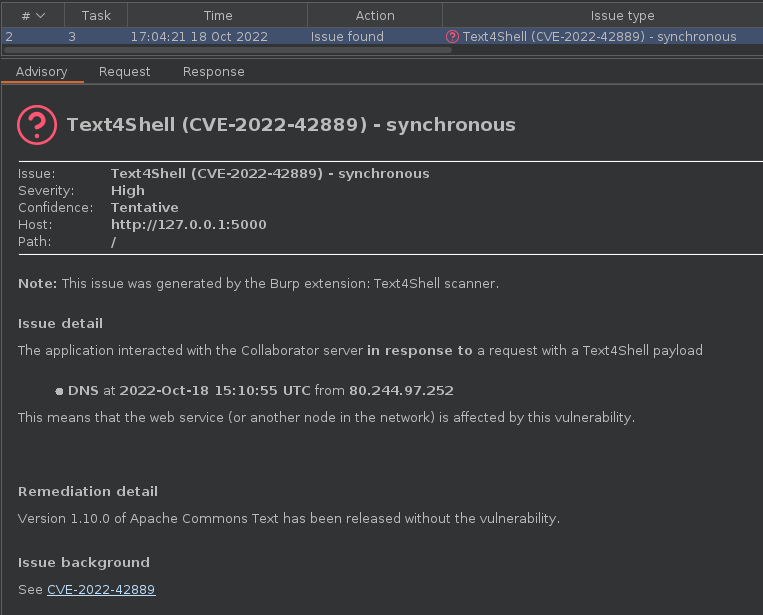 silentsignal/burp-text4shell
Text4Shell scanner for Burp Suite
 evilsocket/altair
Modular web vulnerability scanner with template-driven detection engine for automated testing of XSS, SQLi, LFI, RFI, and sensitive file/directory…
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 k8gege/pyladon
Ladon Scanner For Python, Large Network Penetration Scanner & Cobalt Strike, vulnerability / exploit / detection /…
 redhuntlabs/log4jhunt
An automated, reliable scanner for the Log4Shell (CVE-2021-44228) vulnerability.
 alessiodallapiazza/wpscan
WordPress security scanner that enumerates vulnerable plugins, themes, and users to identify misconfigurations and known vulnerabilities for…
 philesiv/xsleaker
Searcher for cross-site leaks (XS-Leaks)
 rxerium/freepbx-vulns-december-25
Detection for CVE-2025-61675, CVE-2025-61678 & CVE-2025-66039
 rxerium/cve-2025-61882-cve-2025-61884
Detection for CVE-2025-61882 & CVE-2025-61884
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 rxerium/cve-2025-68613
Detection for CVE-2025-68613