
goWAPT
 dzonerzy/gowapt
Go Web Application Penetration Test
fuzzingpenetration-testingscripting-automation+4
dzonerzy/gowaptGo Web Application Penetration Test
 cappricio-securities/crlfi
This is a tool used by several security researchers to find Carriage Return Line Feed Injection Bug
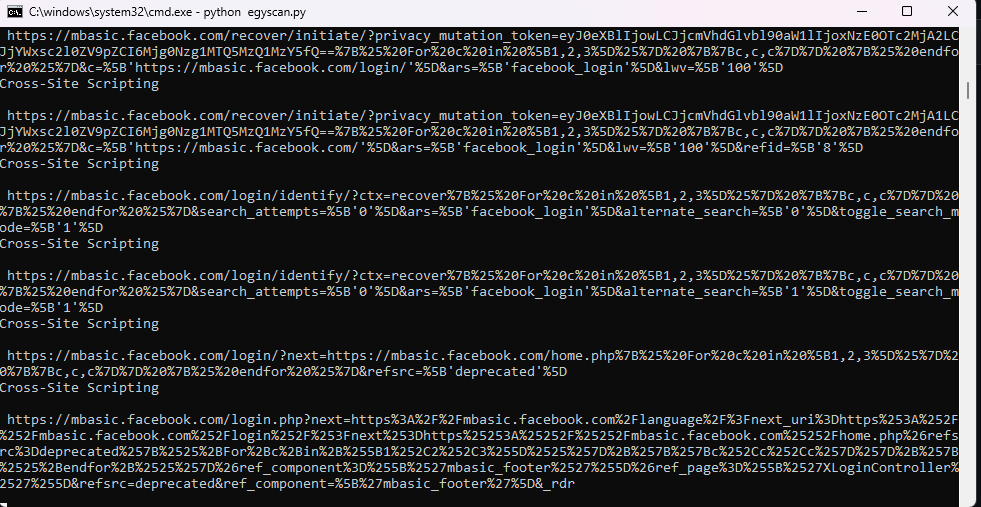 dragonked2/egyscan
Egyscan The Best web vulnerability scanner; it's a multifaceted security powerhouse designed to fortify your web applications against malicious…
 robotshell/magicrecon
MagicRecon is a powerful shell script to maximize the recon and data collection process of an objective and finding common vulnerabilities, all this…
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
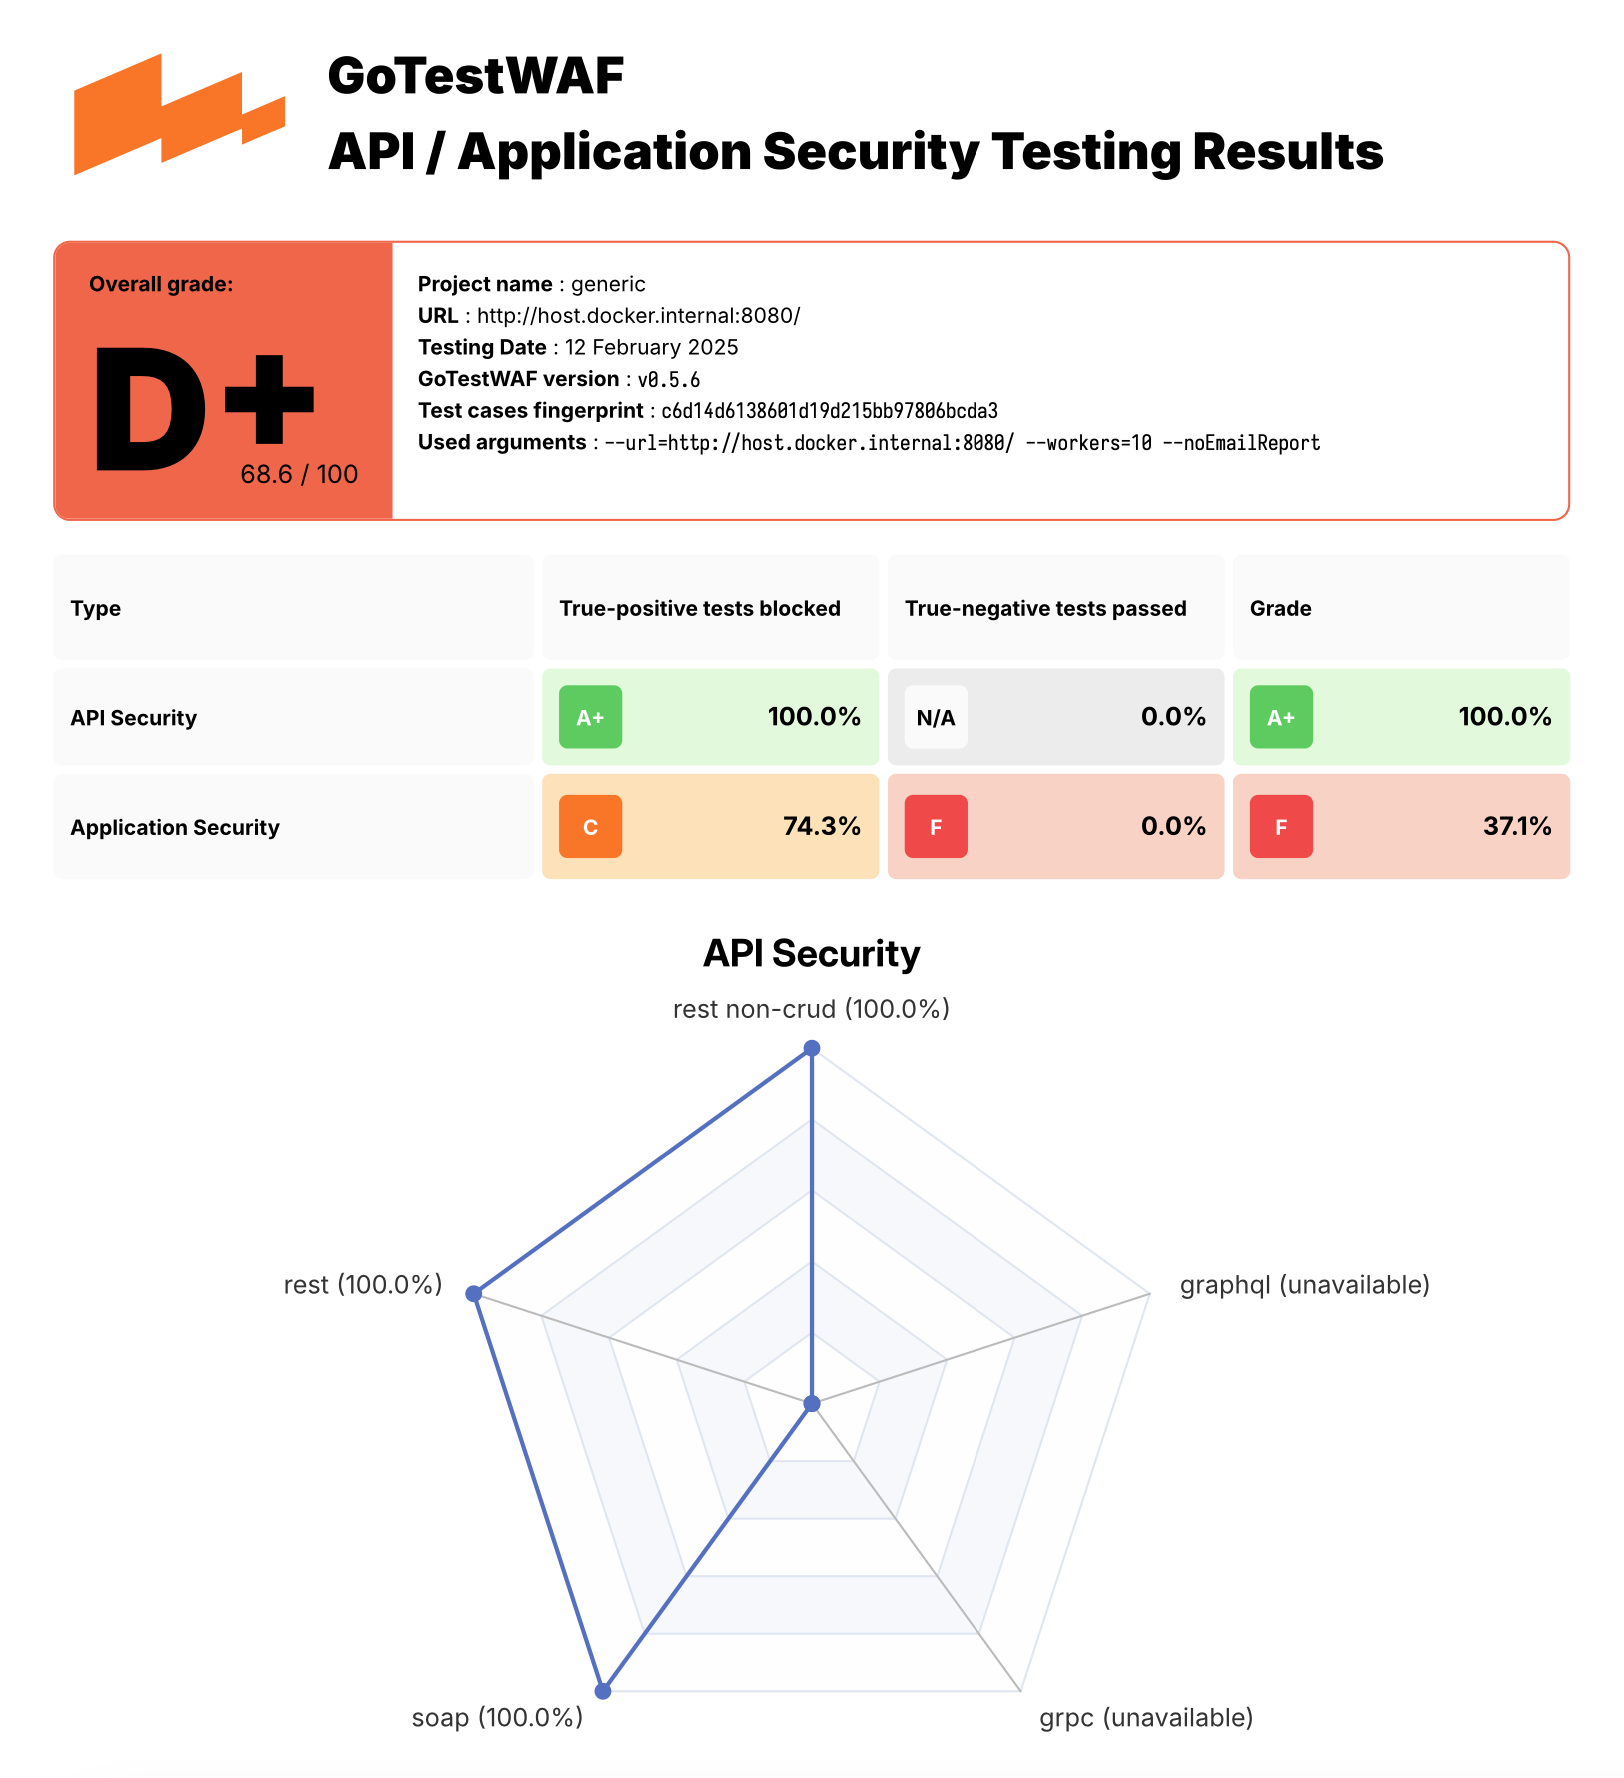 wallarm/gotestwaf
An open-source project in Golang to asess different API Security tools and WAF for detection logic and bypasses
 lfillaz/cve-2024-2997
The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…
 0xuho/cve-2024-2997
The tool helps in quickly identifying vulnerabilities by examining a comprehensive list of potential paths on a website, making it useful for…
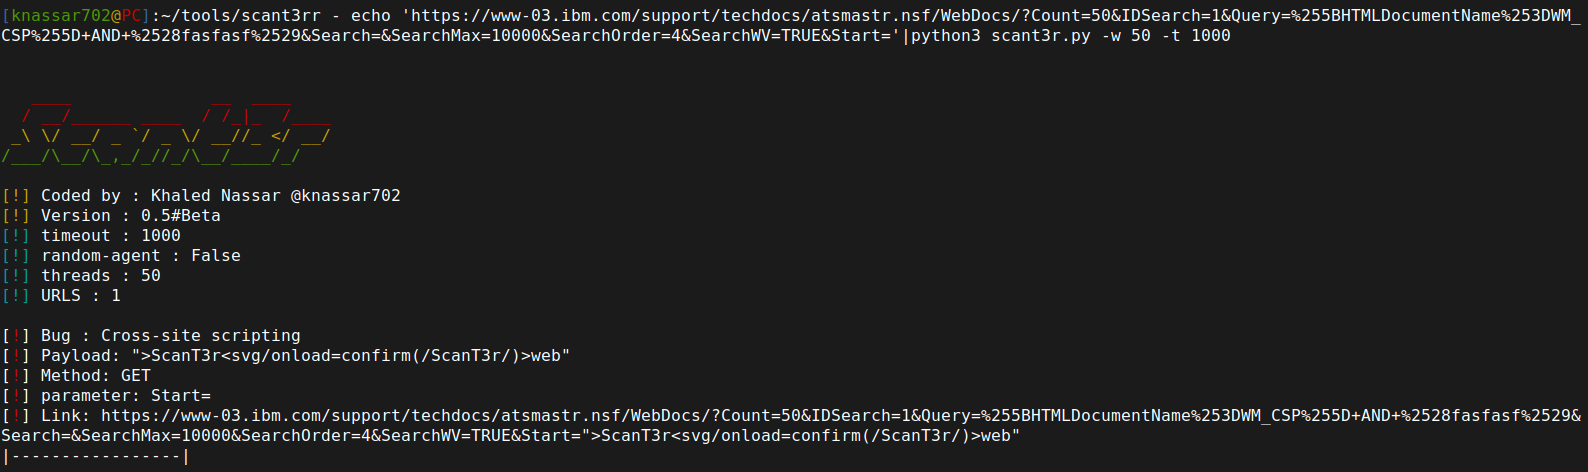 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 mrmtwoj/apache-vulnerability-testing
Apache HTTP Server Vulnerability Testing Tool | PoC for CVE-2024-38472 , CVE-2024-39573 , CVE-2024-38477 , CVE-2024-38476 , CVE-2024-38475 ,…
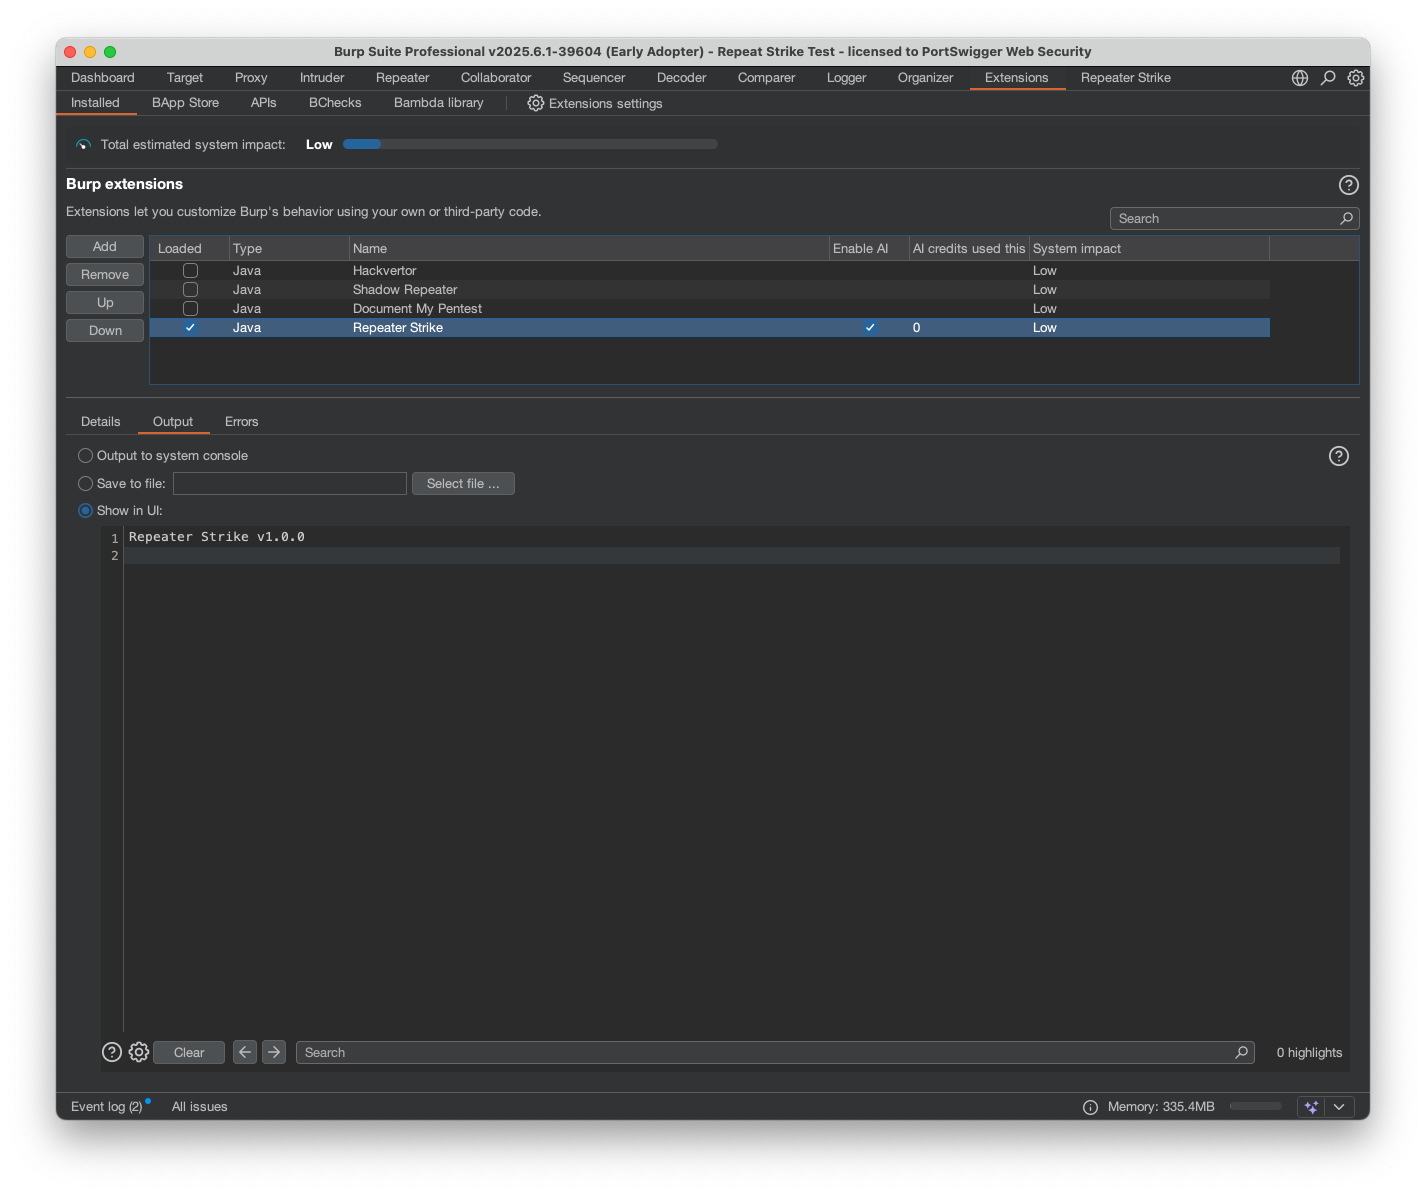 hackvertor/repeat-strike
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
 squ1shification/grafana-plugin-enumerator-cve-2021-43798
Bash-based scanner that enumerates Grafana plugin IDs and tests for CVE-2021-43798 directory traversal by attempting to read /etc/passwd or win.ini…
 xuemian168/cve-2025-30208
全网首发 CVE-2025-31125 CVE-2025-30208 CVE-2025-32395 Vite Scanner
 ferpalma21/nextjs-scanner
This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
 evtdanya/cve-2026-27886
Strapi CVE-2026-27886. Leaking sensitive data via relational filtering due to lack of query sanitization
 dobin/burpsentinel
GUI Burp Plugin to ease discovering of security holes in web applications
 damian89/extended-xss-search
A better version of my xssfinder tool - scans for different types of xss on a list of urls.
 rxerium/cve-2024-12084
A heap-based buffer overflow flaw was found in the rsync daemon. This issue is due to improper handling of attacker-controlled checksum lengths…