
CVE-2026-85520
 murrez/cve-2026-85520
Python PoC for CVE-2026-85520: detects and exploits unauthenticated arbitrary file write in PrestaShop gmfeed feed.php to achieve RCE, with bulk…
exploitationpenetration-testingreconnaissance+4
murrez/cve-2026-85520Python PoC for CVE-2026-85520: detects and exploits unauthenticated arbitrary file write in PrestaShop gmfeed feed.php to achieve RCE, with bulk…
 pauleprichna/cybersecurity
French cybersecurity lab coursework covering network recon, DDoS, brute force, phishing, Wi-Fi attacks, malware generation, MITM, and a librsvg…
 anoxhunterdump-ctrl/cve-2026-94541-wpmobileapp-authbypass
Defensive analysis, detection scanner, and rule signatures for CVE-2026-94541 (WPMobile.App <= 11.82).
 fl0ydsec/cve-2026-91136
Mass scanner and PoC exploit for CVE-2026-91136, an unauthenticated arbitrary file read in the Divi Plus WordPress plugin via the svg_image REST…
 r0gfall/cve-2026-88804
Python script that checks Rancher instances for CVE-2026-88804 stored XSS and optionally injects an alert(1) payload to confirm exploitation.
 langz337/cve-2026-87902
Scans WordPress Core 4.7.0–7.1.1 for CVE-2026-87902 unauthenticated LFI via double-encoded pagename traversal, with optional PEAR config-create RCE…
 abatsakidis/wp-cve-2026-87902-checker
Defensive WordPress security scanner for CVE-2026-87902 — local filesystem inspection and safe remote HTTP/HTTPS assessment.
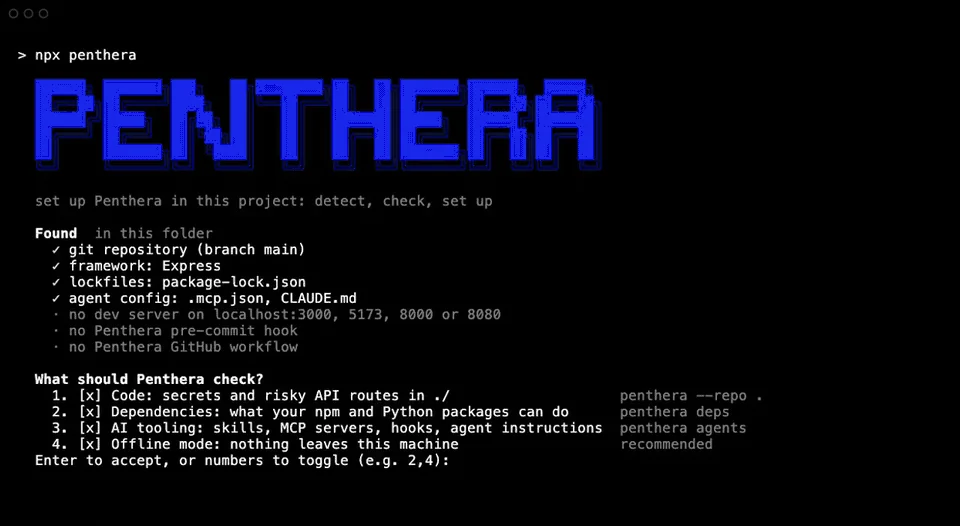 danoszz/penthera
Offline cyber security agent for your apps and AI coding tools. Open R&D: measured in public, improved every release.
 oscerd/cve-2026-101259
Runnable proof-of-concept reproducer for CVE-2026-101259, demonstrating error-message disclosure in Apache Camel camel-coap consumers on Spring Boot…
 bitplugg/kitsune
🦊 nine-tailed pentest framework — nmap + msf + aircrack + sqlmap в одном CLI · 25 модулей · SQLite-сессия · TUI · REST API · pipx install
 nxploited/cve-2026-114509
Laravel TokenGuard authentication bypass through non-string API credentials
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
 hevnsnt/cvengine
AI-first external attack surface assessment with continuous discovery, evidence-based vulnerability validation, and developer-agent MCP integration.
 assetnote/node2shell-scanner
High fidelity detection mechanism for node2shell (CVE-2026-111497)
 affolter-engineering/hvt
Rust CLI that probes HTTP methods (including WebDAV and DeltaV verbs) against a target URL to surface verb tampering, access-control bypasses, and…
 ardakocadoru/xss-cheatsheet
Comprehensive XSS reference covering reflected, stored, DOM and blind payloads, filter bypass, WAF evasion, CSP bypass, mXSS, and real-world CVE case…
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.
 horkimhab/cve-2025-64702-more
Proof-of-concept code and research notes for QPACK/HTTP-3 vulnerabilities (CVE-2025-64702, CVE-2026-12523, CVE-2025-13945) for authorized lab testing.