
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
56 results
CVE-2026-65540 preview

CVE-2026-65540

GitHubtestardou/cve-2026-65540

Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
exploitationvulnerability-analysisweb-application-exploitation+2
2 days ago
dynast-bench preview

dynast-bench

GitHubj3ssie/dynast-bench

A DAST benchmark of intentionally-vulnerable apps with ground-truth answer keys for scoring scanners
api-security-testingcurated-resourceseducation+4
11 days ago
Agentic-Bug-Hunter preview

Agentic-Bug-Hunter

GitHubawarexone/agentic-bug-hunter

AI-powered bug bounty hunting toolkit that works with or without subscription.
ai-securityapi-security-testingcloud-security+8
4.8k9 days ago
gf preview

gf

GitHubtomnomnom/gf

A wrapper around grep, to help you grep for things

code-analysisdynamic-code-analysisgeneral-purpose-utilities+7
2.1k2 years ago
wapiti preview

wapiti

GitHubwapiti-scanner/wapiti

Web vulnerability scanner written in Python3
api-security-testingconfiguration-auditingcrawler+11
1.9k29 days ago
CVE-2026-19478 preview

CVE-2026-19478

GitHubrenzi25031469/cve-2026-19478

Detects CVE-2026-19478 in GitLab CE/EE with a non-destructive Nuclei template that triggers the GraphQL fallback-field method invocation via touch…
api-security-testinginformation-gatheringpenetration-testing+4
125 days ago
CVE-2024-38856-ApacheOfBiz preview

CVE-2024-38856-ApacheOfBiz

GitHubgraysignal/cve-2024-38856-apacheofbiz

Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
exploitationvulnerability-analysisweb-application-exploitation+1
12 years ago
CVE-2026-41473-CyberPanel-AI-Scanner-Unauth preview

CVE-2026-41473-CyberPanel-AI-Scanner-Unauth

GitHubpenteraio/cve-2026-41473-cyberpanel-ai-scanner-unauth

Nuclei detection template for CVE-2026-41473, an unauthenticated read/write API access flaw in CyberPanel AI Scanner before 2.4.4. Uses two HTTP…

api-securityapi-security-testingvulnerability-analysis+3
2 months ago
wp2shell-Exploit-Waf-Bypass preview

wp2shell-Exploit-Waf-Bypass

GitHubm4xsec/wp2shell-exploit-waf-bypass

WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
api-security-testingexploitationpenetration-testing+4
51 month ago
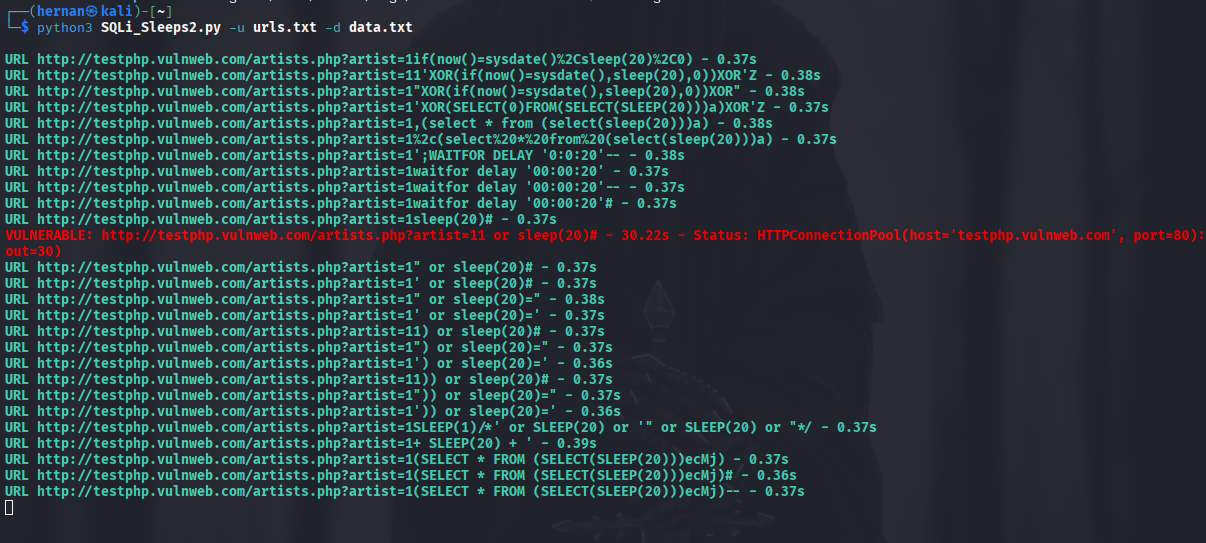
SQLi_Sleeps preview

SQLi_Sleeps

GitHubhernanrodriguez1/sqli_sleeps

Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
penetration-testingweb-application-exploitationweb-security+1
1271 year ago
crlf-powered-desync-scanner preview

crlf-powered-desync-scanner

GitHubt0xodile/crlf-powered-desync-scanner

Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…

exploitationpenetration-testingweb-application-exploitation+2
181 month ago
smugglex preview

smugglex

GitHubhahwul/smugglex

Rust-powered HTTP Request Smuggling Scanner.
api-security-testingdevsecopspenetration-testing+3
13214 days ago
argumentinjectionhammer preview

argumentinjectionhammer

GitHubnccgroup/argumentinjectionhammer

A Burp Extension designed to identify argument injection vulnerabilities.
api-security-testingpenetration-testingvulnerability-scanners+2
1257 years ago
crlfi-scanner preview

crlfi-scanner

GitHubcappricio-securities/crlfi-scanner

CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…

fuzzingpenetration-testingweb-application-exploitation+2
45 months ago
BurpSuite_Pro_v1.7.37 preview

BurpSuite_Pro_v1.7.37

GitHubjas502n/burpsuite_pro_v1.7.37

Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
api-security-testinginformation-gatheringpenetration-testing+4
567 years ago
sql-global-injector preview

sql-global-injector

GitHubnu11secur1ty/sql-global-injector

Python-based web crawler and SQL injection vulnerability scanner using dork queries. Supports proxy and automated scanning for security testing.
crawlerinformation-gatheringreconnaissance+2
24 years ago
BurpSentinel preview

BurpSentinel

GitHubdobin/burpsentinel

GUI Burp Plugin to ease discovering of security holes in web applications

dynamic-code-analysispenetration-testingvulnerability-analysis+3
1539 years ago
zap-api-rust preview

zap-api-rust

GitHubzaproxy/zap-api-rust

Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…

api-securitypenetration-testingvulnerability-scanners+3
153 years ago
Previous1234Next