
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
79 results
LFITester preview

LFITester

GitHubkostas-pa/lfitester

Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…

crawlerexploitationfuzzing+7
112
1 year ago
hvt preview

hvt

GitHubaffolter-engineering/hvt

Rust CLI that probes HTTP methods (including WebDAV and DeltaV verbs) against a target URL to surface verb tampering, access-control bypasses, and…
api-security-testingconfiguration-auditingmisconfiguration+5
26 days ago
thc-BloodMiami preview

thc-BloodMiami

GitHubfoxcornlab/thc-bloodmiami

AI chat-box pentesting tool in C: fires language (SQLi/NoSQL/XSS/SSTI) and prompt injection payloads at chat interfaces and flags the ones that bite
ai-securityapi-security-testingfuzzing+5
9 days ago
XSSYA-V-2.0 preview

XSSYA-V-2.0

GitHubyehia-mamdouh/xssya-v-2.0

Python XSS scanner that confirms reflected and encoded-payload injection, executes payloads to capture cookies, detects WAFs, and tests XST with a…
information-gatheringpayload-generationpenetration-testing+5
839 years ago
php2shell-checker preview

php2shell-checker

GitHubopenai/php2shell-checker

CLI that checks a website's PHP version or a local PHP binary against embedded patch cutoffs to determine php2shell vulnerability status, with JSON…
defensive-toolsinformation-gatheringvulnerability-analysis+3
1.5k11 days ago
CVE-2025-49132 preview

CVE-2025-49132

GitHub2t8a/cve-2025-49132

Python scanner for CVE-2025-49132 that exploits a path traversal in Pterodactyl Panel's locale endpoint to extract exposed database configuration…

data-exfiltrationexploitationinformation-gathering+5
1 year ago
-LogicSentry-AI preview

-LogicSentry-AI

GitHubvighnesh91/-logicsentry-ai

Offline SAST/DAST triage engine that parses source code and replays HAR traffic to detect business-logic flaws, BOLA, race conditions, and privilege…
ai-securityapi-security-testingcode-analysis+9
124 days ago
watchTowr-vs-Atlassian-CVE-2026-21589 preview

watchTowr-vs-Atlassian-CVE-2026-21589

GitHubwatchtowrlabs/watchtowr-vs-atlassian-cve-2026-21589

Python detection artifact that checks Atlassian Jira, Confluence, and Bitbucket instances for the CVE-2026-21589 arbitrary file read vulnerability.

exploitationinformation-gatheringpapers-research+5
1527 days ago
ActiveScanPlusPlus preview

ActiveScanPlusPlus

GitHubalbinowax/activescanplusplus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
api-security-testingdefensive-toolsexploitation+7
66813 days ago
burp-ResponseClusterer preview

burp-ResponseClusterer

GitHubmodzero/burp-responseclusterer

Burp plugin that clusters responses to show an overview of received responses

anomaly-detectiondefensive-toolspenetration-testing+5
147 years ago
active-scan-plus-plus preview

active-scan-plus-plus

GitHubportswigger/active-scan-plus-plus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
api-security-testingdefensive-toolspenetration-testing+6
26011 days ago
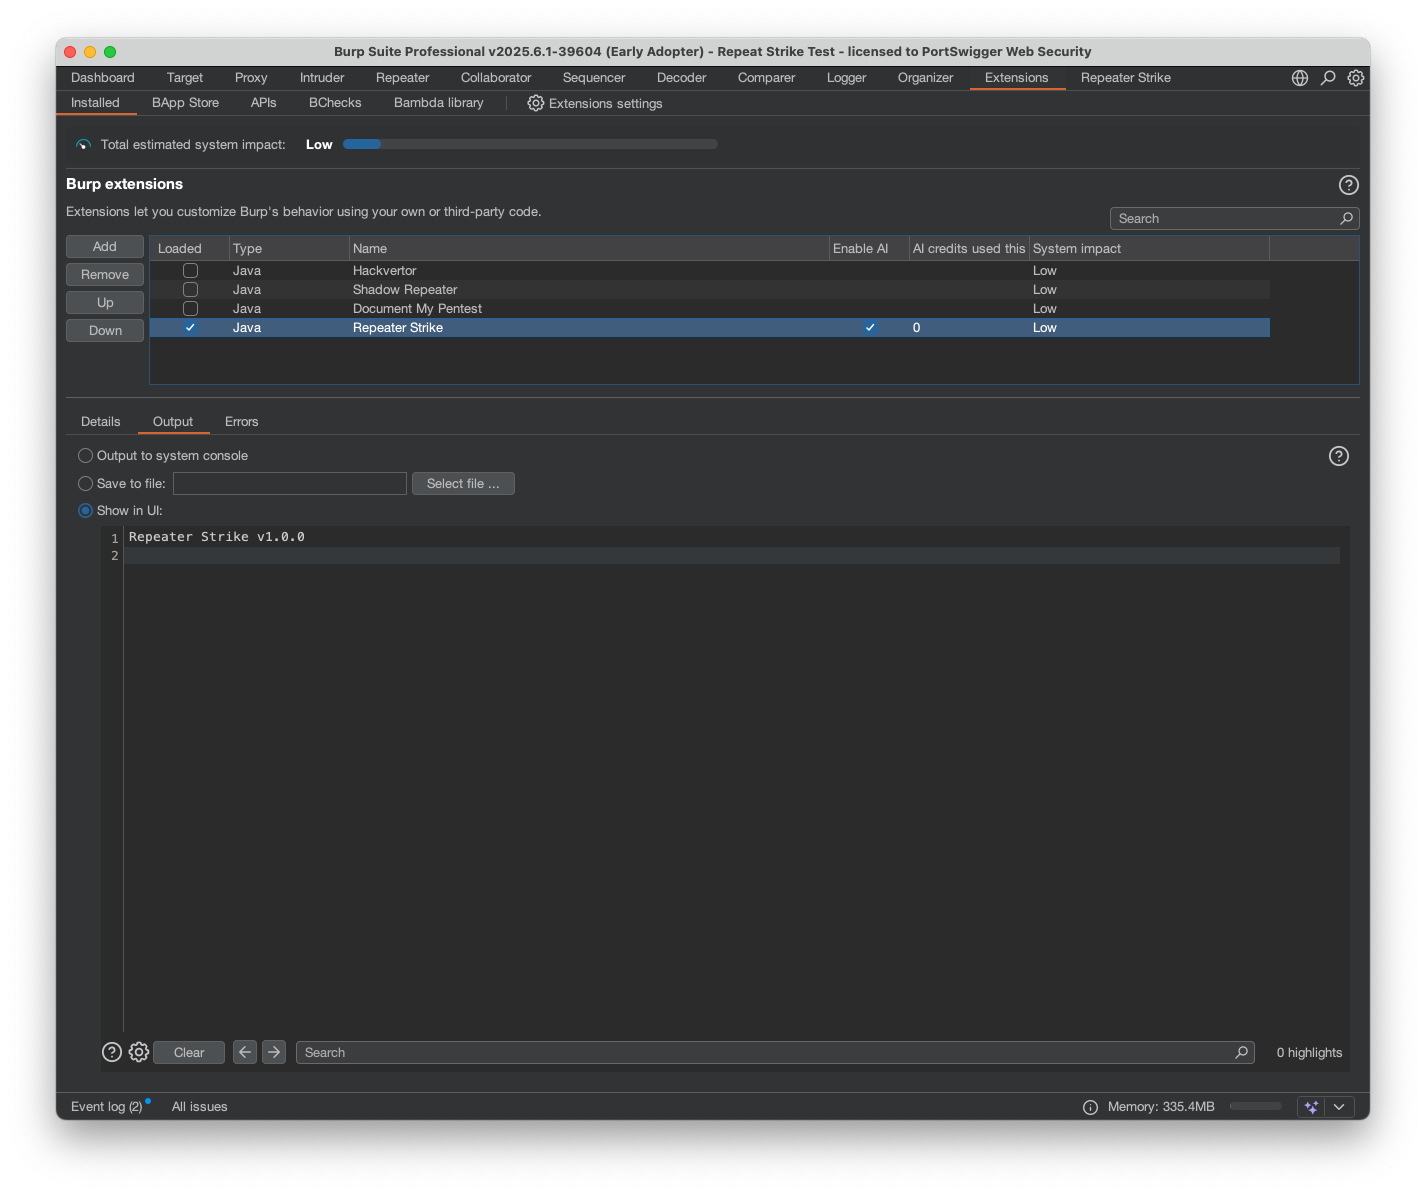
repeat-strike preview

repeat-strike

GitHubhackvertor/repeat-strike

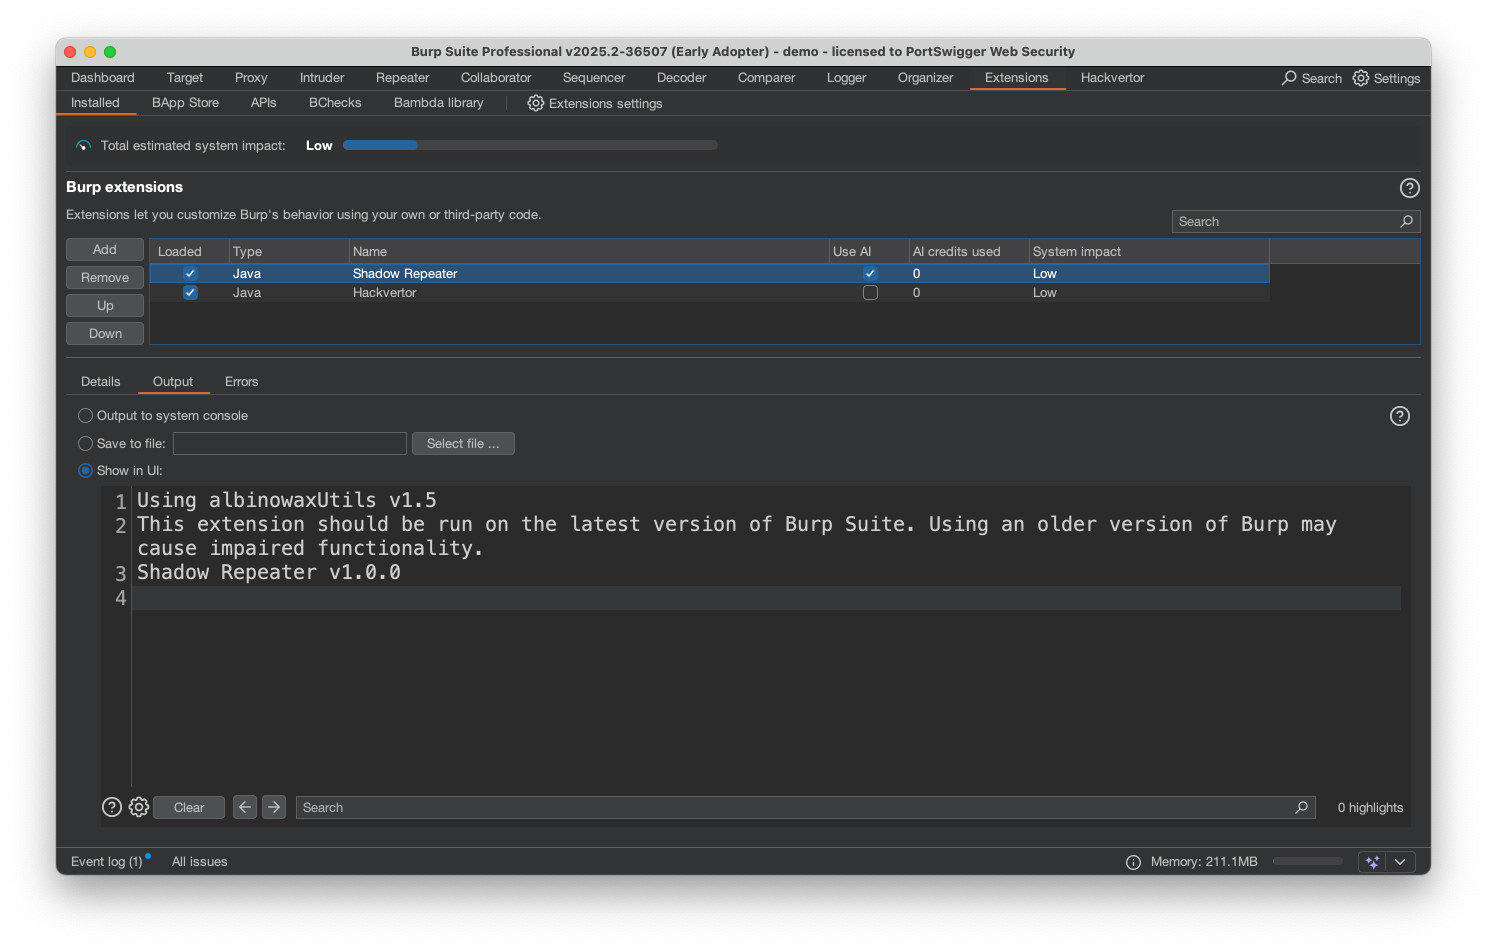
Burp Suite extension that uses AI-generated regex strike rules to detect IDOR and access-control flaws, then scans proxy history to find similar…
ai-securityapi-security-testinginformation-gathering+6
411 year ago
shadow-repeater preview

shadow-repeater

GitHubhackvertor/shadow-repeater

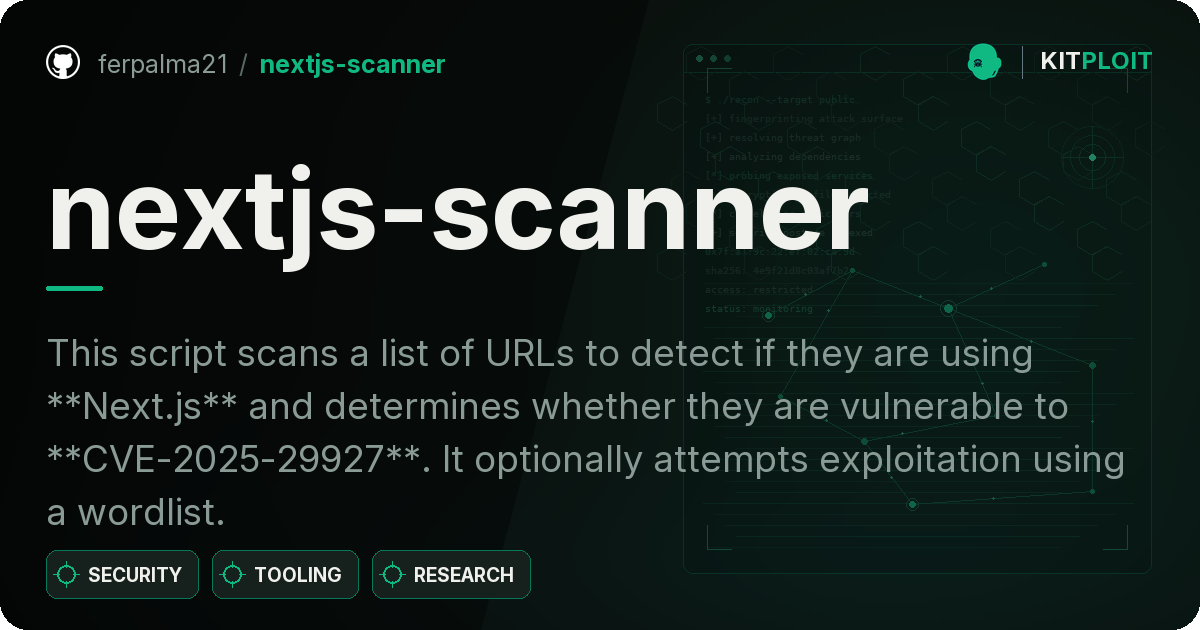
Burp Suite Repeater extension that automatically mutates payloads and analyzes responses to uncover path traversal, SQL injection, XSS, and other web…
ai-securityapi-security-testingfuzzing+6
4311 months ago
nextjs-scanner preview

nextjs-scanner

GitHubferpalma21/nextjs-scanner

This script scans a list of URLs to detect if they are using **Next.js** and determines whether they are vulnerable to **CVE-2025-29927**. It…
exploitationfingerprint-spoofinginformation-gathering+6
21 month ago
CVE-2026-102261 preview

CVE-2026-102261

GitHub7acini/cve-2026-102261

Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.
authentication-authorizationdefensive-toolspenetration-testing+5
1 month ago
CVE-2026-14281-check preview

CVE-2026-14281-check

GitHubabatsakidis/cve-2026-14281-check

A Windows-friendly, non-destructive Python checker for detecting WordPress installations potentially affected by CVE-2026-14281.
defensive-toolsinformation-gatheringreconnaissance+4
1 month ago
Securiscan preview

Securiscan

GitHubvighnesh91/securiscan

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…
ai-securityapi-securityapi-security-testing+8
1 month ago
http-terminator preview

http-terminator

GitHubportswigger/http-terminator

AI-assisted research pipeline that extracts HTTP desync techniques, generates malformed request test-cases, validates them via Burp, and confirms…

ai-securityexploitationfuzzing+8
1253 months ago
Previous12345Next